Skip to content

As security and cyber resilience continue to grow in importance as the top data challenge for organizations today, Commvault is excited to announce the continuation of its webinar series featuring experts from ESG, Microsoft and Commvault. “Navigating Cyber Resilience in a Hybrid World” is set for December 6, 2023, providing insight from our expert panel and sharing the latest ESG research into how organizations are building cyber resilience.  The session will preview highlights from the soon-to be-released ESG study, “A Roadmap to Future-Proof Cyber Resilience with Commvault Cloud,” co-commissioned by Commvault and Microsoft.

Key ingredients for cyber resilience in a hybrid world

The expert panel assembled for this webinar includes Nathan McAfee, Senior Economic Analyst at ESG; Jaimie Fox, Azure Strategy Specialist at Microsoft; and, Vidya Shankaran, Field CTO at Commvault. During this interactive session, the discussion will focus on:

  • Key elements that need to be part of every holistic cyber resilience plan
  • What to consider when striving for the lowest total cost of ownership
  • The role of artificial intelligence (AI) in accelerating your cyber resilience excellence
  • Ensuring successful recovery—an often-over-looked essential ingredient
  • How sustainability can be leveraged to improve your cyber resilience

New opportunities with sustainability and cyber resilience convergence

As part of this session, we’re delighted to feature Jaimie Fox. In addition to his role as an Azure Strategy Specialist at Microsoft, Jaimie is also a founder of the sustainability organization, Data Company One.  Jaimie will share his perspectives on the convergence of sustainability and cyber resilience and discuss how a solid roadmap for cyber resilience also helps organizations achieve their sustainability goals.  This is a discussion you won’t want to miss!

Sign up today and get your questions in

If you have tough questions regarding cyber resilience that you’d like this expert panel to tackle, submit your questions to microsoft@commvault.com. You can register for the December 6th webinar here and download the ESG Study, “Analyzing the Economic Benefits of Cyber Resilience with Commvault Cloud” here.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

In today’s digital landscape, businesses increasingly use hybrid cloud solutions to meet their evolving IT needs. In fact, approximately 87% of companies embrace a hybrid IT approach today.1 Hybrid cloud offers a combination of public and private cloud environments, providing organizations greater flexibility, scalability, and cost-efficiency. Enterprises that want to combine public clouds, private clouds, and on-premises resources to gain the agility they need can be a competitive advantage.

Here are five key building blocks contributing to a hybrid cloud strategy’s success, focusing on lower cost, any-to-any portability, workload management, consolidation, and security.

  1. Lower Cost: One of the primary advantages of adopting a hybrid cloud approach is the potential for cost savings. Organizations can optimize their infrastructure costs by leveraging a mix of public and private cloud resources. Public cloud services offer pay-as-you-go pricing models, allowing businesses to scale resources up or down based on demand, thereby avoiding unnecessary expenses. On the other hand, private clouds provide greater control and security for sensitive data and applications. Businesses can significantly reduce costs by strategically allocating workloads to the most cost-effective cloud environment.
  2. Any-to-Any Portability: Portability is a critical aspect of hybrid cloud success. It refers to seamlessly moving workloads and data between cloud environments, such as on-premises private clouds, public clouds, and edge devices. Any-to-any portability enables organizations to leverage the strengths of each cloud environment while avoiding vendor lock-in. This flexibility allows businesses to adapt to changing requirements, optimize performance, and avoid disruptions.
  3. Workload Management: Efficient workload management is essential for maximizing the benefits of a hybrid cloud strategy. It involves identifying the most suitable cloud environment for each workload based on performance requirements, security needs, and compliance regulations. By effectively managing workloads, organizations can ensure optimal resource utilization, minimize costs, and enhance overall performance. Automation and intelligent workload placement tools can simplify this process, enabling businesses to make data-driven decisions.
  4. Consolidation: Consolidation is crucial in achieving cost savings and operational efficiency in a hybrid cloud environment. Organizations can reduce hardware and maintenance costs by consolidating workloads onto fewer physical servers or virtual machines. Additionally, consolidation simplifies management and improves resource utilization. Through virtualization technologies and containerization, businesses can achieve higher levels of consolidation, leading to lower costs and improved performance.
  5. Security and Compliance: Maintaining robust security and compliance measures is paramount in a hybrid cloud environment. Organizations must ensure that data and applications are protected across all cloud environments. This involves implementing strong access controls, encryption, and monitoring mechanisms that both prevent threats and ensure data is highly available and recoverable from deletion or attack. Compliance with industry regulations and data privacy laws is also critical. Businesses can mitigate risks and maintain regulatory compliance by adopting a comprehensive security strategy and leveraging cloud-native security tools.

A successful hybrid cloud strategy requires careful consideration of various factors, including lower cost, any-to-any portability, workload management, consolidation, and security. Organizations can achieve greater flexibility, scalability, and cost-efficiency by leveraging the right mix of public and private cloud resources. With the right building blocks in place, businesses can unlock the full potential of hybrid cloud and drive innovation in today’s digital era.

No matter what you do or how you do it, Commvault Cloud can help you protect your no matter where it lives with a platform that delivers portability, resiliency, and rapid recovery  — all at the lowest TCO. Here are some additional resources to help you master the hybrid cloud.

See how customers like Power Integrations have transformed their hybrid environments while lowering costs.

“With a long retention strategy, our cloud storage costs were accelerating quickly. Commvault Cloud gave us a way to dramatically lower those costs and keep them predictable, while simultaneously providing us with the data resilience needed to keep our business running.” – Jacob Gsoedl, CIO Power Integrations

Learn how you can master the hybrid cloud with these resources:

References

1. Flextera 2023, “State of the Cloud Report”

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

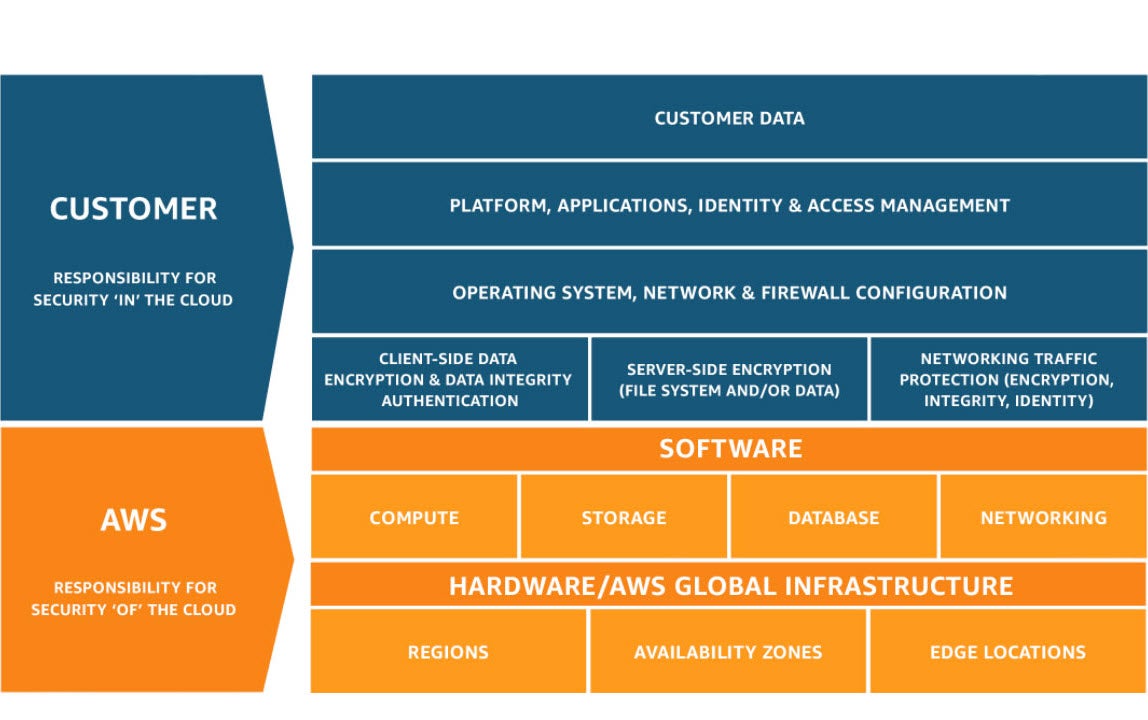
AWS’s Shared Responsibility Model outlines the division of responsibilities between AWS and its customers when it comes to security and compliance in the cloud. AWS manages the security of the cloud, meaning everything from the infrastructure to the physical facilities, while customers are responsible for securing their own data in the cloud and taking appropriate measures to meet specific compliance requirements. This model allows for a flexible approach to security that can be tailored to each customer’s unique needs.

Understanding the AWS Shared Responsibility Model

The AWS Shared Responsibility Model is a framework that outlines how security and compliance responsibilities are shared between AWS and its customers. It is important for businesses to understand this model, as it determines which security controls they are responsible for implementing and which ones are managed by AWS.

Under this model, AWS is responsible for security of the cloud, while customers are responsible for security in the cloud. This means that AWS is responsible for the underlying infrastructure, such as data centers and networks, as well as managing access control to those resources. On the other hand, customers are responsible for securing their own applications and data within their AWS environment.

For example, consider a business that uses Amazon EC2 instances to host their web application. AWS is responsible for ensuring that the physical servers on which these instances run are secure, but the business is responsible for configuring firewalls and security groups to protect their own data.

It is important to note that responsibilities can be shared depending on the specific services used by each customer. The AWS Shared Responsibility Model provides guidelines on which responsibilities should be considered when deploying solutions within an AWS environment.

To further illustrate this point, consider a business that uses both Amazon S3 and Amazon EC2. While AWS manages the physical infrastructure for both services, the responsibility for securing data stored in S3 is mainly on the customer, whereas protecting data on EC2 instances falls under their responsibility.

Some critics argue that there is still confusion around what security risks are being shared. It is important for businesses to take ownership of their end of cloud security risk management so as not to rely solely on providers such as AWS. However, following best practices provided by vendors can go a long way in reducing risk factors in any partnership.

  • The AWS Shared Responsibility Model outlines how security and compliance responsibilities are shared between AWS and its customers, with AWS being responsible for the security of their physical infrastructure, and customers being responsible for securing their own applications and data within an AWS environment. It is important for businesses to understand this model to determine which security controls they should implement. However, businesses should also take ownership of their end of cloud security risk management and not solely rely on providers like AWS, while following best practices provided by vendors can lower risk factors.

Security of the Cloud vs. Security in the Cloud

One of the key concepts that cloud users must understand is the difference between security of the cloud and security in the cloud. As previously stated, AWS is responsible for managing and securing the underlying infrastructure of their cloud service. This is referred to as security of the cloud, as it involves securing the physical infrastructure.

Security in the cloud refers to data protection within a customer’s applications and servers hosted in the cloud. This responsibility falls on customers rather than AWS. It includes managing user access control, network settings and configurations, as well as encryption of sensitive data.

Think of security of the cloud as a hotel’s safe deposit boxes where physical things one keeps are stored. In contrast, security in the cloud is similar to passwords needed to protect one’s one belongings from intruders while inside their hotel room.

It is important to note that businesses should not ignore their responsibilities under security in the cloud just because AWS is responsible for security of the cloud. With this shared responsibility model, AWS provides best practices and guidelines on how customers can ensure their own security in addition to what AWS already provides.

For example, Amazon EC2 instances protected by a firewall provided by AWS have strict default settings with an option to customize. The customer must configure these firewalls on their end such that they will be able to control who can access their instance environments on top of what AWS has done.

Critics argue that relying solely on best practice documentation can result in inadequate protection against attacks. Cloud users need to be diligent about configuring their own systems according to current standards and proactive measures like automated patching systems that alert system managers on when patches become available.

Implementing the AWS Shared Responsibility Model

The AWS Shared Responsibility Model requires both the customer and AWS to take part in ensuring the security and compliance of their system. AWS manages and controls the physical infrastructure stack, while customers are responsible for securing their applications as well as handling identity access management (IAM). It is therefore crucial that customers implement the model effectively to mitigate any potential threats and maintain security.

One key aspect of implementing the model is identifying and evaluating your organization’s data processing needs. This includes understanding your data, classifying each data type and assigning responsibilities to ensure the secure processing and storage of all data. Any sensitive or regulated data must be stored in controlled environments, with strict access control measures in place.

Another important step is selecting a secure architecture design that incorporates access control, network segmentation, logging, monitoring, encryption services, and vulnerability management practices. Access should only be granted based on individual user roles and responsibilities through IAM best practices. At every stage of implementation, cybersecurity awareness training program must be instituted for all employees to ensure they understand their role in maintaining high levels of security.

For instance, let’s say you’re building an application on AWS using Amazon EC2 instances. As per the shared responsibility model of AWS, while AWS takes care of physical security and availability of hardware resources underlying Amazon EC2 instances as well as networks associated with them; it’s your responsibility to manage guest operating systems (including updates) and firewall configurations applied within these machines.

To further solidify this point about user access control, you can use AWS Identity and Access Management (IAM) tools to grant permissions based on what each user needs to do – for instance only allowing read permissions for logs or database queries. IAM also allows for integration with other services such as databases so that users don’t need remote connections – instead they can connect directly within your private network which minimizes exposure points.

An interesting debate that comes up is whether it’s better to be proactive or reactive when it comes to security. The former argues for planning ahead and anticipating potential threats, while the latter involves arriving at solutions after a security breach has already occurred. As with most debates, there are pros and cons to both approaches; however in terms of implementing the AWS Shared Responsibility Model, being proactive is definitely the way to go. This includes conducting periodic vulnerability scans and penetration tests, reviewing logs regularly to identify anomalous activity, and keeping an up-to-date disaster recovery plan ready in case of emergencies.

  • According to a 2020 IDC survey, 64% of IT professionals are leveraging security as a shared responsibility under cloud service providers like AWS to maintain a secure cloud environment.
  • In a 2019 McAfee report, it was found that organizations using AWS experienced more than 2,700 security threats in a month on average, emphasizing the importance of adhering to the shared responsibility model for enhanced protection.
  • A 2018 Gartner report estimates that by 2025, 99% of cloud security failures will be the customer’s fault, highlighting the importance of understanding and managing customer responsibilities within the shared responsibility model.

User Access Control and Data Management Practices

One area where customers have considerable responsibility under the shared model is that of user access control and data management practices. When dealing with critical data, customer permissions must be audited regularly as part of your IAM best practices. In doing so you can ensure that each user only has access to what they need and nothing more.

Data management best practices require you to enforce strict controls over how data is stored, processed, transmitted, accessed and deleted throughout its lifecycle. Data sensitive environments should be secured by role based access control mechanisms as well as encryption solutions like transport layer security (TLS) which safeguard against eavesdropping and man-in-the-middle attacks.

Suppose you have a team of developers working on critical applications in your infrastructure. By using AWS IAM policies in conjunction with Amazon CloudWatch Logs Insights, you can track user activity to find out who accessed what parts of your system and when. With this data, you can determine whether there are any unusual patterns or errors in their login attempts which could indicate a potential security breach.

Additionally by integrating various AWS services you can create a secure environment where users are prevented from leaking sensitive information outside your organization. An example would be using Amazon Macie along with AWS KMS to manage encryption keys so that valuable data stored on S3 is automatically encrypted when it’s written and decrypted when it’s read. This way, unauthorized access to sensitive information is prevented even if your buckets are accidentally exposed.

When it comes to managing user access controls there’s no one-size-fits-all approach; instead different organizations have different requirements and hence must implement a solution that works best for their use case. However, in order to efficiently implement the AWS Shared Responsibility Model genuine effort needs to be made by customers to maintain an environment which is secure and compliant with industry standards.

Advantages of the AWS Shared Responsibility Model

The AWS Shared Responsibility Model has numerous advantages for companies seeking to secure their IT infrastructure while maintaining flexibility in deployment. One clear advantage is that the model allows organizations to focus on their core competencies, rather than expending time and resources on IT security. By entrusting AWS with responsibility for “Security of the Cloud,” organizations can instead concentrate on managing their data, applications and other critical business functions.

Another advantage is that AWS manages all the physical and network infrastructure, reducing the risks of unauthorized access, data breaches or service disruptions. With its global network of data centers, AWS provides reliable, high-performance hosting services around the clock. This level of support enables businesses to scale up or down easily as required, without having to manage hardware upgrades or network implementations themselves.

Furthermore, both AWS and its customers share control over data management practices, meaning that customers can choose the best tools and technologies to manage their data in a way that aligns with their own compliance requirements. This also means that customers can leverage AWS’s industry-leading security controls and compliance certifications to demonstrate adherence to regulatory frameworks.

For example, a healthcare provider using an electronic health record system could use Amazon RDS to host its database while implementing encryption at rest to meet HIPAA compliance requirements. By leveraging AWS’s expertise in security and compliance controls, the company can avoid many of the challenges of managing its own IT infrastructure while still meeting key regulatory standards.

Another benefit is that companies can take advantage of the scalability and agility offered by cloud computing platforms like AWS. With the ability to provision resources on demand and scale up or down quickly as required, businesses can respond more readily to changing market conditions while avoiding unnecessary costs.

Overall, the shared responsibility model offers a flexible yet robust approach to IT security that is tailored to each organization’s unique needs. By leveraging AWS’s broad range of tools and technologies for security and compliance, companies can implement best practices for data management and application security while focusing on their core competencies.

Enhanced Security and Compliance Flexibility

Security and compliance are critical components of any IT infrastructure, especially for businesses that handle sensitive or regulated data. The AWS Shared Responsibility Model provides enhanced security and compliance flexibility by enabling organizations to utilize a range of tools and technologies to meet their unique requirements.

One key advantage is that AWS offers multiple layers of security controls that can be used in various combinations to meet specific needs. For instance, customers can use Amazon Inspector to assess the security vulnerabilities of their applications while leveraging features like AWS Identity and Access Management (IAM) to control user access.

Additionally, AWS provides enterprise-grade encryption capabilities that enable customers to secure their data both at rest and in transit. This includes support for Secure Sockets Layer (SSL)/Transport Layer Security (TLS) for web traffic, Key Management Service (KMS) for cryptographic key handling, and Hardware Security Modules (HSMs) for enhanced security. By making these technologies available, AWS enables customers to build highly secure architectures within its cloud environment.

Another way that the shared responsibility model supports enhanced security and compliance flexibility is by enabling organizations to maintain control over key aspects of their IT infrastructure. For example, using AWS services like Amazon EC2 Dedicated Hosts allows customers to host instances on hardware dedicated exclusively for their use, thus providing greater control over their computing environment and reducing the risks of unauthorized access or other security issues.

An organization handling classified information may require stricter controls than those provided by default shared tenancy architecture. In such cases, using a dedicated hosting solution through AWS would ensure a more secure computing environment without compromising flexibility or performance.

Finally, AWS offers a range of compliance certifications that can help organizations meet regulatory or industry-specific requirements. Compliance certifications applicable across different industries include ISO 27001, PCI DSS, SOC 1/2/3, and HIPAA, among others. By leveraging these certifications and other security tools in combination with the shared responsibility model, organizations can build secure and compliant IT infrastructures that meet their specific needs.

In the next section, we will explore some of the challenges that organizations may face when implementing the AWS Shared Responsibility Model.

Addressing Potential Challenges in the Shared Model

While the AWS Shared Responsibility Model provides a clear framework for dividing responsibilities between customers and service providers, some challenges can arise. These challenges can include understanding who has responsibility for particular elements of security, managing user access controls, and ensuring that compliance regulations are met. In this section, we’ll explore some common challenges faced by organizations when implementing the Shared Responsibility Model and offer suggestions for addressing them.

One common challenge that organizations face is determining what they are responsible for versus what AWS is responsible for in terms of compliance. Depending on the AWS services used and the IT environment integration, different areas of responsibility may fall on different parties. For example, an organization may be unclear about which regulations are applicable to its use of AWS services or how to configure them properly. A helpful approach here would be to consult AWS documentation or experts in the field to clarify any areas of uncertainty.

Another potential challenge is ensuring that users have appropriate access controls while still maintaining proper security posture. The Shared Responsibility Model requires that customers manage their own identities and access control policies within their own environment using IAM tools provided by AWS. This means that customers must ensure that users are authorized to access only what they need to perform their duties. Additionally, customers must ensure that roles and permissions are assigned appropriately based on job function, seniority level, etc., while also limiting access when not needed. Failing to adequately address these concerns can lead to severe consequences such as lost data or compromised systems.

To address these issues, some organizations choose to implement separate identity management solutions outside of AWS. While this can simplify administration and provide greater control over user access policies, it also introduces additional complexity into already complex environments. Moreover, many third-party vendors lack mature integrations with AWS services or may require custom development efforts.

One potential solution is for organizations to utilize AWS’ Identity and Access Management (IAM) service. IAM offers a range of tools and services that enable organizations to define, manage, and enforce policies for access control across their AWS environment. Additionally, customers can leverage IAM roles to provide temporary credentials to external users or use federated login options to support single sign-on (SSO) capabilities.

Another challenge that may arise within the Shared Responsibility Model is ensuring that sufficient levels of security are maintained at all times. While AWS manages the security of its infrastructure layer and abstracted platform services, customers are responsible for implementing secure guest operating systems, applications, and data configurations. One helpful analogy here is thinking about building a house: Just as contractors must ensure that the foundation is stable before adding additional construction layers, organizations must implement appropriate baseline security protocols before entrusting more data or workloads to AWS.

In conclusion, while the AWS Shared Responsibility Model provides an excellent framework for dividing up responsibilities between providers and customers, challenges can arise when implementing it in practice. These challenges commonly include issues around compliance regulations, user access controls, and implementation of appropriate security policies. By leveraging existing AWS tools like Identity and Access Management (IAM), carefully defining areas of responsibility, and following best practices around security configuration management, organizations can better address these challenges and realize the benefits of this model over time.

Common Questions

What are the customer’s responsibilities in the AWS shared responsibility model?

In the AWS shared responsibility model, customers are responsible for securing their own data and applications up to the operating system. This includes configuring security settings, managing access controls, and conducting regular security assessments.

According to research conducted by Gartner, “through 2025, 99% of cloud security failures will be the customer’s fault” (Gartner, 2018). This highlights the importance of understanding and fulfilling customer responsibilities in the shared responsibility model.

AWS provides a variety of tools and resources to help customers meet their responsibilities. These include security features such as Identity and Access Management (IAM) and Services like AWS Config which enables continuous monitoring and compliance checks.

Ultimately, it is crucial for customers to understand and take ownership of their responsibilities in order to safeguard their data and applications on the AWS platform.

What are the AWS provider’s responsibilities in the shared responsibility model?

In the AWS Shared Responsibility Model, the provider’s responsibilities include the security and management of the underlying infrastructure that supports the cloud. This includes physical security of data centers, network and firewall configuration, and operational security such as monitoring and incident response.

According to a report by Gartner in 2022, “AWS continues to be recognized as a leader in public cloud IaaS due to its comprehensive service offerings and expertise in running infrastructure at scale.” The report also highlights AWS’ strong position in security and compliance.

Additionally, AWS offers numerous security features for customers including identity and access management, encryption options, network security tools, and compliance certifications. These features are designed to help customers meet their own shared responsibility obligations.

However, it’s important to note that while AWS provides a secure infrastructure, customers are still responsible for securing their applications, data, and other assets within the cloud. This includes configuring access controls appropriately, patching operating systems and applications, and monitoring for potential threats or vulnerabilities.

Overall, understanding the shared responsibility model is crucial for any organization using cloud services. By working together with their provider (in this case AWS), customers can ensure their data and assets are properly secured in the cloud.

How does the AWS shared responsibility model differ from other cloud service provider models?

The AWS shared responsibility model sets itself apart from other cloud service providers by clearly defining the security responsibilities of both the customer and AWS. This means that customers have more control over their data and infrastructure while still benefiting from the security measures provided by AWS.

Unlike other cloud service providers, AWS takes responsibility for the physical security of their data centers, as well as the security of their cloud infrastructure. This includes the security of hardware, virtualization layer, storage location, and network infrastructure.

On the other hand, customers are responsible for securing their applications and data within the AWS platform. This includes configuring access controls, managing user identities and permissions, encrypting data in transit and at rest, and ensuring compliance with regulations.

According to a report published by Gartner in 2020, the AWS shared responsibility model played a significant role in helping customers improve their overall security posture. In fact, Gartner stated that “by 2023, 99% of cloud security failures will be the customer’s fault.”

In summary, by clearly outlining the security responsibilities of both parties involved, the AWS shared responsibility model provides customers with greater control over their own security while still benefiting from world-class cloud infrastructure security provided by AWS.

Are there any common misconceptions about the AWS shared responsibility model?

Yes, there are common misconceptions about the AWS shared responsibility model. One of the most widespread is that customers tend to believe that once they move to the cloud, all security responsibilities shift entirely to AWS. However, this is not true, and it is important for businesses to understand how the responsibility is shared when using AWS.

According to a survey conducted by LogicMonitor in 2019, 66% of IT professionals believed that cloud providers were solely responsible for securing their customer data. Furthermore, 70% of those surveyed thought they were less accountable for security in a cloud environment compared to traditional on-premise IT infrastructures. These statistics suggest that there is still a misunderstanding regarding security and responsibility in the cloud.

It’s essential to note that while AWS manages physical security and compliance of its infrastructure, customers are responsible for managing security controls within their own accounts. Customers must ensure proper configuration of their applications and infrastructure and implement safeguards such as firewalls, identity access management (IAM), data encryption, patch management, and more.

To quote a statement from AWS’ Shared Responsibility Model whitepaper:

“Customers retain control of what security they choose to implement to protect their content, platform, applications, systems, and networks, no differently than they would in an on-site data center.”

In conclusion, understanding the AWS shared responsibility model is crucial for businesses who use AWS or plan to migrate to the cloud. It’s essential to recognize that although AWS does provide excellent security measures, customers must take responsibility for security controls in their own infrastructures.

How does the shared responsibility model impact security and compliance in AWS?

The shared responsibility model is a key concept in AWS that dictates the different security responsibilities between the cloud service provider and its customers. This model enables users to have greater control over their data, while also allowing AWS to maintain the necessary security standards.

From a security standpoint, customers are responsible for securing their applications, data and credentials, as well as managing compliance requirements, while AWS is responsible for the security of its infrastructure. Amazon claims that its infrastructure is designed to be highly secure, and that it has implemented extensive controls to maintain this level of security—such as physical and environmental controls, network and perimeter controls, and access controls. Additionally, AWS provides built-in security measures such as encryption, monitoring tools and identity and access management services.

In terms of compliance, AWS adheres to various industry standards such as HIPAA for healthcare organizations and PCI DSS for payment card processing companies. However, customers are ultimately responsible for ensuring they comply with any relevant regulations for their industry or region.

According to a report by McAfee in 2020, misconfigured cloud storage services were the primary cause of 1.5 billion records being exposed during the first half of the year alone. This highlights the importance of understanding one’s responsibilities in an AWS environment. Following best practices such as using multi-factor authentication (MFA) for user access and keeping sensitive data encrypted can greatly reduce the risk of data breaches.

Ultimately, understanding the shared responsibility model is crucial for proper security and compliance in AWS. By leveraging AWS’ infrastructure capabilities while also implementing effective security practices on one’s own end, businesses can ensure a secure cloud environment.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Imagine leading security and data protection operations as Chief Information Security Officer (CISO) at a global enterprise when a storm of calls and instant messages erupts your morning routine. A relentless AI-driven attack has taken over devices, systems, and networks – threatening your data.

As the field of artificial intelligence continues to advance, there’s a growing concern about the misuse of AI by cybercriminals to execute advanced attacks. AI-based threats have the potential to be more sophisticated, adaptive, and damaging than traditional attacks. To counteract this evolving risk landscape, businesses must adopt a cyber resilience strategy that embraces innovative approaches. Commvault® Cloud, powered by Metallic ® AI, is the cyber resilience platform for protecting your data and delivering business continuity amidst ever-evolving cyber threats. Combat AI-driven attacks with a platform that is purpose-built to enable true, cloud cyber resilience for the hybrid world, delivering the best security, highest intelligence, and fastest recovery — across cloud, on-prem, and SaaS workloads.

AI-driven Attacks 

 Cybercriminals leverage AI in various ways and explore further enhancements to increase their attack capabilities. For example:

  • Advanced phishing and social engineering
    Generative AI empowers bad actors to automate fraudulent activities, such as crafting of phishing mails, generating fake social media accounts, reviews, and comments, impersonating service and support agents, and carrying out scams. Massive datasets of stolen credentials and personal data can be analyzed in seconds to enhance phishing and social engineering campaigns.
  • Adaptive malware and botnet generation
    AI-driven malware and botnets that shapeshift during attack stages expose exponential risk to IT and security teams by evolving in real-time to avoid security measures, identify vulnerabilities in target systems, and coordinate attacks more efficiently than human-generated threats. A growing concern in cybersecurity is related to AI-generated malware capable of bypass traditional signature-based defenses.
  • Zero-day exploits and supply chain attacks
    Threat actors are creatively hiding malicious code and zero-day exploits from defenders to widen the attack distribution and extend the blast radius. For example, hiding malicious payload inside an AI model that is built to fulfill legitimate functions such as biometric authentication. In another scenario attackers can manipulate AI to learn algorithms of threat intrusion systems and evade their detection.
  • Credential stuffing and brute-force attacks
    By automating the process of gaining unauthorized access to business accounts and systems through stolen credentials and common password combinations AI speeds up the attack itself. Additionally, machine learning algorithms are utilized to evade security detection systems and AI-driven tools accelerate password cracking by analyzing patterns in leaked password databases.
  • Deepfake attacks
    Videos and audio generated by AI impersonate familiar voices and faces to manipulate individuals into performing actions that grant access to sensitive data, systems, and funds. The technology behind deepfakes creates convincing audio and images with minimal input gathered via social media or other public platforms.

AI has the power to amplify the impact and the complexity of cyberattacks increasing potential damage and risks to your data estates. Commvault helps you to address uncertainty by combining cutting edge data protection technology with strong cybersecurity measures in alignment with regulatory frameworks to invest in proper cyber resilience and detection mechanisms that keeps your data protected.

Spotting Threats Early 

ThreatWise, our cyber deception service integrated in the Commvault Cloud that layer’s defenses along the path to your data, shielding it from AI-driven attacks, and surfacing threat actors that are targeting the most valuable assets in production – your data. This early warning layer enables your organization to adopt a cyber resilience strategy defending your data against tomorrows threat actors:

  • Limit the blast radius of an incident and divert the threat sooner – before it’s time to recover. ThreatWise alerts key business stakeholders upon first touch while simultaneously luring attackers in and away from actual critical assets, forcing them to waste resources.
  • Spot the attacker and gather insights about utilized tactics, techniques, and procedures across the complete kill chain. By revealing the original source of the AI-driven attack the symptoms and cause of it can be remediated to stop its aggravation.
  • Delay attacks by confusing and misleading attackers’ algorithms. ThreatWise feeds AI-driven threats fake tokens leading to deceptive data that is making it harder to automate and execute attacks while wasting threat actors’ time.
  • ThreatWise detection is highly accurate, because it’s not reliant on signatures to identify malicious activity, spotting zero-day attacks, shape shifting malware, and silent threats across workloads and data estates.
  • Maximize your response time by automating the alteration of key stakeholders across the business and ease coordination of your recovery to limit impact.

Keeping pace with evolving threats

For more information about how Commvault helps you unleash the power of AI without skyrocketing costs read this blog.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As security and cyber resilience continue to grow in importance as the number one data challenge for organizations today, Commvault is excited to be an inaugural member of the Microsoft Security Copilot Partner Ecosystem. With the launch of Commvault Cloud, the biggest advancement in Commvault’s history, enhanced application of AI and deep integration into Microsoft’s security portfolio are essential elements of Commvault’s continued innovation.

Working together to enhance the value of and interoperability with Microsoft Security Copilot

“We are excited about the opportunity to be part of the Microsoft Security Copilot Partner Ecosystem and the advantages this creates for our joint customers,” said David Ngo, Chief Technology Officer, Hyperscalers, Commvault. “Together with Microsoft, we will continue to build on our 27-plus years of co-engineering to ensure that we remain at the forefront of innovative solutions that solve our joint customers most pressing cyber resilience and cyber security issues—and Microsoft Security Copilot will be a focus for us as we look to advance the use of AI and it’s continued application in data security and cyber resilience.”

Commvault participation in the Microsoft Security Copilot Partner Private Preview

Announced this week at Microsoft Ignite, Commvault is participating in the Microsoft Security Copilot Partner Private Preview. Commvault was selected for the program based on its proven experience with Microsoft security technologies and the valued feedback it can provide to Microsoft.  As part of the program, Commvault is working with Microsoft product teams to help shape Microsoft Security Copilot product development and future releases.

Commvault Cloud Brings “Arlie” the New AI Copilot to Life

In parallel to the joint focus on AI with Microsoft, Commvault is also introducing “Arlie,” short for “Autonomous Resilience”—a new AI copilot that will respond to inquiries from Commvault customers in plain, simple language.  Behind the scenes, Arlie will interface with generative AI models and provide personalized actionable responses.

Learn more – see the joint solution in action

At Commvault, we’re excited to continue our pursuit of excellence in cyber resiliency and cyber security with Microsoft.  For organizations interested in seeing exactly how Commvault is at the forefront of the use of AI in cyber security, be sure to visit https://www.commvault.com/platform.

For anyone interested in learning more about the joint Commvault/Microsoft solution, email us at microsoft@commvault.com.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Every day across the globe, organizations use Microsoft 365 to communicate, create, and store the content that drives their businesses.  This means Microsoft 365 often houses petabytes of valuable data for many customers—data that is critical to business continuity.

Ensuring the resilience and recoverability of Microsoft 365 data

So, how do organizations ensure the safety of Microsoft 365 data, protecting it from unintentional or malicious deletion or large-scale ransomware attacks? In addition to ensuring the availability of applications and infrastructure, Microsoft is adding tools with better performance and trust to enable customers with backup.

Commvault and Microsoft engineers have collaborated to deliver a new solution that protects customers from the most devastating ransomware attacks, using the power of the Microsoft 365 platform itself, with frequent recovery points to which customers can rapidly recover files or emails that might be encrypted or destroyed. This new solution combines the best of Commvault and Microsoft technology with new capabilities for mass data recovery with very high-performance levels, backed by recovery trust from Microsoft.

Building on 27+ years of co-development

“Our product teams have been meeting regularly to ensure that Commvault and Microsoft deliver the best-combined solution to our joint customers,” said David Ngo, Chief Technology Officer, Hyperscalers, Commvault.“Together with Commvault’s current capabilities for flexible, granular recovery and air-gapped infrastructure, the integration with Microsoft 365 Backup Storage enables customers to rapidly respond to malicious attacks and get back to business with minimal disruption. We’re excited to give customers more options to protect their data from malicious attacks.”

“We are pleased to work with Commvault and eager to have customers use their enhanced solutions built on our Microsoft 365 Backup Storage to provide outstanding backup experiences for business stability and confidence,” said Jeff Teper, President, Collaboration Apps and Platforms, Microsoft.

Learn more – see the joint solution in action

At Commvault, we’re excited to pursue data protection excellence with Microsoft.  For organizations interested in seeing exactly how Microsoft 365 Backup Storage will function in a Commvault environment, click here for a walk-through demo.  In the coming weeks, we will publish additional information regarding pricing, public preview, and general availability.  For anyone interested in learning more about the integrated Commvault/Microsoft solution, email us at microsoft@commvault.com.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

At Commvault, we understand that Active Directory sits at the core of your identity and access management infrastructure and is a primary attack vector for bad actors. On December 1, 2023, we are taking the first of several steps towards providing expanded protection for this essential asset in the form of enhanced object and attribute level recovery for both Active Directory and Azure AD (now Microsoft Entra ID). 

The key new features released on December 1 will make it easier for you to identify the scope of a disaster and recover or roll back from it as quickly as possible. The enhanced protection includes: 

  • Accelerated recovery of deleted and changed objects by comparing all objects and attributes between backups. 
  • Recovery of Group Policy Objects, including their security, links, and settings. 
  • Recovery of Entra ID conditional access policies and roles. 
  • Rollback of overwritten or corrupted attributes across many objects at once. 
  • More frequent backups of AD, ensuring it is always possible to restore a recent copy. 

To ensure the highest level of AD protection, we will also transition Commvault® Cloud Backup & Recovery for Active Directory from a free subscription to a paid offering starting December 1, 2023. 

If you are presently protecting your Active Directory or Entra ID environment with Backup & Recovery for Active Directory, you will automatically gain access to the enhanced capabilities described above at no additional cost until June 1, 2024. No action is required on your part, and your scheduled backups will not be disrupted in any way. Starting on December 1, you will have complete access to the expanded functionality in appreciation of your ongoing business. 

If you are not currently protecting Active Directory, you can configure the backup of one Active Directory domain or Entra ID tenant before December 1, 2023, and you will automatically gain free access to these enhanced capabilities until June 1, 2024, with no strings attached. To begin the protection of Active Directory today and gain access to the enhanced protection capabilities through June, open the Commvault portal and click Configure under the Active Directory tile in the Service Catalog.

After June 1, 2024, it will be necessary to purchase a subscription to ensure continued access to the Active Directory service.

Interactive, domain-wide AD comparisons

To make an informed decision as to what objects to restore or roll back, you need a complete report of all changes that have recently occurred in AD. Our new comparisons do just this – they compare all objects and attributes from a backup of your choosing to the current state of AD or another selected backup – and itemize any objects that were deleted or whose attributes have changed. Rather than doing the investigative work yourself, our comparisons will tell you exactly what happened in AD and allow you to interact with the report to search and filter to narrow the results to the objects that require recovery. Most importantly, you can restore the objects directly from the report, eliminating the need to switch between different views and workflows and minimizing downtime or disruption. 

Comparisons can automatically scan for all changes in AD between two points in time or focus on particular areas in AD to speed up results. The results for every comparison are saved so you and your colleagues can review them anytime. 

Related Articles:

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Organizations of all shapes and sizes face unprecedented volumes of cyber threats that can disrupt business operations and tarnish brand reputations. It’s chaotic to say the least. As this threat landscape continues to evolve, it’s crucial for businesses like yours to stay ahead of the bad actors and escalate your cyber defenses.

To help address the chaos, Commvault has partnered with industry leaders in cybersecurity, artificial intelligence (AI), and cloud technologies to help bolster your cyber resilience. These strategic integrations provide customers with advanced security measures, data intelligence, and threat detection capabilities. Combining the strengths of Commvault® Cloud with these innovative partners provides you with enhanced data insights, protection, and mitigation strategies.

The Current Cyber Threat Landscape: When not If

According to a recent IDC study commissioned by Commvault, 61% of respondents believe that data loss within the next 12 months due to increasingly sophisticated access is “likely” to “very likely.” This alarming statistic highlights the urgent need for robust cyber resilience measures. Organizations must be prepared to detect, thwart, and recover from ransomware attacks swiftly. It’s a matter of when and how often.

This is why we have forged partnerships across the security tool chain, including security information and event management (SIEM), security orchestration, automation, and response (SOAR), network detection and response, vulnerability risk threat detection, and data governance and privacy.

Integrating with Leading Security and AI Partners

Commvault’s integration with a diverse range of security and AI partners through the Commvault Cloud platform offers customers a comprehensive approach to cyber resilience. Among them:

  1. Avira: Provides advanced AI-driven threat protection, enabling customers to rapidly identify potential nefarious activity and enhance protection against emerging threats.
  2. CyberArk: We live in a zero-trust world when it comes to cybersecurity. Commvault’s integration with CyberArk’s Identity Security Platform helps customers follow strong Zero Trust architecture practices, reducing the risk of credential theft and exploitation in the face of double and triple extortion attacks.
  3. Darktrace: When “when” happens, quick response is key. Combining Darktrace’s innovative HEAL platform and Commvault’s AI-powered data insights, joint customers can proactively defend against potential cyber threats and swiftly respond to incidents.
  4. Databricks: The more data you amass, the more difficult it can be to maintain governance. The integration between Databricks and Commvault enables customers to leverage AI-driven search capabilities, making it easier to identify sensitive data and improve data governance.
  5. Entrust: Get advanced cyber resiliency to protect critical data from current and future threats with Entrust’s post-quantum cryptography and data encryption solutions, integrated with Commvault Cloud.
  6. Netskope: Netskope’s global SASE cybersecurity platform, combined with Commvault Cloud, helps organizations apply zero trust principles to protect data, ensuring ultra-sensitive data awareness and threat protection.

These build on our already announced integrations with Microsoft Sentinel for intelligent SIEM and Palo Alto Networks’ Cortex XSOAR to accelerate response time.

Battling the threats of today and tomorrow

This is just the tip of the iceberg as there are more integrations with Commvault Cloud in the works to strengthen your cyber resilience against bad actors, malicious threats, and ransomware.

Together, Commvault and our partners help you navigate the evolving threat landscape and safeguard your data, applications, and production workloads across hybrid and multi-cloud environments. To learn more about how these integrations can help power the Commvault Cloud, visit www.commvault.com/platform/integrations.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Under a constant threat of ransomware attacks and malicious cyber activities, cyber resilience is a paramount concern for organizations of all sizes, in all industries. These existential threats make it imperative for businesses to adopt a comprehensive and proactive approach to protect their data and ensure business resilience. That’s why I am thrilled to share our new platform, Commvault® Cloud, powered by Metallic® AI – a transformative platform that revolutionizes cyber resilience in the hybrid enterprise.

With its unified data protection, security, intelligence, threat detection, and recovery capabilities, Commvault Cloud empowers IT and security teams to stay one step ahead of ransomware and other cyber threats. We’re doing this by bringing our on-premises software and Metallic.io SaaS offering together into a single platform with enhancements to the features you already know and love and new capabilities you’re going to love.

Meet your new cyber resiliency partner, Arlie

There’s obviously a lot of hype around AI and how it’s changing the way we work and interact with software and systems. We’re putting AI to use help you act quickly and efficiently.

Users of Commvault Cloud will soon have access to Arlie—short for “Autonomous Resilience” and much easier to say—a new AI co-pilot that’s at the ready 24 hours a day, responding to inquiries in plain, simple language. We’re using Generative AI models to consolidate information and reports plus provide users with personalized actionable responses. You can use Arlie to verify or validate clean point of recovery for critical systems or generate requested code in mere seconds.

I’m excited about the possibilities this creates. It’s fueled by an integration with Azure OpenAI to enable amazing human-like interaction within Commvault Cloud to:

  • Give you real-time threat analysis and report summaries showing the latest information about their cyber resiliency health, removing the need to sift through filters and reports to prioritize the most pressing information. Imagine the time savings.
  • Offer a simplified way to build an integration or code an action: you simply type a description of what you want to do, and the code assistant will generate the code on the spot. No more missing semi-colon fouling up the works.
  • Provide context-sensitive, guided product walk-throughs that make it easy for you to set-up, customize, and tune Commvault Cloud to your specifications. Simply ask “how to” questions and get step-by-step documentation complete with annotated screenshots.
  • Constantly monitors the performance of Commvault Cloud using generative AI to find issues, provide fixes, and offer real-time recommendations on how to optimize cyber resilience.

That’s just the start. We’ll have more generative AI model integrations following fast.

Cloudburst™ Recovery

You know and love us for our ability to recover from ransomware or other critical situations quickly. We’re making it faster and more efficient.

The new Cloudburst™ Recovery capability can help you improve business continuity by using infrastructure-as-code and cloud-scaling to automate rapid and frictionless recovery of data to any location. This enables mass recovery from cloud storage at scale with the highest speed possible. You don’t have to run an expensive cluster in the cloud to be able to do this, saving you money and headache.

Cleanroom Recovery

We also have what we call Cleanroom Recovery, one of the standout features of Commvault Cloud. It’s a cutting-edge service that ensures rapid, frictionless, and reliable recoveries after a cyberattack.

When a cyberattack occurs, having a clean backup is crucial. But it’s equally important to have a clean location for recovery. That’s where Cleanroom Recovery comes in. With Commvault Cloud, you can recover your data to a secure, isolated environment in the cloud that is specifically designed for recovery purposes. This cleanroom environment is “at the ready,” meaning it’s always available to you and prepared to facilitate the recovery process.

Cleanroom Recovery offers several benefits, including:

  • Providing a secure and isolated space for recovery, ensuring that your data is protected from any lingering threats or vulnerabilities. This gives you peace of mind knowing that your recovered data is clean and free from any potential malware or malicious elements.
  • Enabling rapid recoveries. Time is of the essence when it comes to recovering from a cyberattack, and Cleanroom Recovery ensures that the process is as quick and efficient as possible. Using the power of the cloud, Commvault Cloud enables fast and seamless data recovery, minimizing downtime and allowing you to get back up and running in no time.

Cleanroom Recovery is not just for post-attack recovery; it’s also a valuable tool for conducting routine incident response testing. By regularly testing your recovery processes in the cleanroom environment, you can ensure that your systems are prepared and optimized to handle any potential cyber threats. This proactive approach to testing and validation helps to strengthen your overall cyber resilience.

AI-driven threat prediction

Attackers are using AI to make ransomware even quieter and harder to detect. One of the emerging attacks uses AI to change the shape of the malware. Security experts call these shapeshifting or poly-morphic attacks. Whatever you call it, they are extremely hard to see and go undetected by traditional anomaly detection techniques. In Commvault Cloud we’re using AI to fight AI. This helps you find AI-driven zero-day threats that have already impacted backup content so you can quarantine and recover data cleanly while avoiding reinfection during recovery.

Managing cyber resilience for you

As part of the Commvault Cloud release, we’re adding Platinum Resilience, a fully managed service that provides unmatched protection, engagement, and responsiveness to cybersecurity threats and disaster situations. This service, which is being introduced to select customers as part of an early access preview program with full availability planned in early 2024, provides the following:

  • Foundational backup and recovery, advanced AI driven automation, cyber deception, recovery testing and readiness checks, advanced reporting, security audits, custom telemetry, and more.
  • Powerful and comprehensive hybrid data protection and resilience, with the ease of use of the cloud using a dedicated, isolated control plane. 
  • A ransomware readiness and response team dedicated to everything from setup to ongoing testing and validation to recovery upon a cyber event.

We’re confident that Platinum Resilience offers the best in end-to-end cyber resilience and we’re backing that up with a new Commvault Protection Warranty to give everyone from IT managers to board members peace of mind that recovery from an attack is guaranteed.

Commvault Cloud for Cyber Resilience

This is the boldest product launch in my 26-year history here at Commvault. I’m confident that your organization’s approach to cyber resilience will be revolutionized by Commvault Cloud, powered by Metallic AI. With its unified platform, advanced AI capabilities, and unique architecture, Commvault Cloud offers a comprehensive solution for data protection, security, intelligence, and recovery. By leveraging the power of AI, you can benefit from enhanced visibility, simplified processes, and optimized cyber resilience.

With Commvault Cloud, you can have peace of mind knowing that your data is safe, your operations are protected, and your business can continue to thrive in the face of evolving cyber threats. It’s the ultimate solution for achieving cyber resilience in your hybrid enterprise.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Four short years ago, Commvault introduced Metallic, and the promise of data protection for businesses of every size. Our focus was simple – to artfully blend the best of enterprise-grade performance, with a light-touch, cloud-centric consumption model. Harnessing 20+ years of proven Commvault technologies, Metallic was born.  

Now, you didn’t have to sacrifice. Whether across clouds, data centers, or SaaS apps, our customers could uniformly safeguard their data (wherever it lived) while enjoying the durability, simplicity, and scale of the cloud. With constant innovation at the forefront of our vision, Metallic rapidly evolved, supporting the broadest set of hybrid cloud workloads, while pioneering next-generation security, resiliency, and recovery capabilities.   

Thousands of customers later, we are excited to announce the next phase in our journey as Metallic becomes part of the Commvault Cloud

So, what exactly is the Commvault Cloud? We’re glad you asked! 

Commvault Cloud, a unified data resilience platform 

A common misconception is that Commvault bought or acquired our award-winning Metallic SaaS technology. Well, we did neither… we built it from the ground up. Metallic was purposefully crafted to join Commvault’s existing portfolio of data protection offerings, as a light-touch, cloud-centric alternative.  

Commvault Cloud, our newly introduced cyber resiliency and recovery platform, unifies our cloud, software, and appliance-based services into a single place. This not only provides our customers with a consistent and streamlined experience to consume our technologies, but also creates new synergies and capabilities that advance how our customers protect their data. Commvault Cloud stands as the industry’s first platform for true cloud data security. Simpler, smarter and more scalable than ever before for trusted cyber resilience to secure and recover data in today’s hybrid world.

Benefits for Metallic customers  

By melding Metallic and Commvault technologies together into one platform, customers get even faster innovation, automation, and performance. While Metallic users will still enjoy the same SaaS-based backup they’ve come to know and love, the Commvault Cloud will pave the way for even more cloud-delivered advancements in disaster recovery, data security, artificial intelligence, and more. It means the best of all worlds: Simple SaaS protection, next generation cyber recovery innovations, and more flexibility of choice.  

Advanced automation and intelligence with Metallic AI 

While our SaaS-delivered backup and recovery offerings will be consolidated into our new Commvault Cloud platform, the spirit of Metallic lives on in our AI layer: Metallic AI. Metallic AI serves as our artificial intelligence layer that powers our new platform. From automation and machine learning to AI, Metallic AI brings greater performance and efficiency to every aspect of the Commvault Cloud. Metallic AI will also operate as a powerful integration layer for ecosystem partners, enabling developers to create robust, innovative new services that continuously optimize Commvault Cloud, and deliver greater value for those who use it.

We are excited for this next phase in our journey, how the Commvault Cloud is redefining cyber resiliency and recovery as we know it, and continuing to support our customers with award-winning SaaS-based data protection. 

Want to learn more? Check out the following video or visit our FAQ in the Commvault Community for additional details.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Here at Commvault, our values – we connect, we inspire, we care, we deliver – are foundational to everything we do.

This week, we hosted our quarterly internal Global Town Hall meeting and presented our CEO Living Our Values Awards. This awards program helps us to globally recognize and celebrate our Vaulters for their incredible work as they live our values every day.

I’m so proud to announce our FY24 Q2 CEO Living Our Values Award winners:

Metallic Customer Success Team

  • Shrey Ahuja
  • Reine Ayoub
  • Pronoy Banerjee
  • Scott Bauer
  • Ryan Carr
  • Francesco Coppola
  • Elizabeth Crinejo
  • Gemma Dean
  • Arijit Dey
  • Jerienne Esguerra
  • Steve Garrett
  • Melina Guzman
  • Srishma H S
  • Joel Hinchliffe
  • Salman Karim
  • Patrick Kelly
  • Andy Kirby
  • Richard Klauser
  • Kanishka Kohli
  • Brigitte Krause
  • Sanjeev Kumar
  • Tom LaFemina
  • Sally Lavis
  • Yaakov Lidgi
  • Mohana Lingaiah
  • Mark Penny
  • Varad Phatak
  • James Powell
  • Abhinab Pramanik
  • Syed Qadri
  • Sapna Rai
  • Kirk Rose
  • Alessandra Russo
  • Christopher Selph
  • Jayashree Sinha
  • Marta Slusarczyk
  • Nate Sprague
  • Eric Struski
  • David Stupar
  • Vimi Joseph Thengungal
  • Aissa Torres
  • Kent Willshire
  • Tayyeba Zamir

Antonio Silva

Inbar Schuchman

Stephanie Long

Fort Lauderdale Office Opening Team

Sam Hernandez

Stephanie Joyce

Tim Karaban

Tracy Skinner

David Surdukowski

Dee Venello

All these winners set an inspiring example and embody what it truly means to be a Vaulter!

To learn more about what it’s like to work at Commvault, check out our careers site.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

In today’s fast-paced and ever-evolving business landscape, organizations are constantly seeking ways to stay agile and adaptable. This is driving organizations to seek increased flexibility in their software solutions. Traditional on-premises software often falls short in meeting these demands, leading to the rise of Software-as-a-Service (SaaS) solutions. In this blog, we will explore the power of SaaS-delivered flexibility and how it can revolutionize the way businesses operate.

SaaS-delivered flexibility provide organizations with the freedom and adaptability they need from their software solutions. Unlike traditional on-premises software, SaaS solutions are built on cloud infrastructure, allowing businesses to easily scale up or down based on their needs. In fact, 89% of enterprises have a multicloud strategy.1 This scalability enables organizations to quickly adjust to changing market demands, add new users, expand into new markets, or accommodate seasonal fluctuations.

SaaS Considerations

To achieve SaaS-delivered flexibility, there are five key factors to consider:

  1.  It’s important to choose a SaaS provider that offers a highly scalable and reliable cloud infrastructure. A significant advantage of SaaS is its inherent scalability. This ensures that the software can handle increased workloads and provide uninterrupted access to users.
  2. Organizations should look for SaaS solutions that offer anytime, anywhere access. Gone are the days of being tied to a specific physical location to access critical business applications. As of last year, 41.4% of cloud leaders say they are increasing their use of cloud-based services due to the macroeconomic climate.2 This means that employees can access the software and data from any location, as long as they have an internet connection. This flexibility empowers remote work, collaboration across geographies, and increases productivity.
  3. Rapid deployment and updates are crucial for achieving SaaS-delivered flexibility. SaaS solutions can be deployed quickly, often within hours or days, allowing organizations to start using the software and reaping its benefits sooner, driving efficiency and productivity. Additionally, SaaS providers handle updates and maintenance, ensuring that businesses always have access to the latest features and security enhancements without any disruption or costly overhead of maintaining on-premises systems.
  4. Customization without complexity is another important aspect to consider. Flexibility in software often goes hand in hand with customization, so organizations should look for SaaS solutions that offer the ability to tailor the software to their specific business requirements without the need for complex and costly customization. Again, we see a need for this level of customization as 72% of IT Pros are taking a hybrid approach by combining public and private clouds.3 With this model, businesses can configure the software to align with their unique processes and workflows, empowering them to work the way they want to, without compromising on functionality.
  5. Integration and collaboration capabilities are essential for achieving SaaS-delivered flexibility. SaaS solutions should offer APIs and connectors that enable seamless integration and data exchange with other systems. This allows businesses to create a unified ecosystem of software tools, streamlining processes and enhancing productivity.

In conclusion, SaaS-delivered flexibility empowers organizations to adapt quickly to changing business needs. By choosing a SaaS solution that offers scalability, anytime access, rapid deployment and updates, customization options, and integration capabilities, businesses can achieve the flexibility they need to thrive in today’s dynamic business environment. Embracing SaaS is not just a technological shift; it is a strategic move towards future-proofing your business and unlocking its full potential.

For more information on SaaS delivered flexibility, please view our Solution Brief, and watch our recent October 3 webinar on demand.

References

1. Flexera State of the Cloud report, 2023 – 2. Google Cloud Brand Pulse Survey, 2022 – 3. Google Cloud Brand Pulse Survey, 2022

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Why Should You Lower Your RTO?

With a low RTO, you can ensure minimal perceivable disruption of business operations for your internal operations and customers — or no disruptions at all. Revenue is also at stake. Each second that passes while your systems are down and waiting to recover is lost revenue. RTO has a direct correlation to less revenue loss.

Here are two distinct ways you can use cloud backup-as-a-service to effectively bolster your RTO and ensure business continuity during any type of disruption.

1. Granular Recovery

In the event of lost or compromised data, the speed at which you can restore the data is the centerpiece of your RTO. Although full backup image restore is an option for data recovery, this can result in long delays and extended downtime as you wait for each file to be restored, regardless of its mission-critical importance.

Granular file recovery is the superior alternative to full backup image restore because it allows you to perform both file and image-based level recovery from a single pass backup operation. This type of recovery allows the user to identify and prioritize certain mission-critical data and workloads to speed up recovery time and ensure business continuity, instead of waiting for the entire instance to be restored — drastically improving RTO.

2. Flexible Recovery

Flexible recovery is somewhat related to granular recovery. With flexible recovery, you can recover to any account in any region. This means that if one account or region is down, you can recover to another account or region that has not been compromised and quickly resume operating, which can certainly help in optimizing RTO.

Optimize Recovery Time Objective with the Industry’s Best Cloud Backup

Disaster recovery planning is essential for enterprises looking to ensure business continuity during malicious attacks and unplanned disruptions to internal infrastructure. Creating an optimized (i.e. lowered) RTO is a vital component to protecting your enterprise and end users.

Built natively in the cloud, Clumio’s industry-leading rapid recovery capabilities leverage granular recovery, incremental forever backup, and flexible recovery to equip today’s enterprises with fast and efficient data restores that can refine RTO and maintain business continuity during any type of disaster event.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Although AWS backup services certainly provides plenty of its own benefits in terms of versatility, it also has certain shortcomings that prevent it from being a comprehensive solution—not to mention offering only marginal control over cloud costs.

Here are five of the primary challenges AWS backup presents when used on its own.

Five Common Challenges of Using AWS Backup

No Ransomware Protection

Ransomware has become a prevailing threat to enterprises of all types and sizes, with costs forecasted to reach $10.5 trillion annually by 2025. Security experts estimate that one ransomware attack occurs every 11 seconds. How can you effectively protect your data and ideally avoid a ransomware scenario altogether? Or even ensure that you can recover quickly from an attack?

When enterprises use AWS Backup to protect data sources such as S3, EC2, EBS, and RDS, snapshots are automatically created and kept in the same account as the primary data, leaving no separation between the primary data and snapshots.

This means that if a hacker gains access to the primary account, they can easily compromise the snapshots before moving onto the primary data.

Once the primary data has been compromised, there are no longer any backups to restore from—the enterprise’s data has been completely locked. They are now at the mercy of the hackers, who may still keep or destroy the data even after receiving the ransom payment.

Long Recovery Times

Backup is not the only aspect of the data protection equation; data recovery is equally important. If an enterprise’s primary data gets corrupted—be it from bad actors or data failure—it has to have a way to recover the data as fast as possible to avoid significant disruptions to business continuity and its end users.

The lack of visibility into snapshots can lead to costly delays in recovery. Without a precise form of granular recovery, restoring data from an AWS backup can require a substantial amount of time due to the complex process of identifying which data needs to be restored and in what order.

Limited Visibility

The lack of visibility into snapshots within AWS doesn’t just affect recovery time, it can also complicate proving backup compliance with auditors and insurers. Furthermore, maintaining consistent policies across all applications and accounts is difficult and time-consuming when there is limited visibility into snapshots.

Additional Complexity

The basic out-of-the-box capabilities of AWS backup can lead to ongoing complexities that require constant attention from IT teams and their resources. For example, IT teams have to routinely write complex scripts to add any missing functionalities into their data protection solution.

Such scenarios work against the goal of cloud computing in the first place, which is to leverage the speed and agility of the cloud. If you constantly have to devote extra resources just to keep AWS cloud backup running smoothly, you’re not being efficient.

Unpredictable Costs

Aside from ensuring a reliable, secure data backup and recovery system, enterprises also turn to cloud backup to gain cost-efficiencies. At first glance, the TCO with AWS backup can seem reasonable, but expenses can begin to pile up—sometimes exponentially over time.

This is due to the standard snapshot replication and storage process within AWS backup. Snapshots are replicated for long-term retention across accounts, resulting in higher backup costs.

Additional egress charges for any cross-account transfers can further increase these costs, all of which will snowball over time, catching many enterprises off guard.

Why Clumio is the Solution to AWS Backup Challenges

Clumio was specifically designed to meet the various challenges enterprises can encounter when using AWS backup. The cloud-native platform provides AWS backup and recovery through an intuitive interface that requires no additional hardware or software to run.

With Clumio, enterprises receive:

  • Best-in-Class Security that provides air-gapped and immutable backups that are end-to-end encrypted—to provide protection against threats like ransomware and bad actors
  • Rapid Recovery via a granular approach that quickly locates and restores backup files and can cut restore time from several hours to just minutes
  • Better Visibility into your data protection plans and compliance status to ensure you’re meeting business requirements
  • Simpler Backup Management with features like global policies and protection groups that automate long-term data retention as well as data classification
  • Lower TCO thanks to no longer needing to install additional resources, pay egress charges, devote additional IT resources to manage the process, or make mirror copies of snapshots— reducing backup costs by up to 50%

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

EC2-Other is a cost category in AWS billing that includes multiple service related usage types such as data transfer, EBS volumes and snapshots, elastic IP addresses, and NAT gateways. Customers can use it to calculate the total cost of running EC2 instances, excluding fixed hourly instance running costs. Understanding EC2-Other is crucial to isolate individual cost categories within it so that you can optimize your usage of EC2 instances efficiently and reduce unnecessary costs.

Understanding EC2-Other

When it comes to cloud computing, Amazon Elastic Compute Cloud (EC2) is one of the most popular options available on the market. EC2 offers a wide range of benefits, including cost savings, flexibility, and accessibility, but to get the most out of your instance, it’s important to understand the different types of EC2 instances as well as the billing and cost categories associated with them.

First, let’s take a closer look at EC2-Other. This cost category is created by Amazon and is often the second largest cost category on an AWS bill for heavy EC2 users. It includes multiple service-related usage types like data transfer, elastic IP addresses, EBS volumes and snapshots, NAT gateways and more. Essentially, EC2-Other encompasses all costs associated with running your EC2 instances except for fixed hourly instance running costs.

To provide an analogy: think of the EC2 hourly instance running costs as similar to renting an apartment with fixed rent each month. In comparison, EC2-Other would include all other monthly expenses like utilities (electricity, water, gas), cable or internet connection fees, as well as any additional maintenance fees.

Understanding how AWS reports total EC2 costs can be daunting as different reporting tools display costs in varying ways. However, it’s crucial for tracking your usage and monitoring your spending so you can isolate individual cost categories within EC2-Other. Two categories that customers can use to get the total cost of running their EC2 instances include EC2-Instances and EC2-Other.

Now that we have a basic understanding of what EC2-Other means in terms of an AWS bill let’s delve further into the different types of EC2 instances available.

Types of EC2 Instances

Amazon provides several different types of instances to fit individual user needs. Within these categories are varying instance sizes and pricing options.

For instance, the General Purpose burstable instances, as the name suggests, offer a balance between compute memory, CPU, and network bandwidth capabilities. The T3 and M6g instance families are part of this category. If you have workloads with inconsistent usage patterns then these instances could be a great fit.

In contrast, high-performance computing workloads might prefer compute-optimized instances, which come in C6g and C5n family groups. These instances feature custom processors and large memory footprints.

Memory-optimized instances are ideal for workloads that require large scale data manipulation And fast processing power. They incorporate the R5a and R6g. Users can leverage up to 768 GB to support any of their big data applications.

Next up is storage optimized instances (I3en), perfect for data intensive tasks at petabyte scale.

Last but not least, GPU based instances combine the CPU capabilities of the EC2 alongside GPUs purpose built to enable ML training or rendering.

Of course, one might argue: why bother with all these varying types? Though it may seem overwhelming, understanding your precise use case will help you save cost while ensuring optimal performance. For example, running batch jobs are much less expensive with the Standard or above options instead of starting multiple on-demand instances to get the same computation done at a higher price point.

Understanding which type of EC2 instance is right for a specific workload has become increasingly important in recent years as companies lean towards virtualized environments. In the next section we’ll take a closer look at how each instance type differs in terms of performance and features so you can make an informed decision on what works best for your particular business needs.

  • Amazon offers a range of EC2 instances for users to choose from based on their specific workload requirements. Each instance type has its own unique set of features and capabilities designed to optimize performance while minimizing costs. It is important for companies to understand their precise use cases in order to select the best EC2 instance type that aligns with their business needs. By doing so, they can ensure optimal performance while mitigating unnecessary expenses.

AWS Billing and Cost Categories

Amazon Elastic Compute Cloud (EC2) is one of the most widely used cloud computing services in the world. With EC2, users have access to a wide range of virtual machines, or “instances,” which they can use to run software applications, store data, and perform other computing tasks in the cloud. However, as with any cloud service, understanding the costs associated with using EC2 is critical to managing expenses and optimizing usage.

AWS Billing and Cost Categories are a key aspect of using EC2 effectively. Amazon has designed specific cost categories to provide users with a clear understanding of how much they are spending on different types of EC2 instances and related services. By breaking down the costs in this way, users can gain valuable insights into their usage patterns, identify ways to save money, and optimize their overall experience using EC2.

There are two primary cost categories for EC2 – EC2 Instances and EC2-Other. EC2 Instances include the hourly charge for running an instance as well as any additional costs for data transfer or storage associated with that instance. The pricing model for these instances varies depending on factors such as location, operating system, instance type, and usage pattern.

EC2-Other is a separate cost category created by Amazon which could be the second largest cost category on your AWS Bill if you are a heavy EC2 user. It includes a range of service-related usage types such as data transfer, EBS volumes and snapshots, elastic IP addresses, NAT gateways and more. Understanding what costs fall under this category is crucial to unpacking where your expenses lie within that grouping.

AWS reporting tools display total EC2 costs in different ways because several methodologies exist for calculating total EC2 costs based on the tool used. One calculated metric from Cost explorer is called EC2-Other expenditure that calculates the total cost of running your EC2 instances while excluding fixed hourly instance running costs. This can help AWS users determine the expenses associated with different activities without getting bogged down in the details of individual usage operations.

Benefits of Using EC2-Other

EC2-Other has several benefits that make it a crucial part of any cloud computing strategy. One of the key benefits is cost savings and flexibility. By understanding how to isolate individual cost categories within EC2-Other, users can save money by optimizing their usage of EC2 instances in the cloud. For example, if a user identifies an unused NAT gateway or elastic IP address, they can remove these services and save costs accordingly.

In addition to cost savings, EC2-Other provides enhanced security and accessibility features for users. Accessible storage volumes and snapshots offer more flexible backup solutions, while Elastic IPs provide robust means of failover and disaster recovery. This level of redundancy is excellent protection against costly shutdowns or failures that could create inconsistent results, productivity losses or even potential data loss.

Another critical benefit of using EC2-Other is the ability to analyze usage data further. Usage type groups break down each type into its purpose thereby providing clear visibility on how much they are spending in every aspect. It enables pinpoint accuracy when optimizing the overall system by moving between the totality of your EC2 footprint and dive into some of the supplemental usage aspects requiring attention.

By leveraging tools such as Purchase Options grouping, users who have already purchased AWS Reserved Instances can further optimize their usage patterns and reduce overall expenses by adjusting reserved instance coverage based on actual utilization levels instead of predicted ones.

  • In 2023, it was reported that EC2 services accounted for approximately 55% of the total AWS revenue, making it critical to gain insights into its associated costs.
  • The cost of Amazon EC2-Other typically makes up around 10%-20% of the total EC2-related expenses on an average user’s AWS bill.
  • A recent study estimated that analyzing and optimizing EC2-Other costs could potentially yield an average savings of 15%-30% for high-volume Amazon EC2 users who adopt efficient management strategies.

Cost Savings and Flexibility

When it comes to cloud computing, one of the biggest benefits is cost savings. Amazon EC2-Other offers a numerous cost-saving opportunities that can help you optimize your AWS spending and ultimately reduce your AWS billing.

For example, with EC2-Other, you only pay for what you use. Instead of purchasing hardware and infrastructure upfront, which can be expensive, you can simply rent only the resources you need to run your applications. This gives you the flexibility to scale up or down based on your needs without breaking the bank.

Another way EC2-Other offers cost savings is through Reserved Instances or Spot Instances. Reserved instances offer discounts on usage while providing flexibility in terms of instance types, operating systems, and tenancy options. Spot instances provide even greater discounts but are recommended for non-critical applications that have flexible start and end times.

While offering big cost savings, being able to scale up and down with ease also provides a great deal of flexibility. You can quickly increase capacity when there’s a sudden surge in demand or scale your compute environment down during periods of reduced activity.

Say you’re running an e-commerce website and anticipate a high spike in traffic for an upcoming sale event. With EC2-Other, instead of worrying about having enough resources available for the coming week, you can simply spin up additional instances as needed during the peak period and then spin them down afterward. This ensures that you have just enough resources when needed without paying for unnecessary instances during non-peak periods.

All these features make Amazon EC2-Other a popular choice among cloud users looking to save costs while increasing their infrastructure’s flexibility.

Security and Accessibility

AWS has consistently followed industry-standard security practices to ensure safe access to its services over time. Amazon EC2-Other reinforces these best practices by providing safe, isolated network connections, auto-scaling features that protect against system failures, and more.

EC2-Other also provides fine-grained control over access to instances and other resources. For example, you can use security groups to define inbound and outbound traffic rules for your instances, configure network access lists to allow access or deny permissions to specific IP addresses or CIDR blocks, and use Amazon VPCs (Virtual Private Clouds) to create isolated networks for your instances.

At the same time, EC2-Other is highly accessible from anywhere in the world. For instance, you can start up an instance on a cloud server located in Singapore and run its applications from New York with ease. You can also access your instances using the AWS Management Console, a web interface that gives you full control of your instances’ settings, performance metrics, storage usage, and more.

Just like how a bank’s vault provides both security and accessibility—locks keep valuables secure while tellers allow authorized individuals access to their accounts—the EC2-Other’s balance between security and accessibility protects users’ data assets while enabling their teams’ concurrent workflows.

Moreover, EC2-Other assures security by encrypting data both at rest and in transit. You can encrypt Elastic Block Store (EBS) volumes or snapshots with either AWS-KMS (Key Management Service) Managed Keys or Customer Master Keys. This adds an extra layer of protection to confidential data during transfer to different parties through external protocols like HTTPS or SSH.

Analyzing EC2-Other Costs

Analyzing EC2-Other costs is essential to understand the total EC2 cost, which includes all running costs of an EC2 instance except for the fixed hourly instance running costs. EC2-Other includes a range of usage types such as data transfer, EBS volumes and snapshots, elastic IP addresses, and NAT gateways. However, identifying individual cost categories within EC2-Other can be challenging due to the different ways AWS reporting tools display total EC2 costs.

To isolate individual cost categories within EC2-Other, it’s crucial to understand the three logical categories of EC2 costs: existence costs, utilization costs, and subresource costs. Existence costs are those that accumulate when an EC2 instance runs regardless of how much it is utilized. Utilization costs are those that accumulate when an instance is used beyond its fixed hourly cost. Finally, subresource-related charges arise because of additional services linked to an instance.

For example, consider a situation where a company has a 24×7 running web server on an m5.large instance in the US East Region. In this case, the existence cost will be the hourly rate charged by Amazon for keeping this instance online for 730 hours per month (24×30 days). The utilization cost for this situation can be assessed by looking at incoming traffic source regions. During high traffic periods, say from Russia or China instead of their target audience in the US East region, excess traffic could result in excessive utilization charges.

AWS’ cost allocation report shows usage costs separately for each usage type within each service category. In contrast, Cost Explorer aggregates these charges into broader categories such as Data Transfer or Elastic IP addresses while ignoring specific utilization-related charges like VPCPeering-In and Out or PublicIP-In and Out.

Understanding the individual classes of costs goes a long way in helping companies understand the breakdown of their EC2 billing charges, enabling them to identify unnecessary costs and optimize their usage.

Utilization, Existence, and Subresource Costs

Before reducing your costs with EC2-Other, it’s important first to understand how Amazon bills you for its services.

As discussed earlier, AWS separates costs into various categories depending on what service they pertain to. One such category is “EC2-Other.” By looking at individual cost categories within EC2-Other, you can get a sense of which services are costing you the most and where you can make cost-saving optimizations.

In the next section, we’ll dive into these individual categories with a focus on how to identify and isolate them for cost optimization.

Identifying the Right EC2-Other for Your Needs

Optimizing EC2-Other Usage

Utilization cost is one of the individual categories under EC2-Other. Amazon calculates this based on network usage and data consumption from instances that exceed their fixed hourly instance running cost. In contrast, existence cost includes costs incurred by the instance when it is not being used actively but stays online waiting for requests. Finally, subresource-related charges are those that arise as additional utilization-related services linked to an instance.

To isolate utilization costs by operation from other types of costs like existence or subresource-related charges, analyze the values in lineItem/Operation of your AWS Cost Explorer report. Some values denote existence cost like RunningHours:C5 on demand while others indicate Utilization costs like VPCPeering-In and Out or PublicIP-In and Out.

Some companies may argue that isolating individual categories within EC2-Other does not help much since these categories interact with each other. A high amount of data transfer to an EC2 instance like sending large files or backing up databases will result in higher elastic IP and NAT gateway usage charges, leading to unexpected bills. Therefore greater optimization can come from analyzing total cost rather than attempting to break down individual categories within it.

Analyzing EC2-Other costs is similar to a puzzle where pieces need to be put together accurately for a full picture. Ultimately, understanding the individual pieces allows companies first to understand how much each problem area contributes towards the end state’s solution before formulating solutions across all these areas.

AWS offers several tools that customers can use to track their costs effectively and optimize their EC2-Other usage. By examining comprehensive data sets such as utilization, existence and subresource-related charges, you can begin to truly optimize your EC2-Other usage while reducing costs.

Identifying the Right EC2-Other for Your Needs

Utilizing EC2-Other to its fullest potential requires a deep understanding of the different types of instances as well as the cost breakdowns associated with each. Determining which instance type best suits your needs and then optimizing its usage through continuous monitoring can help in achieving significant cost savings.

Amazon offers numerous different instance types for EC2-Other, ranging from general-purpose instances for computing and memory-intensive applications to storage-optimized instances for companies with vast amounts of data. Adopting an instance type that doesn’t fit your workload can lead to unnecessary spending or sub-optimal performance. Therefore, it’s vital first to identify specific patterns within your usage across individual instances to identify the areas that require modifications.

Utilization costs vary significantly by application workload and operational requirements, making it essential to monitor your EC2 usage regularly to ensure optimal resource allocation. It is often found that keeping a balance between instances with spiky workloads and steady-state demand enables organizations to realize significant cost savings while maximizing performance.

Organizations that have dynamic workload demands should leverage spot pricing where possible. These pricing rates are much lower than the standard pay-as-you-consume model, as they represent the available capacity in a given availability zone. However, spot pricing is only feasible when working with non-critical workloads since the rate could fluctuate depending on demand dynamics. Therefore, organizations need to carefully evaluate their workload needs before deciding whether spot pricing is right for them.

Optimizing EC2 instance usage is similar to driving a car more efficiently by monitoring speed, gear selection, and fuel economy metrics in real-time. The more information you have about how your car is performing, the better equipped you are at optimising your fuel usage and prolonging your car’s durability.

Frequently Asked Questions

How much does it cost to use EC2-Other compared to other instances?

The cost of using EC2-Other instances can vary depending on a few factors such as the region, type of instance, and usage duration. However, in general, EC2-Other instances are priced competitively compared to other instances offered by Amazon Web Services (AWS).

For example, according to AWS’s pricing calculator, the cost for an m5.xlarge instance (one of the most popular Instance types) in the US East (N. Virginia) region is $0.192/hour. On the other hand, the cost for an x1e.xlarge instance (an EC2-Other instance optimized for high-performance computing workloads) in the same region is $0.759/hour. Although this may seem more expensive at first glance, it’s essential to note that EC2-Other instances are designed for specific tasks and require specialized hardware to achieve optimal performance.

Additionally, AWS offers different pricing models that can further reduce costs when using EC2-Other instances. One such model is Spot Instances, which allows users to get spare computing capacity at a discounted price when there’s excess capacity available in AWS data centers. This model can provide significant discounts of up to 90% off on-demand prices.

In conclusion, while EC2-Other instances’ costs may appear higher than other instances initially when you factor in the specialized nature of these instances and their unique capabilities, they offer great value for money and can be priced competitively with other similar services in the market.

What specific services or features fall under the category of EC2-Other?

EC2-Other refers to the various services and features that are available as part of Amazon’s Elastic Compute Cloud (EC2) platform, beyond its standard instances. These services and features offer tremendous benefits for businesses that require more robust computing power or that need to run specialized applications.

Some specific examples of EC2-Other services and features include:

1. Dedicated Hosts: With dedicated hosts, businesses can have an entire physical server dedicated to their use, providing greater control over resources and security.

2. Spot Instances: Spot instances allow companies to bid on unused EC2 capacity, potentially saving up to 90% on costs while still getting access to high-performance computing power.

3. GPU Instances: For businesses that require high-performance graphics processing units (GPUs) for advanced applications like machine learning or scientific research, Amazon offers powerful GPU instances with up to 8 NVIDIA Tesla V100 GPUs per instance.

4. Fargate: Fargate is a serverless computing service that allows businesses to deploy containerized applications directly onto EC2 without having to manage servers themselves.

5. Batch: Batch is a fully-managed service for running batch computing workloads at scale.

These are just a few examples of the many services and features offered under the EC2-Other category. According to recent studies, EC2 instances (both standard and other) are in high demand globally, with nearly half of all cloud workloads running on AWS as of 2020 (Source: Synergy Research Group). As such, utilizing EC2-Other can offer significant advantages in terms of scalability, performance, and cost savings for businesses looking to take advantage of cloud computing technology.

Can EC2-Other be used for specific types of applications or workloads?

Yes, EC2-Other can be used for specific types of applications or workloads. In fact, it offers a wide variety of instance types to cater to different computing needs, ranging from general purpose instances to memory optimized and GPU instances. These instances have varying CPU, memory, storage, and networking capabilities to meet the specific requirements of different workloads.

For example, if you’re running compute-intensive workloads such as scientific simulations or video encoding, you could choose an instance type that has more CPU cores and higher clock speeds. On the other hand, if you’re running memory-intensive workloads such as large-scale relational databases or in-memory caching systems, you could go for an instance type that has more RAM.

In addition to the variety of instance types, EC2-Other also provides flexible pricing options that allow you to optimize your costs based on your usage patterns and capacity needs. You can choose between On-Demand Instances that offer pay-as-you-go pricing with no upfront costs or reservations, Reserved Instances that provide significant discounts but require upfront payment for a specified term, or Spot Instances that let you bid on unused capacity at a lower price.

According to a report by Synergy Research Group, Amazon Web Services (AWS), including EC2-Other, had a 33% share of the global cloud infrastructure market in Q3 2022. This indicates the popularity and trustworthiness of AWS services among users worldwide.

In conclusion, EC2-Other is a versatile and scalable compute service that can be used for various types of applications and workloads. It provides a range of instance types with different configurations and competitive pricing options to suit diverse business needs. With its proven track record and solid customer base, it’s definitely worth considering as your cloud computing solution.

How does EC2-Other differ from other EC2 instances?

EC2-Other differs from other EC2 instances in that it provides users with unique configurations to meet specific computing requirements. Unlike other EC2 instances, EC2-Other does not fall into any pre-defined categories and allows users to fully customize their virtual machines by selecting different combinations of CPU, memory, storage, and networking options.

This level of customization makes EC2-Other an excellent choice for running specialized workloads such as machine learning, high-performance computing, big data analytics, and other complex applications that require tailor-made configurations. According to a recent report by Synergy Research Group, Amazon Web Services (AWS), the parent company behind EC2-Other, holds a significant lead in the cloud infrastructure services market with over 30% share.

One of the key advantages of using EC2-Other is that it provides scalability and flexibility without any long-term commitments or upfront costs. Users only pay for what they use, and can easily modify their instance types or numbers with just a few clicks. Furthermore, EC2-Other comes equipped with a wide range of security features such as network firewalls, encryption at rest and in transit, identity and access management (IAM), and compliance certifications that ensure secure operations.

In conclusion, EC2-Other is a game-changing feature within the AWS ecosystem as it gives users complete control over their computing environments. It lets businesses optimize their resource allocation to reduce costs while achieving optimal performance levels for their unique use cases.

Are there any limitations or performance considerations to keep in mind when using EC2-Other?

Yes, there are certain limitations and performance considerations to keep in mind when using EC2-Other for cloud computing. Here is a rundown of some of the most significant ones:

1. Limited Availability Zones: EC2-Other is only available in limited Availability Zones, meaning your options for deploying in different regions may be limited. This can cause issues if you require better geographical coverage across different regions.

2. Lower Network Performance: Compared to other EC2 instance types, EC2-Other instances have lower network performance due to the use of software-defined networking (SDN) technology instead of dedicated hardware resources. This can impact bandwidth and latency requirements for certain workloads.

3. Inflexibility: EC2-Other instances are not as flexible as other instances, which may create some challenges when scaling or adjusting your infrastructure requirements.

Despite these limitations, it’s important to note that EC2-Other still has many benefits for cloud computing workloads. For example, it can provide more economical options for certain applications with low resource utilization requirements.

According to a recent study by Synergy Research Group, AWS continues to lead the public cloud market with a 33% share (as of Q4 2022). Therefore, given the adoption rate and demand for AWS services worldwide, we believe that any limitations on using EC2-Other are outweighed by its clear advantages over traditional on-premises IT infrastructure when it comes to cost-effectiveness and scalability for companies.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

In today’s digital landscape, hybrid environments are the norm rather than the exception for organizations of all sizes. As companies juggle a multitude of workloads, adopt SaaS solutions, and migrate applications to the cloud, they are also faced with the challenge of repatriating data on-premises. This ongoing data sprawl, combined with the ever-evolving threat landscape featuring advanced, AI-fueled attacks, underscores the critical importance of robust data protection strategies to drive cyber resiliency.

To ensure data security and compliance across their entire environment, organizations must integrate data protection measures right from the outset. This proactive approach minimizes risks and potential vulnerabilities, providing comprehensive cyber resiliency.

However, the journey towards cloud adoption is not a one-size-fits-all approach. It’s granular and app-specific, with some applications being rehosted while others are refactored to leverage cloud-native PaaS and Kubernetes services. To navigate this complexity, organizations need a clear blueprint for cloud data protection and resilience that extends to the edge of their environment.

This blueprint must encompass cloud data protection that provides security and resiliency across the entire hybrid infrastructure. This includes all cloud workloads, applications, and services, regardless of their location. Moreover, it should enable seamless data movement between clouds and back on-premises, all while offering a unified view of your entire environment.

To bolster cyber resiliency a comprehensive cloud data protection blueprint should address the following crucial aspects:

  1. Cost-Optimization: Commvault’s unique range of offerings, spanning SaaS, software, and on-premises solutions, can significantly reduce infrastructure management overhead.
  1. Fast Recovery: Thanks to flexible, performance-optimized storage and the ability to create air-gapped copies for ransomware protection, companies can minimize costly downtime.
  1. Air-Gapped Security: Hybrid cloud architecture enables air-gapped protection, complementing ransomware strategies.
  1. Broad Coverage: Commvault provides the broadest coverage for on-premises, SaaS, and hybrid cloud workloads.
  1. Simple Management: Commvault offers a single-pane-of-glass management interface, combined with the agility of a service.
  1. Reliability for Peace of Mind:  Leveraging industry-leading trusted solutions rather than unproven point products provides peace of mind in an environment where cyber resiliency and data protection are paramount.

The Gateway to Hybrid Cloud Adoption

Data protection isn’t just a necessity; it can also be the gateway to effective hybrid cloud adoption for many organizations. The right data protection solution supports cloud maturity by enabling data protection across workloads, regardless of their location on the cloud journey. This provides a solid foundation for a hybrid enterprise, offering the flexibility to protect data where it resides today and where it will be in the future.

Commvault stands out as the unified data protection platform designed for cyber resiliency in the modern, hybrid cloud world. With a coverage breadth that surpasses competing solutions, manageable through a single pane of glass, Commvault instills confidence in managing ongoing changes without the need for multiple point solutions as workloads evolve and grow.

In a hybrid cloud environment where data is scattered across various platforms, Commvault ensures that your organization’s most valuable asset—your data—is protected, compliant, and ready to drive your business forward, regardless of where it resides. Embrace the future of cyber resiliency with Commvault, your trusted partner in safeguarding your data in the hybrid world.

To learn more about how customers have utilized Commvault to create their blueprint for the cloud, click here or join our upcoming webinar on October 3rd, Five Critical Building Blocks for Hybrid Cloud Success.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

In today’s hybrid multi-cloud world, enterprises are running applications and supporting workloads in on-premises, Edge, Cloud or SaaS. As new applications and locations emerge, ensuring consistent strategy around data protection and recoverability wherever data lives is critical – especially in the face of rapidly proliferating, and increasingly autonomous threats.

Gartner Critical Capabilities report, which is released as an essential companion to the Gartner Magic Quadrant, assesses vendors based on 15 key capabilities including Data Center Integration, Platform Security, Ransomware, and Management and more, across seven Use Cases.

We are thrilled and honored that Commvault Backup & Recovery has scored the highest in six of the seven Use Cases in the Gartner Critical Capabilities for Enterprise Backup and Recovery Software Solutions: On-premises (4.74/5), On-premises and SaaS (4.58/5), Hybrid/Multicloud (4.76/5), Hybrid/Multicloud and SaaS (4.65/5), Disaster Recovery (4.48/5), and Ransomware Detection, Protection and Recovery (4.39/5)! Commvault ranked   second highest (4.36/5) for the Data Services Use Case.1

On-premises (4.74/5)

On-premises and SaaS (4.58/5)

Hybrid/Multicloud (4.76/5)

Hybrid/Multicloud and SaaS (4.65/5)

Disaster Recovery (4.48/5)

Ransomware Detection, Protection and Recovery (4.39/5)

We believe/think/feel that the release of this year’s report is indicative of the industry as a whole; data continues to require stronger protection, cyber threat detection and recovery across more environments. At Commvault, this is our sweet spot – delivering secure data protection for the hybrid world. We are honored to be recognized in this year’s Critical Capabilities report and ranked highest in six of out the seven Use Cases. We provide the right mix of detection, security, and recoverability capabilities to help customers meet cyber threats head-on.

We are a twelve-time Leader in the Gartner Magic Quadrant and being recognized again in the Gartner Critical Capabilities report. We [AG3] are grateful to our customers for partnering with us in this journey of continuous customer-first innovation and to our partners in building a data ecosystem with no boundaries.

Get your copy of the 2023 Gartner Critical Capabilities for Enterprise Backup and Recovery Solutions!


Gartner, Magic Quadrant for Enterprise Backup and Recovery Software Solutions, Michael Hoeck, Nik Simpson, Jerry Rozeman, Jason Donham, 7 August 2023. This Magic Quadrant report was previously published as Magic Quadrant for Data Center Backup and Recovery Solutions (2016-2017; 2019-2020); Magic Quadrant for Enterprise Backup Software and Integrated Appliances (2014-2015); Magic Quadrant for Enterprise Backup/Recovery Software (2012-2013); and Magic Quadrant for Enterprise Disk-Based Backup/Recovery (2011).

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally, and MAGIC QUADRANT is a registered trademark of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.

This graphic was published by Gartner, Inc. as part of a larger research document and should be evaluated in the context of the entire document. The Gartner document is available upon request from Commvault.

1. Gartner, “2023 Gartner® Critical Capabilities for Enterprise Backup and Recovery Software Solutions,” Jason Donham, Jerry Rozeman, Michael Hoeck, Nik Simpson, 18 September 2023.

Gartner disclaimer

Gartner does not endorse any vendor, product or service depicted in our research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Fall is upon us! Which means it’s pumpkin spiced latte season and Cybersecurity Awareness Month is just around the corner. It’s a good time to check in on your incident response playbook, particularly the recovery phase. Remember, your cloud provider is responsible for the durability and uptime of their service, but your data—its resilience, integrity, and security—is your responsibility.

Backups—your final defense in the cloud

Risk profiles for cloud data encompass a range of scenarios, including unintentional data deletion due to human error, erroneous software deletes, malicious wipeouts, insider threats from disgruntled or departing employees, and targeted ransomware campaigns. A robust backup and recovery strategy, fortified with features such as data versioning, encryption, and air gaps, serves to enhance organizational data resilience. This multi-layered approach aims to minimize the impact of adverse data incidents by providing fast and secure data restoration, thus mitigating operational downtime and financial losses.

Air-gapped backups can save your company

Snapshots, often stored in production accounts, share the same risk as production data. Cross-account snapshots are also not enough, as they still fall under the organization’s primary security domain. For example, if an actor gains access to the right workload or the right administrator credentials, all data can often be manipulated. A more secure approach involves creating a virtual air gap between the primary account and the backup storage, offering an out of band layer of defense against ransomware and other cyberattacks.

Benefits of air-gapped backups

  • Ransomware resilience: Air-gapped backups ensure data recoverability, even when primary datasets are compromised.
  • Data integrity: Unauthorized access and data tampering are mitigated, particularly with immutable backups.
  • Regulatory compliance: Cybersecurity insurance and specific industry regulations often mandate air-gapped backups, ensuring both data protection and policy adherence.
  • Rapid recovery: Air-gapped backups facilitate quick data restoration, reducing downtime and mitigating adverse impacts.
  • Assurance: Secure backups offer peace of mind and enable IT resources to focus on other mission-critical operations.

Adding protection without adding cost or complexity

Stronger data protection through air-gapped, immutable backups is just one of the reasons that customers turn to Clumio. As organizations grow their cloud presence, controlling costs becomes another challenge to tackle. IT teams are tasked with reducing cloud costs, but often lack visibility into where they can cut their AWS bill without limiting business innovation.

Analyst firm ESG found that Clumio helps customers reduce costs by 30% on average through a uniquely architected solution that optimizes backup and recovery processes. Consumption reports further assist IT teams by identifying where organizations are spending the most for their AWS backups so they can better manage their storage spend. Clumio customers are typically able to reduce their backup costs while increasing their data security.

Clumio at Gartner IT Symposium, October 16-19, 2023

Join us at the Gartner IT Symposium in Orlando, Florida, at Booth #147. Stop by to chat with me or our Field CTO about how Clumio fits into your AWS data protection strategy while meeting your budget constraints.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago