Skip to content

In today’s world, data is your most valuable asset, and organizations are constantly collecting, processing, and storing massive amounts of data. Kubernetes is a container orchestration tool that has become increasingly popular for managing and deploying applications in a scalable and innovative way. In a recent survey, we learned that more than 75% of organizations use containers. However, organizations adopting containers and Kubernetes must consider data protection and security concerns.

In this blog, we will explore the various challenges organizations face when protecting data in their Kubernetes environment. Additionally, we will dive into tools and techniques to ensure data protection for your entire Kubernetes environment.

Kubernetes is no longer something that is coming or on the roadmap – it’s here. In fact, among those organizations that have adopted containers, nearly all (94%) use Kubernetes, and most (86%) even find it critical to their operations. This doesn’t come as a surprise since we also learned that Kubernetes is helping drive effective cloud migration and flexibility, container orchestration, and workload mobility. Organizations also see improved scalability, availability, and DevOps processes when implementing Kubernetes.

Now that we know organizations truly embrace Kubernetes and will continue to use it more moving forward let’s look at what they primarily use it for. On average, over half of an organization’s data (59%) is orchestrated with Kubernetes, and nearly all organizations (94%) plan to utilize Kubernetes more in the next five years to protect their data. However, most organizations (89%) also expect to do more work to protect their data in Kubernetes in the next five years.

Assessing your Kubernetes protection needs

As with any change or disruption, organizations face issues with identifying vulnerabilities and fully understanding their systems and needs when using Kubernetes. When moving to cloud-native applications, customers must be aware that backups and data protection are not always guaranteed. Most cloud service providers follow the Shared Responsibility Model, where they are responsible for securing their service infrastructure, and customers are responsible for securing their data and applications within the cloud environment. About half of organizations currently face challenges with identifying vulnerabilities (52%), assessing backups (49%), scaling based on the scope of operations (49%), and understanding system complexity (48%).

The survey also revealed the top features for organizations when implementing Kubernetes.  Two-thirds of organizations (64%) believe ensuring data security is important in a full data protection system for Kubernetes. Additionally, flexible levels of recovery (56%) and ransomware protection (52%) are important features to more than half of organizations. Additionally, nearly all organizations (95%) find it important that they can back-up data in Kubernetes.

So what does this mean for the future of Kubernetes and ensuring you have a robust data protection strategy for your new stateful K8s applications? You need to recover from all challenges you face today and in the future, such as:

  • Operator error
  • Hardware and software failure
  • Targeted ransomware/malware attacks

Commvault and Kubernetes – protect K8s containers without getting boxed in

Commvault provides K8s-native protection for your stateful (and stateless) K8s applications in a convenient SaaS-based backup and recovery solution. Safeguarding K8s applications includes protecting all configuration data (pods, manifests, secrets, CRDs) and the persistent application data (persistent volumes, persistent volume claims). Protection of K8s configuration and data allows granular recovery of application configuration, persistent data, or the entire application to the original or a new cluster. Recovery to on-premises or cloud locations provides your business with application mobility and the agility to adopt the K8s distribution and operational model that works for your developers. Full data protection of your Kubernetes cluster means recovery of any/all applications can be ensured in a data loss event. And with Commvault, you won’t get boxed into using a single-purpose tool. Our K8s protection is part of Commvault’s strategy to secure, defend, and recover all data distributed across the hybrid cloud. Here’s how GigaOm describes this in its recent Kubernetes Data Protection Radar Report:

Commvault Backup & Recovery is a backup solution that supports more than Kubernetes workloads, making it suitable for hybrid applications that run across Kubernetes, VMs, and cloud services, consolidating backup operations on a single platform.”

–  GigaOm, January 26, 2023

Read about Commvault’s leadership in Kubernetes data protection https://www.commvault.com/analyst-reports#gigaom.

Source: Hanover Research, Kubernetes Attributes and Usage, February 2023

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

I’m excited to share that Commvault has been recognized by Great Place to Work® India for our culture of care and belonging.

We were listed as one of India’s Best Workplaces in Health & Wellness 2022, based on a comprehensive and rigorous assessment that identifies leaders in well-designed practices for workplace wellness.

We’ve also been Accredited for Inclusive Practices™, a Diversity, Equity & Inclusion initiative by Great Place to Work Institute India. This assessment identifies organizations that have internal and external practices to promote equal and equitable participation of historically excluded communities (women, other gender identities, LGBTIQA+, persons with disabilities, veterans, individuals returning from a career break, and other under-represented minorities in the country) in the workplace.


I’m so proud our organization has achieved this recognition. Here at Commvault, we continue to prioritize our culture of holistic wellbeing and DE&I as we support each other and show how we care.

When it comes to health and wellness, we believe the total wellness of each of our employees builds a better company and a better world. Having a healthy work-life balance is crucial and creating a culture of balance and flexibility is greatly important to us. And we know that in order to deliver for our customers and partners, we must deliver for ourselves first… which means caring for ourselves! We also continue to honor and celebrate our diverse Vaulter community and cultivate an environment of respect and belonging. Listening to the experiences and perspectives of others and learning how to better support one another empowers us to create a more equitable future together. 

Congratulations to our India team!

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Transformative, channel-friendly, and cutting-edge are just a few of the adjectives the editors over at CRN used to describe the companies they’ve chosen as the cream of the crop – the 2023 CRN Storage 100 List – an honor that recognizes industry-leading storage vendors that deliver the best channel-friendly products and services the industry has to offer.  

According to the publication, the companies they chose for this year’s Storage 100 list have been selected by CRN editors for their “perseverance in pushing the boundaries of innovation through cutting-edge technology and strategic partnerships.” 

It’s definitely a difficult landscape to navigate, with too many vendors to count. Luckily, the Storage 100 list is a valuable resource for solution providers looking for vendors that can support them in a complex storage market with industry-leading portfolios in areas such as data protection, management and resilience; software-defined storage, and storage components.  

CRN emphasized that this year’s list also represents the industry leaders of storage technology that can be used for on-premises or cloud deployments. This is a critical point. Resiliency is key in a world where vendors and partners are trying to help customers keep their data safe, unharmed, and always-on across cloud, on-prem, and SaaS workloads…enter Commvault.  

Recognized in the Data Protection, Management, and Resilience category, we offer a simple and unified Data Protection Platform that spans the complete enterprise data estate, regardless of where that data lives. Whether it’s software-defined distributed storage such as containers, a storage appliance like Commvault Grid, or cloud storage in the form of Metallic Recovery Reserve™, Commvault helps customers accelerate their digital transformation journey with unmatched scalability, security, and resiliency.  

Blaine Raddon, CEO of The Channel Company shared his sentiments about this year’s program, stating, “CRN’s 2023 Storage 100 list recognizes the leading vendors that are delivering transformative advancements in storage technology and bringing modern solutions to customers and solution providers that are built for the future. We are honored to recognize their contributions as the leading players in storage technology for 2023.” 

Like CRN, we are also honored; honored to be celebrated for our industry-leading data protection, honored to be highlighted as a recommended choice for solution providers, and honored to continuously be innovating. 

The CRN Storage 100 list will be featured in the April 2023 issue of CRN Magazine and online at www.crn.com/storage100.  

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Spring is a time of renewal and rejuvenation – when we can finally shed the weight of winter and start anew. As flowers bloom and trees bud, it’s the perfect time to reassess and enhance your data protection and recovery plans.

Like planting a garden, taking stock of what you have and what you need is important. Just as you wouldn’t plant a flower in unsuitable soil or without sufficient water, you wouldn’t secure your data with the wrong tools or without a plan. As the saying goes, “fail to plan, plan to fail.” This is especially true when it comes to safeguarding your organization’s data.

The ramifications of a data breach or loss can be catastrophic, ranging from lost revenue and productivity to reputational damage and legal consequences. Minimizing the impact of such events requires a comprehensive readiness plan to prepare for and respond to potential outages.

Being recovery ready means having the confidence and ability to quickly recover any data across your environment.

Routine maintenance is key

One of the most important aspects of a successful garden is tending to it regularly. The same is true of data protection. You can’t simply set it and forget it. Regularly reviewing and updating your plans will ensure they remain effective and continue to meet your business needs. And with the growing frequency and sophistication of ransomware attacks, conducting regular assessments of your infrastructure and readiness plan has never been more crucial.

Fortunately, having a comprehensive data protection solution supported by expert resources can be a game-changer to help reduce the risk of ransomware and ensure a rapid recovery from an attack. You have the most robust data protection capabilities and access to expert support at every step during your data protection journey with Commvault® Professional Services.

Additionally, having a data protection solution that offers a robust set of continuously updated and expanded features is vital in your review efforts. Implementing a regular maintenance schedule to manage your data protection environment allows you to incorporate and update valuable capabilities. Visit our What’s New Page for Platform Releases to explore our latest features and enhancements.

Be ready for anything

Maintain a state of readiness so you can respond to any data-compromising event. Whether your organization needs more support in designing your ransomware recovery readiness plan, maintaining it, or recovering from an attack, with Commvault Readiness Solutions, you choose the service level that best aligns with your business requirements. Service offerings include:

Ready helps you align Commvault’s technical capabilities with your recovery objectives.

Steady assists you in monitoring and maintaining a state of recovery readiness.

Respond helps accelerate your return to normal business operations in the event of an outage or disaster.

Harvest data protection success

Just as a well-tended garden can bring happiness, a robust data protection and recovery plan can provide peace of mind. So, take advantage of the spring season to plant the seeds of a strong data protection and recovery plan and watch as it grows and flourishes in the months ahead.

Chat with a representative to learn how Commvault can help prepare your ransomware response plan.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

We know that data protection can be a serious matter, but we’re here to put a fun spin on it for World Backup Day! Are you ready to evaluate how you secure your sensitive information and ask the tough questions about the products you’re using?

At Commvault, we understand the importance of data protection, and we’re here to provide you with the answers you deserve. Join us on a journey as we tackle six of the most frequently asked data protection questions, and we’ll show you how to keep your business secure.

https://play.vidyard.com/AMTPw7ny3Ahn5Ju3rCTFEr

Data breaches and privacy violations can be a real headache for businesses. Not only can they lead to legal and financial repercussions, but they can also harm your reputation and customer trust. That’s why it’s crucial to be informed and vigilant when it comes to your data protection strategies.

It’s time to separate fact from fiction when it comes to data protection. Don’t fall for those fancy marketing claims without doing your research first. Are these companies innovating at the same pace as your data growth? Are they helping you make the most out of your IT budget? Are they selling you a product when what you really need is a platform? These are the questions you need to ask!

Partner with a trusted data protection provider, like Commvault, to ensure that your sensitive information is always safe and sound. Contact us today to learn more about our data protection solutions, and let us help you protect your business and your clients’ information.

Remember, data protection doesn’t have to be boring. With the right attitude and a little bit of fun, you can stay informed and secure while making sure your business thrives!

Follow Commvault on Social Media for more insights on #WorldBackupDay!

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As Women’s History Month comes to an end, we’re continuing to celebrate women at Commvault all year round! As a working mom and proud co-leader of our Family Support Network Employee Affinity Group (EAG), I wanted to share my experience in hopes to empower working moms (and dads!) everywhere.

I began my career in Human Resources (HR) over 25 years ago, and have been at Commvault for the past 11 years. I was always a people-centric person, and being in HR allowed me to celebrate the human side of the business and focus on the people, a company’s most important asset. Building strong connections and empowering people to thrive and grow is what has inspired me throughout my career.

Having empathy has always been an integral part of my role as an HR leader, but my level of empathy completely evolved once I became a mom. I am blessed to have two beautiful sons in my life – Jake, 8, and Ryan, 6 – but my journey wasn’t without challenges. In 2016, I found out I was pregnant with identical twin boys. After my initial shock that I was going to be 42 years old with three children under the age of two – I was overjoyed! After some complications 24 weeks into my pregnancy, I ended up delivering Ryan and Max prematurely. The next day, Max passed peacefully in my husband’s arms. I was completely numb after this tragedy, yet still had a critical newborn baby in the hospital and a 19-month-old at home whom I had to stay positive (and thankful) for. 129 days and three surgeries later, Ryan was released from the hospital, a day after his original due date. He’s a happy and healthy boy today.

As a mom, you change after you have kids. And after losing a child, I changed even more. It made me realize that you never know someone’s full story – which is why always leading with empathy and care is crucial to building relationships and creating a positive, supportive work environment. That’s why I’m so passionate about not only what I do in HR, but also my involvement with our Family Support Network EAG. This is a support group for working parents and caretakers in all facets of family life – from being a new parent to dealing with toddlers, tweens, teens, and aging parents.  

In the spirit of celebrating working moms (and all working parents!) I wanted to share some tips and tricks I’ve learned from my fellow Vaulters that have helped me become a better working parent:

  • Learn how to unplug from work. Disconnecting is harder said than done, however, we all have to unplug at some point or else we’ll burn out. Remember – taking time to reset is crucial in helping us come back to work the next day refreshed and recharged. I turn off my phone at night after a certain time to help disconnect from work.
  • Talk to your kids about your job. Working and living at home is the reality for many of us in this new hybrid work world. Young children often don’t understand why mom is home but can’t spend time with them during certain hours. Explaining what your job is to your kids can help them better understand you and the concept of this new way of remote working.
  • Embrace planning. Whenever I have a busy week coming up, I create a schedule and plan ahead to make things less stressful. A big thing for me – planning dinners. This allows me to avoid wasting time figuring out what we’re going to eat after a hectic day and gives me more quality time with my kids.
  • Remember that feeling guilty is normal. Finding a balance between being a parent and working is always going to be a challenge. We’ll likely always have moments when work gets in the way and we feel guilty about having to miss time with our kids. Or on the flip side, we may feel guilty stepping away from work to do something with our kids. Find a routine that works best for you and remember to not be so hard on yourself!

Trial and error is the key to success in many aspects of our lives, especially with parenting. I can tell you firsthand that life throws many obstacles at us, and at the end of the day, it’s important to realize that we are all human. Celebrating and supporting each other as parents and caretakers is what helps us stay grounded and inspired, so let’s continue to embrace the power of empathy! When we open our minds and hearts to better understand each other, it not only makes us better professionally but personally too. I’m so thankful to my global Vaulter community and our Family Support Network for allowing me to share my story and learn from others every day.

To learn more about Commvault’s culture of caring, click here.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Data protection is a team sport. We pride ourselves on our alliance and technology partner community, and there is no question that partnering to provide more deeply integrated and effective solutions adds value for our customers.

But one thing we don’t do (unlike some we could name….) and that is to partner to fill and hide gaps and then position it as a benefit to customers.

There’s no integration, no added value, just PR and additional complexity… And it’s the customer who suffers.

What does that mean for the customer?

Let’s be honest, most vendors in the backup market are good at a limited or select set of things:  Good at VM backup, good at big backup appliances, good at protecting Salesforce, good at protecting M365, or Oracle or Kubernetes, but rarely are they good at LOTS of things…which leaves them with gaps in their solution capabilities, a few bricks shy of a load, lacking cohesion, or just plain green with envy – take your pick on the saying that applies.

This problem really rears itself when customers find themselves and their business has evolved to need new data protection capabilities such as protection of Azure Active Directory, Oracle Cloud, or more proactive data security. 

Not every vendor has the vision to anticipate these innovations and changing business needs and incorporate them into their solutions, meaning they’ll be left trying to catch up or be left behind.  This forces, the vendor to look in the mirror at their own technology stack (or tech debt) and realize the change is too big or will take too long for them to deliver it on their own, and in that case they have to either give up on addressing that need or go in search of someone they can buy or partner with to bolt-on that functionality.  

Despite the marketecture, at the end of the day you are left with two or more completely different solutions, with little to no integrations between them, supported by multiple account teams, and ultimately get more of what you don’t want in your environment:  Cost, complexity, friction, and risk. 

Now you’re faced with more questions:

  • Who do you even call if something breaks?
  • How can you consolidate or automate when you keep adding more pieces into the puzzle?
Really, it makes Mando angry!

So what is “THE WAY”?

We can agree that more products = more cost = more complexity = more risk, right?

Well, fixing that is something pretty obvious – and much simpler:  Tackle data protection with a single unified solution.  Multicloud, on-prem, SaaS, hybrid — One solution to rule your data! 

[Commvault enters the chat]

Rather than rely on others to do the work for us, we’ve built the Commvault platform from the ground up, which has allowed us to easily grow the solution to meet new challenges and demands such as data governance, transformation, and multi/hybrid cloud evolutions in customer environments.   

We’ve been listening to our customers and anticipating their needs for a long time. 

Just to name off a few examples:

When our customers needed deduplication to reduce their storage costs, we built
it right into the software. In fact, we were the first to deliver embedded software
deduplication without the need for expensive proprietary appliances.
Anticipating the future potential for containers, we built in protection
for containerized workloads as far back as 2017.
Understanding the shift to SaaS, we built Metallic – the first (and still only) fully
managed SaaS backup service for muilticloud, SaaS, endpoint, and hybrid
data protection. Operating as a unified platform, Metallic and Commvault provide
flexibility and value for customers to choose the best fit for their environment
and expand as their needs grow.
Recognizing the need for increased data security against growing threats, we built
ransomware detection into the platform.
A few years later we launched Metallic Recovery Reserve, which was the first dedicated
cloud air-gap solution in the data protection market.  Every one of our competitors
followed suit over the following 24 months.

Owning the Code

OWNING the code also makes it easy for us to pivot and expand the services of the platform to encompass new workloads such as cloud, DBaaS, SaaS and allows us to leverage the latest infrastructure innovations like object storage, containers, and cloud compute/storage technologies (e.g.: AWS Graviton) to efficiently deliver those services how you need to consume them.   

This unified approach also enables a higher degree of automation across the environment and provides greater observability to potential risks and threats to the data.  Automate. Secure. Respond.  These all get easier when you can consolidate and reduce the friction by reducing the tools and touch points needed to manage your diversifying data landscape.

So, if your environment was all virtual and physical systems yesterday – Commvault has you covered.  And you added cloud and M365 into it today – Commvault has you covered.  And then when you need to add containers, new cloud-native apps, and more in tomorrow, guess what?  Commvault still has you covered.  No need to reinvent the wheel or bolt on more point products to cover the changes in YOUR data needs – you can trust Commvault to provide that consistent data protection across whatever your data is and wherever it lives.

In Conclusion

QUESTION IT – When you’re digging into HOW a vendor or vendor(s) are actually going to deliver their solution and meet your business needs, to see if it’s all just more talk or if it can really do everything it says it can. 

Ask yourself: Should you really be using a data protection provider that can’t protect your SaaS data?”

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

March is a month for us to celebrate women, as we honor both Women’s History Month and International Women’s Day.

As a Vaulter and member of our Women in Technology Employee Resource Group (ERG), I recently had the great honor and privilege to lead a group of students at San Diego City College for the City Women Rock Conference to celebrate International Women’s Day on March 8th. The conference is designed to ignite, inspire, empower, and uplift students – many of whom face significant adversity, such as overcoming challenges of poverty, domestic and gang-related violence, and personal hardships. During the conference, our local community came together to share stories of triumph, reflecting on the many achievements of women throughout history and providing a blueprint for not only achieving goals, but lifting up others along the way. City Women Rock focuses on the following key strategies to empower women to achieve their goals:

  • Gratitude practice
  • Journaling
  • Prioritizing self-care
  • Voicing your dreams
  • Goal setting
  • Positive affirmations 
  • Asking for help 
  • Transforming fear into fuel 
  • Overcoming self-limiting beliefs 

These strategies truly resonate with me, and I was honored to speak at the conference to share more on this and my personal story of overcoming an eating disorder, addiction, and low self-esteem in my early adolescence years. These challenges ultimately led me to a 15-year path of healing, transformation, and growth. I can proudly say that I came out on the other side with unshakeable self-love and inner confidence. Implementing positive changes has resulted in becoming the woman, mother, daughter, sister, friend, and leader that I always wanted to be.

I’m so thankful for my local community and the opportunities that organizations like City Women Rock provide to women to allow us to be our best selves. I’m also grateful for my Vaulter community and our Women in Technology ERG. This ERG brings together both women and allies to elevate and advance gender equality in technology and celebrate the inspiring women of Commvault who are driving our innovation and growth every day.

We all have personal stories to share of strength, stability and overcoming adversity. As we continue to celebrate women throughout March, let’s remember the importance of empowering ourselves and others to uplift, inspire and encourage each other to achieve GREATNESS.

To learn more about Commvault’s culture and ERGs, click here.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

The rise of cloud computing has revolutionized the way organizations manage their data and has quickly become the preferred method for storing and accessing critical information. Pre-pandemic – cloud adoption for databases was growing at an exponential rate, with more and more organizations making the switch to single cloud vendors. Post-pandemic – Cloud database adoption continues to grow but as customers become more cloud-savvy most enterprises are embracing a multi-cloud and/or hybrid cloud approach to get the best of both/multiple worlds for their database workloads.

According to a Flexera report, 89% of all enterprises use multi-cloud while 80% of enterprises have a hybrid cloud strategy with single or multiple clouds.

A hybrid or multi-cloud database strategy comes with its own challenges –

  • Complexity – Keeping track of multiple tools for multiple clouds and multiple database types.
  • Cost – Redundant costs increase as teams across an organization employ their own tools, sometimes doubling up on capabilities and infrastructure.
  • Security – Security teams must defend against new threats while managing cloud database services and tools that are different from one cloud provider to the next. Security becomes more challenging with an ever-growing attack surface.

Here is how Commvault helps mitigate these challenges for cloud database protection –

  • Management made simple
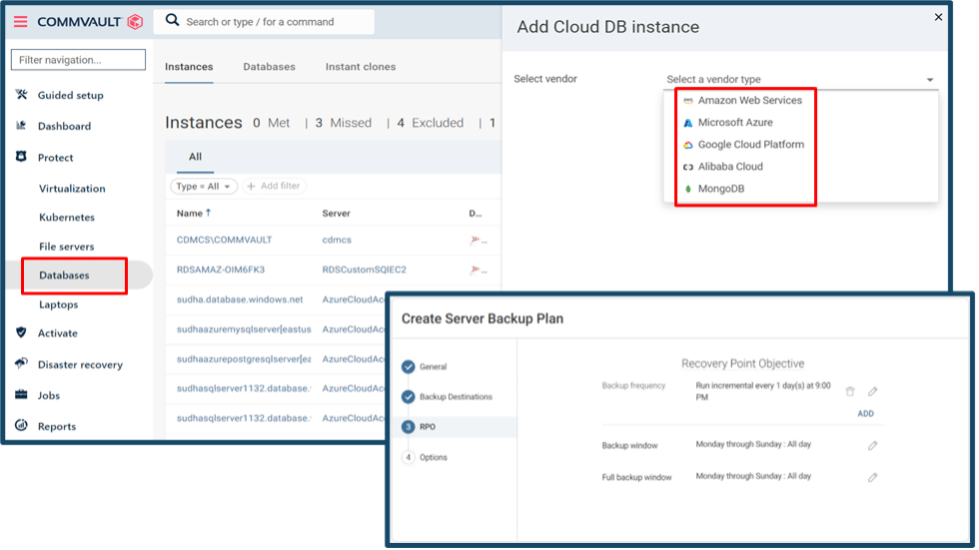
    Single UI and API-first support that gives simplified & unified control with cloud-native integration to automatically discover, protect and manage database copy lifecycle. Ability to define RPO policies that are uniform across hybrid cloud & multi-cloud with a blend of snap and backup. Ability to protect instances, complete regions, or multiple regions.
  • Broad workload, cloud, and multi-cloud portability support 
    Commvault has the largest cloud, database workload, and multi-cloud portability support as compared to any backup vendor in the market today thus meeting the customer’s data protection needs no matter where they are in their multi-cloud journey.
  • Cost Savings
    Most backup vendors use snap as a backup strategy for their cloud databases. They provide snap orchestration which, while easing management overhead does not reduce the snap storage costs. Commvault on the other hand provides customers with a unique way to blend snap and export-based backups which leads to significant reduction in cloud database protection costs as compared to other solutions.
  • Security
    Secure access to the Commvault environment with RBAC-based control and multi-factor authentication. Ensure that backups are tamper-proof with encryption and air-gapped immutability. 

In conclusion, Commvault helps to manage databases on-premises and across multiple clouds using a single platform. We continue to innovate and bring new products and solutions to the ever-changing database eco system to provide simple, comprehensive, secure and cost-effective data protection and recovery capabilities where customers needed it the most.

To learn more:

References

1- Source: https://www.flexera.com/blog/cloud/cloud-computing-trends-2022-state-of-the-cloud-report/

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

The Modern Cloud Era.

It sounds so dramatic and official, like some sort of changing of the guard akin to moving between the Jurassic and Cretaceous eras, but what does it really mean?

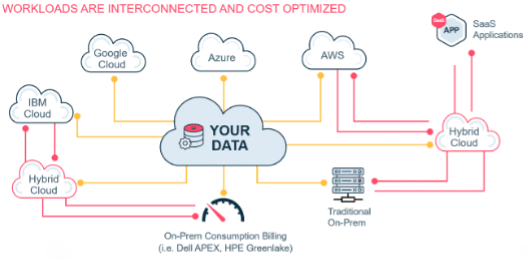
It means that the challenges and opportunities presented by the widespread adoption of the cloud have led to a world where, rather than dinosaurs, hybrid and multi cloud adoption has become the new mainstream. Almost every company on the planet is leveraging at least one kind of cloud, with many adopting formal diversification strategies to leverage hybrid and multi cloud approaches. This diversification, however, can lead to complexity which brings new challenges in the realms of cost optimization and risk mitigation.

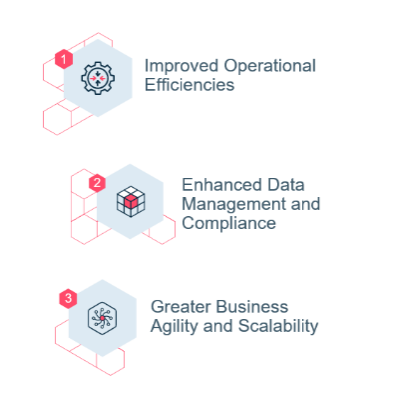
The Modern Cloud Era is about navigating the world of digital transformation, where every company and department relies on modern tools to get their jobs done. In this new world, the importance of getting data and workloads organized and centrally managed across a purposeful multi-platform strategy to deliver on business objectives while maximizing cost efficiency and risk mitigation cannot be overstated. When executed correctly, hybrid and multi cloud strategies can lead to improved operational efficiencies, enhanced data management and compliance capabilities, and greater business scalability. When done wrong it can create artificial data silos, increase the human for skilled labor, and require additional labor hours to implement and support.


We recently had the privilege of having our Vice President of Solutions Engineering, Cesar Cid de Rivera and Sr. Director of Solutions Engineering, Vincenzo Costantino give a talk on how to best navigate the waters of this new, Modern Cloud Era. Together, Cesar and Vincenzo identified three primary benefits of successfully implementing a hybrid & multi-cloud strategy, as well as some tips in how to get there.

Some of the major benefits you can hope to expect are:

  • Improved Operational Efficiencies for your process and staff execution
  • Enhanced Data Management and Compliance Capabilities
  • Achieving Greater Business Agility and Scalability 


1. Operational Efficiencies
Finding staff with a wide range of competencies in multiple native cloud interfaces can be difficult and costly. By leveraging centralized platforms that provide manageability across all clouds and workload types, you can remove this barrier and allow the platform to do the heavy lifting. Commvault Command Center is an example of a platform that provides native manageability across cloud providers and workload types with just a few clicks, saving time and money while reducing that need for expensive niche talent.

Another challenge in improving operational efficiencies is the risk of downtime, productivity loss, and potential compliance breaches resulting from unintentional human error. Policy-based automation can be a life saver in these scenarios, giving IT teams the peace of mind of a “set it and forget it” approach to critical workload movements and failover procedures. The Commvault Command Center can empower IT teams to easily create and set automation plans, either from scratch or from an existing template.

2. Enhanced Data Management and Compliance Capabilities
In a Modern Cloud Era of rapidly migrating workloads and form-factors between clouds and form-factors, data sprawl can become a major concern. That data sprawl, however, goes beyond simple storage capacity concerns and has serious implications in contributing to the unintentional creation of a larger attack surface for bad actors, as well as inflating cloud provider fees. 

Taking control of data sprawl begins with ensuring that the right data is on the right storage tiers and has been de-duped and optimized across all environments and workloads. Deduplication and compression can generate savings up to 80%, while storage tier optimization can increase that savings by another 35%. This approach can lead to downstream benefits such as reduced RTO and a smaller attack plane to be targeted by bad actors.

3. Achieving Greater Business Agility and Scalability
Lack of visibility into ALL data, no matter where it lives is the critical underpinning of any successful hybrid or multi-cloud operation. Overcoming this obstacle is critical for success and can be done utilizing a truly centralized platform for all your workload environments. The good news is that Commvault provides one unified experience for your entire data protection strategy, rapidly enhancing your operational agility in catering to outages, audits, and events, without impacting production.


For a detailed overview of this topic and additional information about how Commvault’s powerful technology suite can accomplish this and much more, please visit our website.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

There is no simple answer, mainly because you can’t boil down cloud backup solutions to just one or two primary characteristics. Here are five of the most important aspects to consider when weighing your options for a cloud backup provider.

5 Considerations When Choosing a Cloud Backup Solution

Management

Many cloud backup users tend to assume that the cloud architecture will make the backup management process easier, but it’s never a given. Aside from the actual managing of the backups (scheduling, running recovery tests, etc.), you still have to account for the planning of data usage, upgrades, patching, and security.

Simplicity and usability are key, so it’s best to avoid products with multiple management consoles or require extra hardware.

Instead, opt for a single solution backup service with an intuitive interface that provides clear visibility into all the processes you are responsible for while eliminating any guesswork and manual processes when possible.

Scale

Cloud architecture provides enterprises with a virtually limitless supply of storage and processing resources, but not every backup solution finds ways to leverage these abilities fully. And then there’s the guesswork involved with forecasting compute usage and storage demand, which can easily lead to over-provisioning or under-provisioning. The former can cause you to spend too much, while the latter can result in performance bottlenecks, gaps in data protection, and compromised recoveries.

Seek out a cloud-native, serverless backup solution that can quickly scale with increasing storage demands while removing any need to forecast future usage. Problem solved.

Compliance

Today’s compliance landscape is complicated and fluid due to the emerging location-specific laws regarding user data retention within certain jurisdictions. In simpler terms, there’s a lot at stake, and you have to be sure you’re in compliance with everything from these data privacy laws to proving the security and frequency of your backup during insurance audits.

The key to meeting compliance is three-fold: understanding your specific compliance requirements, having clear visibility into your compliance status, and rock-solid data security.

It’s best to choose a cloud backup solution that will offer a single view into your compliance status, notify you when backups are out of compliance, and provide features that can quickly and easily prove compliance in the event of an audit by pulling specific, relevant data. Your cloud backup solution should also be able to store backups outside of production environments and provide end-to-end encryption to meet compliance security requirements.

Security

Securing customer data and protecting it from threats like ransomware is paramount—but far from simple. Data security typically involves complicated decisions made across multiple cloud infrastructure resources. And you have to get all of them right. Not only do you have to meet data governance requirements related to security (such as ISO/IEC 27001, SSAE 18, HIPAA, and PCI), you also have to frequently manage and update access rights while ensuring there are no gaps anywhere.

Do not overlook this aspect! Choose a cloud backup solutions vendor with a security-first mindset that can align with your security needs, rather than one that merely offers it as an add-on. This includes the ability to store backups in an air-gap and away from primary accounts, end-to-end encryption on all backups, and the ability to change keys when desired.

Cost

The cloud is supposed to offer cost-efficiencies when it comes to backup and storage, but choosing the wrong cloud backup solution can result in the opposite. This is often due to surprise charges that you did not anticipate, such as egress, bandwidth, and storage. There’s also the issue of racking up expenses from inefficient creation, storage, and usage of snapshots. To make matters worse, many vendors offer confusing pricing models that are overly complicated, making it hard to predict what the TCO should even be.

You can avoid excessive cloud spending by choosing a cloud backup vendor with a simple, straightforward pricing model that clearly spells out the ongoing charges.

Clumio: The Superior Cloud Backup Solution

Clumio is a secure AWS cloud backup solution for enterprises that removes the complexity of software and hardware management while leveraging the cloud’s scale, economics, and elasticity.

More importantly, Clumio addresses all the aforementioned cloud backup aspects of management, scale, compliance, security, and cost by offering features such as:

  • Turnkey ransomware protection via Air-gapped storage of backups away from production accounts
  • Clear visibility and management of compliance requirements
  • End-to-end encryption of backups
  • The use of cloud-scale to support any size environment
  • Insights that provide recommendations for optimizing AWS backups
  • Cost analyzer to help reduce unnecessary cloud spend

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

https://play.vidyard.com/hFMHqJvmMJXMVRZLNiUEnR
Takeaway 1: Despite the challenges of a ransomware attack, having data stored in the cloud can help minimize the damage and keep operations running.

The panellists discussed the challenges of a ransomware attack, with Tony Kinkead noting that ransomware cybersecurity was a big part of their product offering. Paul Vries discussed the attack they experienced, saying, “We have a nonprivice environment and everything was encrypted. Everything that was the main joint was encrypted.”

He explained that they had to use indicators of compromise to determine which files were uploaded and when the attack occurred, and then restore to a safe version of the data.

Vries further noted that they had already moved a lot of users to the cloud, which helped minimize the damage and keep operations running: “A lot of the office users could remain working because their data was already in the cloud and only the main joint device were attacked.” This allowed them to focus on documenting the attack and getting ahead of it the next time.

Takeaway 2: Cybersecurity is an arms race, and organizations need to take steps to reduce their risk of attack.

Organizations need to take steps to reduce the risk of attack, as attackers only need to find one weakness to be successful. As Kinkead put it, organizations need to create a layered level of security in order to operate in a Zero Trust security model. “You want to secure every part of your infrastructure by itself,” he said, noting that “if the attacker gets access to a portion of your network, you were lucky.”

Vries agreed, noting that “it’s an arms race, and the attackers only have to find one weakness and you have to protect against all of them.”

Martijn Hoogesteger shared an example of how this can work in practice, noting that his organization had “deployed a number of decoys” to “whitelist and take out some noise” in a South American R&D facility. This allowed them to “stop the individual” who was attempting to gain access to the “crown jewels” of the organization.

Takeaway 3: The key to successful data protection is to act quickly and have a plan in place

Kinkead stressed the importance of acting fast in the data protection phase. “You have to act immediately, but you also have to follow the plan or work with external teams to come up with the right approach,” he said.

“You have to have a strategy around the immutability of your backups to be able to recover your data yourself, even though you might still be paying to prevent them from publishing some of that data.”

Remko Deenik pointed out that there was still more that could be done to protect data, while Vries noted the importance of awareness. Kinkead suggested that collaboration was key, saying, “like I also heard from Microsoft earlier, like collaboratively define those standards and there are already a lot of those standards that we worked out, like CIS and a lot of others, where we basically agree on what should be base hardening rules, what should be best practices, et cetera.”

Vries also suggested that IP addresses and exports could be used to contact systems locally, while Deenik suggested that digital forensic investigations could be used to figure out what data had been stolen. He noted that even if the data was stolen, it may still be possible to innovate and stay in business.

Discover how prepared you are for ransomware attacks by taking our quick assessment today. Evaluate your ransomware protection and recovery capabilities and get valuable insights from Commvault’s experts. Don’t leave your business vulnerable to cyber threats, act now and find out your level of ransomware preparedness! 
https://www.commvault.com/ransomware/risk-assessment

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As Co-Executive Sponsors of our Women in Technology Employee Resource Group (ERG), we’re thrilled to celebrate International Women’s Day as we honor women’s achievements, raise awareness about bias, and take action to drive gender equality. But we’re not just celebrating for one day… we’re honouring women the entire month of March, which also happens to be Women’s History Month! Our Women in Technology ERG brings together both women and allies to elevate and advance gender equality in technology and celebrate the inspiring women of Commvault who are driving our innovation and growth every day.

Today we’re amplifying our Vaulters’ voices across the world as they share stories of women who have inspired them throughout their lives.

In the coming weeks, we’ll be hosting a variety of learning opportunities and global events, in partnership with our DE&I team, to connect and inspire as we continue the conversation together about equity in action.

It’s so inspiring to see our Vaulter community come together and celebrate the importance of a diverse, equitable, and inclusive culture. We continue to work together to create a world where difference is valued and belonging is a non-negotiable both inside and outside our workplaces.  

Click here to learn more about what it’s like to work at Commvault.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

The cloud has revolutionized how businesses operate, allowing them to take advantage of its scalability and flexibility while reducing costs. However, protecting data remains a critical challenge, with 98% of businesses reporting a cloud data breach within 1.5 years1, according to IDC research – highlighting the need for organizations to take additional measures to protect their data.

Cloud service providers understand the importance of safeguarding data and applications within their environment and have developed a Shared Responsibility Model (SRM). This model requires businesses to take ownership of securing their data and applications within the cloud environment.

Cloud providers have different approaches to protecting data, which adds to the complexity, and businesses need to understand the specific details and nuances from provider to provider.

As such, customers must develop a holistic data protection strategy to ensure they have the necessary controls to protect their data even when relying on native tools included by their provider. This post will explore what this model means for customers and why it is essential to have a comprehensive data protection strategy across cloud and hybrid environments to use cloud services safely and securely.

Why are businesses increasing their adoption of cloud computing?

Cloud computing has extended the possibilities for businesses and provides many advantages. Having workloads, applications, and services running on the cloud or hybrid environments gives businesses greater flexibility and incredible scalability to accommodate growth. In addition to these valuable benefits, having a wide variety of software as a service (SaaS) applications delivered via the cloud enhances operations, optimizes resource utilization, and brings agility and efficiency to business workloads. It’s no surprise that most companies have already embraced the cloud or are actively transitioning workloads, with Gartner estimating that over 95% of new digital workloads will be deployed on cloud-native platforms by 20253.

Another key advantage that makes cloud computing so attractive is that it allows users to access data and applications quickly and easily without requiring advanced technical knowledge or expertise. This makes it easier for businesses to deploy applications and manage data in a shorter time– something that would otherwise require significant technical know-how or experience with traditional IT environments.

For these reasons, more and more companies are turning to cloud computing to manage their data and applications. The SRM ensures that both customers and providers understand what needs to be secured within the cloud environment so that companies can take full advantage of this technology safely and securely.

What is the Shared Responsibility Model?

The Shared Responsibility Model (SRM) is a cloud security strategy that states that while cloud providers are responsible for securing their service infrastructure, customers are responsible for securing their data and applications within the cloud environment. This division of accountability is designed to ensure that both parties understand what needs to be secured and how it should be done. This model allows companies to use cloud services’ scalability and flexibility while having faith in their provider’s ability to maintain a secure infrastructure.

To use cloud services safely and securely, customers must understand their role in the SRM. This means developing a holistic data protection strategy that considers their provider’s native tools and any additional security measures the customer might need to put in place. By doing so, customers can better protect their data from threats such as malicious attacks, unauthorized access, data leakage, and more.

What Are Cloud Providers Responsible For?

Cloud providers are responsible for the security and privacy of their cloud computing infrastructure, including physical security, data storage, network protection, host firewalls, access control, and software vulnerability patching. They must also ensure that their services meet legal and regulatory compliance requirements. In addition to providing all these critical components of a secure cloud environment, they are also responsible for the operational integrity of their system, ensuring its availability, scalability, fault tolerance, performance optimization, cost management, and overall reliability.

Each provider supplies a detailed description of what falls under their cover. For example, in its simplest form, AWS states explicitly that they are “responsible for protecting the infrastructure that runs all of their services in the AWS Cloud.”  

Another critical responsibility of cloud providers is to keep their customers informed of any changes or updates to their platforms or services. This includes alerting customers when a new security patch has been released or a service is no longer supported. Providers should also have a well-defined process for responding quickly and efficiently to any security incidents that arise.

Cloud providers should also have rigorous identity management practices to control who has access to the customer’s data within the cloud environment. This includes authenticating user identities with multi-factor authentication methods and regularly reviewing permissions associated with each account to ensure only authorized personnel can access sensitive information.

Finally, cloud providers should be transparent with customers about how they are protecting their data and informing them of any new changes or compliance updates that may affect their operations.

How can responsibilities differ across cloud providers?

While the Shared Responsibility Model can initially seem simple, cloud providers have different approaches to securing their customers’ data, meaning their responsibilities can vary significantly. For example, some cloud providers may have more stringent access control policies than others, meaning customers may require higher levels of authentication or authorization when accessing their accounts and data.

Other providers also offer different tools and features that customers can use to protect their data. Some might provide advanced encryption and essential management services that customers can use to ensure their information is safe in the cloud. Others may provide customers with granular auditing capabilities to track and monitor who has accessed specific files or directories within their environment.

Furthermore, the security requirements of each provider will differ based on the type of cloud services they offer. Microsoft details how the division of responsibility changes between customers and Microsoft, according to the deployment type. Infrastructure as a Service (IaaS) providers typically require customers to maintain responsibility for protecting the operating system, applications, and data stored within their virtual machines. Whereas Platform as a Service (PaaS) providers often offer more capabilities out-of-the-box, such as managed databases, web servers, and development frameworks – all of which must be configured according to the customer’s security requirements.

Finally, customers need to remember that while cloud providers are responsible for providing secure environments and tools, there are no assurances that customer data will remain private or secure if companies do not adequately implement best practices regarding access control, encryption, and other necessary measures. That said, businesses must understand what each provider is responsible for regarding data protection to choose the right partner for their needs.

Companies should carefully review each Cloud Provider’s responsibilities to know precisely what they are responsible for versus their service provider when protecting their data from malicious actors, misconfigurations and meeting compliance requirements.

What Are Customers Responsible For?

Despite cloud data being subject to the same responsibilities as any on-premise computing system, many companies remain unaware of this fact. The Shared Responsibility Model outlines that customers are responsible for securing the data and applications within a cloud environment – yet research has found that only 39% of organizations are confident in their ability to do so effectively4.

Ensuring these responsibilities are met requires implementing additional security measures such as backup and recovery, encryption, identity and access management, and monitoring.

Key Data Protection Considerations

  •  A robust data protection strategy for all workloads is essential for the total visibility and security of hybrid cloud environments. With regular backups of all workloads, organizations can be better prepared to respond in case of data loss due to either a cybersecurity event or a natural disaster. Additionally, having data readily accessible enables IT teams to restore any lost workloads quickly and efficiently with minimal downtime.
  • Encryption is critical when protecting sensitive data, such as financial or personal information, from unauthorized access attempts from external sources and internal personnel who could misuse customer information. Still, only 17% of businesses are encrypting at least half of the sensitive data they store in the cloud5. Customers should ensure they have robust encryption protocols across their environment and regularly re-inspect and apply the latest available options.
  • Identity and Access Management (IAM) is also essential for cloud service customers. Implementing an IAM system will enable customers to control who has access to their cloud environment on a user level, allowing only authorized personnel to view or modify data. By utilizing multi-factor authentication, customers can enjoy better protection from breaches and limit the potential damage a malicious actor could cause. Additionally, customers should ensure that their authentication methods meet the standards set by their industry’s governing body or regulatory agencies. Furthermore, companies should have a Separation of Duty (SOD) policy to further protect cloud data from misuse by any single account holder.
  • Monitoring and managing cloud and hybrid environments is a complex task, as cloud-based data resources constantly change. Therefore, using a monitoring and observability service is essential for administrators to ensure the security and proper management of cloud data. Cloud-native tools such as Amazon CloudWatch and Azure Monitor enable real-time monitoring and visibility into cloud, hybrid, and on-premises applications and infrastructure resources. The provision of data analysis not only helps administrators gain actionable insights from cloud data but also access crucial information about the performance of their cloud environment.

By following the best practices regarding security protocols, businesses can ensure they have the necessary controls to protect their data while taking full advantage of the benefits offered by cloud computing services. Ultimately, it’s up to each company’s circumstances when deciding what specific measures must be taken to keep sensitive information safe from external threats or unauthorized access.

Why You Need a Holistic Data Protection Strategy

With cloud related threats topping the list of cyber security concerns for UK senior executives and 90% saying they have experienced a greater exposure to cyber risks due to increased digitization in the last two years6, customers should continuously develop and maintain a holistic data protection strategy to ensure their data is secure, even when relying on the cloud provider’s native tools. A holistic approach involves understanding the full scope of data security requirements across multiple clouds and implementing appropriate technical, operational, and physical controls.

One of the most important reasons for this type of strategy is to identify and address any potential risks or vulnerabilities that could occur due to the increased use of cloud services. While cloud providers may have robust security measures in place, only 52% of CISOs are confident they are able to fully enforce a consistent security policy across all applications in the cloud7, meaning any additional security measures taken by businesses can provide extra layers of protection against malicious attacks, unauthorized access, data leakage, and other cyber threats.

In addition to helping protect sensitive data from potential threats, a holistic data protection strategy can also help businesses comply with various industry regulations such as HIPAA or GDPR. By having an adequate data protection plan in place, companies can better ensure they meet all relevant compliance standards while still taking advantage of all the benefits of using cloud-based services.

Encryption and backup are vital considerations customers should keep in mind to ensure data protection.  To achieve this, customers should also consider investing in third-party vendors like Commvault that provide additional layers of security for their cloud environments to complement native tools, ensure they meet their responsibilities, and effectively protect their data.

Microsoft echoes this statement in their Services Agreement, stating, all online services suffer occasional disruptions and outages, and Microsoft is not liable for any disruption or loss you may suffer as a result. and we recommend that you regularly backup Your Content and Data that you store on the Services or store using Third-Party Apps and Services.

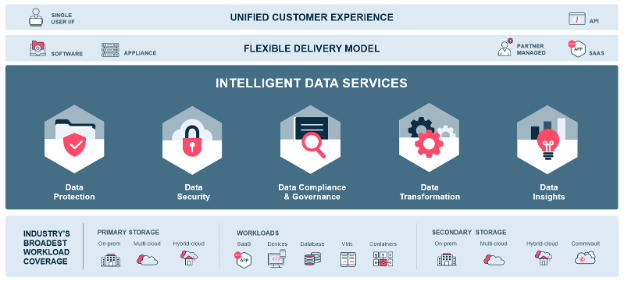
Commvault goes beyond backup by providing a simple and unified Data Protection Platform that spans all customer data – regardless of whether legacy or modern workloads live on-premises, in the cloud, or spread across a hybrid environment. Our knowledge of cloud options and deep integrations with a broad range of cloud providers offers the integration and automation possibilities to meet your unique data management and protection requirements.

Finally, customer organizations need to have clear ownership over their data so that everyone involved knows who is responsible for what type of information and how it should be handled securely throughout its entire lifecycle. This includes identifying who has access rights over specific sets of data as well as when those rights must be revoked (e.g., after an employee leaves the organization).

By having a holistic data protection strategy in place alongside their provider’s native tools, customers can better protect their information from external threats while also ensuring their operations meet regulatory requirements as necessary.

Companies need to invest time into creating such strategies to safely take full advantage of the benefits offered by cloud computing without putting themselves at risk for costly breaches or fines due to non-compliance issues down the line.

Final Thoughts on Cloud Data Protection Strategies

With cyber-attacks increasing and nearly half of all data breaches happening in the cloud8, organizations must take adequate measures to protect their data and environment. The Shared Responsibility Model is a crucial cloud security strategy that emphasizes an effective combination of customer responsibility in developing proactive defense plans with third-party solutions for additional layers of protection when using cloud services. To successfully implement this approach, customers must understand how responsibilities differ across different providers to minimize potential risks while taking full advantage of the services offered by these platforms.

To learn more about how we protect your Cloud Environments, visit our digital transformation and SaaS-Delivered Solution pages. You can also discover more about our latest release on our what’s new page.

References

1. IDC survey, commissioned by Ermetic. – 3. Gartner IT Symposium/Xpo 2021 – 4. CSA Understanding Cloud Data Security and Priorities 2022 – 5. 2021 Thales Global Cloud Security Study – 6. PWC Cyber Security Outlook 2023 – 7. BlueFort Security 2022 CISO survey – Help net security – 8. IBM and the Ponemon Institute’s 2021 Cost of a Data Breach

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Here at Commvault, we celebrated Black History Month with a variety of experiences, virtual events, and conversations hosted by our DE&I team and Multi-Culture Employee Resource Group (ERG).

This year, the theme of Black History Month 2023 was Resistance, in recognition of those who have fought against oppression, and is a time when we remember the global heroes of Black history, honor their fight by condemning racism, and champion change not only during Black History Month but every day of the year. As a global community, our goal was to explore these concepts through our programming this month under the theme “equity in action.”

As a Commvault community, we started our celebrations by supporting and joining a virtual cultural celebration with BLK House Virtual to experience joy through Black music as a reminder that we continue connections and community-building.

Later in the month, we hosted our Black History keynote event with special guest Arika Pierce, JD. With over 15 years of experience in corporate leadership, Arika is the CEO and founder of Piercing Strategies and works with organizations to develop their professionals by ensuring they have the right tools and resources to excel in their organizations and grow and thrive as inclusive leaders. Throughout the interactive session, Arika shared challenges and strategies for motivating leaders to engage in DE&I work, actionable ways leaders can prioritize diversity, equity, and inclusion, and evidence-based DE&I practices to improve workplace culture.

To close out the month, we hosted a Courageous Conversation with our newest Board Member, Shane Sanders, and our Chief People Officer, Martha Delehanty, where they discussed his career journey and perspectives on how the theme of “equity in action” has impacted him as a Black man. Shane also shared career advice, highlights, and challenges he has experienced throughout his personal and professional life. He also shared more on the social cost of not embracing diversity and inclusion in the workplace.


Although Black History Month concludes today, we are committed to continuing these conversations about diversity, equity, and inclusion here at Commvault and are excited about the celebrations we have planned throughout the year to further our efforts.

To learn more about our DE&I efforts at Commvault, click here.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As Senior Product Marketing Manager at Metallic, I was honored to recently have been awarded a CEO Living Our Values Award by our leadership team for the Metallic Threatwise launch. With ThreatWise, Commvault moved into uncharted territory as the only data protection platform to offer fully-integrated deception technology, capable of surfacing unknown and zero-day cyber threats before they reach your data – and it’s time to recover. Bringing this next-generation service to market was a significant milestone in supporting how our customers combat and respond to cyber threats, and I was fortunate to be a part of the team who helped deliver these capabilities.

Winning this award made me reflect on my time at Commvault and how it has shaped my professional journey. I joined Commvault in 2020 and was part of the first wave of employees who started during the pandemic. Growing up in New Jersey, and having spent the majority of my career in the tech industry, I was very familiar with the Commvault name – not only for it’s reputation as a perennial leader in the data protection space but also for its reputation as a great place to work.

As a Product Marketing Manager, I live in between many different worlds, driving and supporting launch activities for our Metallic services Commvault’s portfolio of SaaS-delivered data protection solutions. Working in this cross-functional capacity has challenged me but also presented the opportunity to work alongside many different areas of our business. From Product and Engineering to Operations and Customer Success (and everything in between), I partner with various stakeholders daily to achieve one common mission: deliver the best data protection services possible. Working as a collective unit to deliver against this promise is what drives me, and my colleagues, every day. On the customer front, this high level of collaboration has paid significant dividends as we rapidly innovate to bring best-in-class products to market for businesses of all sizes. On the professional front, it has allowed me to build new connections, expand my expertise outside of the Product Marketing domain, and further hone and mature my skillset.

When first arriving to the Metallic team, we were just getting our feet underneath us. Now, just three short years in, the trajectory and the growth have been remarkable. What started as an incubation project within Commvault, Metallic has achieved hyper-growth – more than tripling our portfolio offerings, garnering around 3,000 customers, and introducing new innovations that disrupt and advance the data protection market. I know everyone in Commvault has worked so hard to make this happen – it’s the teamwork, the maniacal focus on helping our customers, and the drive of our employees that have allowed us to reach this massive achievement.

Our values – we connect, we inspire, we care, and we deliver – continue to move our business forward. The past few years have been a wild, exciting ride, and I can’t wait for what the future holds for Commvault and Metallic.   

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

This codification of privacy is transforming how businesses are expected to operate. There is no more question of what happens when a business doesn’t invest in a cyber program and who’s responsible. Let’s take a quick look at what will shape this year.

US Privacy Regulations Take Action: CCPA, NYDFS, and SEC Update Requirements

CCPA may be amended. Currently the CCPA has an open request for comment on how audits fit with CCPA. In addition, we will start seeing rulings in cases around CCPA showing what we can expect for the reality of losses from not complying. For those who want to keep track with us, Perkins Coie has a great tracker.

NYDFS will likely be amended. Industry comments are under review. Once DFS makes its recommendations it will move through the legislation process. Notable takes:

    • “The CISO and the highest-ranking officer of the covered entities are both required to sign a certificate of compliance, and notice of compliance must be delivered annually to the NYDFS.” – Morgan Lewis.
    • This is more than a privacy law, this includes business resiliency, and secure operations

The SEC wants their new rules in place ASAP. This includes provisions for Cyber Security reporting requirements alongside considering rules requiring adoption of standard practices. As with all federal rules, this one may take some time. Other provisions, notably around carbon footprint reporting, seem to be causing friction. We will see if the SEC makes their timeline.

$100 Million penalty for BIPA violations. In 2022, we saw cases relating to the Louisiana BIPA come to a close with significant penalties being doled out. The rubber is meeting the road, and liabilities are a reality. Read more at Data Protection Report.

Why Executive Leaders Must Prioritize Cybersecurity Expertise

With this strong legislative push, real world liabilities are here. Executive leaders can no longer ignore the advice of security teams. The reality is most businesses are not ready. A quick snip from Forbes illustrates this perfectly:

“Our analysis showed that only 51% of Fortune 100 companies have a director on their boards with relevant cybersecurity experience. The situation in the Fortune 200 and 500 is more concerning: only 9% have cyber-savvy directors. Worse still are the companies in the Russell 3000 smaller than those in the Fortune 500: only 8% have cyber directors. There is a total shortage of 2,724 directors with cybersecurity expertise across all Russell 3000 companies.” –Forbes

To be successful in filling these positions, security leaders will need to have an opinion on what’s changing from a legal perspective, how that impacts business strategy, and how the business creates opportunity in markets with changing regulations.

Succinctly, CISOs need to be part of every strategic board level conversation. An active CISO can actually be a competitive advantage. These active leaders will understand the business data, how to use it for market advantages, and meet new regulatory challenges. Companies that can stay ahead of the changing regulatory environment will realize greater return. Companies that view compliance as a checkbox will fall behind.

Adherence to compliance regulations is critical to your business’s operations, but it doesn’t have to consume an outsized portion of your resources. Let Clumio help automate compliance and simplify management while reducing your data protection costs. Contact us for a customized consultation.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

The past year has been amazing – our data protection portfolio has won many accolades of technology leadership from industry analysts like Gartner, Forrester and GigaOm. These wins are no doubt driven by our relentless passion to protect our customers’ data in a difficult world and our fundamental belief that continuous customer collaboration is key to pragmatic innovation.

The next chapter of our 26-year journey of customer-driven innovation is now here – we are excited to announce the General Availability of Commvault Platform Release 2023! Commvault PR 2023 introduces several new features and additions to strengthen our customers’ security posture, deepen our rich integration with all major hyperscalers and introduce more smart savings through operational efficiencies.
Hundreds of customers have already benefited from these new capabilities during the Technology Preview phase, that started on December 15, 2022.

Harnessing the power of multi-cloud

What differentiates our approach to the ecosystem – and yes, we continue to support the broadest ecosystem when it comes to data protection – is how our integrations are seamlessly built-in and not just clumsily bolted on for a quick mention. Deeper the integrations, greater the synergies enjoyed by our customers.

Commvault PR 2023 carries new deep integrations to make it easier for our customers to protect their data across Microsoft Azure, AWS Cloud, Google Cloud Platform and Oracle Cloud Infrastructure.

Take, for instance, our new integration with Microsoft Azure Restore Points. We worked closely with Microsoft to be the first data protection platform to support Azure Restore Points. While Azure has had incremental snapshot capabilities, this new integration allows for application consistency across disks, while reducing costs with the option to use more cost-efficient storage tiers for backups. Commvault PR 2023 also introduces integration with Amazon FSx for NetApp which brings the same on-premises NetApp ONTAP policy-based protection to AWS. The new release also introduces support for Oracle Cloud Infrastructure (OCI) infrequent access & combined storage tiers to help reduce costs for protecting your cloud data.

Enhancing data security

Our trusted approach to data protection is shaped by the fundamental customer direction that data security is an integral and inseparable component of data protection. Building on our robust multi-layered ransomware detection, protection and recovery framework, Commvault PR 2023 introduces new integrations to drive data protection insights into the broader security ecosystem.

An important aspect of data protection is to leverage data awareness to proactively alert IT teams when threats arise. Commvault PR 2023 introduces a new Security Information and Event Management (SIEM) connector that makes it easy to feed alerts, events, and audit data to other platforms through webhooks APIs or even Syslog. Leveraging standard protocols ensures we can work with virtually any SIEM or event management system giving security teams better visibility to anomalies and threats in their data. 

Driving smart savings

With the uncertainty of a global recession looming, customers in every industry are looking to optimize costs in their budgets to make up for the increased spending for security and mission-critical areas. We are continuing to help provide options to lower the cost for data

New capabilities to use single region snapshots vs. multi-region snapshots for GCP can save 30% of that cost to backup resources. Sometimes improving cost is as simple as reducing the time it takes to protect applications.

Our optimizations for Hadoop, leveraging snapdiff, can take what was hours long backup scans to just minutes thanks to the enhancements in how we scan for changed blocks.

These are just a few of the amazing features we have in Platform Release 2023. You can learn about more of the latest features in our What’s New page for Platform Releases. Connect with our product management team and others in our communities for all the latest news and release information. 

Join us live on March 8th, 2023 at our Platform Release 2023 customer webinar.  Register here

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago