Skip to content

Data protection and cloud migration and recovery planning, oh my! Experience it all with Commvault at Oracle CloudWorld, Booth #23, running September 19-21 in Las Vegas.

We’re only a few weeks away from the show and boy do we have a packed agenda for customers, partners, and show attendees!

First up, our speaking sessions and tutorials. Get these on your calendar before it’s too late!

  • Tues, Sept 19 at 5:00 pm PDT – OCI Data Protection: Building Cyber Response Strategies to Lower Risk—and TCO
    • Decrease Risks and Costs! Learn how Commvault and Oracle are redefining modern data protection for Oracle Cloud Infrastructure (OCI).
  • Wed, Sept 20 at 1:00 pm PDT – Your VMware Estate Migration: Maintain Control and Maximize Security
    • It’s as easy as 1-2-3! Follow this step-by-step tutorial to seamlessly deploy and migrate VMware workloads to OCVS (Oracle Cloud VMware Solution), using Commvault data protection.
  • Wed, Sept 20 at 3:55 pm PDT – Partners: The Ransomware Playbook – why Firewalls and Backups are not Enough
    • Attention partners, now’s the time to walk away a hero and help your customers defeat their biggest threat – ransomware.
  • Thurs, Sept 21 at 8:30 am PDT – OCI and Commvault Partner to Secure, Protect, Recover Your Hybrid Environment
    • Want to know the secret when it comes to cost savings? Simplifying management, optimizing cloud strategies, reducing security risks, and improving business continuity with Commvault.
  • Thurs, Sept 21 at 1:05 pm PDT – How Commvault Helps Redefine Data Protection for Oracle Partners and Customers
    • Partners, this one’s for you! Discover ways to exceed your customers’ expectations while helping them secure, defend, and recover their most precious resource, their data.

Next, be sure to stop by the Commvault booth (Booth #23) where you’ll experience the best in data protection for the widest breadth of workloads, first-hand. We’re here to help accelerate your OCI journey by delivering superior price-performance, built-in enhanced security, and simplified recovery and management.

  • Are you a planner? No need to rush around during the show. Schedule a meeting in advance and we’ll hold your spot.
  • Do you prefer a more spontaneous approach? We’ll be hosting brief 10-minute sessions throughout the show days. This is your opportunity to quickly learn the ins and outs of simplifying your backup strategy….and you may walk away with some pretty cool prizes.
  • How about testing the technology for yourself? We’ve got you covered with demos showcasing fast backup and recovery of cloud and on-premises workloads, and Metallic Recovery Reserve on OCI for air-gapped protection. 

Are you convinced yet that Commvault Booth #23 is the place to be? We’ll see you in Las Vegas!

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

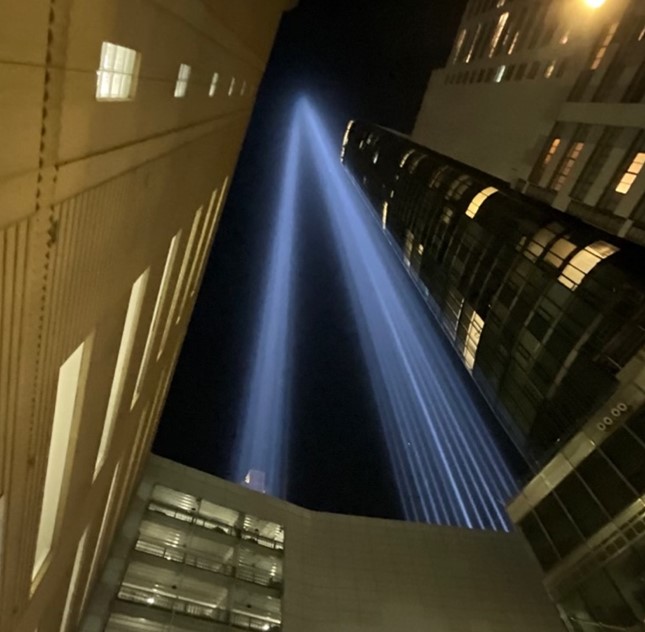
Monday, September 11th is Patriot Day and a National Day of Service and Remembrance in the United States as we commemorate the 22nd anniversary of the September 11th (9/11) terrorist attacks.  

September 11, 2001 was a loss felt worldwide. Today, we remember those who lost their lives on that day, thank the brave first responders who put their lives on the line and honor the sacrifices made to protect our freedom.  

As I reflect on that day, how our communities came together always stands out to me. We put aside our divisions and united in caring for one another, supporting one another, and projecting hope; I tend to describe this as compassion. Those efforts resonate with me today and each time I step out of my front door into the daily complexities surrounding us all. Each interaction where we can inject more compassion into the community helps. 

As a U.S. Navy veteran, I am proud to be the executive sponsor of our VALOR (Veterans) Employee Resource Group (ERG) here at Commvault. To honor the anniversary of 9/11, our VALOR ERG held our annual Commvault Climbs challenge, where Vaulters around the world are challenged to climb as many as 104 flights of stairs to honor the brave firefighters and first responders who climbed the stairs of the Twin Towers of the World Trade Center to save the lives of those who were trapped. Each year, I’m reminded of the incredible support across our company as we live our value of caring.   

Let’s take the time today to remember those who lost their lives on 9/11, reflect on the bravery of the first responders in those moments, and honor those who volunteered to serve their country in response to the tragedy. 

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Cyber threats continue to evolve and become more persistent. Worldwide spending on security solutions and services is expected to reach nearly $300 billion in 20261 – a 37% increase from current spending, indicating the increasing threat level. Surprisingly, despite greater awareness and investment, 83% of organizations have experienced more than one data breach in their lifetime2. These numbers highlight the crucial need for recovery readiness, with data security a top concern as cloud storage becomes the popular option for offsite backups.

The need for immutability

Immutability is defined as “the ability of any data to be maintained in a non-fungible state for a specific duration of time”. Data immutability can be attained via various methods working in conjunction with each other.  An immutable architecture, then, is a model in which no updates, security patches, or configuration changes happen “in-place” on production systems. If any change is needed, a new version of the architecture is built and deployed into production.  Immutability protects within, as well as outside of the backup solution.

Organizations need an immutable architecture to ensure their data is safe and secure and, more importantly, ready whenever they need to restore it. Immutability is a proven technique used to reduce cyber-attacks on backup data and ensure that backup copies aren’t changed in any way.

The best indicator that you have a reliable backup solution is your ability to recover data quickly. This comes partly from proper planning and architecting your backup and recovery solution. However, this can be a difficult challenge when your data is up against so much opposition. In the past, hardware failures, natural disasters, and human error were likely “top of mind” outage threats. Today, ransomware and insider threats have taken over as top concerns. It’s apparent that planning and architecture design is not enough; today’s backup and recovery solution must be immutable, so you have peace of mind that your data is safe.

Mutable vs. Immutable

There is an essential distinction between mutable and immutable infrastructure when protecting valuable data. Traditional mutable infrastructure is more flexible and allows for updates and integrations to be made quickly, but this can also make it easier for cybercriminals to access and manipulate data.

These bad actors often target businesses through data breaches, which can have severe consequences such as reputational damage, loss of revenue, and legal problems. This is where an immutable architecture comes in, offering a more secure and tamper-proof solution to protect data from internal and external threats.

Immutability for regulatory compliance

Immutable storage is essential for any organization to protect its business-critical or private data. This is especially important for industries like healthcare, finance, and law, which have strict legal and regulatory requirements to safeguard sensitive data from unauthorized access or tampering. Immutable storage helps organizations comply with requirements like those put forth by the SEC, CFTC, and FINRA related to the recording, storage and retention of electronic records and facilitates easy recovery in case of data loss or corruption.

Commvault Cloud is immutable by default

With every environment having its own mix of infrastructure, securing backup data against random unauthorized changes can seem challenging. Therefore, Commvault has taken an agnostic approach to immutability. Leveraging a hardened, multi-layered approach to data protection, we provide robust controls that prevent various types of threats to backup data and ensure copies are highly recoverable from accidental deletion or malicious attack. Natively, all backup data is protected at the storage level. Backup copies and operations live in a virtually air-gapped location, in an isolated security domain, decoupled from source environments. Retention locks can also be applied to prevent unwarranted modifications to data retention policies.

With Commvault Cloud, you do not need special hardware or cloud storage accounts to lock backup data against ransomware threats. If you happen to have Write-Once, Read Many (WORM), object lock, or snapshot supported hardware (which Commvault fully supports), you can still use Commvault’s built-in locking capabilities to complement and layer on top of existing security controls. Having the ability to layer security controls across different infrastructure types is what places Commvault’s immutable solution ahead of the competition.

Multi-factor authentication, AES 256 bit at-rest encryption, firewalls, and other zero-trust access controls block internal and external movement of data by unauthorized parties. All security protocols employed adhere to security best practices and are based upon NIST 800-53, SOC2 type II, and ISO27001:2013 guidelines and compliance requirements.

With built-in zero-trust security protocols, Commvault Cloud meets the most stringent confidentiality, integrity, and availability standards for government agencies and business, alike.

Commvault Cloud’s immutable infrastructure architecture

Commvault’s machine learning platform extends immutable protection capabilities by providing a proactive platform for detecting and responding to threats accordingly. We employ a multi-layered approach to protect against various threat vectors and ensure data is safe and include storage locking to combat ransomware and Zero trust AAA controls up and down the backup and recovery stack to provide comprehensive protection. Isolation and air gapping utilizes TLS encrypted network topologies and infrastructure is hardened to reduce the attack surface.

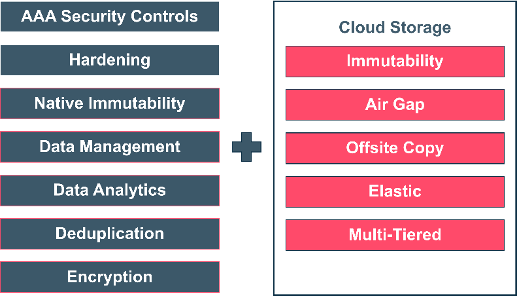
At a high level, the Commvault platform includes these seven layers combined with immutable cloud storage:

Cloud storage provides enhanced options for defending, securing, and restoring your data. Immutable by default, it all adds up to the most flexible data protection you can deploy anywhere and at scale for any workload.

Your Protection, Your Way: Immutability for Software and SaaS

Commvault Grid makes implementing an immutable architecture as an integrated appliance or reference design for an all-in-one solution easier. It delivers comprehensive data management for all workloads from a single, extensible platform. Commvault Cloud employs a multi-layered approach to protect against various threat vectors and ensure data is safe. Commvault’s immutable architecture consists of:

  • Software (Compliance Lock)
    • Attempt: Backup admin tries to reduce retention, delete backup job, policy, or library accidentally
    • Action: Denied by Compliance Lock
  • Operating System (Access controls)
    • Attempt: Authorized user tries to encrypt, move, or delete files or reformat a disk
    • Action: OS blocks users and/or ransomware attacks through access controls
  • File System (Immutability at the storage layer)
    • Attempt: Authorized or malicious user tries to modify or encrypt protected backup data
    • Action: Immutable file system prevents backup data from being modified/encrypted

Commvault AirGap is a fully managed cloud storage target for the Commvault SaaS hybrid cloud portfolio, as well as Backup and Recovery and Commvault Grid. Cloud adoption is accelerated with optimized storage options and air gapped copies of data to ensure ransomware recovery.

Commvault AirGap is optimized cloud data protection, offering:

  • Short or long-term cloud storage, from one vendor, managed in one interface
  • Controlled costs via optimized storage
  • Unified naming for all cloud storage

With Commvault AirGap, you can have both primary and secondary backup copies for all your workloads in the following storage tiers:

  • Azure Hot
  • Azure Cool
  • OCI Standard (Commvault Cloud SaaS only)
  • OCI Infrequent Access (Commvault Cloud SaaS only)

And while all the above solutions can elevate your cyber resilience strategy, it also provides significant cost savings. Commvault Cloud’s air-gapping, immutability, and more importantly, ability to effectively restore an environment can have a $1.06 million ransomware benefit over the 3-year analysis.3

Conclusion

Data threats are becoming increasingly sophisticated, and there’s no getting around the fact that backup and recovery platforms today must offer greater protection against cyber threats. Commvault solves this problem with an immutable architecture that provides complete data security and fast recovery of any workload, no matter where it lives. Our layered approach reduces risk while helping organizations meet compliance requirements without sacrificing performance.

Now is the time to ask the tough questions regarding your data security provider so you can be fully confident that your data is safe, secure, and compliant. Start exploring our immutable architecture today and discover how staying ahead of potential threats with the right solution has never been easier or more secure.


References

1. IDC Worldwide Security Spending Guide – 2. IBM Cost of a Data Breach Report 2022 – 3. Analyzing the Economic Benefits of Data Protection with Commvault on Microsoft Azure

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

In an organization’s ongoing battle against ransomware threats, safeguarding Personally Identifiable Information (PII) – the data encompassing sensitive personal information whose compromise can lead to severe legal, financial, and reputational consequences – is a critical imperative.  As ransomware attacks continue to evolve in sophistication, safeguarding PII data has become paramount for effective defense strategies.

  • Mitigating Legal and Financial Risks: After a ransomware attack, the unveiling of PII data can expose organizations to significant legal and financial risks. Data breaches may result in hefty fines, regulatory penalties, and class-action lawsuits. To reduce vulnerability to such liabilities, organizations must proactively discover and secure PII data, demonstrating their commitment to data protection and privacy.
  • Thwarting Data Exfiltration: Ransomware attackers frequently threaten to publish or sell stolen data to coerce victims into paying ransoms. Identifying and securing PII data is required to pinpoint critical assets that attackers might target for exfiltration. Robust access controls, encryption measures, and data loss prevention protocols act as strong deterrents against unauthorized extraction.
  • Tailored Protection by Prioritizing PII Data: Recognizing that not all data is of equal value, organizations should adopt a strategic approach to protection. PII data, given its high susceptibility to identity theft and fraud, demands special attention. Through meticulous discovery and categorization, organizations can allocate resources to fortify their most sensitive and valuable data, thereby enhancing the efficacy of overall cybersecurity measures.

Recognizing the need for strong protection of PII data is part one. Identifying a solution to accomplish this task is the second piece of the puzzle.

Commvault Risk Analysis: AI to the Rescue

Commvault Risk Analysis is a comprehensive solution aiding organizations in discovering, evaluating, overseeing, and implementing measures to minimize data-related risks. By gaining visibility into these, organizations can easily identify and categorize sensitive data to help mitigate potential data breaches and foster efficient cross-functional collaboration. Commvault Risk Analysis forms the backbone of smart, proactive data management strategies designed to reduce risks and costs.

Sensitive data detection relies heavily on AI methods that can process vast amounts of data quickly and accurately, and Commvault Risk Analysis is modernized with such capabilities. These AI-driven techniques significantly enhance the accuracy and efficiency of identifying sensitive information within large and diverse datasets.

  • Comprehensive PII Management: Risk Analysis Entity Manager equips organizations with a versatile toolset for managing various PII types identified through content analysis. This feature includes predefined PII entities and the flexibility to create custom entities to finetune the model for specific datasets and datatypes. These entities encompass specific PII categories, allowing for sensitivity level adjustments and associated keywords. This system enables configuration for default and customized entity types, forming the foundation for effective PII management.
  • AI-Powered Contextual Learning for Data Classification: Leveraging AI-driven contextual learning, Commvault Risk Analysis can achieve precise data classification. Unlike traditional methods, AI-driven approaches use machine learning algorithms to understand the context and adapt to evolving data patterns. This reduces false positives and false negatives by considering surrounding text, metadata, and contextual cues. These systems efficiently identify sensitive data and automate classification, bolstering data security, compliance, and governance.
  • Empowering Data Classification Through Training Models: Training classification models with custom datasets is essential for accurate identification of document types. This involves uploading representative files that mirror desired categories, allowing the model to build a strong foundation. Continuous refinement is possible by adding additional documents that finetune the classification model, leading to more accurate sensitive data detection.
  • Azure Cognitive Services for Data Classification Insights: Integrating Azure Cognitive Services with Commvault Risk Analysis further enhances the recognition of diverse data types within sensitive datasets. AI-driven algorithms can identify intricate patterns defining various data categories and business domains. Deep learning and text analytics capabilities of Azure Cognitive Services boost data classification accuracy, efficiency, and compliance even in complex unstructured data. The synergy between Azure’s Cognitive Services and sensitive data governance capabilities of Risk Analysis offers a cohesive and integrated experience, that not only facilitates more accurate data governance but also a modern AI-enabled deep learning approach that continuously adapts as datasets evolve.

In today’s digital landscape fraught with ransomware dangers, safeguarding PII data is not merely a necessity but a responsibility. By embracing AI-driven intelligent technologies, and a commitment to a robust data protection wrapper around sensitive data, organizations can fortify their defenses against ransomware attacks and ensure the security and privacy of the sensitive data they store.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Fans of science fiction know Artificial Intelligence (AI) is a recurring theme – and has been for quite some time. Movies, books and even video games embrace it as an advanced technology that powers robots, cyborgs, spaceships – you name it. And core to the mythos of AI is that it thinks in a manner indistinguishable from that of a human, while operating with the speed and intelligence of a computer.

We’re not there yet; as much as I’d like my own version of Tony Stark’s Mark V armor, I’ll have to settle for being able to ask Alexa facts about Chuck Norris. But we are making swift progress – I recently learned a popular online tech publication had been using AI to generate articles for months – and was none the wiser, thanks to ChatGPT and other Large Language Models (LLMs).  

LLMs promise to revolutionize how we interact personally and professionally. We’re seeing incredible interest and funding being poured into their development – and it’s just beginning. In today’s business world, AI is being viewed as the key to unlock technological advancement, competitive advantage, and in turn, profitability.

It’s why tech giants like Microsoft, Meta, and Google each referenced AI almost 50 times in their recent earnings calls. As a result, you may be asking yourself “What if AI could help my business…”

  • Make better decisions?
  • Operate more efficiently?
  • Save costs?
  • Enhance customer relationships?

The good news is that it can absolutely do all the above.

The bad news? AI isn’t free. Quite the opposite, in fact.

The Cost of AI

AI, like anything in its infancy, requires learning. So how does one go about teaching ChatGPT and other LLMs how to work? Simply put, money. Tony Stark kind of money.

It’s been reported that ChatGPT utilized over 10,000 GPUs (Graphic Processing Units) to train it. (Now we know where all the graphics cards went for the last two years.) And the most powerful GPU on the planet will run you $30,000. Which means ChatGPT had an awfully expensive childhood. But that’s not all. It’s estimated that ChatGPT costs upwards of $700,000 per day to operate. Why? Well…

AI Requires Cloud Infrastructure

If generating AI were as simple as harnessing the pixel pushing power of Nvidia or AMD, we would see it proliferate at an even higher rate than it currently is. But to deliver AI, you need additional hardware and infrastructure. That means servers – many, many servers. And not coincidentally, today’s enterprises need the same to fulfill their data protection needs. And where do they turn to do that? The cloud.

That’s right – the same infrastructure that defends, protects, and secures your data is now being used to make AI available to the masses. It drives LLMs, machine learning, and automation, just to name a few. Those use cases are going to exponentially increase because AI makes great use of raw computing power and scalability. And because the more things change, the more they stay the same – in this instance, we’re talking about reducing the cost of AI to ensure a healthy bottom line for your business.

Extra ROI from Your Data Protection Platform

The natural progression of innovation and technical economics involves experimenting to find a way to optimize a use case in hardware (silicon processors)  and then shift it into software (ChatGPT)  so that everyone can benefit from it. Using that logic, you’re probably already in the cloud. More likely, multiple clouds. To take advantage of this paradigm, you need to implement cost-effective solutions that ensure the integrity of your dataset.

One way to do so is by using Data Protection as a Service (DPaaS) to reduce your operational spend on cloud Infrastructure to help pay for those growing AI bills. You’re already optimizing your business in myriad ways; this methodology is a natural fit. It’s a virtuous cycle: grow your business by utilizing existing resources to reduce costs, which are then invested back into the business.

Driving Down Today’s TCO is Just the Start

Where DPaaS is concerned, enterprises are rightfully focused on security first, with TCO (Total Cost of Ownership) being a close second. TCO is quantitative in nature, so it can be difficult to know how to evaluate vendor claims. At the end of the day, these are the current table stakes:

  • Deduplication and data tiering: Maximize storage efficiencies and control cloud costs.
  • Cloud-native storage: Storage costs should always decrease when utilizing a DPaaS vendor alongside your cloud provider.
  • Proactive Ransomware Monitoring and Alerting: This also includes end to end data encryption and data immutability.
  • Multi-Cloud Data Protection: Companies should use the right cloud technology that suits their business needs. And vendors should offer DPaaS solutions that support all of them.
  •  Broad Spectrum of Workloads: Companies use a mix of SaaS, IaaS, and on-premises resources – your DPaaS solution needs to support all of it.
  • Robust reporting: Includes compliance analytics to stay current and proactively address future requests on demand.

If you can check all of the above boxes, you’re well on your way to driving down the cost of your data protection investment. Now it’s time to start thinking about what’s next and where to reinvest those savings.

The Future of Data Protection

AI-enhanced data protection will offer continuous innovation, based on machine learning and other advancements that are driven by the needs of modern organizations. And because we are at the intersection of data protection not only in the cloud, but also on-premises, we need a unique perspective on what that could look like. What if you could:

  • Automate tasks to drive better efficiencies?
  • Continuously analyze data and find root cause for problems instantly?
  • Be more efficient with less resources?
  • Utilize your data to make better decisions?
  • Receive high-fidelity security alerts?
  • Use data-driven insights to automatically understand customer or employee needs, and generate the right result, at the right time?

Soon, these will be the new table stakes. Your data protection, whether you know it or not, is a direct on-ramp for your ability to harness AI, affordably.

It’s YOUR data. What will you do with it?

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

At Commvault, we believe that investing in our people begins with the next generation of leaders.

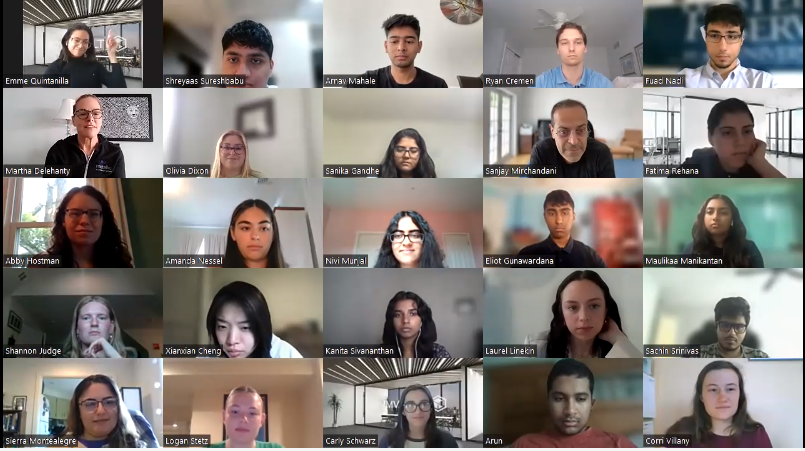
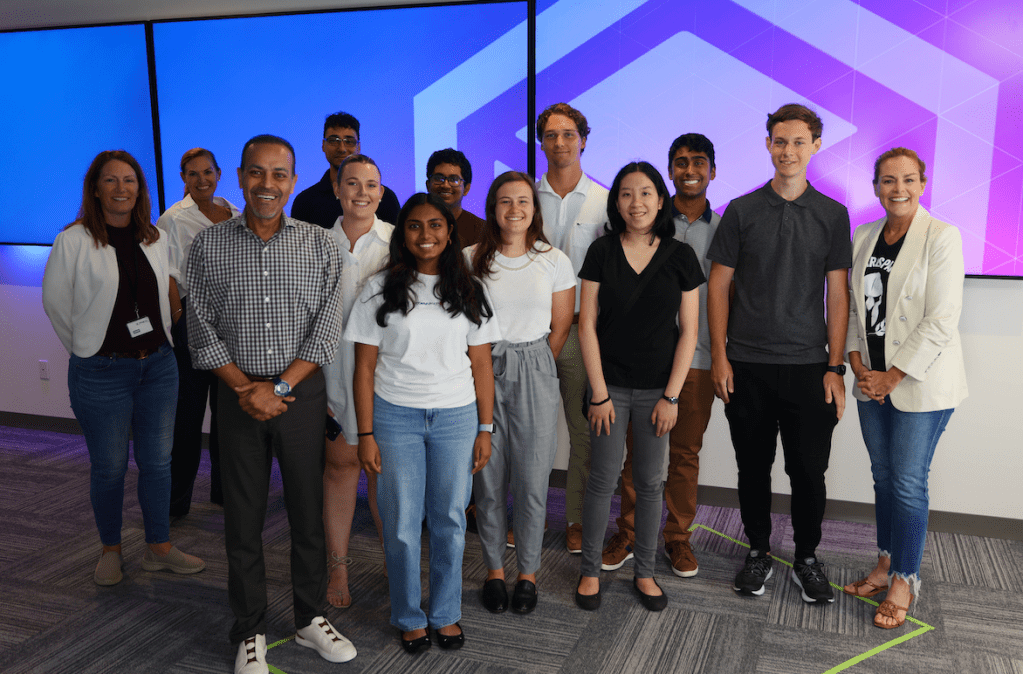
Our U.S. summer internship program recently concluded, and I’m so incredibly proud of the work done by our intern class these past few months! Our intern program provides students with meaningful work experiences as we empower these aspiring professionals to grow and learn with us at Commvault. And our hybrid work environment allows our remote-first work to spread through into our development of the next generation of talent.

https://play.vidyard.com/Qkt2ixrpHZMpyKoaC6R2mb

We prioritize collaboration with leadership, mentorship, and networking opportunities, providing training and direct experience that enables our interns to expand their professional network and technical skillset are all core to this program. These are the minds that will help shape the future for us all!

The internship program concludes with a project contest, which is an exciting opportunity for our interns to present a product idea, process improvement, or survey results tied to their field of study to a panel of our cross-functional leaders. And let me tell you, the innovation we see each year through these projects is exceptional! This year’s projects ranged from built applications, sizing tools, and more!

Each year, I’m reminded of the importance of having mentors to provide insight into new workplace innovations and perspectives. Our continuous culture of learning allows us to embrace and celebrate the ideas of everyone within our global Vaulter community!

We continue to always inspire our next generation of leaders and give them an exceptional experience during their time here. I want to extend a huge thank you to our 2023 U.S. summer intern class for all their amazing contributions to Commvault. Congratulations all!

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Recently, the fifth annual AWS Storage Day was held – a virtual event streamed on Twitch during which Amazon Web Services (AWS) shares the latest news and innovations around their storage portfolio. The event is a celebration of customer-focused innovation, something we at Commvault pride ourselves in, which is why we are honored to have been invited by AWS to participate in this year’s festivities.

Listening to the sessions, it was no surprise to us (given our leadership position in the data protection space – 12 times in a row, in fact) that data was at the heart of every discussion. The newest features and capabilities announced during Storage Day provide new options to customers and application developers to innovate without limits by leveraging the elasticity and scale of AWS storage while still maintaining that all-important cost-efficiency along the way. It is clear that these new enhancements and the 17+ years of innovation leading up to them – across Amazon S3, Amazon EBS, and many more – will power the next generation of Generative AI apps under development right now.

Some of the announcements we thought were especially exciting included:

Then there’s the one most near and dear to our hearts – customers are now able to recover up to 85% faster from Amazon S3 Glacier, further maximizing the value of their archived assets. We might be a little biased, though, as our own Michael Fasulo presented on this very topic alongside Nitish Pandey, a product leader on the Amazon S3 team, in a session during Storage Day (that you can rewatch here).

We were so excited to share the latest example of the great collaboration and innovation that Commvault and AWS are bringing to our joint customers — allowing them to recover their data significantly faster, at no additional cost, from the ultra-low cost, long-term, secure, and durable Amazon S3 Glacier Flexible Retrieval storage class. At its simplest, it’s all about helping our customers protect their data and be able to recover it when their business needs it most. And having partners like AWS who are aligned in that vision and share that customer obsession enables us to do some remarkable things together.  You can read more about this joint solution and why we’re so excited about it on the AWS Storage Blog: Reduce recovery time and optimize storage costs with faster restores from Amazon S3 Glacier storage classes and Commvault.

Now, Storage Day wasn’t all new announcements. There were also some great Amazon S3 primers that helped give us all the confidence that securityremains the top priority for AWS and their customers’ data while also staying relentlessly focused on data durability in everything they do with customer storage. These themes resonate with us, as well, as we are intently focused on securing, defending, and recovering our customers’ data across AWS and their entire data estate. And if you’re looking to find out more about how we are working together to strengthen our customers’ security posture and improve their resiliency, you’re in luck.  

We teased it during the stream of our session, but you can now register for our Technology Touchdowns event on September 6th where we’ll go deep into our playbook and show you what Game-Winning Data Protection with Commvault and AWS looks like. We’ll even be joined by Peyton Manning –2x Super Bowl-Winning Champion, 5x NFL MVP & Member of the Pro Football Hall of Fame – for a candid discussion about teamwork, leadership, and experiences from his successful career.  We’re looking forward to continuing the momentum from this Storage Day event and diving deeper into what makes our partnership with AWS so exciting for customers. 

Quick Links:

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As part of our promise to not only help our customers deliver, but create a more sustainable world, I’m pleased to share the launch of our Carbon Reduction Calculator. Now available on our Command Center Dashboard, we are offering an overview of carbon footprint savings that our customers can potentially achieve with Commvault’s deduplication and compression.

Data centers are large consumers of energy, and as such, they can contribute significantly to the global carbon dioxide emissions. Therefore, implementing energy efficiency measures, such as upgrading to more efficient hardware, improving cooling systems, and optimizing server utilization, and using technologies such as deduplication and compression that help reduce their overall Data Center storage requirements among other things, can significantly reduce a data center’s carbon footprint.

As consumers become increasingly aware of the environmental impact of their purchasing decisions, carbon footprint savings can be an important selling point for companies that prioritize sustainability. Adopting sustainable practices and technologies and reducing carbon footprint can not only contribute to a healthier planet but also lead to cost savings and enhance brand reputation. 

A carbon footprint savings calculator in a data center context can help organizations assess their environmental impact and make informed decisions about implementing sustainable practices and technologies that can aid in reducing their overall carbon footprint. For calculating carbon footprint savings in a data center, our customers typically consider factors such as the data center’s location, size, energy usage, and electricity source. And all these factors are based on industry-established measured metrics.

Our Carbon Reduction Calculator measures the amount of disk storage and energy consumption required before and after deduplication and compression, as delivered by Commvault, and presents this information in terms of more relatable equivalent values, such as the number of barrels of oil consumed, number of smartphones charged, number of passenger vehicles that it could have powered, etc.

At Commvault, part of our commitment to environmental, social, and governance (ESG) is helping our customers and partners manage their data more sustainably. 

With our Carbon Reduction Calculator, we’re not only helping our customers manage and protect their data, but we’re helping them do good for the environment with more sustainably friendly business practices.  

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

At Commvault, we’re revolutionizing how businesses tackle risk, safeguard valuable data, and drive better business outcomes. On June 6th, we unveiled our game-changing innovations that empower businesses of all sizes to take a proactive approach with layered protection.

But our commitment to data security doesn’t end there. We’re excited to announce the launch of Commvault Platform Release 2023E – our latest release introducing additional enhancements for managing and safeguarding your entire data estate.

Global Data Management across Metallic and Commvault Deployment

Commvault PR 2023E introduces https://www.commvault.com/platform/products/cloud-command our new Saas-based platform that provides real-time insights, unified dashboards, and consolidated views of your data across all deployment forms. All in one convenient location!

 Enhancing Commvault Command Center’s capabilities, our new solution streamlines processes and eliminates manual checks and multiple dashboard reviews. Easily track and analyze data trends, prepare for future risks, and quickly identify vulnerabilities across all delivery options using comprehensive security metrics. Enjoy enhanced visibility and actionable insights to streamline your data management.

Reduce guesswork. Automate dormant threat detection and clean file recovery.

Commvault PR 2023E includes our new Threat Scan product’s general availability (GA), which ensures IT admins can be confident that their backup data is clean, safe, and recoverable.

Ransomware threats are something we’ve all heard of, and we know how devastating they can be for organizations. Starting with the initial access, usually through phishing, stolen credentials, or an exploit. The threat then moves laterally, before the big impact – data destruction, encryption, and exfiltration.

On average, a threats dwell time in an environment is around 20-52 days1, depending on how advanced the organization’s defenses are. But here’s the catch: backups happen all the time, and threats can lurk within them before they’re even discovered. This means that infected backups put data recovery at risk. Not only does it take longer to get clean data back, but there’s also the risk of re-infection.

That’s where Commvault Threat Scan comes in; IT admins can take control and defend their backup data by proactively identifying malware threats to avoid reinfection during recovery. Threat Scan automatically analyzes backup data to find encrypted or corrupted files, allowing users to recover trusted versions of their data quickly. Suspected threats can be isolated and quarantined, enabling further analysis by forensic teams in a secure environment.

Unify Data Protection and Security

Building on Commvault’s existing SIEM connector, PR2023E introduces bidirectional integration support for Microsoft Sentinel and Palo Alto XSOAR to improve collaboration and reduce incident response time with automated orchestration and combined insights.

SecOps teams face the constant challenge of handling a high volume of security events, requiring them to adopt automation to effectively respond to and minimize cyber threats. While specific tools are used to gather security events, logs, and alerts, there is a significant gap as these tools fail to collect important information from data protection platforms. This lack of visibility leaves SecOps teams with a blind spot in their overall defense.

Our latest integration brings together the power and visibility of data protection and security platforms, enhancing internal collaboration and overall security posture. Our runbooks make it easy to automate actions out of the box through a secure connection. No more working in silos! SecOps and ITOps can now join forces to tackle security incidents and automate actions like revoking access, disabling data aging, or other data policies.

Better protect data with new integrations for Dell PowerProtect Data Domain

Customers using PowerProtect Data Domain can now easily manage their data through the same native compression, deduplication, and replication processes. This exciting update brings tighter integration with Commvault and PowerProtect Data Domain, which our customers have eagerly asked for.

With the newest capabilities, customers can now leverage the Data Domain Boost Client for native integration with PowerProtect Data Domain. Whether you’re already using our native SDK support with Commvault compression and deduplication, or just starting to protect and utilize PowerProtect Data Domain as a target, you have the flexibility to choose. Access enhanced capabilities through the PowerProtect dashboards and enjoy features like native replication.

Commvault utilizes secure APIs to communicate with PowerProtect Data Domain, and our data plane integration ensures seamless accessibility for all workloads.

These are just a few of the amazing features we have in Platform Release 2023E. You can learn about more of the latest features on our What’s New page for Platform Releases. Connect with our product management team and others in our communities for all the latest news and release information. 

References

1. Sophos Active Adversary Playbook 2022

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Ransomware protection and recovery is a never-ending challenge. Organizations invest in improving their cyber security, and cybercriminals leverage new hacks and tactics to discover and exploit network and system vulnerabilities. It is a continuous game of cyber leapfrog that every organization faces. As these cyberthreats continue to evolve, companies need the right tools to protect their data and ensure that it can be reliably recovered in the event of an attack or system failure. You need a modern data protection solution with built-in security, defense, and rapid recovery to protect against the most advanced threats.

Data Protection Redefined

In today’s digital landscape, cyberthreats have become increasingly sophisticated, and organizations must adopt a proactive approach to data protection. These solutions often only come into play post-impact, after bad actors have compromised data and damage is done. To combat this, organizations must look beyond conventional security tools and take steps to ensure data resiliency. Commvault delivers the right breadth of detection, security, and recovery capabilities to actively secure, defend, and recover data broadly across production and backup environments.

Three Pillars of Data Protection

Commvault’s A-to-Z data protection delivers layered protection across cloud, on-prem, and SaaS workloads. We provide this through our three pillars of data protection: Secure, Defend, and Recover. Securing data with hardened, zero trust, immutable architecture with built-in security protocols to prevent unwanted access and drive compliance in the face of evolving cyberthreats. Defending data with next-generation early warning and in-depth monitoring to surface and neutralize zero-day and insider threats before they cause harm. Recovering data with proactive and reliable recoverability across the industry’s broadest workload coverage, proven to reduce downtime, thwart data loss, and accelerate response times for unrivaled business continuity.

A-to-Z data protection

Creating a secure environment is essential for any organization and having a well-defined plan to protect data is more critical than ever. Commvault provides a wide array of data protection capabilities that safeguard data from internal and external threats. These capabilities provide various benefits to organizations in terms of security, data integrity, and reliability. Improved security measures mean confidential information is kept safe from unauthorized access or malicious attacks. Enhanced data integrity ensures that customer records remain accurate and up to date. Additionally, increased reliability helps organizations maintain compliance with industry regulations. Hardened, secure-by-design protocols include air-gapped backup copies by layering cloud security with restrictive account access and data isolation. Ensure your backup data is immutable with security controls to prevent data from being tampered with, deleted, modified, or altered. In the event of a cyber-attack, if your corporate network becomes infected, air-gapped backup copies will remain isolated, untouched, and available for restoration.

A fast and clean recovery is essential for business continuity. All of your data protection solutions need to follow a multilayered security model and Zero Trust architecture framework to help reduce your attack surface and eliminate any security gaps within your infrastructure.

By using these technologies and taking steps towards creating a secure environment, organizations can stay ahead of the curve when defending against emerging threats and ensure that their systems are always protected against cyberthreats.

From air gap to Zero Trust principles, Commvault has you covered from A-to-Z with the core capabilities of Data secured; Data defended; and Data recovered. With Commvault, you’re ready to protect and recover from ransomware, read our A-to-Z solutions brief and A-to-Z Infographic.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

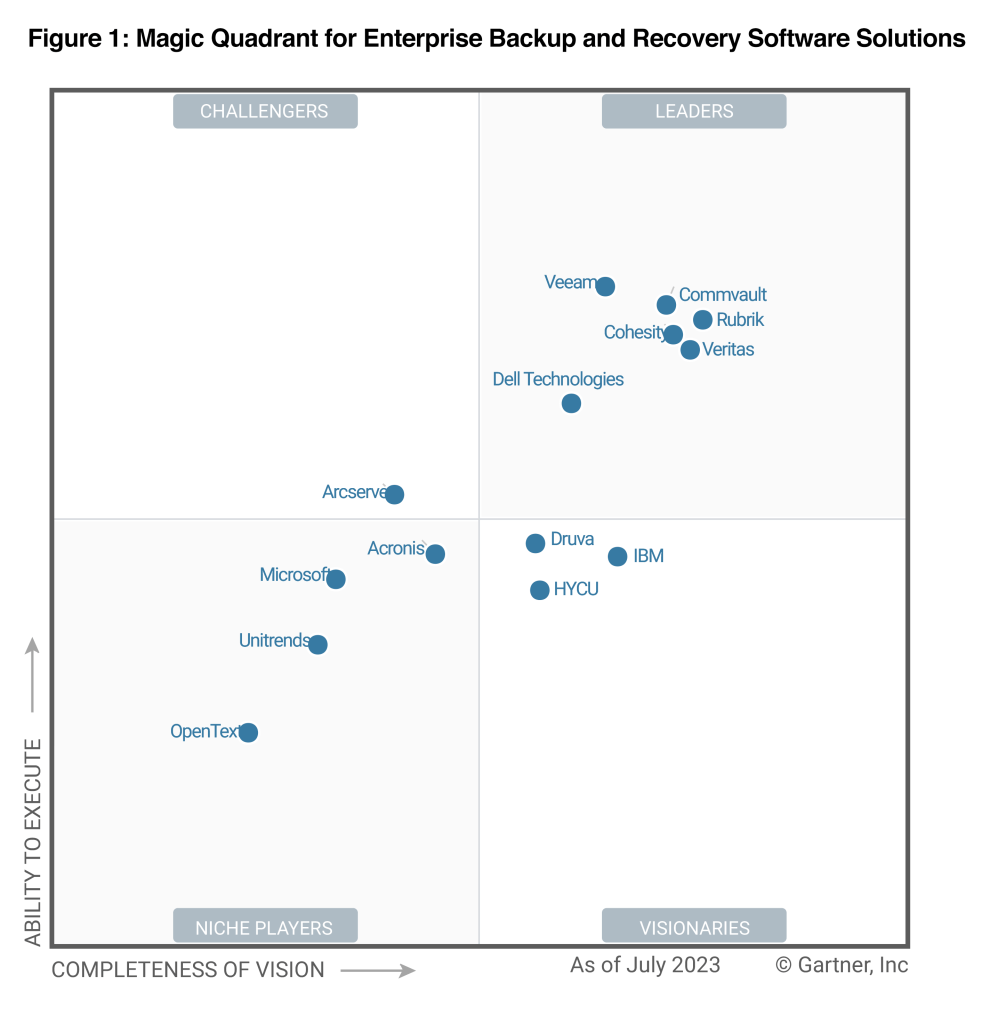
We’re honored to be recognized as a Leader in the 2023 Gartner® Magic Quadrant™ for Enterprise Backup and Recovery Software Solutions for the 12th consecutive year. And, as Commvault’s Chief Marketing and Chief Product Officers, we have to say it never gets old.

From our perspective, recognition like this further validates that Commvault continues to innovate and deliver the resilient data protection and support CIOs, CISOs, and their teams depend on today.

In its latest report, Gartner recognized Commvault as a Leader for our Ability to Execute and Completeness of Vision with our software and SaaS offerings being evaluated. Read the report to learn more about the identified Strengths and Cautions of each recognized vendor in the market.

But what about the future?  In recent conversations with customers and partners, we’ve consistently heard one thing: the complexity and expense of protecting data in a hybrid world is overwhelming security and IT teams everywhere.

Why? Much of it has to do with the modern threats coming from the new wave of pervasive, rapidly proliferating, and increasingly autonomous threats we’re seeing every day. The attacks may be new, but the approach most are taking to stop them is not. They require a more modern approach that spans protection and cyber resilience and brings together the power of AI with the flexibility and ease of SaaS. For instance, our latest capabilities for Metallic ThreatWise provide customers cyber deception tactics in addition to traditional protection, helping to uncover unknown threats, contain and limit exposure windows, and flag ransomware activity before it takes hold.

Not only is this the only way to ensure that today’s hybrid business has uniform protection across all its data and workloads, wherever they live, it sharply reduces infrastructure costs and complexity. Having one data protection platform with software and SaaS enables you to manage your entire experience across your environment. And the automation and machine learning we’ve built into our offerings makes it easier for customers to recover their data in the event of an issue.

It’s a new vision of what data protection should and must become as the modern threatscape continues to evolve. A vision backed by a major investment in innovations that we’ll be revealing through some exciting new capabilities in the coming months. Stay tuned.


Gartner, Magic Quadrant for Enterprise Backup and Recovery Software Solutions, Michael Hoeck, Nik Simpson, Jerry Rozeman, Jason Donham, 7 August 2023. This Magic Quadrant report was previously published as Magic Quadrant for Data Center Backup and Recovery Solutions (2016-2017; 2019-2020); Magic Quadrant for Enterprise Backup Software and Integrated Appliances (2014-2015); Magic Quadrant for Enterprise Backup/Recovery Software (2012-2013); and Magic Quadrant for Enterprise Disk-Based Backup/Recovery (2011).

GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally, and MAGIC QUADRANT is a registered trademark of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.

Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.

This graphic was published by Gartner, Inc. as part of a larger research document and should be evaluated in the context of the entire document. The Gartner document is available upon request from Commvault.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Here at Commvault, our values – we connect, we inspire, we care, we deliver – are foundational to everything we do.

This week we hosted our quarterly internal Global Town Hall meeting and presented our CEO Living Our Values Awards. This quarterly awards program helps us globally recognize and celebrate our Vaulters for their incredible work as they live our values every day.

I’m so proud to announce our FY24 Q1 CEO Living Our Values Award winners:

Craig Glover

Lindsey Keenan

Talent Team

Critical Situation Team

Competitive Marketing Campaign Team

All these winners set an inspiring example and embody what it truly means to be a Vaulter!

To learn more about what it’s like to work at Commvault, check out our careers site.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

If you think a ransomware attack is the worst thing to happen to your organization, I hate to tell you – That’s only the beginning.

Don’t misunderstand – an attack is awful. But after an attack, you’re somewhat of a wounded gazelle and the predators start circling. While you may not be responsible for the attack itself, if you mishandle the recovery, regulatory requirements, and communication, you may be hit with fines and lawsuits. And if that isn’t enough: attackers, competitors, and even potential acquirors and activists may seize the opportunity to pounce.

Which is why, as a Chief Legal and Compliance Officer and an independent board member, I believe you need a proven, practiced data protection plan long before your data is compromised. To help you through this, here are four steps I would take in weighing and responding to an attack:

#1 Secure your Perimeter. At the first sign of an attack, you need to slam the door shut, stop the bleeding. CrowdStrike recently estimated that an attack window is 84 minutes. That’s how long you have before data is bricked, exfiltrated, or destroyed. You don’t have time to debate and the moment you need to close all entry and access points to your business, a ransomware attack cannot be first time you bring the cross-functional team of IT, Security, Legal and others together. You need to be a well-oiled machine and act fast. Practice this like a drill. Know what assets you have, what they access – and be prepared to shut it all down.  

#2 Assess the Damage. Once the perimeter is secure, you must assess the damage. What data was exposed or taken? What damage was done? What is your contractual obligation for maintaining and protecting customer or constituent data? How does this impact you in terms of industry, state, federal, and international regulations? There are more disclosure requirements on the horizon and as PwC recently noted its 2023 Global Digital Trust Insights survey, “only 9% of the respondents feel highly confident that they can effectively meet all disclosure requirements.” The sooner your team is engaged in the planning, assessment, and remediation process, the better.

#3 Were you a victim or negligent? Did you leave the perimeter unsecured? Did you have loose access or security controls? Do you have a data protection plan in place? When was your last tabletop exercise or system tests? Were the right controls in place to prevent (or quickly detect) the attack? Do you have cybersecurity awareness training in place for employees so they’ve learned how to identify phishing attempts? Customers expect that when they give you their data, you will protect it. Having a data protection plan or solution in place is the cost of doing business. Without it, you are not a victim.

#4 Communicate. Communicate. Communicate. Be transparent with your critical stakeholders. The speed in which you disclose can be a delicate balance because you’re still assessing the impact, identifying the root cause, and remediating. Clearly, your CEO and C-Suite leaders need to know as soon as possible and you’ll alert your Board of Directors. But the most important people you need to communicate with are those impacted by the breach, such as your customers, partners, or employees. You need to notify them as soon as possible.

Bottom line: The attackers are on the horizon, they get smarter everyday and time is not your friend. These steps will help you detect and recover quicker from an attack and will give you the confidence that you have taken responsible, informed steps to protect your data.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

AI: A Transformative Force in Various Industries

AI is ushering in a profound transformation across the world today, revolutionizing various aspects of our daily lives and industries. From the way we communicate to the services we use, AI has become an omnipresent force.

  • In healthcare, AI aids in diagnosis and treatment, enhancing patient care and accelerating medical research.
  • AI-driven virtual assistants have become our reliable companions, streamlining tasks, and making our homes smarter. It is shaping the future of transportation through self-driving vehicles, promoting efficiency and safety on the roads.
  • In finance, AI-driven algorithms optimize investments and detect fraudulent activities, securing our financial transactions.
  • AI also plays a pivotal role in addressing global challenges, such as climate change, by optimizing energy consumption and weather forecasting.

With its ability to process vast amounts of data and learn from experience, AI is constantly evolving, presenting boundless opportunities for innovation and progress.

As AI permeates deeper into our society, its transformative impact is becoming increasingly evident, redefining the world we live in and inspiring a future of limitless possibilities.

AI Empowering Data Protection: Fortifying Defenses Against Cyber Threats

The art of the possible in the data protection industry is magnified by the transformative power of AI. With AI’s unparalleled ability to analyze and process vast amounts of data, organizations can fortify their defenses against ever-evolving cyber threats. AI-driven solutions enable real-time threat detection, identifying potential breaches and anomalies before they escalate, complete with an automated approach to recovery in case of any eventuality.

Automated data protection with backup and recovery processes ensure data integrity, while AI’s predictive analytics not only anticipate hardware failures and optimize storage management but also provide the ability to become a proactive and intelligent endeavor in streamlining data protection and recovery operations that are aligned with business SLAs, as AI continuously learns from historical data, improving its predictive capabilities over time.

This convergence of human expertise and AI-driven insights empowers the data protection industry to stay one step ahead, securing sensitive information and fostering resilience in the face of cyber and disastrous events. Embracing AI in data protection is not just a possibility; it’s a powerful reality that sets the stage for a safer and more secure digital future.

Democratizing AI: Commvault’s Commitment to Innovation

As the global technology landscape continues to evolve, AI (Artificial Intelligence) has quickly become a cornerstone of innovation. At Commvault, we believe in the democratization of this game-changing technology, making it accessible to organizations of all sizes and across various sectors.

The goal is not only to leverage AI in streamlining operations but also to use it to revolutionize the user experience and the way that security operations interact and collaborate with data protection teams for seamless recovery of data and IT operations, thereby minimizing downtime in the face of cyber or disaster events. The integration of AI into Commvault’s Data Protection Platform is a testament to this commitment.

Data Protection: Safeguarding the Lifeblood of Organizations

It is crucial for all organizations to recognize the significance of data protection, backup, and recovery in today’s world. These aspects play a pivotal role in an organization’s Business Continuity and Disaster Recovery (BCDR) planning.

As AI revolutionizes various industries, understanding the importance of safeguarding data becomes paramount. Data is the lifeblood of any organization, and without robust protection measures, the risk of data loss, cyber threats, and operational disruptions increases significantly. By comprehending the essence of data protection, backup, and recovery, individuals can actively contribute to their organization’s resilience and preparedness in the face of potential disasters.

As AI drives innovations in technology and data management, fostering a collective awareness of the critical role data protection plays empowers us all to ensure the continuity and longevity of our organizations in an ever-evolving digital landscape.

AI-Driven Automation: Redefining Data Protection Processes

Data Protection technologies provide the much-needed data protected copies of organizations’ data, serving as the “Insurance Policy” to help them recover after a cyber-attack or natural calamity. These technologies safeguard valuable data and keep the operations running even in the face of disasters, cyber-attacks, or system failures.

The traditional backup and recovery processes, while essential, are often time-consuming and demand considerable manual effort. This is where AI comes in. With Commvault platform’s AI-driven capabilities, Commvault helps automate routine tasks, enhancing system efficiency, and reducing technical debt.

AI-Powered Insights: Enhancing Data Protection Efficiency

Commvault’s platform uses AI for management by exception, analyzing the status and completion time of thousands of daily backup jobs to learn typical behavior and identify anomalies. The platform can provide granular views, right down to jobs/events with a curated view of unique or unusual events based on their frequency, severity, and type, reducing any operational overheads. This helps with faster triaging as the data points supplemented are not contaminated with false positives.

Commvault’s AI capabilities also include file anomaly detection as “Indicators of Attack” and entropy analysis for “Indicators of Compromise” for identifying potential ransomware attacks or file compromises.

Fostering User Experience: AI-Powered Analytics and Reports

At Commvault, the vision of AI transcends automation. Commvault is committed to using AI to enhance the user experience. Our AI-powered solutions provide insightful analytics and comprehensive reports, enabling administrators and decision-makers to make data-led business decisions.

A Smarter Data Protection Solution for the Future

We are excited about the prospects that AI holds for us and for our customers. Together, we are paving the way for a smarter, more efficient data protection solution that is future-ready and future-proof.

Stay tuned for upcoming blog posts as we delve into the advanced capabilities within Commvault, fortified by AI/ML, that empower organizations to safeguard their valuable data with confidence of recovery readiness and provide peace of mind to businesses!

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Businesses of all sizes have turned to, standardized on, and leaned into cloud-delivered technology. From private to public, the cloud offers the unique capability to reimagine IT infrastructure and how we develop and consume applications. But as with any modernization process, it doesn’t come without challenges.

Protecting data in and across clouds can be difficult.

Native tooling offers baseline utilities, but cloud platforms aren’t purpose-built for data protection. While leading IaaS (Infrastructure as a Service) and SaaS (Software as a Service) providers deliver robust, durable, and highly performant platforms to consume cloud services, they aren’t steeped in comprehensive backup and recovery of data.

With emerging cyber threats on the rise, today’s businesses must understand their role in protecting data stored in the cloud, and the gaps that overreliance on native tooling present to their business (and data).

The Laws of Protecting Cloud Data

To start, it’s important to understand your business’ role in data protection. Whether at the edge, in the data center, or (drumroll…) across any of your new favorite SaaS or IaaS platforms, the Shared Responsibility Model dictates that protecting data is always the customer’s responsibility. After all, it is YOUR data.

This common principle has led many businesses to consider backup utilities residing within native platforms. What modern businesses commonly find is that they need more. They need dedicated security tools that minimize the risk of an attack on data. They need rapid response capabilities that drive business continuity and mitigate loss. They need standardized management, compliance, and protection that layers across disparate cloud and on-prem environments.

So how do dedicated data protection solutions deliver? Here are three irreplaceable elements of third-party protection for your cloud data:

  1. Isolation and Immutability
    Data protection best practices revolve around preserving and maintaining pristine data copies. This is particularly important when facing data loss at the hands of advanced cyber threats, rogue administrators, or accidental user deletion. At its core, safeguarding data in the cloud demands the need for source-side data isolation.

    With native tooling, production and tertiary copies live within the same security boundary – meaning that impacted production environments could neutralize backup utilizes or data copies themselves. How would I effectively recover if my compromised environment also contained my backups? Air-gapping data outside source environments separates backup data into a separate security domain. This means events occurring in and around cloud platforms cannot also leap into backup copies. Additionally, immutable-by-design architectures ensure data remains unmodified, unaltered, and can’t be tampered with. This further reduces the risk of impact, applying a zero-trust approach to ensuring clean data is available and recoverable at a moment’s notice.

  2. Protection, Recoverability, and Compliance
    Cloud service providers have a lot on their plates. From availability and uptime, to access and performance, best-in-class offerings deliver reliable environments to run your applications and your business. But they can’t be everything to everyone. When facing a data loss event, businesses must have confidence and proven solutions to get data back quickly – without compromise.

    Dedicated data protection solutions offer elevated performance in the realm of backup, retention, and recoverability. This is the ability to safeguard structured or unstructured cloud data at scale, for comprehensive and deep coverage of unique data types living in diverse workloads and applications. Built-in, long-term retention offers extended protection of active and deleted data beyond recycling bin and tombstone limits. Granular and flexible recovery, powers version-level recoveries and mass environment-wide restores. And dedicated controls help maintain data compliance with local, regulatory, and internal regulations.

    This level of precision, speed, and control enables businesses to uniquely meet backup and recovery SLAs while adhering to the most rigorous confidentiality, integrity, and availability standards for government agencies and businesses, alike.

  3. Cloud-Agnostic Coverage
    Businesses operate in a hybrid and multi-cloud world. Application adoption, mergers and acquisitions, and line of business needs have introduced myriad cloud applications and infrastructures – all with varying levels of native backup utilities. This disparity across environments introduces risk as data in the cloud is siloed, requires case-by-case oversight, and consumes IT overhead to safeguard.

    Protecting and managing cloud data estates requires a uniform platform that reaches across disjointed cloud and SaaS environments and eliminates gaps. This simplifies data protection workflows and reduces blind spots by consolidating backups, compliance, and recoveries under one hood. It enables centralized governance and can also accelerate cloud adoption, knowing enterprises have a single experience to protect data uniformly across existing and future investments.

Is your data living in the cloud? For more information on safeguarding cloud and SaaS workloads, visit the following page.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

The digital age has brought with it a whole host of new challenges, especially the unwelcome and relentless assault from ransomware and other threats. This has been compounded by pandemic and the hybrid workplace, which has broadened the attack surface for phishing and other social engineering attacks that target employees’ home offices and data.

It’s not just business, it’s personal.

As Security and IT professionals, we’ve done what we can to harden our environment accordingly. We’ve strengthened our perimeter, stayed on top of our endpoint controls, security patching, embraced zero-trust guiding principles, and introduced more proactive and rigorous data protection strategies. It’s a constant evolving battlefield with complexities and challenges. We do this at the speed of business while being mindful of our spend to manage risk and deliver great service to our customers.

But let’s face it. Today, in most cases, you are your family’s Security or IT practitioner. And data (and the subsequent threats) goes wherever our employees go, which is all the more reason to extend cybersecurity awareness education and training programs outside the office to ensure our people are ready to be our first line of defense.

As a CISO, here are my recommendations for doing this:

First, if it isn’t already, investing in ongoing awareness programs needs to be one of your priorities in 2023. Protection is not limited to one person or one team. A CISO and its team of security practitioners are core to a Security program, however the true strength is in numbers. In other words, by educating and engaging the entire organization on online safety protocols, businesses can be better equipped for cyberthreats. This starts with teaching them how to recognize phishing emails or malicious links containing malware; identity theft prevention techniques; and use encryption and password best practices.

Next, you need to encourage them to take proactive steps to protect their home and office networks, which includes physical security vigilance by protecting their devices and being vigilant of their surroundings. Maintaining regular software updates and security patches; securing their home wireless networks; encrypting sensitive data and files to ensure authorized access; setting strong and unique passwords; and using multi-factor authentication as an extra layer of protection. Frankly, it’s good hygiene for work and for home.

Last, but certainly not least, as a CISO or IT professional, you too need to get personal by creating an atmosphere where employees feel comfortable asking questions about data protection. This comfort, trust, and open line of communication is critical to engage with your workplace and for employees to own their safety measures.

It’s not enough to hope that you aren’t impacted by an incident or breach. It’s improbable. After all, it’s just a matter of time until you are attacked. And cyberattacks have become increasingly sophisticated, with malicious actors using a range of tactics to gain access to your assets and sensitive information to disrupt your business or personal life. Phishing emails, ransomware campaigns, and malware downloads are just the start, so make sure your employees are educated, engaged, and ready for whatever little devil arrives at home, in the office, or on the road.

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

As a longstanding Microsoft partner, one of the most anticipated events of the year is Microsoft Inspire – happening this week (July 18th – 19th). As cyberthreats, AI, and hybrid cloud environments continue to reshape the current business landscape, there’ll be a significant focus on all things data.

And, also, protecting that data.

Today’s customers face significant data challenges. Organizations are under immense pressure to safeguard their business from internal and external attacks. As risks mount, today’s organizations need trusted technologies and partners with proven solutions they can rely on. Solutions that uniformly protect their data from new and emerging threats. Coverage that layers across data centers, clouds, and beyond – for future-proof protection today and tomorrow.

This need is what’s driven Commvault to deliver next-generation data protection and security capabilities alongside Microsoft innovations.

In fact, in the recently released ESG Study, Analyzing the Economic Benefits of Data Protection with Commvault on Azure, customers share why they trust Commvault and why the Commvault/Microsoft relationship is so important to them. One customer summed it up best when they stated, “With Microsoft and Commvault, changes in the cloud are non-issues for us.” This is why more of your customers than ever before are turning to Commvault to protect their data, providing the confidence they need to accelerate their cloud journey.

Driving Innovations for Today’s Businesses

Constant innovation has fueled the Commvault/Microsoft partnership for over two decades to deliver unique capabilities for a future-proof, ready for anything data protection strategy. As Nathan McAfee, Senior Economic Analyst at ESG, comments “the shared roadmaps between the two organizations provide assurance that, as needs change, the solution will grow to meet expanded data protection requirements.” Or, as another customer stated it so eloquently, “We never have to worry about Commvault or Microsoft going away. We sleep better at night knowing we have these two companies behind our most important asset, our intellectual property (our data).” Here’s just a snapshot of recent data protection innovations:

  • Cloud-native data protection: Modern data protection needs to be agile. Commvault’s cloud-delivered solution (Metallic) offers enterprise-grade data protection with the simplicity of SaaS. Built leveraging the durability and scale of Azure, Commvault delivers award-winning protection and security across data estates without the need for infrastructure expenses, costly overhead, or routine maintenance and upgrades. And as the ONLY data protection provider to achieve FedRAMP High In Process – In PMO Review status, Commvault offers a hardened, multi-layered approach to securing data from advanced threats.
  • Comprehensive Microsoft Cloud coverage: Say goodbye to point solutions. Commvault’s deep breadth of Microsoft Cloud workload coverage offers single-solution protection of your most critical environments. From the data center to the edge, we’re constantly evolving, adding support for new and emerging workloads. This provides customers with simplicity and ease of use – knowing critical data in Microsoft 365 (including GCC High environments), Dynamics 365 (including the Power Platform), and Microsoft Azure (including new Azure PaaS workloads such as ComosDB, MariaDB, SQL, and more) is safe, compliant, and recoverable from a single source.
  • Improved security and response: Data protection should start sooner. Commvault has made significant investments in delivering proactive cybersecurity capabilities that defend data, detect threats, and minimize attacks to reduce the risk of compromised data. Building upon this, we announced new bi-directional integrations with Microsoft Sentinel earlier this summer. This integration increases visibility, automates countermeasures, and accelerates response between systems to amplify cyber response and bring IT and Security teams together. It builds upon our unique data security capabilities, such as ThreatWise™, our patented early warning system that surfaces stealthy and advanced cyber threats in production – before data is compromised.

Leveraging New Microsoft 365 APIs

Announced at this week’s Inspire event are new Syntex innovations in support of Microsoft 365. Among those announcements was Microsoft 365 Backup, which provides highly performant recovery capabilities for large data restores. We’re excited to be an early member of the associated Partner Program and integrate these capabilities into our award-winning Metallic offering, as we help businesses of every size to keep their critical data safe, compliant, and recoverable from threats.

We look forward to sharing more details in the weeks to come as we leverage these new capabilities to further enhance Commvault’s Microsoft 365 Backup data protection solution. In the meantime:

  • Reach us at microsoft@commvault.com
  • Join us for an exclusive look into the findings of the ESG Study on July 26th: “Is Your Hybrid Cloud Data Protection Leading to Risky Business?”—register here
  • Download the complete ESG Study today

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

https://play.vidyard.com/Sfjb3UmVP3qHW55HuUU7LS

Cyberthreats have proved to be a perpetual game of cat and mouse. Security teams, on one hand, aim to stay one step ahead, leveling up defenses to uncover and ward off new forms of cyber threats. At the same time, bad actors are constantly evolving to employ new techniques that exploit vulnerabilities and outmaneuver even the most sophisticated of security stacks. And stealth is the name of the game… New forms of attack, including Living Off the Land techniques, are stealthy and once again upping the ante and challenging business’ ability to detect threats – before data is compromised.

Constant Innovation Fuels Cyberthreats

For security teams, they already have their work cut out. From the cloud to the data center, data lives in more places than ever before – and it all needs protecting. That’s a lot of ground to cover, and one weak link introduces risk and potential avenues for attackers to exploit. If that wasn’t challenging enough, cyberthreats also don’t exactly sit still. They’re constantly innovating with new tools and techniques that silently bypass security tooling and compromise systems, applications, and environments. Take for instance Locker malware, which was particularly popular in the late 2000s. Locker disrupted computer access by injecting malicious code to lock users out. Access was only regained when victims paid a ransom. Antivirus tools eventually caught up and Locker became too bulky and slow for a good success rate of attacks. Threat actors recognized this and flipped the script, favoring a new form of stealth technique that was quieter, faster, and could bypass recently improved antivirus technology – file encryption.

Advanced, Silent Techniques Threaten Data

Today, cyberthreats once again look different. Silent attacks, which can remain hidden in systems for extended periods of time, pose a unique risk to businesses. Take Living Off the Land techniques that leverage signed binaries (LOLBins), scripts (LOLScripts), and libraries for example. This method, recently deployed by the Volt Typhoon hacking group, is particularly novel and hard to decipher. It doesn’t use conventional malware files but leverages conventional utilities, executables, and repositories to execute its attack. Traditional security tools based on signatures and traffic analysis cannot detect stealth techniques such as LOLBins used by the Volt Typhoon group, as legitimate tools/information camouflage malicious activity to blend in and bypass even the most advanced security defenses. Once more, bad actors have moved the goal posts, leveraging new, stealthy schemas that go undetected and compromise data unbeknownst to their victims.

New Threats Require New Thinking

https://play.vidyard.com/LkKWWGTGKVtfPBmdBcGQBH

As advanced stealth and persistent techniques become mainstream, defending data from these attacks must also be reimagined to keep pace. Just as bad actors can cloak themselves when employing stealth techniques, defending data against these threats can also employ similar tactics. The use of modern cyber deception can alter the playing field, introducing highly effective decoys masked as real resources and assets, in turn, exposing threats lurking (or in this case, disguised and legitimate utilities) in your network. ThreatWise™, Commvault’s patented early warning system, offers next-generation detection capabilities to surface zero-day and unknown cyberthreats – including recent LOLBins methods. Using look-a-like authentic decoys, ThreatWise™ actively defends data by obfuscating the attack surface, tricking bad actors into engaging with false resources during recon, discovery, and lateral movement. This eliminates blindspots by exposing internal and external threat actors that silently breach perimeter defenses, alerting stakeholders before its time to recover and joining IT and Security Teams for more effective incident response.

For more information on ThreatWise™, please visit https://www.commvault.com/platform/products/threatwise

More related posts


888×500-blog.8

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements
Thumbnail_Blog-What-is-Resops-2026

What Is ResOps – and Why Cyber Resilience Needs It

Read more about What Is ResOps – and Why Cyber Resilience Needs It
Thumbnail_Blog-Playbook-2026

Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago

Read more about Prove It Before You Need It: The Playbook I Wish I’d Had 10 Years Ago