Skip to content

In the ever-evolving landscape of financial technology, regulatory compliance has become a critical aspect of business operations. One of the most significant recent developments in this area is the European Union’s Digital Operational Resilience Act (DORA), which aims to enhance the resilience of the financial sector by setting stringent standards for data management and other operational processes. This blog delves into the importance of data management in complying with DORA and how organizations can navigate these new regulations effectively.

What is DORA?

DORA is a comprehensive regulatory framework designed to address the growing digital risks faced by the financial sector. It covers a wide range of areas, including information and communication technology (ICT) risk management, incident reporting, and third-party service provider oversight. The primary goal of DORA is to verify that financial institutions can maintain their operations and services even in the face of digital disruptions, thereby protecting consumers and maintaining financial stability.

The Importance of Data Management

Data management is at the heart of DORA’s regulatory requirements. Financial institutions must have robust data management practices to maintain the accuracy, integrity, and availability of data. This is crucial for several reasons:

  1. Risk mitigation: Effective data management helps identify and mitigate potential risks. By maintaining accurate and up-to-date data, institutions quickly can detect anomalies and take corrective actions to prevent operational disruptions.
  2. Compliance reporting: DORA mandates detailed incident reporting and regular assessments of ICT risk management. Accurate data is essential for generating these reports and confirming that they meet regulatory standards.
  3. Operational efficiency: Well-managed data can streamline operations, reduce redundancies, and improve decision-making processes. This not only enhances compliance but also boosts overall business performance.
  4. Customer trust: With data breaches and cyberattacks commonplace, maintaining the security and privacy of customer data is paramount. DORA’s data management requirements help build and maintain customer trust.

Key Data Management Requirements Under DORA

To comply with DORA, financial institutions must adhere to several key data management requirements:

  1. Data governance: Establish a clear and comprehensive data governance framework. This includes defining roles and responsibilities, setting data policies, and making sure that your data management practices are integrated into your overall risk management strategy.
  2. Data quality: Verify that data is accurate, complete, and consistent. This involves implementing data validation processes, regular data audits, and using advanced analytics to monitor data quality.
  3. Data security: Implement robust security measures to protect data from unauthorized access, breaches, and cyber threats. This includes encryption, access controls, and regular security assessments.
  4. Data availability: Data must be available and accessible when needed. This involves having reliable backup and recovery systems, as well as disaster recovery plans.
  5. Data privacy: Comply with data privacy regulations, such as the General Data Protection Regulation (GDPR). This includes obtaining proper consent, anonymizing data where necessary, and providing transparency to customers about how their data is used.
  6. Data lifecycle management: Manage the entire lifecycle of data, from creation to disposal. This includes data retention policies, data archiving, and secure data deletion practices.

Implementing Data Management Practices

Implementing effective data management practices to comply with DORA involves several steps:

  1. Assessment and planning: Conduct a thorough assessment of your current data management practices to identify gaps and areas for improvement. Develop a comprehensive plan that aligns with DORA’s requirements and your business objectives.
  2. Technology investment: Invest in advanced data management technologies, such as data lakes, data warehouses, and data governance tools. These technologies can help automate data validation, security, and privacy processes, making compliance more manageable.
  3. Training and awareness: Educate your employees on the importance of data management and the specific requirements of DORA. Foster a culture of data responsibility and awareness throughout the organization.
  4. Regular audits and reviews: Conduct regular audits and reviews of your data management practices to maintain ongoing compliance. Use the results of these audits to make continuous improvements.
  5. Third-party oversight: If you rely on third-party service providers for data management, they also must comply with DORA. This includes conducting due diligence, signing service-level agreements (SLAs), and monitoring their performance regularly.

Best Practices for Data Management

To better understand how to implement DORA’s data management requirements, let’s look at some best practices:

Best Practice: Data Quality Metrics

Use data quality metrics to monitor the accuracy, completeness, and consistency of your data. These metrics can help you identify and address data issues proactively. Improved data quality leads to better decision-making and more reliable compliance reporting.

Best Practice: Automated Data Validation

Implement automated data validation processes to confirm that data is accurate and complete before it is used. This reduces the risk of human error and keeps your data consistently validated.

Best Practice: Secure Data Access Controls

Use role-based access controls and multi-factor authentication to protect sensitive data from unauthorized access. Enhanced security measures reduce the risk of data breaches and confirm that only authorized personnel can access sensitive information.

Challenges and Solutions

While implementing DORA’s data management requirements can be challenging, there are solutions to overcome these obstacles:

  1. Data silos: Many organizations struggle with data silos, where data is stored in isolated systems and departments. This can make it difficult to verify data consistency and availability.
    • Solution: Implement a centralized data management system that integrates data from various sources. This can help break down silos and keep data consistent and accessible.
  2. Resource constraints: Smaller financial institutions may lack the resources to invest in advanced data management technologies and training.
    • Solution: Consider outsourcing data management to third-party service providers that specialize in compliance and have the necessary resources and expertise.
  3. Complexity of regulations: DORA is a complex regulatory framework with many requirements. Understanding and implementing these requirements can be overwhelming.
    • Solution: Seek the help of regulatory compliance experts and use compliance management software to simplify the process.

The Future of Data Management in Regulatory Compliance

As technology continues to evolve, so will the regulatory landscape. Financial institutions must be prepared to adapt their data management practices to meet new and emerging regulations. Here are a few trends to watch:

  1. Artificial Intelligence and Machine Learning can help automate data management processes, improve data quality, and enhance security. These technologies also can help predict and prevent potential risks.
  2. Cloud computing offers scalable and flexible solutions for data management. It can help financial institutions manage large volumes of data more efficiently and securely.
  3. Blockchain technology can provide a secure and transparent way to manage and share data. It can help maintain data integrity and reduce the risk of fraud.
  4. Regulatory technology solutions are designed to help financial institutions comply with regulations more efficiently. These solutions can automate compliance processes, reduce manual effort, and provide real-time monitoring and reporting.

Data Management Is Key to DORA Compliance

DORA represents a significant step forward in enhancing the digital operational resilience of the financial sector. Effective data management is crucial for compliance with DORA and for maintaining the trust and confidence of customers and regulators. By implementing robust data governance, maintaining data quality and security, and staying ahead of regulatory trends, financial institutions can not only meet DORA’s requirements but also gain a competitive edge in the digital age.

DORA’s data management requirements are not just a regulatory burden but an opportunity to improve operational efficiency, mitigate risks, and build a more resilient and trustworthy financial institution. Embrace these requirements and use them as a catalyst for positive change in your organization.

Learn more about how you can prepare for the Digital Operational Resilience Act in our Exploring DORA blog series:


More related posts


person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Forrester recently published the “Forrester Wave: Data Resilience Solutions Q4 2024,” which illustrated a shakeup from the latest 2022 version to the 2024 version by dropping two of the three former “Leaders” to “Strong Performers,” and elevating two former “Strong Performers” to “Leaders.” 

As a result, Commvault was the only vendor that has maintained a position as a “Leader” in all the publications of the Forrester Wave for Data Resilience since its inception in 2019. 

What enabled Commvault to maintain and elevate the status of a top “Leader” in the Wave from 2022 to 2024? In the words of Forrester: “Commvault’s strategic strengths include a commitment to innovation through R&D and acquisition as well as a well-developed partner ecosystem of channel, technology, go-to-market, and infrastructure partners.”  

After going public in 2006, Commvault has continuously and vigorously maintained a cadence of innovation to stay ahead of the latest trends in data management and resilience market. Commvault has delivered not only Backup-as-a-Service for hybrid cloud and container workloads but expanded most recently to modern cloud-native distributed application resilience services through the acquisitions of Appranix, recently renamed Cloud Rewind, and Clumio for cloud-native data heavy workloads.

As cloud-native customers look for hyperscaled environment protection and recovery, Commvault now offers highly differentiated cloud and cyber resilience capabilities, thanks to the ease of onboarding, agentless, and quick-to-realize value of the modern cloud-native software it acquired.

Not only did Forrester recognize the distinct differentiation of Commvault’s modern cloud-native software capabilities by rating them with the highest possible score for the “Hyperscale Cloud/IaaS” and “Kubernetes and Containers” criteria, but other reports also ranked and scored Commvault’s cloud-native capabilities as the most advanced in the industry.  

In the 2024 Gartner Critical Capabilities for Enterprise Backup and Recovery Software Solutions, Commvault was ranked as the top vendor for the “Hybrid/Multicloud” and “SaaS” use cases. In addition, Commvault was positioned as the top “Leader” in GigaOm’s 2024 Sonar for Cloud Native Data Protection. With the acquisition of Appranix, Commvault also has pioneered the cloud infrastructure recovery assurance market cloud-native applications.1 

Not only is Commvault generating results in the leading industry analyst reports, but it also has reported double-digit revenue growth, positive cash flow, and profitability five quarters running. 

Indeed, Commvault’s commitment to innovation and customer-driven nature has elevated it to deliver the most advanced software to address that latest cloud resilience requirements of the modern enterprise.  

1 Hype Cycle for Backup and Data Protection Technologies, 2024, Gartner, July 2024 

More related posts


person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Consolidation, like the recent Cohesity-Veritas deal, is expected in a dynamic industry that has rapidly moved from data protection to cyber resilience. We too have complemented our bold and disruptive product roadmap with a few key acquisitions – with one significant difference.

We have a well-defined strategy that includes detailed integration planning and prioritizes our customer needs. So, while Cohesity and Veritas try to make sense of a complex deal and rationalize overlapping portfolios, we are focused on you, our customers.

Our acquisition strategy is all about enhancing our Commvault Cloud cyber resilience platform with cutting-edge capabilities that give you immediate value and solve for future use cases. Case in point, bolstered by our Appranix acquisition in April, our new and unique Cloud Rewind offering helps customers quickly restore their cloud applications and data environments to where they were before a cyberattack or breach. This can mean the difference between a minor disruption and a major crisis. Cloud Rewind is already a key part of our platform and customers are seeing the benefits.

Additionally, by bringing Clumio into the Commvault family, we are revolutionizing recovery for next gen cloud-native stacks – like large and growing GenAI environments with billions of objects in a massive Amazon S3 bucket. Recovery at this scope and scale is truly game-changing, and we just announced Clumio Backtrack to make this easier for customers.

You see, when it comes to M&A, the big questions we ask ourselves are: will this benefit the customer versus forcing them to make unnatural choices? Does the integration complement our platform? And will this help our customers be more resilient?    

We are pushing the boundaries of what’s possible – bringing in the best and brightest minds, planning to invest in R&D, and where it makes sense, making acquisitions to give you cutting-edge, cloud-first technologies.

Commvault is here to help you keep your business continuous.

More related posts


person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

At Commvault, we believe that nurturing an open, supportive environment is key to a thriving workplace. This November, at the Commvault COE, we dedicated the entire month to raising awareness and driving meaningful conversations around men’s mental health during our Commvault Cares Quarter of Caring– a global initiative that encourages prioritizing well-being for all employees. By focusing on this often-overlooked issue, we aimed to create an atmosphere where everyone feels empowered to speak up and seek support.

Throughout the month, we engaged employees with a series of impactful activities. These included sharing thought-provoking notes and compelling facts across channels, as well as encouraging managers to incorporate mental health check-ins during their regular interactions to drive open communication.

On Nov. 19, our International Men’s Day celebration brought employees together for an enriching day of fellowship that included games, a panel discussion featuring diverse perspectives on mental health, and more. We also hosted expert-led sessions, including Karthik R.’s workshop on overcoming fears and embracing vulnerability. Each of these initiatives was thoughtfully designed to raise awareness, provide practical tools, and inspire a culture of empathy and connection.

Additionally, as part of our commitment to mental health, we conducted a survey to understand how our employees perceive mental health support at Commvault. The results were encouraging: 76% of respondents felt comfortable discussing mental health concerns with colleagues or managers, and 68% expressed that they feel supported by their teams when facing challenges.

These insights reinforce our belief that creating a culture of openness and empathy is vital to employee well-being. At Commvault, we provide a wide range of support to keep our employees’ health and well-being a top priority.

In addition to regular check-ins by managers and monthly workshops, we take immense pride in offering valuable resources, including doctor-on-call services, partnerships with Cult Fitness, and the Spring Health benefit – all aimed at helping employees prioritize both their physical and mental health.

Looking ahead, we remain committed to keeping these conversations alive. By continuing to prioritize mental health through programs like these and reinforcing our support systems, we strive to create a workplace where every employee, regardless of gender, feels valued, heard, and supported. Let’s keep breaking barriers and building an inclusive environment where mental health is treated with the same importance as physical health – every day of the year.

Learn more about how we support our employees and build community at Commvault through our Diversity, Equity, and Inclusion programs.

More related posts


person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

The Digital Operational Resilience Act (DORA) is set to revolutionize the way financial entities approach cybersecurity and operational resilience. As organizations in the EU prepare to comply with this new regulation that takes effect January 17, it’s crucial to understand how DORA will impact cyber recovery strategies. This post delves into the key changes and considerations for enhancing your cyber recovery plans under DORA.

Understanding DORA

DORA aims to ensure that financial entities can withstand, respond to, and recover from all types of operational disruptions and threats. This includes cyberattacks, which have become increasingly sophisticated and frequent. The regulation mandates that financial institutions implement robust operational resilience frameworks, including comprehensive cyber recovery strategies.

Key Changes in Cyber Recovery Strategies

Financial institutions have long had a mandate to protect their data and infrastructure from threats, but DORA aims to increase the overall resilience of financial systems operating in the EU. Here’s how the provisions will affect an organization’s resilience strategies:

1. Incident Response Plan

An incident response plan is crucial for swift and effective action in the event of a cyber incident. This plan should outline the steps to be taken immediately after an incident is detected, including containment, eradication, and recovery. Under DORA, incident response plans must be more detailed and regularly tested. This includes:

    • Clear roles and responsibilities: Define who is responsible for what during a cyber incident.
    • Communication protocols: Establish clear communication channels with stakeholders, regulators, and customers.
    • Regular drills: Conduct regular incident response drills to prepare all team members.
    2. Data Backup and Recovery

    Data is the lifeblood of any organization, and DORA puts increased emphasis on the importance of its integrity and availability. Organizations must:

      • Implement robust backup solutions: Ensure that critical data is backed up regularly and stored securely.
      • Test recovery procedures: Regularly test data recovery procedures to ensure they work as intended.
      • Redundancy: Maintain redundant systems to minimize downtime during a cyber incident.
      3. Third-Party Risk Management

      Many organizations rely on third-party vendors for various services. However, these vendors also can introduce risks. Effective third-party risk management involves:

        • Vendor due diligence: Conduct thorough assessment of the security posture of all third-party vendors.
        • Contractual agreements: Confirm that vendor contracts include clear requirements for cybersecurity and incident response.
        • Ongoing monitoring: Continuously monitor third-party relationships to verify compliance, and identify and mitigate risks.
        4. Regular Audits and Assessments

        DORA requires regular audits and assessments of cybersecurity measures. This includes:

          • Internal audits: Conduct regular internal audits to identify vulnerabilities and areas for improvement.
          • External audits: Engage external auditors to provide an independent assessment of your cybersecurity posture.
          • Risk assessments: Perform regular risk assessments to identify and mitigate potential threats.
          5. Employee Training and Awareness

          Employees are often the first line of defense against cyber threats. Education can help create a culture of vigilance and resilience – and reduce the risk of human error.  Under DORA, organizations must facilitate:

            • Regular training: Provide regular training to all employees on cybersecurity best practices.
            • Awareness campaigns: Conduct awareness campaigns to keep employees informed about the latest threats and best practices.
            • Simulated attacks: Use simulated phishing attacks and other exercises to test employee awareness and response.

            Implementing DORA-Compliant Cyber Recovery Strategies

            While the advent DORA may change some elements of your overall strategy, the basic framework of implementing a plan should be the same. Here are the steps you can take to keep your organization’s cyber recovery plan in compliance:

            1. Assess Current Capabilities: Conduct a thorough assessment of your current cyber recovery capabilities to identify gaps and areas for improvement.
            2. Develop a Comprehensive Plan: Develop a comprehensive cyber recovery plan that addresses all aspects of DORA, including incident response, data backup, third-party risk management, and training.
            3. Allocate Resources: Allocate the necessary resources, including budget, personnel, and technology, to implement your cyber recovery plan.
            4. Test and Refine: Regularly test your cyber recovery plan and refine it based on the results. Continuous improvement is key to maintaining operational resilience.
            5. Document Everything: Document all aspects of your cyber recovery plan, including policies, procedures, and test results. This documentation will be crucial for demonstrating compliance with DORA.

            Compliance Should Lead to Resilience

            DORA represents a significant shift in how financial entities approach cybersecurity and operational resilience. By enhancing incident response plans, implementing robust data backup and recovery solutions, managing third-party risks, conducting regular audits and assessments, and providing comprehensive training and awareness, organizations can build resilient cyber recovery strategies that comply with DORA.

            As the regulatory landscape continues to evolve, it’s essential to stay informed and adapt your strategies accordingly. By proactively addressing the requirements of DORA, you can prepare your organization to withstand, respond to, and recover from cyber incidents, ultimately safeguarding your operations and reputation.

            Learn more about how you can prepare for the Digital Operational Resilience Act in our Exploring DORA blog series:

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            With Thanksgiving this week in the U.S., it’s always a great reminder to take a step back and reflect on what we’re most thankful for.

            I’m so grateful for all the incredible Vaulters across the world and the community we continue to build together. We’re currently celebrating our Commvault Cares Quarter of Caring, an annual initiative dedicated to giving back to our communities and raising awareness of causes close to our hearts. And while caring is a commitment we uphold daily, our Commvault Cares initiative is a time to celebrate our global efforts by engaging, inspiring, connecting, and contributing to our local communities.

            We are halfway through our Quarter of Caring, and I have so much gratitude for the amazing work our Vaulters have done to give back – from local food drives, supporting first responders, and running or walking for a cause. I cannot wait to see what else we accomplish together.

            In the spirit of giving and caring, I encourage us all to keep gratitude top of mind during this time of year. Check out the video below to hear what our Vaulters are most grateful for and what matters most to them this holiday season:

            https://play.vidyard.com/SceDdefShCYvfijdpA2yVQ?

            A little bit of gratitude goes a long way, so be sure to share it with others. As I like to say, sharing is caring. And to everyone celebrating Thanksgiving this week with your loved ones, I hope you have a wonderful holiday.

            To get an inside look at what it’s like to work at Commvault, visit our careers website.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            I’m thrilled to share that Commvault has earned the Women’s Choice Award for Best Company to Work For in 2024, with distinctions in the categories of Women, Inclusion, and Millennials. This award is a meaningful acknowledgment of our commitment to fostering an inclusive and supportive culture, where employees of all backgrounds can thrive.

            At Commvault, what we do matters. We’re all about empowering our Vaulters to feel that their contributions are meaningful, not only for our customers and partners, but also for their own career growth and well-being. We know that building a diverse and inclusive workplace is essential to this mission, and we’re dedicated to providing equitable opportunities and a healthy work-life balance so that employees can bring their best selves to work every day.

            Receiving this award highlights our ongoing efforts to close race and gender gaps in the workplace, and our commitment to investing in the next generation of leaders. Through mentorship programs, flexible work arrangements, generous parental leave policies, tuition reimbursement, wellness benefits, and employee groups, we aim to give our teams the resources they need to grow personally and professionally.

            Our programs are designed to help women of all backgrounds navigate their careers, advance, and feel supported, while also providing resources for millennials and employees with diverse lifestyles. We’re honored to receive the Women’s Choice Award as we continue to make Commvault a great place to work.

            For more information about Commvault’s award-winning culture and career opportunities, please visit: Careers at Commvault.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            At Commvault, our purpose goes beyond technology – it’s about uplifting people and communities and standing together to drive real change. During our recent executive visit in the Center of Excellence, we had an opportunity to partner with Rise Against Hunger India (RAHI) in the fight against malnutrition. The staggering fact that nearly half of childhood deaths globally are linked to malnutrition only fuels our determination to act.

            On October 17, 2024, our Board Members, Executive Leadership Team, and Vaulters joined forces in Bangalore, packing over 20,000 meals for those in need. With just a few hours of focused teamwork, we were able to contribute meaningfully to RAHI’s mission of providing nutritious meals, one step closer to a hunger-free world.

            This event is a reflection of our shared values and our deep commitment to bringing real change to society. We are grateful to each Vaulter who brought their energy and heart to the cause, reminding us that even small actions can drive profound impact. Together, we’re taking concrete steps to combat hunger – because when we unite, we create an unstoppable force for good.

            Learn how Commvault is giving back in communities around the globe.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            We’re pleased to share that Microsoft Azure Elastic SAN support for Azure virtual machines (VMs) will be available in private preview following Microsoft Ignite 2024. This innovative offering allows Elastic SAN volumes to be attached to Azure VMs via iSCSI, providing enhanced flexibility and scalability for your cyber resilience and data protection storage needs.

            Michael Fasulo, Senior Director of Product Management at Commvault, sums up the news best: “Throughout our 27+ years of partnership with Microsoft, our goal has always been to provide the broadest workload coverage and native Azure integration, providing unmatched scalability and cost-effectiveness while delivering true continuous business. Our support for Elastic SAN amplifies our strong joint value to customers, embracing today’s cloud-first reality.”

            How This New Feature Can Help Your Organization

            Azure Elastic SAN offers a powerful and flexible storage solution that can help you optimize your workloads and achieve your business goals. With its enhanced performance, scalability, and cost-effectiveness, Elastic SAN is the ideal choice for demanding applications.

            Commvault Cloud’s support for Azure Elastic SAN offers significant advantages for organizations seeking comprehensive cyber resilience solutions. Commvault’s integration with Azure Elastic SAN simplifies backup and recovery processes, while our robust cyber resilience and data protection capabilities provide peace of mind and minimize the risk of data loss.

            Why Is the Adoption of Elastic SAN Accelerating?

            There are many benefits that organizations gain from adopting Elastic SAN, including enhanced performance, scalability, and cost-effectiveness. With the explosion of AI data and the need to effectively protect these large volumes of data, this functionality helps organizations securely and cost-effectively protect and secure these mission-critical workloads. Commvault Cloud’s enhanced coverage of Elastic SAN will help keep these workloads cyber resilient and recoverable from cyberattacks:

            • High-Performance Computing: Deliver demanding HPC applications with exceptional performance.
            • Large-scale databases: Accelerate database operations and improve query response times.
            • Big data analytics: Process and analyze large datasets efficiently.
            • Content Delivery Networks: Streamline content delivery and improve the user experience.

            Learn more

            For a demo and to learn more about our enhanced support of Azure Elastic SAN, visit Commvault Cloud for Microsoft Azure | Commvault and reach out to us at microsoft@commvault.com.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Microsoft Active Directory (AD) and Entra ID are the backbone of your organization’s security infrastructure. When AD fails, your business stops. This comprehensive guide provides actionable strategies to help you protect your directory services from every type of disaster – from simple human errors to sophisticated cyberattacks.

            Why AD Protection Is Non-Negotiable

            Without a functional AD, employees cannot access email, applications, file shares, or any authenticated system. Here’s what’s at stake:

            • Complete business paralysis when users can’t authenticate.
            • Security vulnerabilities from manual workarounds during outages.
            • Regulatory compliance violations affecting audit trails.
            • Reputation damage from service disruptions.
            • Financial losses from productivity stops and recovery costs.

            The AD Disaster Spectrum: Know Your Risks

            Granular Disasters (Hours to Days Impact)

            Think of that routine task gone wrong­ – deleting the wrong user account. Now that user’s productivity is derailed, and there’s time and cost associated with the remedy. Your business is disrupted, and you might suffer reputational damage if they happened to be in the middle of a critical, time-sensitive project.

            Common scenarios include:
            • Accidental object deletion: Single user, group, or organizational unit removal.
            • Permission misconfiguration: Access rights incorrectly modified.
            • Attribute corruption: User properties become invalid.
            • Group Policy conflicts: Policy settings creating authentication issues.
            Domain-Level Disasters (Days to Weeks Impact)
            • Domain controller failure: Hardware or software corruption.
            • Replication issues: Inconsistent data across controllers.
            • Certificate authority problems: Authentication services disrupted.
            • Network segmentation: Sites unable to communicate.
            Forest-Level Disasters (Weeks to Months Impact)

            In worst-case scenarios like schema corruption or ransomware, the entire domain or forest may need to be recovered. These scenarios emphasize the need for robust recovery strategies.

            Critical scenarios include:
            • Schema corruption: Fundamental AD structure damaged.
            • Ransomware attacks: Encrypted or deleted AD database.
            • Complete infrastructure loss: Natural disaster or major cyber incident.
            • Trust relationship failures: Multi-domain environments compromised.

            Your AD Protection Action Plan

            Phase 1: Get the Basics Right (First Month)
            1. Turn on AD Recycle Bin so you can easily restore deleted objects.
            2. Set up daily backups and store them in multiple locations.
            3. Start monitoring for authentication failures and replication issues.
            4. Test your backups to make sure they actually work.
            5. Train your team on basic recovery procedures.
            Phase 2: Build Advanced Protection (Months 2­–3)
            1. Create a recovery lab where you can safely test restores without affecting production.
            2. Set up change tracking so you can see what changed and when.
            3. Automate common fixes to speed up recovery.
            4. Plan for the worst with offline backups.
            5. Add smart monitoring that can detect unusual behavior patterns.

            How Commvault Safeguards Your AD

            Commvault® Cloud Backup & Recovery for Active Directory helps protect your AD and Entra ID to minimize loss, downtime, and cyber risk. It provides frequent backups and fast, accurate recovery of objects, attributes, and entire forests.  

            Key capabilities include:
            • Interactive full domain and tenant comparisons to easily compare changes between two points in time.
            • Granular recovery of missing, damaged, or misconfigured objects and attributes.
            • Automated forest recovery to a pre-attack state.
            • Regular AD recovery testing.
            • Unified protection for AD and Entra ID.
            Next Steps: Implement Your AD Protection Strategy
            1. Assess your current state.
            2. Prioritize implementation based on your highest-risk scenarios.
            3. Establish baseline protection.
            4. Schedule regular testing to validate your recovery capabilities.
            5. Continuously improve based on test results and emerging threats.

            Your AD protection strategy should evolve with your business needs and threat landscape. Regular testing and updates help enable your organization to recover quickly from any AD disaster, and maintain business continuity and user productivity.

            Ready to strengthen your AD protection? Start with a strong backup solution that provides robust recovery capabilities. The investment in robust AD protection can pay dividends when disaster strikes. Try Commvault Cloud Backup & Recovery for Active Directory with a 30-day free trial.


            Learn More

            Check out these other blogs in our Active Directory series:

            Watch our on-demand webinar “The Naked Truth” to see experts simulate a real-world Active Directory outage and demonstrate rapid restoration techniques.


            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

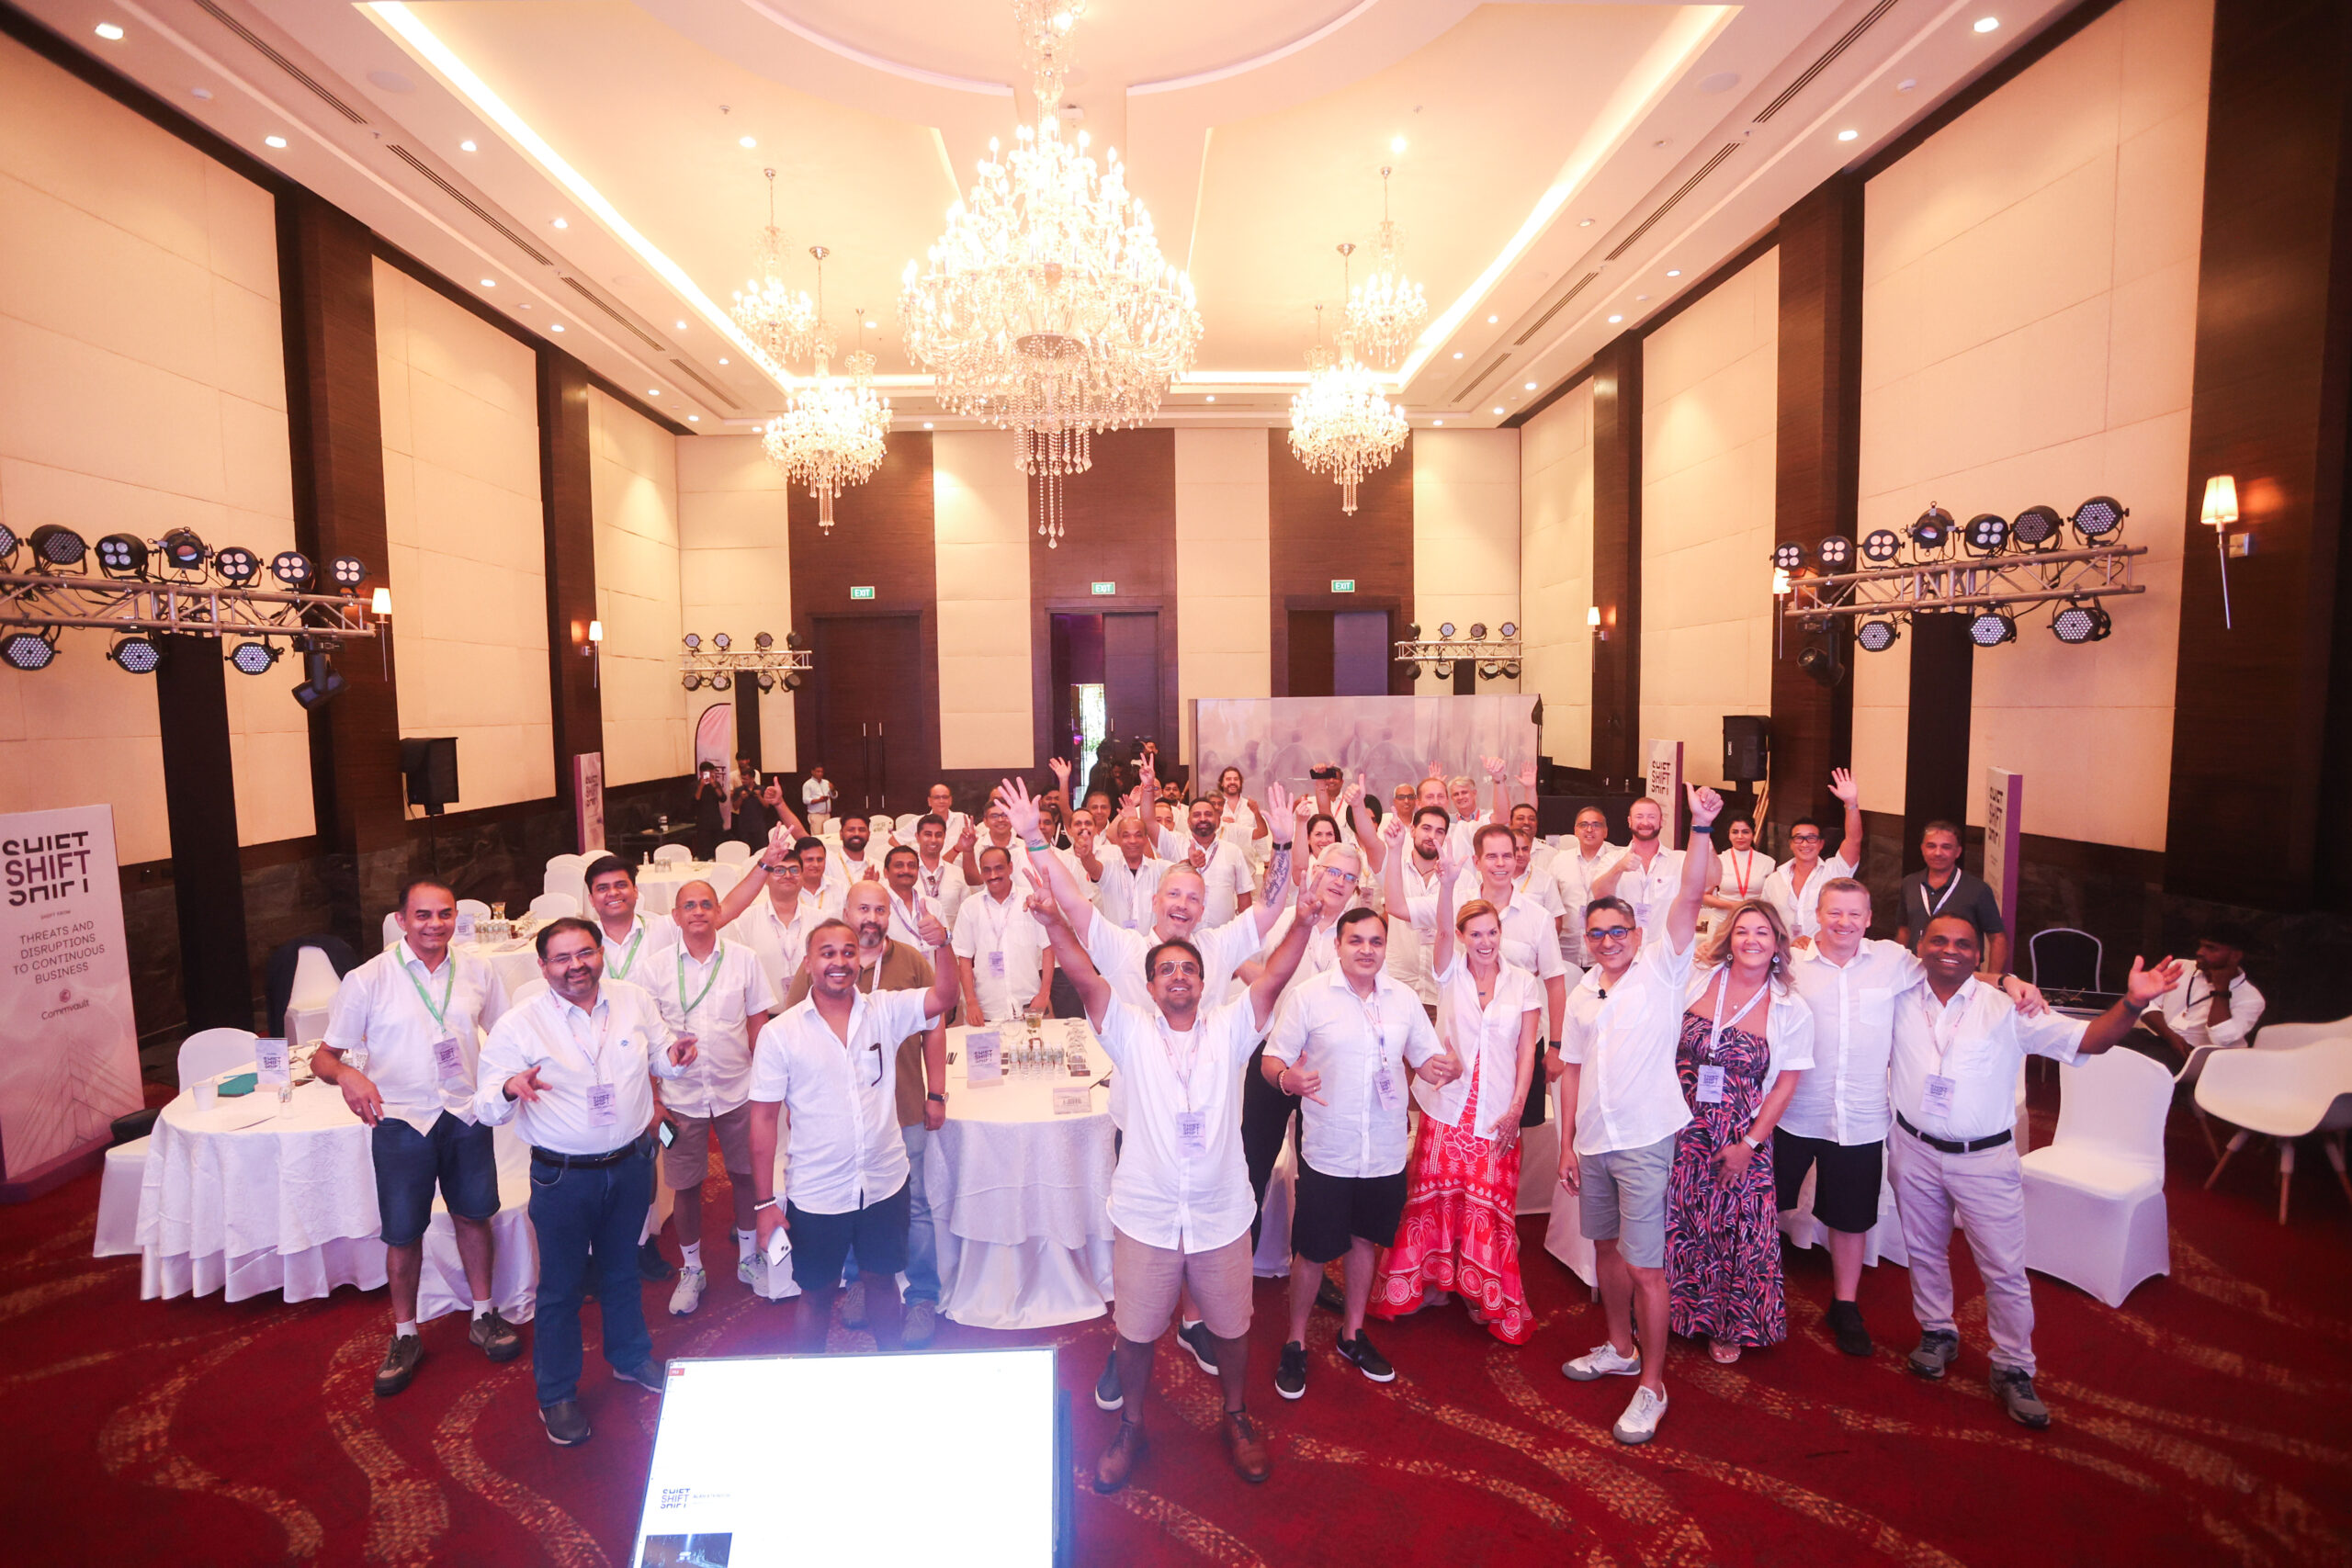
            Two weeks ago, Commvault hosted our second annual SHIFT GSI Partner Summit in Goa, India. This brought together senior executives from the world’s leading global system integrators to examine what cyber resilience means for enterprises rapidly adopting cloud-first strategies and AI-driven technologies to transform their businesses.

            The summit offered a unique opportunity for Commvault and our GSI partners to dig into the distinct challenges these organizations face in making their hybrid cloud environments cyber resilient and how resilience is evolving to keep pace with an always-on, always-available business world. Commvault was excited to have Cognizant, HCLTech, Infosys, Kyndryl, Tata Consultancy Services, Tech Mahindra, and Wipro participate in the two-day summit.

            We also were thrilled to have the marquee sponsorship of Amazon Web Services, Hitachi Vantara, and Microsoft Azure. Their insight and perspectives on the industry enriched participants’ appreciation of the dynamic nature of today’s data environments and underlined the importance of a strong partner ecosystem in staying ahead of cyberthreats, regulatory compliance needs, and disruptive technologies.

            Redefining cyber resilience

            Commvault senior leadership walked partners through our recent cyber resilience solution announcements. These highlighted Commvault Cloud’s flexibility to secure, scale, and manage data environments to the specific needs of enterprises’ hybrid and multi-cloud environments. We shared announcements surrounding cloud-native protection for next-generation AWS, Azure, and Google workloads while strengthening resilience for data at remote sites and in data centers with Hyper Scale X.

            We also dove into how cyber resilience is being redefined and why testing recovery plans in an isolated, secure cleanroom environment must be a critical component of demonstrated cloud cyber resilience. This commitment to helping customers with continuous business was further strengthened by the breadth and depth of innovative capabilities added to our portfolio this fall.

            First we launched Cloud Rewind, our latest innovation to automate the discovery, mapping, and recovery of complex, cloud-native, and SaaS workloads across public cloud. Second, we shared how our recent acquisition of Clumio will help customers nearly instantly recover workloads, including AWS S3 data that are vital to next-generation AI pipelines.

            Recognizing the power of our partnerships across industries

            Our GSI partners took the stage to discuss how our solutions have been incorporated into their cybersecurity, cloud migration, and AI offerings in finance, healthcare, manufacturing, government, and retail. They also shared customer success stories that demonstrate how Commvault has strengthened their cyber resilience and accelerated digital transformation programs.

            It was fitting to close the summit by recognizing the importance of our partners’ collaborations and the innovative approaches they have taken to leveraging our solutions. Each has uniquely contributed to the value and industry-leading position Commvault enjoys around the world and is a testament to the strength of our partnerships. 

            GSI Partner Awards

            Break-through GSI Partner of the Year Award – Cognizant

            Cognizant is honored for its unwavering commitment to prioritizing security and cyber resilience in its enterprise solutions and working closely with Commvault to support customers’ most demanding resilience requirements.

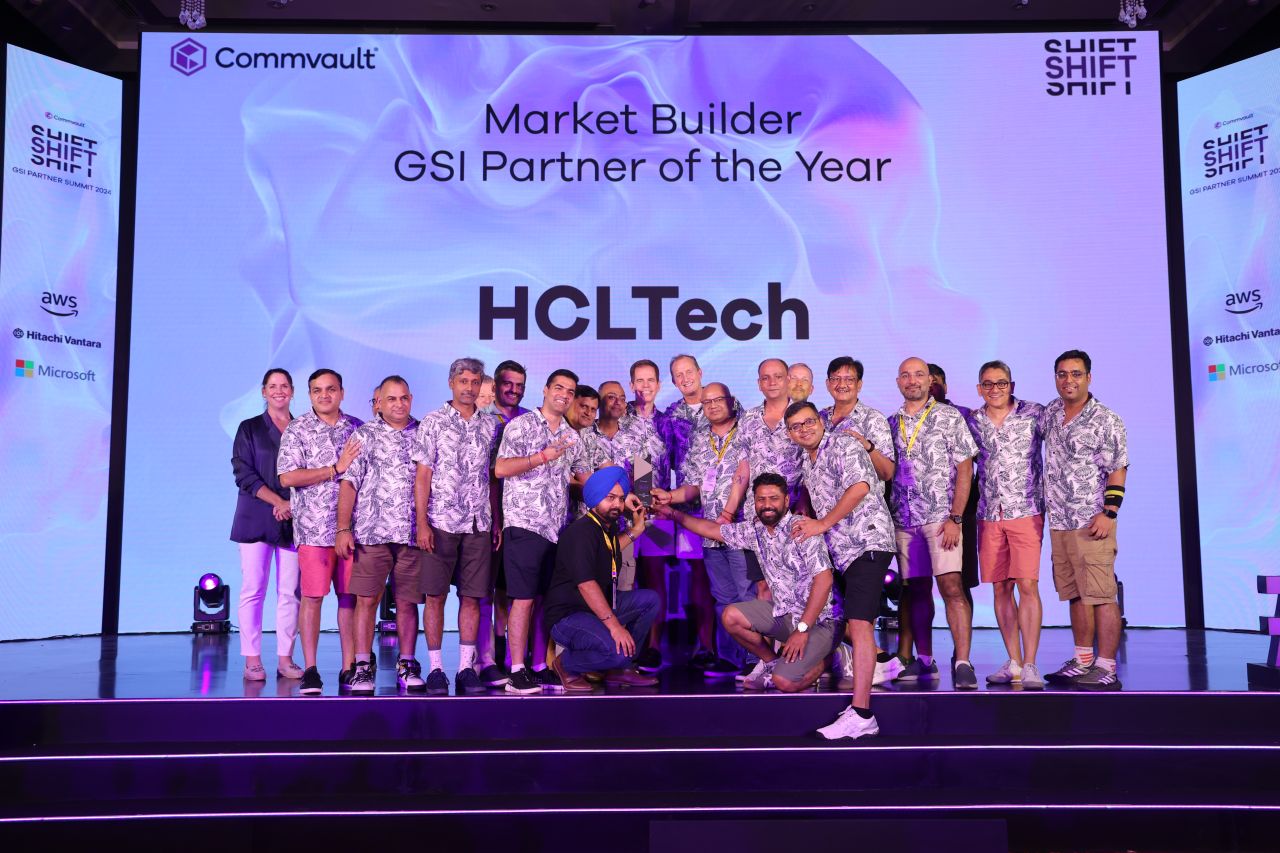
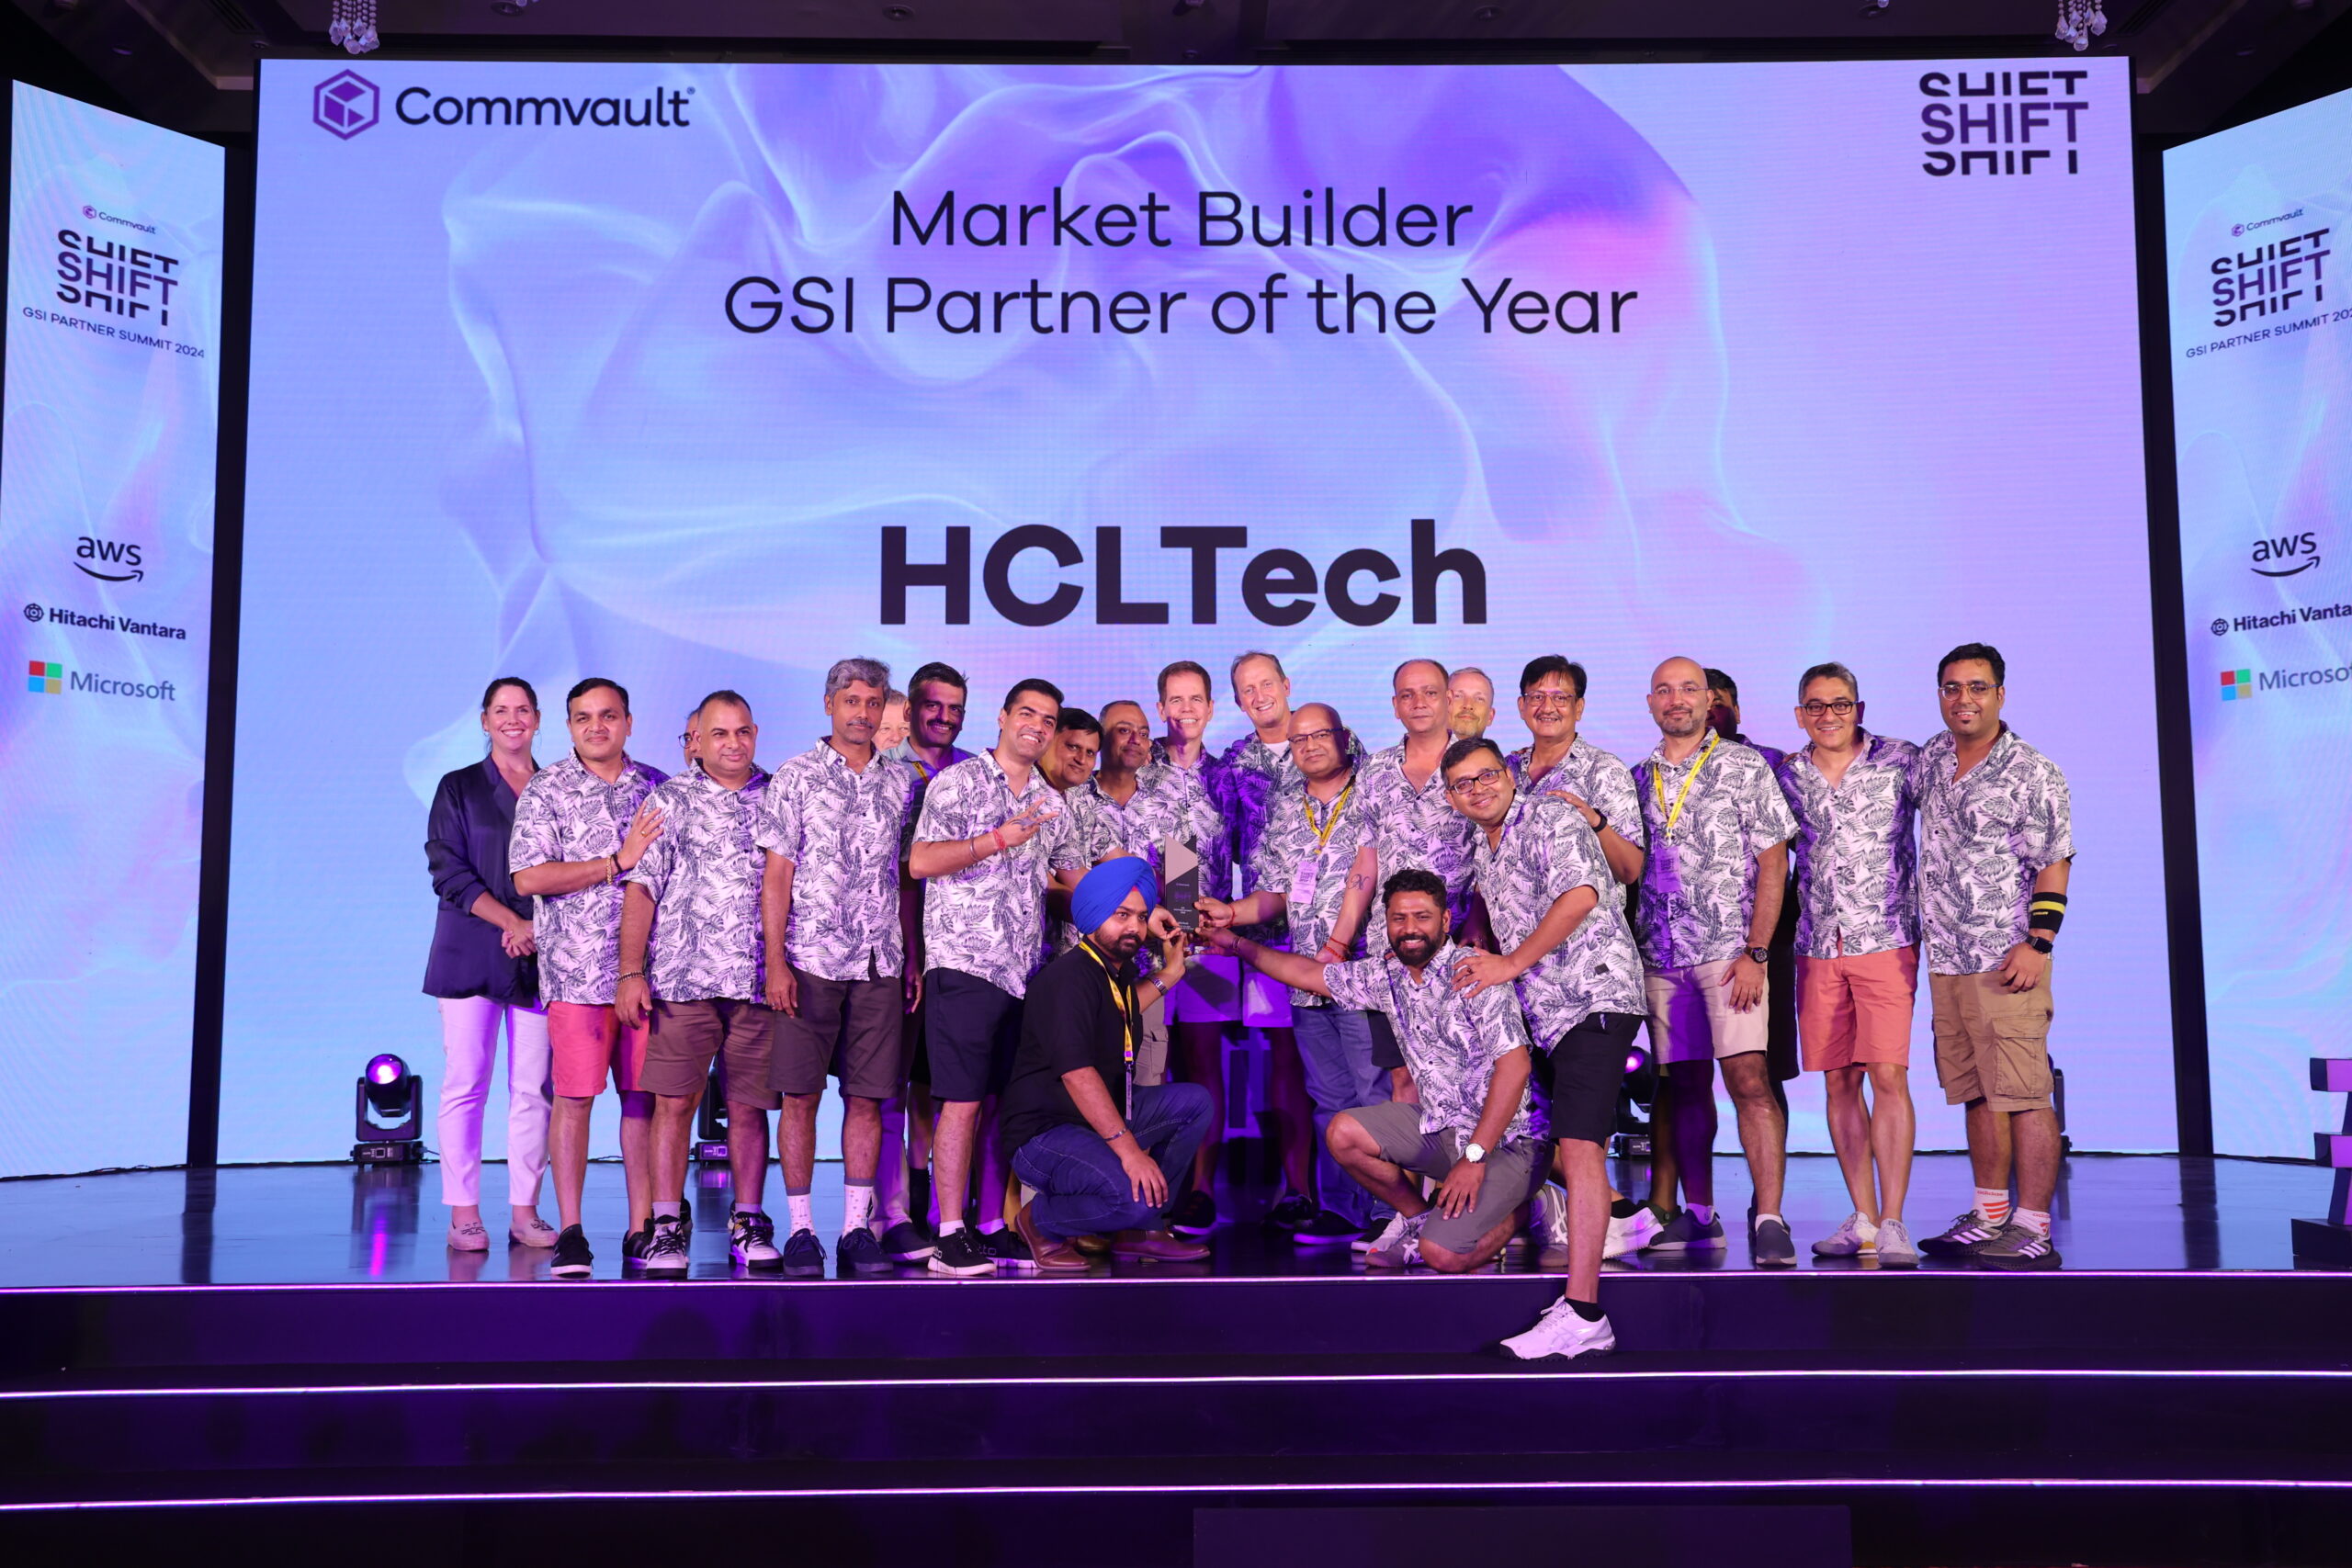
            Market Builder GSI Partner of the Year Award – HCLTech

            HCLTech is awarded our Market Builder Partner for consistently championing Commvault solutions to enable true cloud cyber resilience across hybrid environments in diverse industries and markets. Its VaultNXT offering, powered by Commvault Cloud, exemplifies the power of partnership to address customer needs.

            Resilience Trailblazer Partner of the Year Award – HCLTech

            HCLTech is also commended as our Resilience Trailblazer Partner this year for their exceptional leadership in leveraging Commvault solutions to build cyber resilience for the entire lifecycle of enterprise data. We highlight here their innovative deployment of Threatwise™ to proactively identify silent threats, minimize data exposure, and respond faster using cyber deception technology. Their holistic approach to data readiness and defense raises the bar across industries.


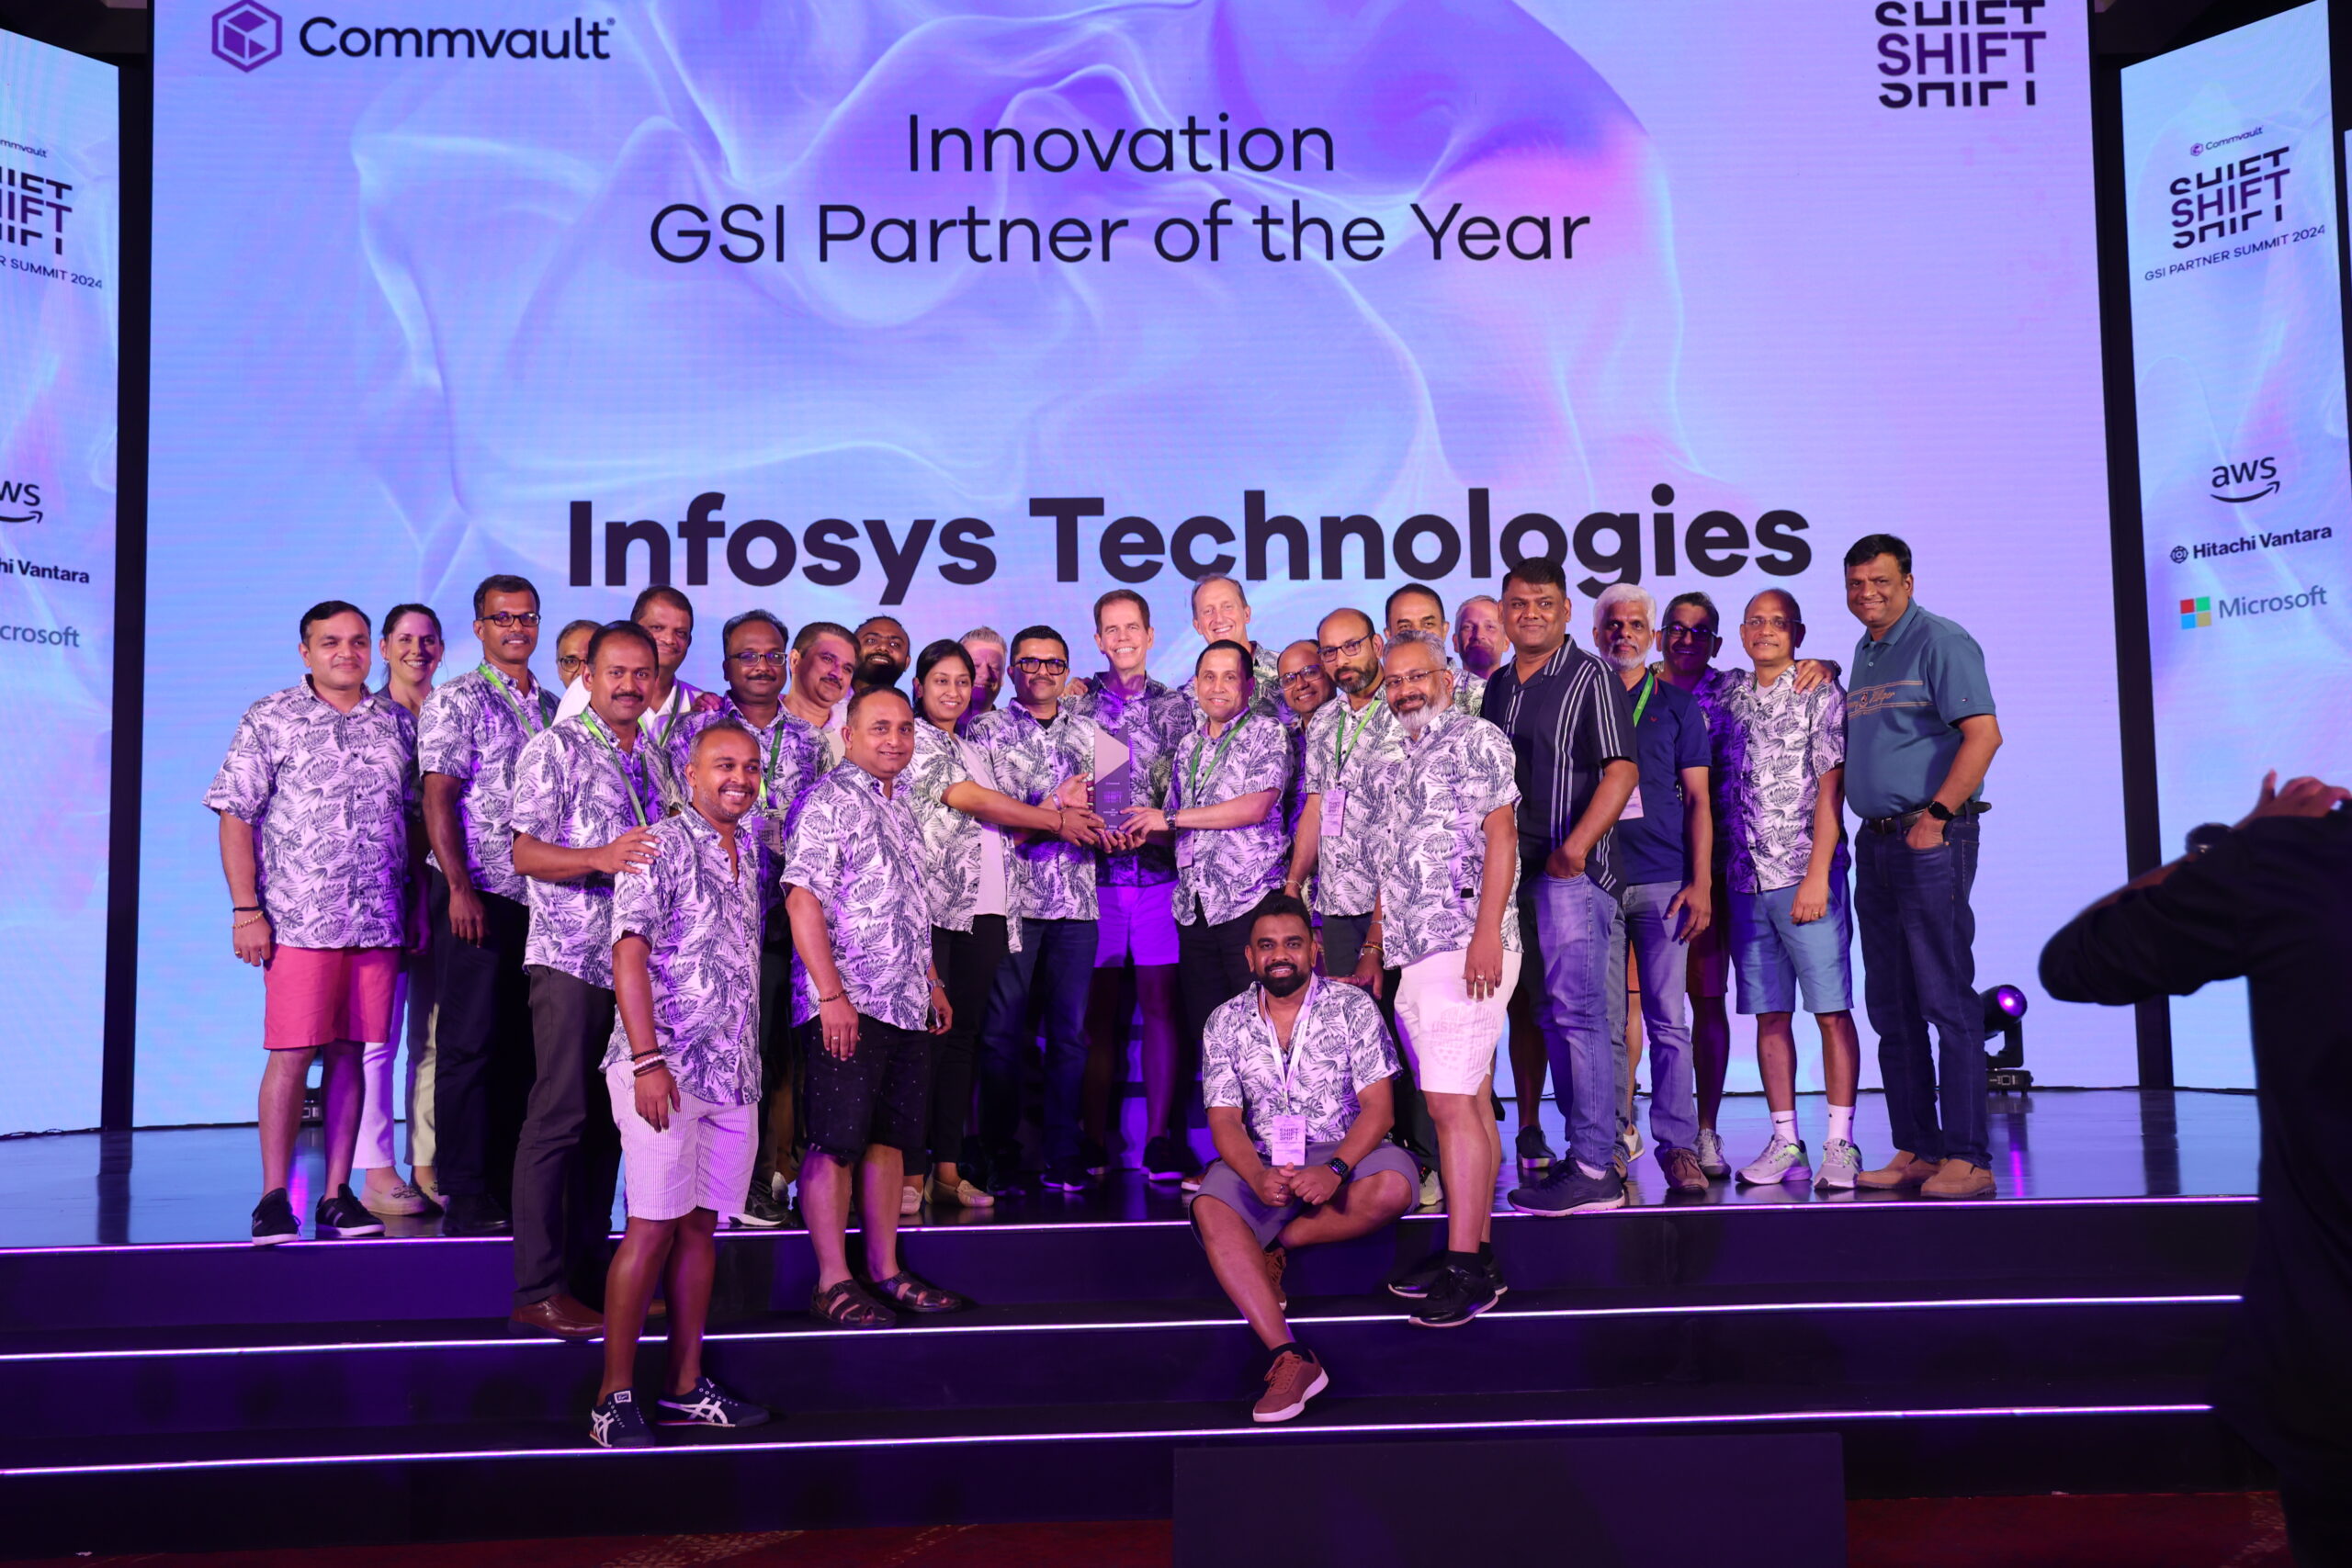
            Innovation GSI Partner of the Year – Infosys

            Infosys is recognized for its vision in being one of our first GSI partners to adopt Commvault Cloud Cleanroom Recovery as a core component of its Data Resiliency Services. Its on-demand services not only address enterprises’ imperative to protect mission-critical data as they accelerate digital transformation and cloud-first strategies but also illustrate the importance of a cloud-based, simple delivery model.

            Momentum GSI Partner of the Year – Kyndryl

            Kyndryl is honored for developing a distinctive strategy to protect and recover sensitive data across hybrid environments with Commvault Cloud solutions. Its forward-thinking strategies address current industry demands and anticipate future challenges, setting a new benchmark for collaborative solution development.

            Strategic services GSI Partner of the Year – Tata Consultancy Services

            TCS is commended as our Strategic Services Partner of the Year for establishing Commvault as a pivotal partner in executing long-term strategies for cyber resilience, compliance, and data management for enterprises across the globe.

            Expansion GSI Partner of the Year – Tech Mahindra

            Tech Mahindra is recognized for its expansion of Commvault Cloud solutions into high-growth emerging markets and building transformative cyber resilience programs for customers across diverse industries.  

            Pathfinder GSI Partner of the Year – Wipro

            Wipro is honored as our Pathfinder Partner of the Year for establishing Centers of Excellence (COE) that highlight the imperative for cybersecurity and resilience leveraging Commvault solutions. Its exceptional client wins working with Commvault and the COEs highlight the immense potential for joint innovation with Commvault.

            Individual Award

            Mountain Mover Award – Ankit Jain, Manager, HCLTech

            Ankit brings extensive experience and a deep understanding of the end-to-end cyber resilience solutions Commvault provides in relation to customers’ IT environments. His ability to overcome roadblocks has played a pivotal role in securing numerous significant and complex wins. Commvault celebrates his trusted role in advising customers and advocating for our cyber resilience solutions.

            Customer Champion Award – Sukumar Rajamanikkam, TCS

            Sukumar is honored with our Customer Champion Award for his unwavering commitment to enabling customer success and satisfaction with Commvault solutions. His expertise with the Commvault Cloud platform and dedication to delivering exceptional customer satisfaction has significantly enhanced our joint customers’ experiences and results.

            Spirit of Resilience Award – Satheesh Tammaji and Mohit Jain, Infosys

            Satheesh and Ankit are honored for their exceptional ability to inspire change in customers approach to security and cyber resilience. Their strategic positioning of Commvault solutions has transformed customers’ data resilience and ability to move faster in their cloud journeys. 

            Our ecosystem of partnerships play an important role in keeping Commvault at the forefront of innovation and anticipating the needs of enterprise customers across industries and use cases. We thank all our partners in making our second annual GSI Partner Summit a resounding success.

            Learn more about our GSI partners here.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            The clock is ticking. The moment you realize your systems are under a ransomware attack, every second counts. The first 24 hours are critical in determining the extent of the damage, mitigating further losses, and setting the stage for recovery. This guide provides a concise action plan to help you navigate this crucial period.

            Critical First Steps

            The first hour after a ransomware attack is so important. Your immediate actions should include the following:

            Immediate Response (First 2-4 Hours)

            • Containment: Prioritize and disconnect infected systems from the network to prevent further spread. This may involve shutting down servers, disabling network segments, and enabling firewall rules to block malicious traffic.
            • Isolate: Physically or virtually isolate critical systems and data stores to limit the impact of the attack.
            • Identify & Triage:Triage critical systems by identifying them and prioritizing their restoration on a clean network. Stage these systems for forensic analysis and identify the accounts involved in the breach.

            Rapid Followup Response (4-6 Hours)

            • Activate: Launch your Incident Response plan (IRP) and assemble your core response team (IT, security, legal, and communications).
            • Assess: Identify the scope of the attack, including affected systems, the type of ransomware involved, and any ransom demands.
            • Secure Backups: Isolate and verify your backups. Confirm they are offline, inaccessible to attackers, and usable for recovery.
            • Communicate: Establish internal and external communication channels to keep stakeholders informed.

            Ongoing Actions (0-24+ Hours)

            • Document:Meticulously document all actions, observations, and communications. This record will be crucial for investigations and recovery, including post-incident forensic analysis. Thoroughly collect all available digital footprints and logs.
            • Investigate: Conduct a thorough investigation to determine the root cause of the attack and identify any vulnerabilities that need to be addressed.

            Containing the Damage and Planning Your Response (6-24+ Hours)

            Once you’ve taken those first steps, you can shift your focus to the following actions.

            • Engage Cyber Insurance: If you have cyber insurance, notify your provider immediately. They can offer valuable guidance, resources, and financial support.
            • Report to Law Enforcement: Contact relevant law enforcement agencies, such as the FBI or your local cybercrime unit, to report the incident.
            • Enlist Cybersecurity Experts: If you lack in-house expertise, bring in cybersecurity specialists. They can assist with malware analysis, advanced containment strategies, and recovery planning.
            • Communication Strategy: Establish a clear communication plan. Keep employees, customers, and stakeholders informed with transparent and timely updates.
            • Recovery Options: Evaluate your recovery options documented in your cyber recovery plan. This may include:
              • Restoring from backups (confirm they are accessible, clean, and verified).
              • Consulting with legal counsel about the possibility of negotiating with attackers (proceed with extreme caution).

            Recovery and Building Resilience (24-48+ Hours)

            The focus of the next 24 hours shifts to actively recovering your systems and implementing measures to improve your security posture:

            • Activate your cyber recovery plan. This might involve restoring from backups and rebuilding affected systems. Consider restoring to a cleanroom environment to keep restored systems and data free from any persistent threats‌. Prioritize critical systems and data to minimize downtime and business disruption.
            • Strengthen your security measures. Take steps to helps reduce future attacks by patching vulnerabilities, updating security software, and implementing multi-factor authentication. Review your security policies and procedures to identify any weaknesses that may have contributed to the attack.
            • Conduct a thorough post-incident review. Analyze the attack to understand how it happened, identify vulnerabilities in your systems, and improve your incident response plan for future events. This review should involve all key stakeholders and lead to actionable changes.
            • Consult with legal counsel. Comply with relevant laws, such as data breach notification laws. Explore potential legal actions against the perpetrators.
            • Maintain vigilance. Continue to monitor your systems for any signs of reinfection or suspicious activity. The threat landscape is constantly evolving, so adapt your security measures accordingly.

            Post-Recovery Actions (Ongoing)

            Recovering from a ransomware attack is a significant undertaking, but the work doesn’t end once your systems and data are restored. Post-recovery is an ongoing process that starts within the first 24 hours and continues throughout the recovery journey. Here’s what it entails:

            • Immediate Post-Incident Analysis (Within 24 Hours): Begin preliminary analysis immediately to gather initial insights into the attack’s origin, methods used, and immediate vulnerabilities. This early analysis informs urgent security enhancements.
            • Ongoing Security Enhancement (Throughout Recovery): Continuously strengthen your security posture based on evolving findings from the ongoing investigation. This may include:
              • Strengthening access controls and authentication measures.
              • Patching vulnerabilities and updating software.
              • Enhancing network security with firewalls, intrusion detection systems, and advanced threat protection tools.
              • Implementing email security solutions to filter malicious attachments and links.
              • Improving endpoint security with antivirus, anti-malware, and endpoint detection and response (EDR) solutions.
            • Employee Training (Ongoing): Reinforce cybersecurity awareness among employees through continuous training and education. Focus on topics such as phishing scams, social engineering, password security, and safe browsing habits.
            • Policy and Protocol Updates (Ongoing): Regularly review and update security policies and protocols based on new information and industry best practices. Confirm they are aligned with regulatory requirements.
            • Backup and Recovery Review (Ongoing): Continuously evaluate and improve your backup and recovery strategy. Check that you have frequent, reliable backups that are stored securely and tested regularly. Consider immutable backups that cannot be altered or deleted by attackers.
            • Cyber Recovery Plan Refinement (Ongoing): Regularly refine your cyber recovery plan based on your experience and evolving threats. Identify areas for improvement and confirm that your plan is up to date and comprehensive.
            • Ongoing Monitoring: Maintain vigilance and continuously monitor your systems and networks for suspicious activity. Leverage security information and event management (SIEM) tools and threat intelligence to proactively identify and respond to potential threats.

            By adopting this ongoing approach to post-recovery, you can continuously improve your organization’s security posture and resilience against future attacks.

            Key Takeaways

            Cyber Recovery Plan: A well-defined cyber recovery plan minimizes downtime, helps to enable continuous business, and reduces the risk of reinfection. It creates a framework for increasing your organization’s cyber resilience or ability to restore access to functionality of critical IT systems and data in the event of a cyberattack.

            • Incident Response Plan: Outlines the steps to take during an attack, including communication protocols, escalation procedures, and roles and responsibilities.
            • Cyber Recovery Plan: Focuses on restoring critical systems and data after an attack.
            • Business Continuity Plan: A broader plan that addresses how to maintain essential business operations during any disruption, including ransomware attacks.

            Act Decisively: The first few hours are critical. Rapid response and containment can significantly limit the damage and improve your chances of a successful recovery.

            Learn and Improve: Every attack is a learning opportunity. Conduct a thorough post-incident analysis to understand what happened, why it happened, and how to prevent it from happening again. Continuously strengthen your security posture and cyber resilience.

            A Final Word

            Navigating a ransomware attack demands decisive action and a commitment to cyber resilience. This starts with developing comprehensive incident response, cyber recovery, and business continuity plans today. Remember that cyber resilience is an ongoing journey. Regularly review and refine your plans, strengthen your security posture, and educate your team. By taking a proactive approach, you can increase your chances of withstanding and recovering from cyber threats. Don’t wait for an attack to happen. Take the first step toward a more secure future.

            Want to be even more prepared?

            Ransomware attacks can be devastating, but with the right planning and preparation, you can significantly reduce the impact. To learn more about building a robust cyber resilience plan, consider attending our Cyber Resilience Planning Workshop. This interactive workshop, offered in cities worldwide, guides participants through the process of creating a comprehensive cyber recovery plan. Using real-world scenarios, the workshop helps organizations develop strategies to withstand and recover from cyberattacks.

            Sign up for a workshop today and take a proactive step toward protecting your organization.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            As the executive sponsor of Commvault’s Veterans Employee Resource Group (VALOR ERG) and U.S. Navy Veteran, I wanted to share my perspective on the significance of Veterans Day and Remembrance Day.  

            Today, November 11, is Veterans Day and Remembrance Day, memorial days tied to Armistice Day, which marked the end of World War I. This day honors both living and lost Veterans who have served their country. Here at Commvault, we’re proud to recognize the sacrifices made by Veterans and their families, and remain humbled by their selflessness and courage.

            We are fortunate to have Veterans among us in our global Vaulter community, and as a Veteran, I know firsthand how our shared experiences in service place a high value on teamwork and informed and inspiring leadership. We draw on these values as we share traditions and memories, and build new relationships. 

            Each year, our VALOR ERG hosts an Honor Hour virtual event to reflect on the sacrifices Veterans have made for our freedoms. These conversations provide our Vaulters with an open dialogue to express what this day means to them personally, acknowledge and remember our histories, reflect on our own experiences with Veterans, and show our gratitude.

            And as part of our Commvault Cares Quarter of Caring initiative, our VALOR ERG is partnering with the Tunnel to Towers Foundation to support all those who have served, as well as their families, especially in the upcoming holiday season. Seeing all the incredible support across our company makes me so proud to be a part of Commvault. 

            I encourage you to take a moment today to reflect on and honor the dedication and resilience of all Veterans who have served their country. Thank you to our Veterans and their families for the sacrifice you have made to keep us all free and safe. 

            Click here to learn more about our diversity, equity, and inclusion efforts at Commvault.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Here at Commvault, our values – we connect, we inspire, we care, and we deliver – are foundational to everything we do and why it matters.

            This week, we hosted our quarterly internal Global Town Hall meeting and presented our FY25 Q2 CEO Living Our Values Awards. This award program globally recognizes and celebrates our Vaulters for their incredible work and for living our values each day.

            I’m so proud to announce our FY25 Q2 CEO Living Our Values Award winners and our employee-nominated Vaulters Choice Award winner below.

            CEO Award Winners

            Haseeb Jawad 

            Michele Dellaventura

            Abhishek Praveen

            Global Events Team

            Kristin Murphy

            Kelly Suffness

            Lauren Whitaker

            Cecily Russell

            Vaulters Choice Award Winner 

            Gregory Jackamonis

            These Vaulters set an inspiring example of what it truly means to be a part of Commvault.

            To learn more about what it is like to work at Commvault, check out our careers site.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Cloud-based applications are the backbone of many businesses, relying heavily on a complex ecosystem of technologies. These applications aren’t just standalone entities – they encompass a variety of components, including virtual machines, containers, networks, subnets, security groups, secondary storage, and serverless functions. Each element plays a critical role in ensuring that cloud applications run smoothly and efficiently.

            However, the resilience of these applications often comes into question, especially when faced with the limitations of standard backup products. Traditional backup solutions typically focus on safeguarding virtual machines and some aspects of storage. This approach, while foundational, falls short of addressing the comprehensive needs of modern cloud applications, which are far more intricate and interconnected.

            Enter Commvault Cloud Rewind, a revolutionary solution designed to bridge this gap. Commvault Cloud Rewind goes beyond traditional backup paradigms by offering an automated system that can inventory, backup, and restore an entire cloud application, along with all its dependencies. This isn’t just about data recovery – it’s about continuous business and enabling restores of an entire operational setup.

            The significance of this kind of capability can’t be overstated, particularly for organizations that leverage public clouds to run their key applications. In the event of a ransomware or malware attack, the ability to restore a cloud application to a point before the attack helps to minimize downtime and operational disruption. This is crucial for maintaining trust and reliability with your customers.

            Moreover, Commvault Cloud Rewind facilitates the creation of exact replicas of cloud applications. This feature is invaluable for testing or development purposes, allowing developers and IT professionals to test changes and updates to the cloned environment without risking the integrity of the live environment. It supports agile development practices and promotes a more robust testing culture within organizations.

            To illustrate the power and efficiency of Commvault Cloud Rewind, check out the demo video below. This video showcases the quick and complete recovery of an application running in Amazon Web Services, from one region to another, in mere minutes. The demo highlights the practical benefits and the technical prowess of Commvault Cloud Rewind, making it a compelling choice for businesses looking to enhance their cloud application resilience.

            For anyone interested in trying out Commvault Cloud Rewind firsthand, visit our website for a free trial. This trial offers a hands-on opportunity to explore how Commvault can transform the way your business thinks about and manages its cloud application resilience.

            As businesses continue to navigate the complexities of cloud environments, solutions like Commvault Cloud Rewind are essential. They not only provide the tools needed to help protect and restore critical applications but also empower organizations to innovate and grow with confidence in their cloud strategies.


            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            If you work in IT and security, there’s nothing more frightening than a data breach. It’s the last day of Cybersecurity Awareness Month – and Halloween in many parts of the world. And a demand for candy beats a demand for ransom every time. Here are our top tips to scare away the bad guys all year long:

            1. Be Unique

            You wouldn’t wear the same costume year after year … would you? Use a password manager to generate and store complex password s for each of your accounts.

            2. Add a Layer of Protection

            Throwing a winter coat over my costume may have ruined a few Halloweens growing up in chilly New England, but using Multi-Factor Authentication to protect your online accounts provides added reassurance.

            3. Stay Up to Date

            Don’t be haunted by the ghosts of employees past. Regularly update your permissions as well as your software, apps, and operating systems. And install security patches to protect against known vulnerabilities.

            4. Be Cautious of Phishing Scams

            The only acceptable phishing is for the good candy in the treat bag. Don’t click on suspicious links or download attachments from unknown sources. Always verify the sender’s email address. (Learn more from The Resilience Rundown podcast episode Fighting Phishing.)

            5. Limit Social Media Sharing

            It’s tempting to post everything about your little ghosts and goblins, but be cautious. Cybercriminals can glean personal information to guess your passwords or answer security questions. (Watch our Social Media episode of the Strive podcast for more safety tips.)

            6. Protect Yourself From Viruses

            Want to stay healthy? Install reputable antivirus and anti-malware software on your devices – and for pete’s sake, don’t bob for apples at a preschool party.

            7. Report Suspicious Activity

            Halloween pranks may be harmless, but cybercrime can have serious repercussions. If you suspect you’ve been a victim, report it to your local law enforcement and national cybercrime agencies.

            There’s no sugarcoating the facts: Malicious attacks can happen at any time. You must remain vigilant to protect your organization from wolves in sheep’s clothing all year long. Follow these tips to significantly improve your online security and help protect yourself and your data from cyber threats.

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            In an increasingly interconnected world, the importance of robust regulatory frameworks to increase the stability and security of financial systems cannot be overstated. The European Union’s Digital Operational Resilience Act (DORA) is a significant regulatory development aimed at enhancing the operational resilience of financial entities. This blog explores how DORA compares to other major regulations globally, highlighting its unique features and the broader implications for the financial industry.

            Understanding DORA

            The European Commission introduced DORA as part of the Digital Finance Package in September 2020. Its primary objective is to enhance the ability of financial institutions to withstand, respond to, and recover from all types of ICT-related disruptions and threats. DORA applies to a wide range of financial entities, including banks, insurance companies, investment firms, and third-party ICT service providers.

            Key components of DORA include:
            1. ICT risk management: Financial entities must implement comprehensive ICT risk management frameworks to identify, assess, and mitigate risks.
            2. Incident reporting: Mandatory reporting of significant ICT-related incidents to competent authorities.
            3. Digital operational resilience testing: Regular testing of ICT systems to enable resilience against disruptions.
            4. Third-party risk management: Enhanced oversight of third-party ICT service providers to hold them to resilience standards.
            5. Information sharing: Encouragement of information sharing among financial entities to improve collective resilience.

            Comparing DORA to Other Regulations and Industry Best Practices

            1. NIST Cybersecurity Framework (United States)

            The National Institute of Standards and Technology Cybersecurity Framework is a voluntary framework that provides guidelines for managing and reducing cybersecurity risks. While not a regulatory requirement, it is widely adopted by U.S. financial institutions.

            • Scope: Unlike DORA, which is mandatory for EU financial entities, the NIST framework is voluntary and can be applied to any industry.
            • Focus: Both frameworks focus on broader cybersecurity risk management practices, with DORA placing significantly more focus on operational resilience.
            • Incident reporting: DORA mandates incident reporting, while NIST encourages it but does not require it.
            2. GDPR (European Union)

            The General Data Protection Regulation another significant EU regulation, primarily focused on data protection and privacy.

            • Scope: GDPR applies to all organizations processing personal data of EU citizens, while DORA is specific to financial entities.
            • Focus: GDPR emphasizes data protection and privacy, whereas DORA focuses on operational resilience and ICT risk management.
            • Incident reporting: Both regulations require incident reporting, but GDPR focuses on personal data breaches, while DORA covers a broader range of ICT incidents.
            3. Basel III (Global)

            Basel III is a global set of international regulatory standards developed by the Basel Committee on Banking Supervision to strengthen regulation, supervision, and risk management within the banking sector. The EU is implementing the Basel III framework beginning January 1, 2025, while the implementation in United States and United Kingdom is likely to be delayed.

            • Scope: Basel III is specific to internationally active banks, while DORA applies to a wider range of financial entities.
            • Focus: Basel III focuses on capital adequacy, stress testing, and market liquidity risk, whereas DORA focuses on ICT risk management. Both address operational resilience.
            • Incident reporting: Basel III does not specifically mandate ICT incident reporting, unlike DORA.
            4. FCA Operational Resilience Framework (United Kingdom)

            The Financial Conduct Authority in the UK has its own operational resilience framework, which shares similarities with DORA.

            • Scope: Both frameworks apply to financial entities, but the FCA framework is specific to the UK.
            • Focus: Both frameworks emphasize operational resilience, but DORA has a broader scope, including third-party risk management and information sharing.
            • Incident reporting: Both frameworks require incident reporting, but DORA has more detailed requirements.

            Implications for the Financial Industry

            The introduction of DORA represents a significant step toward enhancing the operational resilience of financial entities in the EU. By mandating comprehensive ICT risk management, regular resilience testing, and robust incident reporting, DORA aims to mitigate the impact of ICT-related disruptions on the financial system.

            For financial entities operating globally, compliance with multiple regulatory frameworks can be challenging. However, the principles of DORA align with many existing regulations and industry best practices, such as the NIST Cybersecurity Framework and the FCA Operational Resilience Framework. This alignment can facilitate a more integrated approach to managing ICT risks and operational resilience. As long the main capabilities required by DORA are addressed, financial entities remain free to use ICT risk management models that are differently framed or categorized.

            Conclusion

            DORA sets a high standard for operational resilience in the financial sector, with its comprehensive approach to ICT risk management, incident reporting, and third-party oversight. While it shares similarities with other regulations, its mandatory nature and broad scope make it a unique and influential regulatory framework. As the global regulatory landscape continues to evolve, financial entities must stay informed and adapt to maintain compliance and resilience in an increasingly digital world.

            Learn more about how you can prepare for the Digital Operational Resilience Act in our Exploring DORA blog series:
            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Welcome to the first in our three-part blog post series on Microsoft Active Directory data backup and recovery. This series will explore the criticality of AD in your resilience strategy and considerations for protection. Let’s begin with an introduction of why AD is so important.

            Ransomware has become a perpetual game of cat and mouse. As IT and security teams strive to stay one step ahead, threat actors ruthlessly mine for new methods, means, and vectors for their exploits. Their latest focus is AD. As a core element of centralized management, AD has become a primary target and pathway to execute ransomware attacks. Now more than ever, it’s critical that today’s businesses consider AD protection in their overarching security and ransomware response strategies.

            The Keys to the Castle

            As a widely adopted authentication tool for small, medium, and enterprise businesses, Microsoft AD and Entra ID are the gatekeepers of authorization processes for networks, applications, and environments. AD is the quarterback of system access and controls an ever-changing pool of users, groups, policies, and app permissions.

            While AD simplifies the administration of access to key systems, it can be particularly challenging to secure as it holds the keys to an organization’s most crown jewels – its infrastructure and data. It also has become a data protection blind spot for many organizations. One misconfiguration, leaked password, or dormant account can enable a bad actor to elevate privileges and steal, corrupt, or deny access to critical applications and their data.

            Numerous workloads within companies depend on AD to grant employees access to critical business systems that are essential for generating revenue, delivering patient care, maintaining manufacturing operations, and supporting nonprofit initiatives. Without AD, business operations would grind to a halt.

            Propagating an Attack

            Experts are finding AD is playing a key and increasingly larger role in executing attacks. In fact, a study by EMA Research showed that 50% of organizations experienced an attack on AD/Entra ID in the last one to two years. By exploiting blind spots, bad actors can compromise privileged accounts, mimic authorized users, and silently traverse infrastructure, workstations, and applications to establish their foothold. Failing to safeguard AD enables attackers with a centralized location to control and sever access to critical business assets.

            How Commvault Helps

            Safeguarding AD from ransomware requires purpose-built tools to recover from attacks. And while some businesses have developed homegrown solutions, they are time-consuming to maintain, upkeep, and administer. With Commvault Cloud, you get dedicated, single-solution protection for Microsoft AD and Entra ID to help quickly restore your data.

            Frequent backups enable users to undo damaging and unwanted changes to objects and attributes, including users, groups, app registrations, and more. Fast, granular recovery options allow administrators to view what’s changed in their environment and easily recover missing, damaged, or misconfigured items to thwart ongoing attacks.

            Visit Commvault.com/platform/active-directory to learn more about how Commvault helps safeguard AD against corruption, accidental deletion, or malicious attacks. 

            More related posts


            person-escalator-crocus-888×500

            Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

            Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
            Thumbnail_Blog-Architect-for-tomorrow-2026

            Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

            Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience
            Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

            The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

            Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan