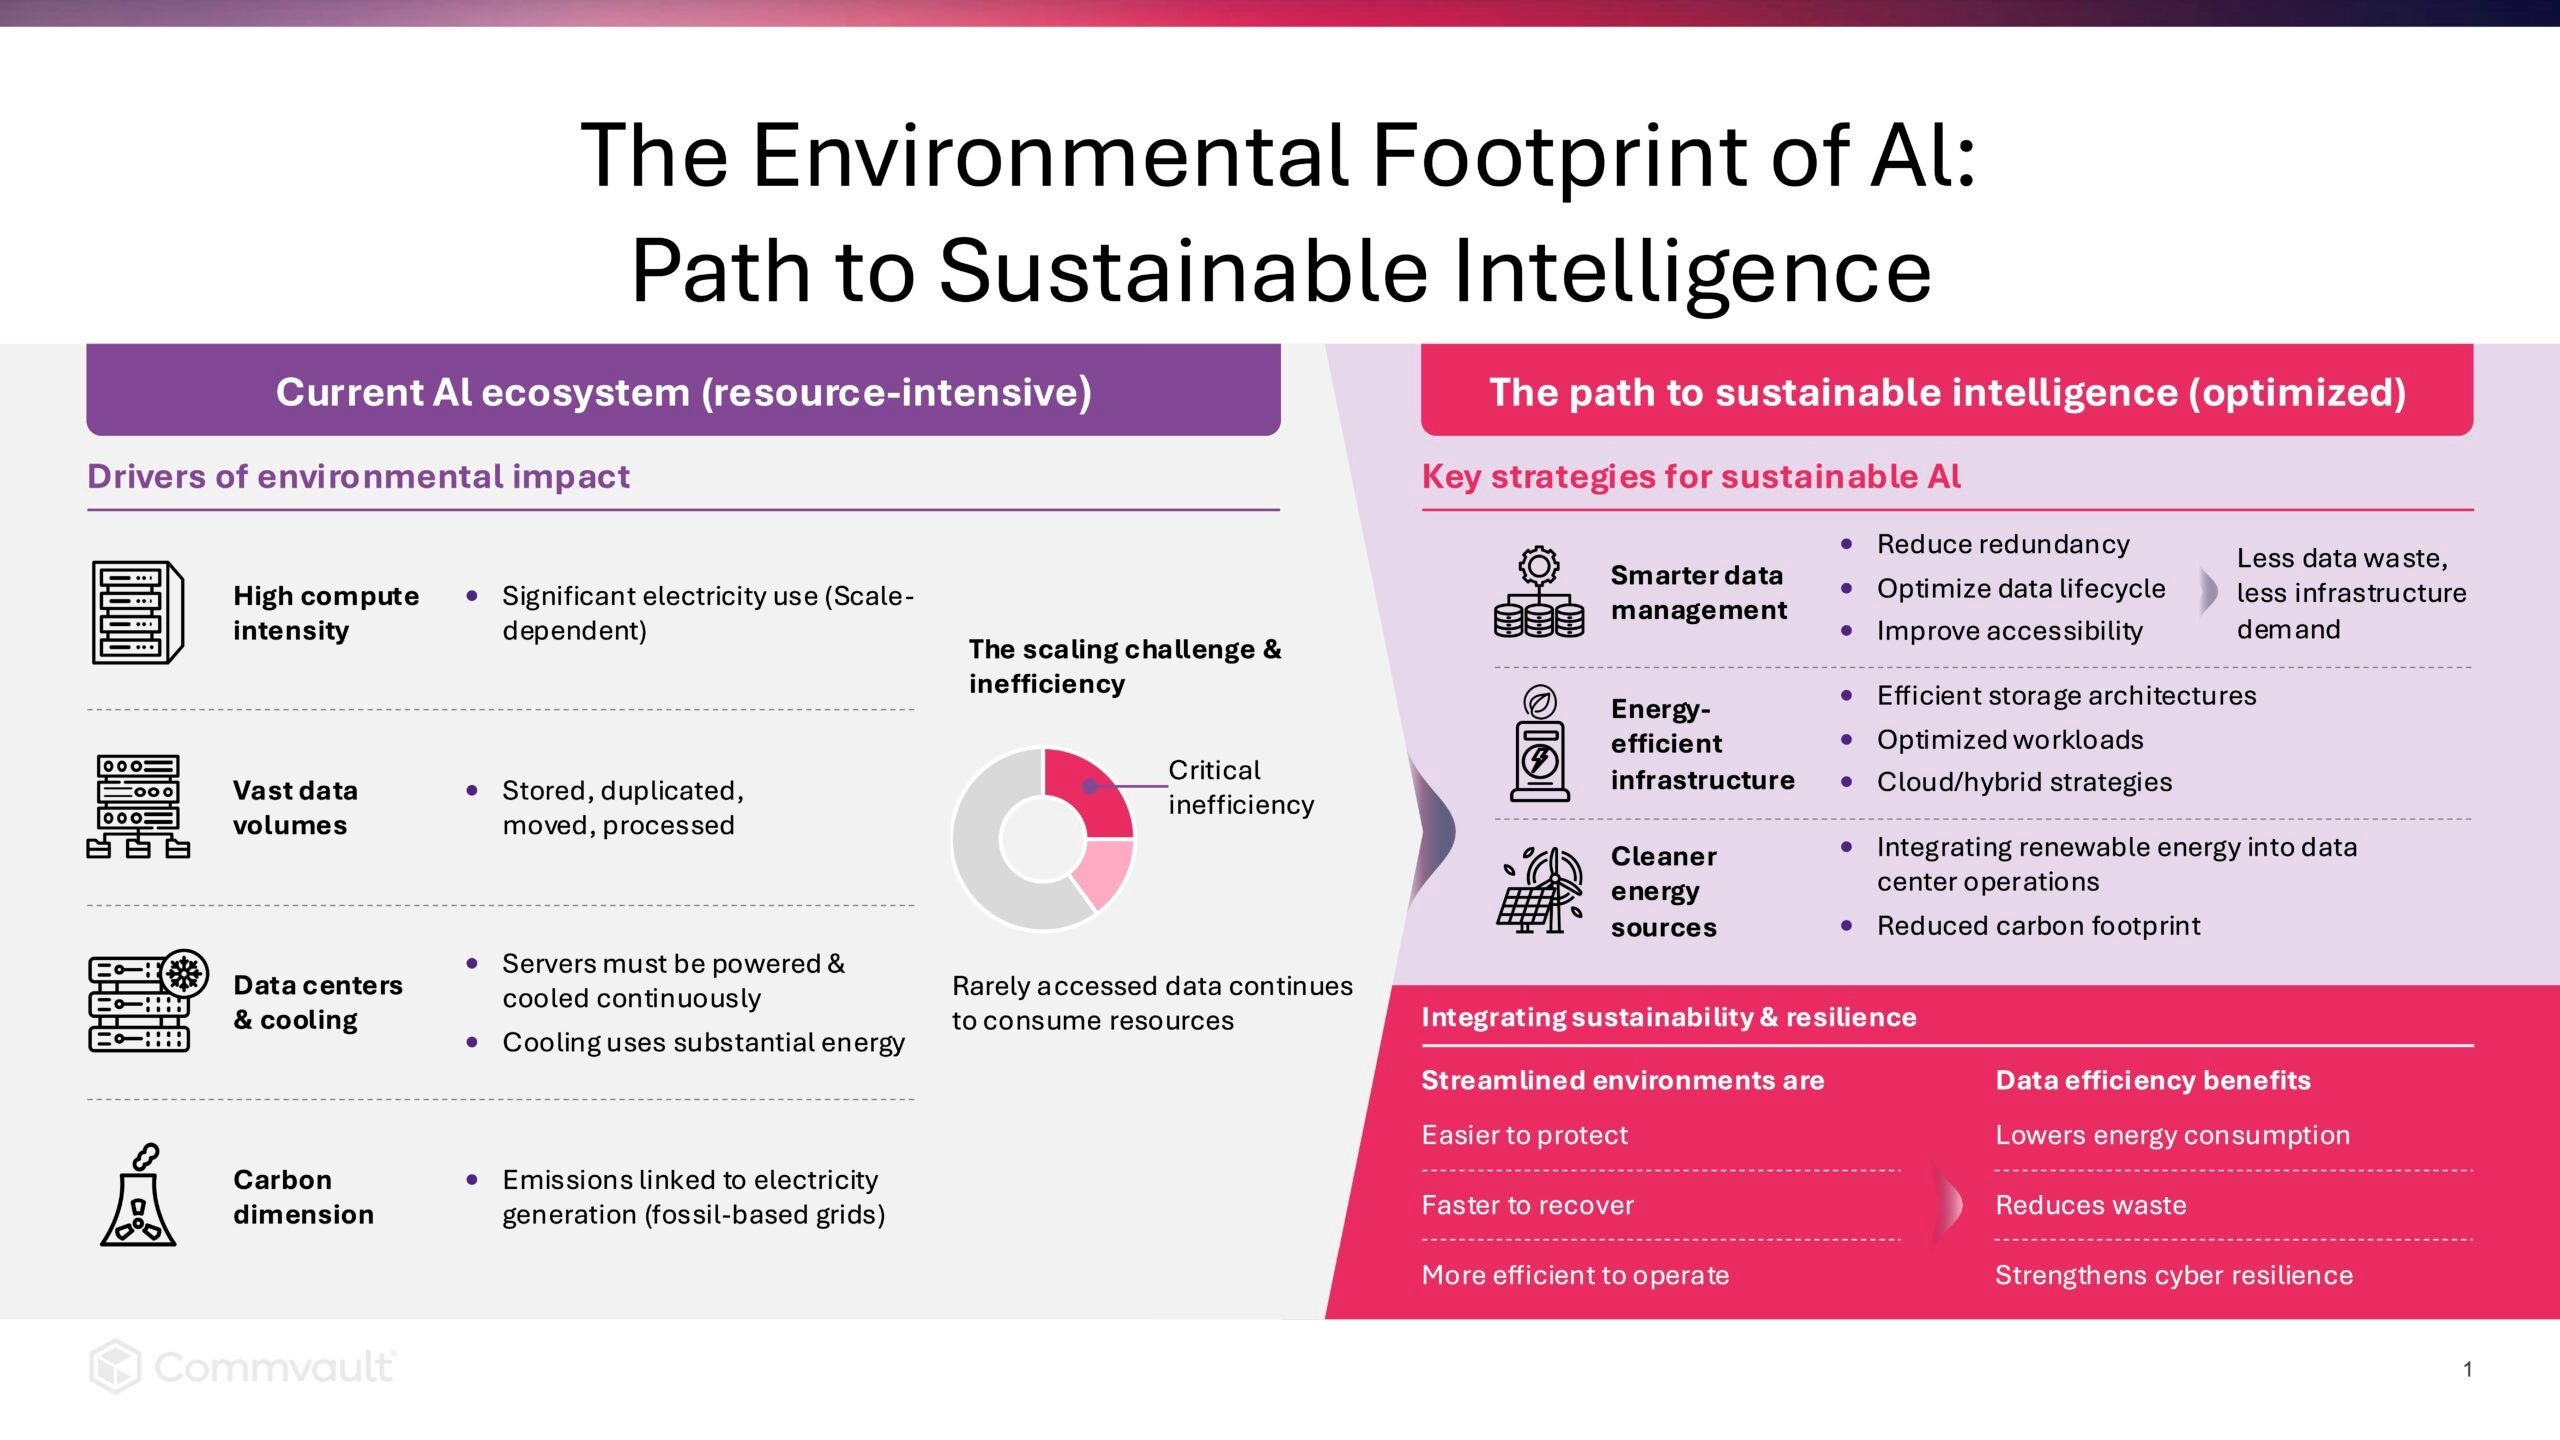
Die wichtigsten Erkenntnisse
- Bei der „Minimum Viable Sovereignty“ (MVS) geht es darum, für die jeweiligen Workloads das richtige Maß an Kontrolle anzuwenden.
- Die Gleichbehandlung aller Workloads kann zu unnötiger Komplexität und Kosten oder zu unzureichendem Schutz führen.
- Unternehmen lassen sich in der Regel in drei Souveränitätsprofile einteilen: „True Sovereign“, „Regulated Enterprise“ und „Hybrid Multi-Cloud“.
- Eine einheitliche Governance über gemischte Umgebungen hinweg ist eine der größten betrieblichen Herausforderungen.
There is a version of the digital sovereignty conversation that leads organizations somewhere expensive, operationally burdensome, and – if they’re being honest – further than their actual obligations require. Maximum sovereignty sounds responsible. In practice, it’s often a miscalibration.
There is an equally common version that leads somewhere dangerously thin – controls that satisfy a checklist but wouldn’t survive an audit, an incident, or a regulator who has stopped accepting documented intent as proof of demonstrated control.
The organizations that get sovereignty right tend to do something more rigorous and more practical than either extreme: They ask what they actually owe, to whom, and for what. Then they build to that standard – no more, no less.
This is the discipline of MVS, introduced in the „„Digital Sovereignty Readiness Report““ and developed in full here.
MVS isn’t a shortcut. It’s a recognition that the goal is the right level of control, applied consistently, across every workload that requires it.
Nicht alle Workloads sind gleich
The starting point for an MVS approach is workload classification – and most organizations skip it entirely.
A trading system processing regulated financial data carries fundamentally different sovereignty obligations than an internal HR collaboration tool. A database holding personal data of EU citizens is subject to a different legal and regulatory regime than a development environment running anonymized test data.
Treating all of these identically – either by applying maximum sovereign controls across the board or by assuming a single deployment model covers everything – is how organizations end up either over-engineered or under-protected.
The right question before any deployment decision: What does this workload require across each of the four sovereignty pillars? The Readiness Report includes a self-assessment structured around exactly that question.
The Three Profiles – and What They Actually Need
Regulierte Unternehmen lassen sich in drei erkennbare Profile einteilen, die jeweils unterschiedliche Hauptantriebsfaktoren und Investitionsprioritäten aufweisen.
- The True Sovereign. Government agencies, defense contractors, and critical national infrastructure operators. For these organizations, sovereignty is not a compliance requirement – it is an operational mandate. Maximum control over every dimension of the technology stack is often legally required, and the cost tradeoffs are accepted because the alternative is not.
- The Regulated Organization. Financial services firms, healthcare organizations, energy companies. These organizations face binding requirements from DORA, NIS2, GDPR, and sector-specific frameworks. Compliance obligations may also map to EU certification schemes – including EUCS, EUCC, BSI C5, and SecNumCloud – depending on sector and deployment context.
on-negotiable in certain areas – particularly around data residency, operational access controls, and recovery within jurisdictional boundaries. But not every workload carries the same obligation.
- The Hybrid Multi-Cloud Organization. Organizations with existing hyperscaler investments facing increasing sovereignty pressure from customers, regulators, or procurement requirements. Their challenge is not wholesale migration – it’s layering sovereign controls onto a mixed estate and maintaining consistent governance across it.
Die Kosten einer falschen Kalibrierung
Over-engineering sovereignty creates its own operational risks. Organizations that apply maximum sovereign controls to workloads that don’t require them absorb cost and complexity that serves no regulatory or business purpose.
Under-engineering is the more common failure mode, and the more dangerous one. It typically doesn’t show up until the audit arrives – or, more seriously, until an incident occurs and recovery becomes a legally constrained problem. (That failure mode is the subject of the vierten Beitrags dieser Reihe) umfasst.
Ein praktischer Ausgangspunkt
Ein MVS-Ansatz umfasst drei Schritte:
- Classify workloads by their actual sovereignty requirements across each pillar – don’t start with deployment models.
- Ordnen Sie jede Workload-Klasse der Bereitstellungsstufe zu, die diese Anforderungen erfüllt, und zwar über das gesamte Spektrum hinweg – von Regionen öffentlicher Hyperscaler über souveräne Public Clouds bis hin zu lokal verwalteten Umgebungen.
- Govern the resulting mixed estate consistently – controls, audit evidence, and recovery capabilities must be demonstrable across the full environment, not just the most-sovereign tier.
The third step is where most programs struggle. Maintaining consistent sovereignty controls across a mixed estate is an operational governance challenge – and specifically the domain of Operational Sovereignty – dem Thema des dritten Beitrags dieser Reihe, der Säule, die in den meisten Strategien erst nachträglich berücksichtigt wird.
Nutzen Sie die Selbsteinschätzung im„„Digital Sovereignty Readiness Report“““, um Ihre aktuelle Situation in allen vier Säulen zu ermitteln.
FAQs
F: Was ist „Minimum Viable Sovereignty“ (MVS)?
A: MVS bezeichnet die Praxis, Souveränitätskontrollen auf der Grundlage tatsächlicher geschäftlicher und regulatorischer Anforderungen anzuwenden. Damit soll sowohl eine übermäßige Komplexität als auch ein unzureichender Schutz vermieden werden.
F: Warum ist die Einstufung der Arbeitsbelastung wichtig?
A: Verschiedene Workloads sind mit unterschiedlichen regulatorischen und betrieblichen Verpflichtungen verbunden. Die Klassifizierung von Workloads hilft Unternehmen dabei, die angemessenen Souveränitätskontrollen anzuwenden.
F: Welche drei gängigen Souveränitätsprofile gibt es?
A: Die drei Profile sind eigenständige Organisationen, regulierte Organisationen und hybride Multi-Cloud-Organisationen. Jede davon unterliegt spezifischen betrieblichen und Compliance-Anforderungen.
F: Welche Risiken ergeben sich aus einer übermäßigen Regulierung der Souveränität?
A: Übermäßige Kontrollen können die Komplexität der Geschäftsabläufe und die Kosten erhöhen, ohne dass dadurch ein nennenswerter Nutzen in Bezug auf die Einhaltung von Vorschriften oder den Geschäftswert entsteht.
F: Warum stellen gemischte Umgebungen eine Herausforderung für die Governance dar?
A: Unternehmen nutzen häufig mehrere Cloud- und Infrastrukturmodelle. Es ist schwierig, in allen Umgebungen einheitliche Kontrollmaßnahmen, Prüfungsnachweise und Recovery-Standards aufrechtzuerhalten.
Ruben Renders ist Solutions Director, MSP, bei Commvault.
 Die automatische Erkennung sorgt dafür, dass neue Berichte und Ordner im Zuge der Weiterentwicklung der Umgebungen berücksichtigt werden, während die zentralisierte Verwaltung eine zentrale Anlaufstelle für die Überwachung, Verwaltung und Wiederherstellung von Daten in großem Umfang bietet.