La Ley de Resiliencia Operativa Digital (DORA) entró en vigor el 17 de enero, con unas directrices exhaustivas y un marco normativo detallado sobre cómo todas las entidades de servicios financieros que operan en la Unión Europea deben garantizar la resiliencia de los datos frente a interrupciones imprevistas.
La DORA también reconoce una realidad ampliamente aceptada por los profesionales de la ciberseguridad: ya no se trata de si se producirá un ciberataque, sino de cuándo. Esta legislación fundamental aporta un nuevo nivel de rigor y responsabilidad al sector de los servicios financieros, que seguirá evolucionando para salvaguardar la estabilidad de la UE y del ecosistema financiero mundial.
Actualmente, muchos sectores de la industria de los servicios financieros, más allá de los bancos tradicionales y las entidades de crédito, están sujetos a la DORA, entre ellos los proveedores de servicios de pago, las empresas de inversión, los centros de negociación, las aseguradoras y los proveedores externos de servicios de tecnologías de la información y la comunicación (TIC).
Those that are new to this level of regulation may struggle to comply, as indicated by European financial regulators’ DORA “Dry Run Exercise.”1 They also likely will face additional scrutiny by interconnected customers, partners and other stakeholders as a new operational risk. Non-compliance no longer means just the potential for a very large fine but also reputational damage and liability for a company, its directors, and its partners.
While it remains to be seen how quickly financial regulators act, DORA represents a shift from guidelines for data readiness and cyber resilience to enforcement of it. Given the expansive nature of DORA, which significantly broadens the EU’s financial regulation of IT, regulators, lacking unlimited expertise and resources, may face challenges enforcing all aspects of DORA immediately. As a result, regulators are likely to adopt a targeted approach, focusing on the most critical and visible areas of noncompliance.
Qué es lo que las entidades financieras están priorizando
A top priority for DORA compliance is the submission of accurate and technically compliant registers of information. Financial regulators have emphasized that registers will be a primary focus of enforcement, and they expect organizations to submit them early in 2025. Submitting an accurate register that details the organization’s most significant IT providers may be more beneficial than submitting incomplete information about all of its IT providers.2
For data protection leaders and CIOs, DORA is a call to action to examine legacy systems and consider whether they are capable of withstanding today’s cyberthreats and can deliver the performance required for efficient, rapid service recovery.
Más allá de identificar y catalogar los sistemas, aplicaciones y cargas de trabajo clave junto con sus respectivos proveedores de TIC, las organizaciones deben analizar detenidamente las capacidades fundamentales que protegen, defienden y recuperan dichos sistemas. Entre las capacidades críticas se incluyen:
- Data protection and cyber recovery
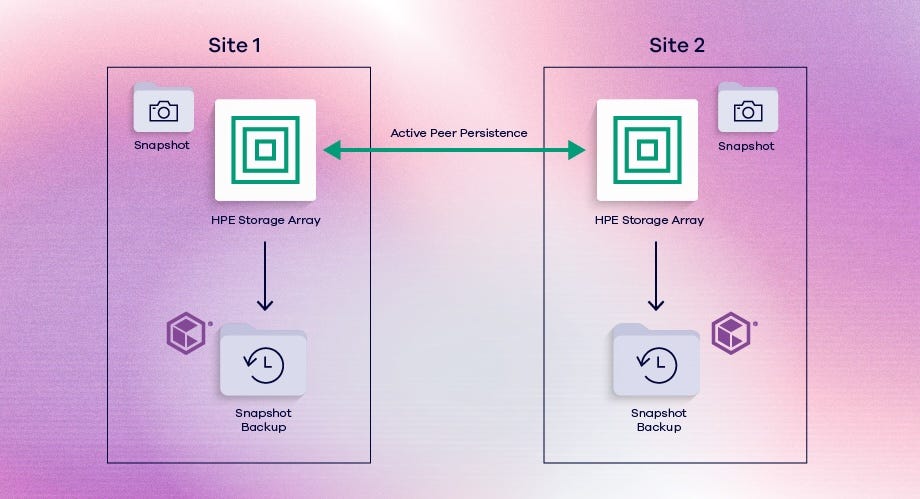
cibernética: Las capacidades de Recovery rápido son esenciales en el marco de la DORA para minimizar el impacto operativo de un ataque. La única forma de alcanzar el RTO más estricto y ultracorto que se exige para los sistemas críticos es llevar a cabo la recuperación mediante instantáneas inmutables basadas en almacenamiento. Estas instantáneas deben almacenarse de forma segura en un repositorio aislado (o con aislamiento físico virtual).
- Early-warning threat detection
Identifying and remediating potential cyberthreats earlier is an important aspect of data protection and readiness. The capability to continuously scan data to detect anomalies and identify threats like ransomware and malware in real time and automate remediation is essential for faster containment of an attack.
- Isolated recovery environments (IRE) or cleanrooms for resilience testing
Establishing a completely self-contained IRE, where data can be restored for forensic and application analysis and validated as clean before returning to production, speeds recovery. IREs also allow organizations to continuously test and improve cyber recovery practices for organizational readiness.
- Scalability and performance
Businesses will continue to evolve their services, face new regulatory requirements, and deal with emerging cyberthreats. It’s important to consider a solution’s ability to scale as data requirements change across distributed, hybrid environments while maintaining high-performance speeds for data protection and recovery.
Cumplimiento con confianza
Organizations that delay establishing robust capabilities to meet DORA and other evolving resilience regulations – such as PSD2, NIS2, APRA CPS 230, and the European Cyber Resilience Act coming into effect in 2026 – may find themselves with mounting challenges to overcome. They also may find themselves at competitive disadvantage to firms that can demonstrate their ability to remain resilient in the face of disruptions in the global financial ecosystem.
Working with partners that understand the regulation’s resilience requirements and deploying robust solutions can help enable organizations to be compliant and better prepared to meet new regulatory challenges and defend their data environment against emerging threats.
Pure Storage and Commvault have come together to build a joint solution, modular in design, that helps financial institutions enhance their cyber resilience practices and address key pillars of DORA for incident response and resilience testing. The solution is built by integrating the leading cyber resilience capabilities of Commvault® Cloud with the highly secure, high-performance Pure Storage platform. Learn more about the solution and our commitment to cyber resilience aquí.
¿Estás preparado cibernéticamente?
Readiness reflects mature cyber resilience, where technology, people, and processes work seamlessly to enable continuous business in the face of any cyber challenge. Evaluate your organization’s cyber resilience with Commvault’s la Evaluación de Madurez Cibernética.
1 Principales conclusiones del ejercicio de simulación de las Autoridades de Supervisión Europeas (ESA) de 2024, Autoridad Bancaria Europea, 17 de diciembre de 2024.
2 Countdown to DORA – Four Takeaway Points from Regulators’ December Statements, Skadden, Arps, Slate, Meagher & Flom, LLP, Jan. 3, 2025