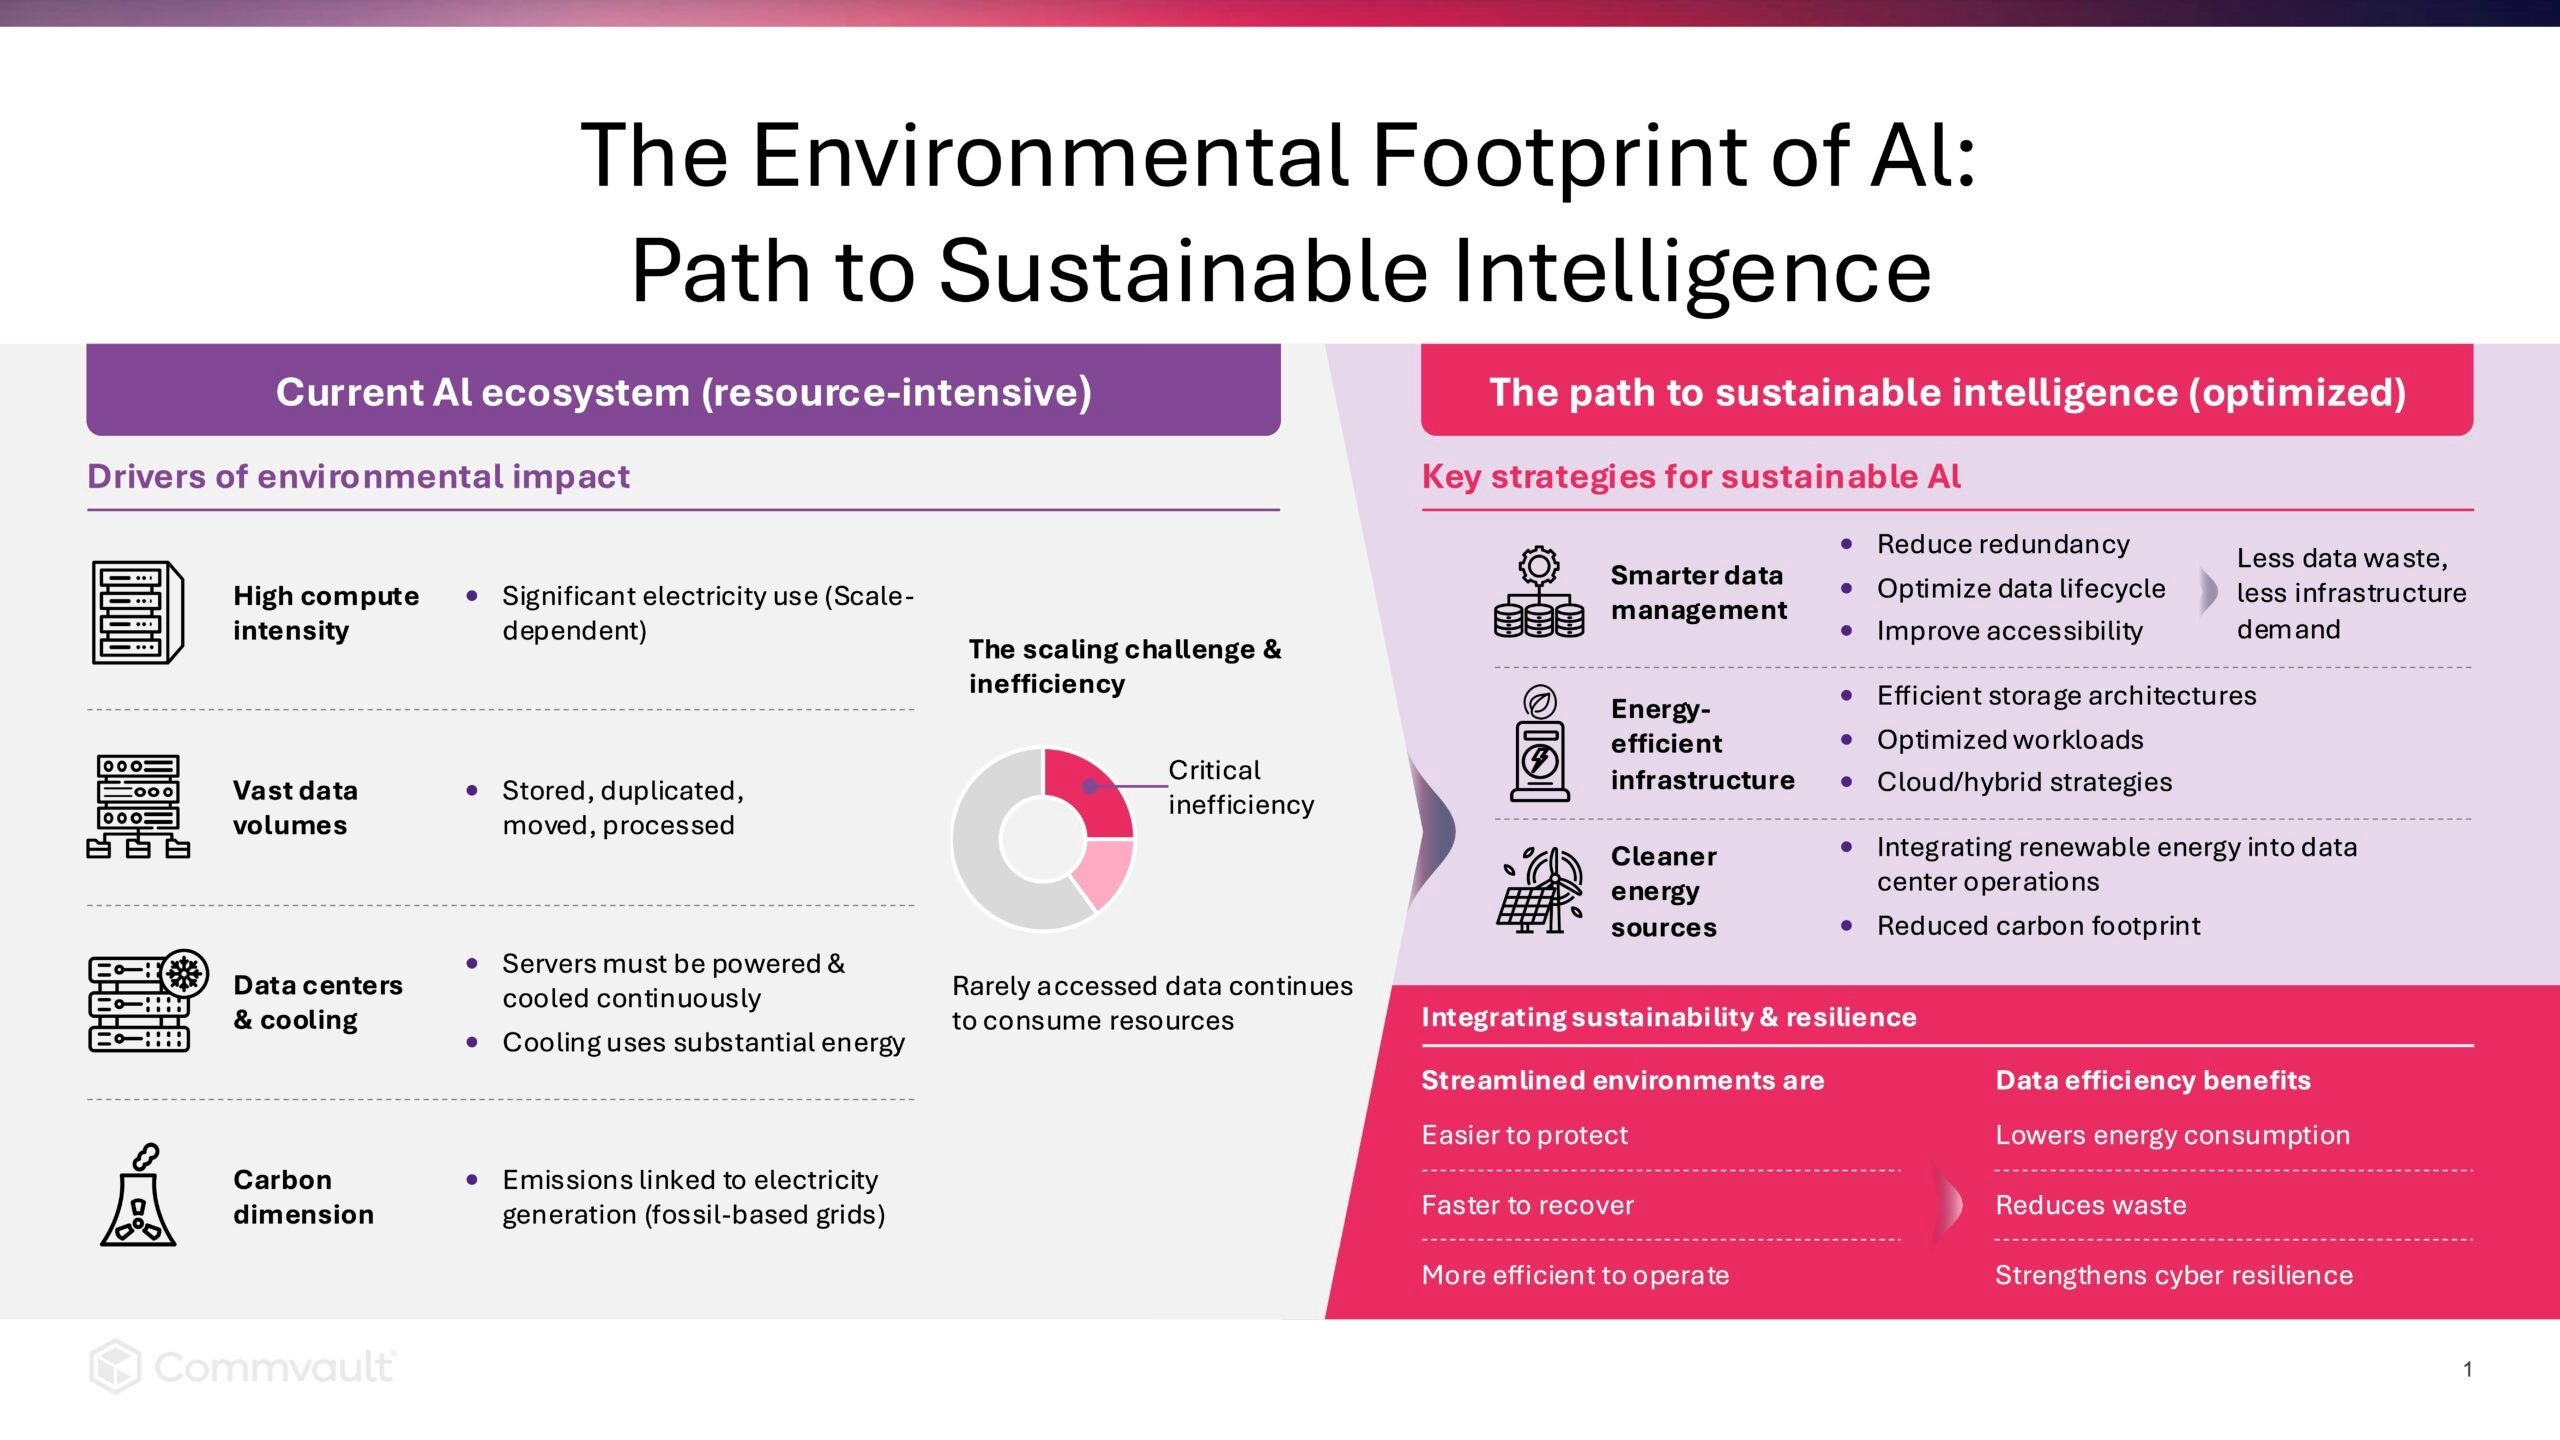
Punti di forza
- La sovranità minima necessaria (MVS) si concentra sull’applicazione del giusto livello di controllo ai carichi di lavoro appropriati.
- Trattare tutti i carichi di lavoro allo stesso modo può comportare complessità e costi superflui o una protezione insufficiente.
- Le organizzazioni rientrano in genere in tre profili di sovranità: sovranità totale, impresa regolamentata e multi-cloud ibrido.
- Una governance coerente in ambienti misti rappresenta una delle maggiori sfide operative.
There is a version of the digital sovereignty conversation that leads organizations somewhere expensive, operationally burdensome, and – if they’re being honest – further than their actual obligations require. Maximum sovereignty sounds responsible. In practice, it’s often a miscalibration.
There is an equally common version that leads somewhere dangerously thin – controls that satisfy a checklist but wouldn’t survive an audit, an incident, or a regulator who has stopped accepting documented intent as proof of demonstrated control.
The organizations that get sovereignty right tend to do something more rigorous and more practical than either extreme: They ask what they actually owe, to whom, and for what. Then they build to that standard – no more, no less.
This is the discipline of MVS, introduced in the Rapporto sulla Readiness per la sovranità digitale and developed in full here.
MVS isn’t a shortcut. It’s a recognition that the goal is the right level of control, applied consistently, across every workload that requires it.
Non tutti i carichi di lavoro sono uguali
The starting point for an MVS approach is workload classification – and most organizations skip it entirely.
A trading system processing regulated financial data carries fundamentally different sovereignty obligations than an internal HR collaboration tool. A database holding personal data of EU citizens is subject to a different legal and regulatory regime than a development environment running anonymized test data.
Treating all of these identically – either by applying maximum sovereign controls across the board or by assuming a single deployment model covers everything – is how organizations end up either over-engineered or under-protected.
The right question before any deployment decision: What does this workload require across each of the four sovereignty pillars? The Readiness Report includes a self-assessment structured around exactly that question.
The Three Profiles – and What They Actually Need
Le imprese soggette a regolamentazione rientrano in tre profili ben definiti, ciascuno con motivazioni principali e priorità di investimento diverse.
- The True Sovereign. Government agencies, defense contractors, and critical national infrastructure operators. For these organizations, sovereignty is not a compliance requirement – it is an operational mandate. Maximum control over every dimension of the technology stack is often legally required, and the cost tradeoffs are accepted because the alternative is not.
- The Regulated Organization. Financial services firms, healthcare organizations, energy companies. These organizations face binding requirements from DORA, NIS2, GDPR, and sector-specific frameworks. Compliance obligations may also map to EU certification schemes – including EUCS, EUCC, BSI C5, and SecNumCloud – depending on sector and deployment context.
on-negotiable in certain areas – particularly around data residency, operational access controls, and recovery within jurisdictional boundaries. But not every workload carries the same obligation.
- The Hybrid Multi-Cloud Organization. Organizations with existing hyperscaler investments facing increasing sovereignty pressure from customers, regulators, or procurement requirements. Their challenge is not wholesale migration – it’s layering sovereign controls onto a mixed estate and maintaining consistent governance across it.
Il costo di una calibrazione errata
Over-engineering sovereignty creates its own operational risks. Organizations that apply maximum sovereign controls to workloads that don’t require them absorb cost and complexity that serves no regulatory or business purpose.
Under-engineering is the more common failure mode, and the more dangerous one. It typically doesn’t show up until the audit arrives – or, more seriously, until an incident occurs and recovery becomes a legally constrained problem. (That failure mode is the subject of the quarto articolo di questa serie.)
Un punto di partenza pratico
Un approccio MVS prevede tre passaggi:
- Classify workloads by their actual sovereignty requirements across each pillar – don’t start with deployment models.
- Mappare ciascuna classe di carico di lavoro al livello di implementazione che soddisfa tali requisiti, nell’intero spettro che va dalle regioni degli hyperscaler pubblici al cloud pubblico sovrano fino agli ambienti gestiti on-premise.
- Govern the resulting mixed estate consistently – controls, audit evidence, and recovery capabilities must be demonstrable across the full environment, not just the most-sovereign tier.
The third step is where most programs struggle. Maintaining consistent sovereignty controls across a mixed estate is an operational governance challenge – and specifically the domain of Operational Sovereignty – argomento del terzo articolo di questa serie, il pilastro che la maggior parte delle strategie considera come un aspetto secondario.
Utilizzate l’autovalutazione contenuta nelRapporto sulla Readiness per la sovranità digitaleper individuare la vostra posizione attuale rispetto a tutti e quattro i pilastri.
Domande frequenti
D: Che cos’è la “sovranità minima funzionante” (MVS)?
A: L’MVS consiste nell’applicare controlli di sovranità in base alle effettive esigenze aziendali e normative. Ha lo scopo di evitare sia un eccesso di complessità che una protezione insufficiente.
D: Perché è importante la classificazione del carico di lavoro?
A: Carichi di lavoro diversi comportano obblighi normativi e operativi diversi. La classificazione dei carichi di lavoro aiuta le organizzazioni ad applicare il livello appropriato di controlli di sovranità.
D: Quali sono i tre profili di sovranità più comuni?
A: I tre profili sono: organizzazioni sovrane vere e proprie, organizzazioni regolamentate e organizzazioni ibride multi-cloud. Ciascuna di esse presenta requisiti operativi e di conformità distinti.
D: Quali rischi comporta un approccio eccessivamente ingegneristico alla sovranità?
A: Controlli eccessivi possono aumentare la complessità operativa e i costi senza garantire una conformità significativa né apportare valore aggiunto all’azienda.
D: Perché gli ambienti misti comportano sfide in termini di governance?
A: Le organizzazioni operano spesso su più modelli di cloud e infrastrutture. È difficile garantire la coerenza dei controlli, delle prove di audit e degli standard di Recovery in tutti gli ambienti.
Ruben Renders è direttore delle soluzioni MSP presso Commvault.
 Il rilevamento automatico garantisce la protezione dei nuovi report e delle nuove cartelle man mano che gli ambienti si evolvono, mentre la gestione centralizzata offre un unico punto di controllo per monitorare, gestire e ripristinare i dati su larga scala.