Skip to content

Every year on October 24, the world pauses for the International Day of Climate Action, reminding us that protecting the planet is no longer a choice, but a shared responsibility. Climate change isn’t coming – it’s here. And how we respond today will shape the future of our communities, our businesses, and our planet.

At Commvault, resilience is what we do – not just for data, but for the world we all share.

Sustainability: The Core of Resilience

Our mission to safeguard data goes hand in hand with our commitment to safeguard the environment. In FY25, we made meaningful progress toward our climate resilience goals:

  • Le emissioni Scope 2 sono diminuite di oltre il 13%, grazie a un uso più intelligente dell’energia e all’efficienza delle operazioni dei data center.
  • Emissions intensity fell from 12.7 to 9.6 metric tons CO₂e per million USD revenue, showing that growth and sustainability can move forward together.
  • La nostra sede centrale, certificata LEED, continua a essere all’avanguardia grazie all’integrazione delle energie rinnovabili, a sistemi efficienti dal punto di vista idrico e a solidi programmi di riciclaggio.

In everything from how we power our offices to how we design our technology, we consider sustainability a key driver of business continuity.

Data That Works for the Planet

The same innovation that drives Commvault’s cyber resilience is helping advance climate resilience.

By optimizing data storage, reducing redundancies, and improving workload efficiency, our cloud solutions enable customers to use less energy and achieve their own sustainability goals. Less waste. Lower energy use. More resilience.

Because when data works smarter, the planet breathes easier.

Collective Action, Shared Progress

We know climate action is not a solo mission. That’s why Commvault collaborates with partners who share our environmental values and participates in community initiatives like the Net Zero Institute to help accelerate the transition to a low-carbon economy.

We also align our climate governance with the Task Force on Climate-Related Financial Disclosures (TCFD), driving accountability from the top down.

From Awareness to Action

The path to a sustainable future begins with small, intentional choices, like turning off a light, optimizing a server, rethinking a commute. Every decision matters.

This International Day of Climate Action, let’s all take a step toward progress. Because resilience – whether in data, business, or the environment – is built together.

Aakanksha Kashyap è specialista ESG presso Commvault.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Punti di forza

  • As few as 250 poisoned samples can compromise a large AI model – turning your data lake into a prime attack surface.
  • I campioni avvelenati possono impiantare backdoor che persistono anche dopo il retraining o la messa a punto.
  • A practical defense centers on “protect, detect, roll back,” treating data protection as core to AI integrity.
  • Backup, set di dati con versioni e ripristini dettagliati consentono un rapido ripristino a uno stato pulito e affidabile.
  • Commvault + Satori aggiungono funzionalità di rilevamento dei dati, controllo degli accessi in tempo reale, monitoraggio delle attività LLM e policy-plus-rollback unificato per rafforzare la resilienza dell’IA.

I’ve been thinking a lot about Anthropic’s latest research – and it’s unsettling. It found that as few as 250 poisoned samples can compromise a massive AI model.
👉 [Read la ricerca yourself.]

That’s right – a few hundred corrupted files can undo months of training and billions of parameters. Not thousands. Not millions. Just hundreds.

For anyone building or managing AI, this changes everything. Your AI data lake has become your primary attack surface – and if you can’t trust your data, you can’t trust your models.

💣 Small Samples, Big Consequences

Anthropic ha dimostrato che:

  • Una manciata di campioni avvelenati può impiantare backdoor nascoste.
  • Queste vulnerabilità possono persistere anche dopo la riqualificazione e la messa a punto.
  • Attackers don’t need to flood your system – they just need a foothold.

AI integrity isn’t only a model problem – it’s a data protection problem.

🧩 The Practical Defense: Protect. Detect. Roll Back.

In Commvault, vediamo le organizzazioni affrettarsi a costruirepipeline di IA senza garantire completamente la sicurezza delle fondamenta. When data is compromised, your best defense is the ability to roll back to a clean, trusted state.

That’s why backups, set di dati con controllo delle versioni, e i ripristini granulari stanno diventando essenziali per l’IA tanto quanto le GPU e i pesi dei modelli.

Commvault può aiutarti a:

  • Cattura istantanee immutabili del tuo data lake.
  • Ripristina una versione funzionante.
  • Verifica la discendenza, la provenienza e la cronologia delle modifiche.
  • Bloccare i backup contro la manomissione (tramite archiviazione WORM).

Because when it comes to AI, protection isn’t just about avoiding failure – it’s about being able to recover fast and clean when it happens.

🔐 The Power of Satori: Smarter, Safer AI Data

Ora che Satori fa parte di Commvault, ora offriamo funzionalità più ampie in materia di sicurezza dei dati e governance dell’IA che possono aiutarvi a:

  • Rileva automaticamente i dati sensibili su cloud, magazzini e laghi.
  • Control access in real time – who sees what, when, and how.
  • Monitorare l’attività dell’IA e dell’LLM per rilevare tempestivamente eventuali anomalie.
  • Unify policy and rollback – restoring data and supporting compliance from one place.

Insieme, Commvault + Satori forniscono funzionalità di base resilienti e intelligenti per i dati che aiutano a rilevare, proteggere e recuperare dalle minacce in continua evoluzione dei dati AI.

🚀 The Future of AI Resilience

This is exactly what we’ll be discussing at Commvault Shift | Virtual – how to secure, protect, and recover the data that drives AI.

Join us to hear from industry leaders about building trusted, resilient AI systems that can help withstand data corruption, cyber threats, and human error.

👉 Register here: commvault.com/SHIFT VirtualProteggi la tua IA. Proteggi i tuoi dati. Costruisci un futuro più resiliente.

Domande frequenti

Q: What does “250 poisoned files” actually mean for my models?
A: The blog cites Anthropic’s finding that only a few hundred corrupted samples can meaningfully compromise a massive model – no flood required. It highlights that attackers need only a small foothold to degrade behavior or implant triggers.

Q: Why might retraining fail to remove poisoning?
A: Some backdoors survive standard retraining and fine-tuning because the malicious signal is subtle and reinforced by the broader dataset. The result is a model that behaves normally until a hidden trigger appears.

Q: What immediate defenses should we prioritize?
A: Adopt a “protect, detect, roll back” strategy: Secure your data pipeline, monitor for anomalies, and maintain the ability to revert to a known-good state. Treat data protection as foundational – on par with model weights and GPUs.

Q: How do backups and versioned datasets help in practice?
A: Immutable snapshots, version history, and fine-grained restores enable you to quickly recover clean data, verify lineage and provenance, and continue operations without carrying hidden compromises forward.

Q: What additional value does Satori bring with Commvault?
A: Satori expands capabilities with automatic discovery of sensitive data across clouds and lakes, real-time access control, LLM activity monitoring for early anomaly detection, and unified policy plus rollback to support compliance and recovery.

Q: Isn’t model security enough without data protections?
A: Model-centric controls are necessary but incomplete. The post argues that AI integrity is as much a data protection problem as a model problem; without trusted data, even well-secured models can be subverted.

Thomas Bryant è direttore senior del marketing di prodotto presso Commvault.

Blog correlati:

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

La seconda edizione diLo stato di Readiness dei dati in AsiaIl rapporto, un rapporto completo redatto da Tech Research Asia su incarico di Commvault, offre una visione chiara delle sfide e delle realtà che devono affrontare le organizzazioni in tutto il continente. Basato su un sondaggio condotto su 1.218 aziende in Indonesia, Hong Kong, Corea, Malesia, Filippine, Singapore, Thailandia e Vietnam, il rapporto rivela le tendenze critiche in materia di crescita dei dati, pressioni normative, adozione dell’intelligenza artificiale e cyber resilience.
Ecco alcuni dei punti salienti che richiedono l’attenzione dei leader aziendali e IT:

Crescita senza precedenti dei dati e complessità dell’infrastruttura

I patrimoni di dati stanno crescendo a un ritmo sempre più veloce.

  • L’organizzazione mediaAsiatica ha registrato una crescita dei dati pari al 40% negli ultimi 12 mesi, un aumento significativo rispetto al 31% registrato l’anno precedente.
  • Questa esplosione di dati, il 66% dei quali non strutturati, risiede in ambienti sempre più complessi.
  • La maggior parte delle aziende (63%) opera oggi in cloud cloud cloud ibridi, creando un ecosistema tentacolare e interdipendente che è difficile da gestire e proteggere.
  • Questa complessità sta avendo un impatto negativo, con il 38% delle organizzazioni che ammette di non avere fiducia nella propria capacità di ripristinare le operazioni aziendali dopo una violazione.


Il paradosso dell’intelligenza artificiale: elevata diffusione nonostante l’alto rischio

L’intelligenza artificiale sta riscuotendo un grande successo: il 74% delle organizzazioni asiatiche utilizza attualmente soluzioni di intelligenza artificiale destinate al mondo aziendale. Tuttavia,si ha una visione lucida dei rischi connessi.

  • Questa complessità sta avendo un impatto negativo, con il 38% delle organizzazioni che ammette di non avere fiducia nella propria capacità di ripristinare le operazioni aziendali dopo una violazione.
  • Un incredibile 73% di queste organizzazioni ritiene che l’implementazione dell’IA aumenti la probabilità di una violazione della sicurezza informatica.
  • Nonostante questa consapevolezza, la due diligence è ancora carente. È preoccupante che il 58% delle organizzazioni non abbia effettuato controlli di sicurezza approfonditi sui propri strumenti di IA prima della loro implementazione e che meno della metà (46%) disponga di politiche complete per proteggere i dati generati dall’IA.

The Tangled Web of Regulations

The regulatory landscape across Asia is becoming increasingly intricate and, at times, contradictory.

  • Esigenze contrastanti: il 53% delle organizzazioni riferisce di dover affrontare requisiti normativi contrastanti per i propri dati in diverse aree geografiche.
  • Onere normativo: il 52% delle aziende deve conformarsi ad almeno quattro importanti atti normativi.
  • Conformità dell’IA: la sfida è aggravata dalle normative specifiche sull’IA, alle quali è soggetto quasi il 60% delle aziende, mentre un altro 27% prevede di esservi soggetto entro il prossimo anno.

La triste realtà degli attacchi informatici e del ripristino dei dati

There remains a significant disconnect between the expectations of business leaders and the reality of IT recovery after a cyber incident. While 72% of business leaders expect to be back in business within five days of an incident, the reality is that 70% of businesses take more than a week to recover.
The report also sheds light on the direct impacts of attacks:

  • Tra le aziende che hanno subito violazioni, l’83% ha subito una fuga di dati.
  • Meno della metà (41%) è riuscita a recuperare il 100% dei propri dati.
  • Sebbene il 57% delle aziende abbia una politica che vieta il pagamento dei riscatti, il 34% di quelle che adottano tale politica ha pagato il riscatto quando è stato attaccato.

Imparare con fatica

Interestingly, organisations that have experienced a breach demonstrate a more mature and realistic understanding of their capabilities. They are more likely to have comprehensive incident response plans and a clearer grasp of the complexities involved in recovery. For instance, breached companies are almost twice as likely to view their internal AI tools as a high cybersecurity risk compared to those that have not been breached.
To gain a deeper understanding of these findings and benchmark your organisation against your peers, download the full Lo stato di Readiness dei dati in Asiarapporto. Il rapporto completo offre un’analisi dettagliata, dati specifici per paese e spunti pratici per aiutarti a migliorare le tue strategie di gestione dei dati, di Recovery e di resilienza informatica, al fine di garantire la continuità operativa.

More related posts


Cyber Resilience

Read more about Cyber Resilience

Cyber Security

Read more about Cyber Security

In conversations with three Chief Medical Information Officers across different healthcare systems, each was asked about their most recent cybersecurity incident. The answer was unanimous and telling: None had experienced a direct attack on their own systems. Instead, all three were grappling with the aftermath of third-party vendor breaches that cascaded through their operations.

This isn’t coincidence – it’s the new reality of healthcare cybersecurity.

The Vendor’s Vendor Problem

“We are big enough to have these experts on staff that are our experts to protect us,” one CMIO explained. “Sometimes I feel that that can be a barrier to agility because of how strict we are and how thorough we are in those evaluations. But I think that we can’t ensure that our partners do the same.”

Here’s the challenge: Healthcare organizations have become incredibly sophisticated at vetting direct vendors. The contracting process is rigorous, security assessments are thorough, and compliance requirements are non-negotiable.

But what happens when your vendor makes a deal with another vendor? Suddenly, you’re exposed to risks you never evaluated, from companies you’ve never heard of, through relationships you don’t control.

One security leader illustrated this perfectly: “I’m going to make a deal to use Vendor X to do something for me here. But Vendor X may make a deal with Vendor Y that lets them do their job. So if there’s a problem with Vendor Y who I’m not technically contracted with, but my vendor needs them to function, I can’t control that.”

Quando l’ecosistema fallisce

La regola di backup 3-2-1Change Healthcare incident provides a stark example. When its systems went down due to a cyberattack, it wasn’t just Change Healthcare that suffered – it was every healthcare organization that relied on its prescription processing services.

One CMIO described the impact: “We had a lot of issues sending prescriptions, receiving them, having issues being unclear of what went through, what didn’t go through, and who didn’t have their medications.”
La regola di backup 3-2-1downstream clinical impact was immediate and severe. Patients couldn’t get medications, providers couldn’t verify prescription statuses, and healthcare teams scrambled to identify which patients might be affected. This was a direct patient safety issue caused by a vendor incident completely outside the control of healthcare providers.

But the clinical impact was just the beginning. The compliance implications were equally severe, highlighting a fundamental challenge in healthcare’s regulatory landscape.

La trappola della conformità: quando i fallimenti dei fornitori diventano un problema normativo per voi

Healthcare organizations face a harsh regulatory reality: Vendor incidents don’t absolve them of compliance responsibilities. In fact, they often amplify them.

HIPAA requires covered entities to establish Business Associate Agreements with vendors handling protected health information. While these agreements theoretically transfer some liability, the practical reality is different. When a vendor suffers a breach, the healthcare provider still faces potential penalties, regulatory scrutiny, and mandatory reporting requirements.
La regola di backup 3-2-1reporting burden alone creates significant operational strain. HIPAA’s proposed 72-hour reporting mandates, similar to regulations like EU NIS2 and DORA for cross-border institutions, require healthcare providers to disclose incidents quickly, regardless of whether the breach originated from their own systems or a vendor’s.

As one CMIO noted: “We actually have to communicate to the state, to the Centers for Medicaid and Medicare Services: ‘This is what’s going on. This is where we are with our recovery.’”

This means that during an active incident – when clinical teams are scrambling to maintain patient care and IT teams are coordinating recovery efforts – compliance teams must simultaneously investigate, document, and report on incidents they didn’t cause and may have limited visibility into.
La regola di backup 3-2-1data sovereignty challenge adds complexity. Vendors storing healthcare data outside approved regions can trigger compliance violations that organizations may not even know exist until an incident forces a comprehensive audit of their vendor ecosystem.

“We require [vendors] to give us anything and everything we asked for to review,” explained one security leader who’s experienced a vendor ransomware attack. “So, there was actually no limitations on what we could ask.”

But this level of oversight is typically only possible with the largest vendor relationships, leaving many smaller but still critical vendor dependencies in compliance blind spots.

Il campanello d’allarme di CrowdStrike

La regola di backup 3-2-1Incidente relativo a CrowdStrike drove home another reality: When critical infrastructure providers fail, the entire healthcare ecosystem fails simultaneously.

“We did [tabletop exercises] with the assumption that it would be a ransomware attack… a very kind of localized event,” one leader reflected. “And this was affecting the entire ecosystem. And that’s where we [learned] that we needed to have more resiliency practices that would incorporate where the ecosystem itself would be widely affected.”
La regola di backup 3-2-1challenge wasn’t just technical – it was operational and regulatory. When everyone is down at once, the usual backup plans (like calling vendors for support or switching to alternate providers) simply don’t work.

Healthcare organizations faced not only interrupted patient care and massive downtime costs but also complex compliance reporting requirements for an incident that originated entirely outside their control.

Oltre la tradizionale valutazione dei rischi

Healthcare organizations are discovering that their traditional approach to vendor risk management isn’t enough. The standard process – sending questionnaires, reviewing documentation, checking compliance certifications – only covers direct relationships.

But post-incident, the conversation is changing. Instead of just asking “Do you do this? Do you do that?” organizations are demanding to see exactly how vendors execute security and recovery plans. They’re asking for evidence of testing, requiring contractual rights to review sub-vendor relationships, and building in financial protections.

Il nuovo modello di relazione con i fornitori

Le organizzazioni sanitarie lungimiranti stanno adottando diverse misure concrete per affrontare il rischio dell’ecosistema:

  • Data sovereignty: “We want to start taking more ownership over the data… so that we have something we can rebuild or even switch over to another third party if possible,” one leader said.
    Rather than letting vendors hold all the data, organizations are requiring regular data exports and maintaining their own copies of critical information. This approach helps address data residency requirements and enables compliance continuity even when vendors fail.
  • Evoluzione contrattuale migliorata: le negoziazioni contrattuali post-incidente ora affrontano esplicitamente gli obblighi di conformità. Le organizzazioni richiedono tempi di notifica che soddisfino i requisiti normativi, garanzie di ripristino che riducano al minimo i costi di inattività e un risarcimento finanziario sia per le perdite dirette che per le sanzioni di conformità derivanti da interruzioni causate dai fornitori.
  • Compliance-aware update management: The Incidente relativo a CrowdStrike highlighted how vendor updates can create both operational and compliance risks. Many organizations have implemented “two versions behind” policies for critical security updates, balancing the risk of delayed patches against the risk of compliance violations from untested updates that could cause widespread outages.
  • Integrazione normativa nella gestione dei fornitori: le organizzazioni stanno integrando direttamente le considerazioni relative alla conformità nella valutazione dei fornitori e nella supervisione continua. Ciò include la certezza che i fornitori siano in grado di soddisfare gli stessi requisiti di segnalazione entro 72 ore, mantenere un’adeguata residenza dei dati e fornire la documentazione necessaria per la segnalazione normativa.

The Insurance Industry’s Perspective

Perhaps most telling is how the insurance industry views these risks. As one security leader shared from a colleague in insurance risk modeling: “The number one risk that we have is the kind of outage like CrowdStrike, where we’re so dependent upon these technology platforms that when we’re out, there’s massive disruptions in services and in operations. She says that’s the number one risk in our risk model. It’s not ransomware attacks.”

This shift in risk assessment reflects a fundamental change. Traditional cybersecurity focused on preventing bad actors from getting in. Modern cybersecurity also must address the reality that critical vendors – with the best of intentions and strong security practices – still can bring down entire ecosystems through operational failures.

La sfida della minimamente vitale in un mondo ecosistemico

Traditional recovery planning often assumes you can restore everything systematically, but when entire ecosystems fail simultaneously, organizations must focus on minimum viable recovery (MVR).
La regola di backup 3-2-1concept of minimum viability becomes critical when your vendors, their vendors, and potentially your backup vendors are all affected. As we’ve explored in our analysis of minacce informatiche nel settore sanitario e MVR, the question isn’t just “How do we recover everything?” but “What are the bare essentials we need to keep patient care running while the ecosystem rebuilds itself?”

This ecosystem reality makes Prontozza di recupero dell’organizzazione more complex than ever. When you can’t rely on your usual vendors or backup providers, your MVR plan must account for true independence from the broader ecosystem – at least temporarily.

Andare avanti

Organizations can’t just secure their own perimeter; they need to understand and plan for the interconnected web of dependencies that modern healthcare relies on. This means fundamentally rethinking business continuity planning to account for simultaneous ecosystem failures. It means maintaining data sovereignty even when using SaaS providers. And it means accepting that some risks simply can’t be eliminated – only managed and planned for.
La regola di backup 3-2-1healthcare leaders we spoke with weren’t pessimistic about these challenges; they were pragmatic. They understand that the benefits of interconnected, cloud-based healthcare systems far outweigh the risks.

Verifica la resilienza del tuo ecosistema

Understanding the risks is just the first step. The next is honestly assessing whether your organization is prepared for the new reality of interconnected failures. How confident are you that your MVR plan would work when your usual vendors and backup systems also are compromised?

Healthcare organizations serious about ecosystem resilience should evaluate their readiness across three critical areas: business-critical prioritization, measurable technical response, and Prontozza di recupero dell’organizzazione. Commvault’s Valutazione della fattibilità minima nel settore sanitario helps evaluate your current capabilities and offers actionable recommendations for closing any gaps.

Don’t wait for the next ecosystem-wide incident to discover whether your recovery plans account for the reality of interconnected healthcare IT. Fai il test oggi stesso and build true resilience for tomorrow’s challenges.


Blog correlati:

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

A powerful go-to-market strategy is what separates leaders from the pack in the competitive cyber resilience market. At Commvault, we’re dedicated to providing our partners with the strategic resources needed to help grow revenue, build customer trust,esolidify your reputation as a market leader with Commvault.
That’s why we are excited to announce two game-changing resources designed to elevate your salesemarketing efforts: a reimagined Hub delle campagne Commvaulte il nuovoGuida rapida alle strategie di vendita per i partner.

Ottimizza il tuo marketing con l’hub delle campagne

Based on partner feedback, our newly imagined Campaigns Hub is your destination for ready-to-use, results-driven marketing. The Campaigns Hub is a powerful, intuitive platform that simplifies the creation of targeted campaigns, helping you build awareness, generate leads,eupsell Commvault’s suite of solutions. And now our platform integrates seamlessly with your existing strategies, enabling cohesive brand messagingemaximum impact.
With the Campaigns Hub, you’ll find:

  • Targeted campaigns you can launch in minutes. Choose from a library of pre-built multi-language campaigns – from “Securing Continuity for Minimum Viable Business” to “Microsoft Active Directory Protection” –ecustomize the content to fit your audience’s unique needs.
  • A new, powerful webcast program. Leverage Commvault’s best speakersecontent directly from the Campaigns Hub using our on-demand webcasts along with the promotional materials to drive leadseawareness.
  • A new, co-branded assessment tool. Contact our Marketing Conciergeerequest a co-branded minimum viability assessment tool that provides benchmarks to your customers in minuteseputs leads directly in your inbox.  
  • Risorse di alto valore per i clienti da utilizzare sulla vostra platform sull’hub. Ora potete accedere ai contenuti chiave dei clienti Commvault e alle campagne promozionali tramite l’Hub delle campagne e integrare queste preziose risorse nelle vostre iniziative di marketing più ampie sull’hub, oppure scaricarle e utilizzarle sulla vostra platform.
  • Our complimentary Marketing Concierge service that makes campaigns even easier. You don’t need to use MDF or pay for our Marketing Concierge service to help you customizeerun the latest Commvault campaigns to grow your business. Try out the service with a Sessione di attivazione della campagna 1:1.

Aumenta il successo delle vendite con i playbook At-A-Glance

To complement your marketing efforts, Commvault also has launched our new Guida rapida alle strategie di vendita per i partner. We’ve condensed our most popular Guide strategiche per le vendite dei partner into a concise, easy-to-use one-page format, packed with the essential tools you need to articulate valueeenhance customer engagement.
Each playbook includes:

  • Concise call scripts: Confidently articulate the unique value propositions of Commvault’s productsesolutions.
  • Objection handling: Turn potential roadblocks into opportunities with prepared responses to common customer challenges.
  • Customer-ready materials: Accelerate sales cycles by sharing curated whitepapers, solution briefs, case studies, eBooks,emore.

By combining the power of the Hub delle campagne Commvault with the strategic guidance of the At-A-Glance Sales Playbooks, you can create impactful, end-to-end campaigns that drive customer engagementeachieve greater sales success.

Sblocca il tuo potenziale con Commvault

Ready to transform your go-to-market strategyemaximize the value of Commvault’s offerings? Explore the Hub delle campagne CommvaulteGuide strategiche per le vendite dei partnernel Portale Partner. Esplora il sito per conto tuo oppure prenota unaSessione di attivazione della campagna 1:1con il nostro servizio gratuito di assistenza marketing personalizzata per ricevere un supporto mirato.

More related posts


Cyber Resilience

Read more about Cyber Resilience

Quando gli hacker attaccano, la velocità non è tutto. Il ripristino rapido dei dati compromessi non fa altro che reintrodurre la minaccia, creando un circolo vizioso di infezioni e reinfezioni. Recentemente ho redatto un white paper insieme ai miei colleghi diKyndrylintitolato,Ridefinire il concetto di “cyber Recovery”: presentiamo il Mean Time to Clean Recovery (MTCR) where we introduced a fundamental shift: measuring how fast you can restore from clean, verified data rather than just any available backup.

Here are the five critical steps that determine your organization’s MTCR:


  1. Creare un ambiente pulito in cui poter guarire.

The problem: Recovery to an infected infrastructure will simply reinfect your restored systems.

The solution: Isolated Recovery Environments (IREs) or cleanrooms – compute and storage infrastructure physically or virtually separated from production environments where attackers never had access.

Reality check: Without an IRE, modern forensic teams need 24 to 72 hours to certify complex hybrid environments as “clean.” Your MTCR automatically becomes measured in days, not hours.


  1. Trova dati puliti da cui eseguire il ripristino.

The hidden threat: Modern attackers operate in stealth for weeks before launching attacks, seeding malicious payloads throughout your environment – including backup systems.

The breakthrough: Automated scanning for Indicators of Compromise can help identify clean backup sets without the trial-and-error cycle of testing each backup until you find one that works.

Collaboration required: This step demands tight integration between SysOps teams (who manage backups) and SecOps teams (who understand current threats). Forensic analysis reveals attack signatures that must be fed into the scanning process.


  1. Recuperare i dati in tempi accettabili.

The uncomfortable truth: Enterprise backup solutions often deliver “10+ hours per terabyte” recovery performance. Scale this to typical enterprise services requiring hundreds of terabytes, and you’re looking at weeks of recovery time.

The reality: Most backup infrastructure was designed for nightly incremental backups (5% data change), not full-scale business restoration (100% recovery).

The solution: Purpose-built cyber resilience platforms with high-performance recovery capabilities, combined with minimum viable company (MVC) prioritization – focusing on the critical 20% of services that enable 80% of business function.


  1. Mantenere l’integrità dei dati su tutta la platform.

The challenge: Enterprise systems don’t exist in isolation. During recovery, systems restored from backups taken at different times create data integrity nightmares.

Example scenario:

  • Database clienti: backup martedì alle 3 del mattino
  • Sistema di fatturazione: backup lunedì alle 23:00
  • Sistema di inventario: backup mercoledì alle 6 del mattino

Result: Orders for customers who don’t exist, invoices for products not in inventory.

The Process: Restoration sequencing based on dependencies, data reconciliation across integrated systems, and comprehensive consistency checks before production return.


  1. Test prima del ritorno in produzione.

The rush trap: Under pressure, IT teams often rush systems back online without comprehensive testing, leading to partially functional systems or reintroduction of attack remnants.


Convalida completa:
  • Test funzionali dei processi aziendali fondamentali
  • Convalida della sicurezza tramite scansione delle vulnerabilità
  • Verifica dell’integrità dei dati su tutte le piattaforme
  • Convalida dei processi aziendali da parte dei team applicativi

Critical success factor: Pre-define your MVC acceptance criteria – the specific functionality that must work before you’re truly “recovered.”


La sfida dell’integrazione

These aren’t sequential steps – they’re interconnected capabilities that must work together. Your MTCR is only as fast as your slowest step and only as reliable as your weakest validation point.

The investment reality: Clean recovery requires purpose-built cyber resilience platforms, isolated recovery environments, automated scanning tools, and dedicated recovery networks. But the cost of prolonged downtime and reinfection is far greater.


Prossimi passi:
  1. Valuta quanto tempo richiederebbe ciascuna fase nel tuo ambiente attuale.
  2. Identifica la tua lacuna più grande.
  3. Calcolare il costo dei tempi di inattività prolungati rispetto all’investimento nell’infrastruttura.
  4. Inizia dai servizi aziendali più importanti.

The era of “backup and pray” is over. Organizations that master these five steps don’t just recover faster – they recover once, cleanly, and with confidence.


Per saperne di più

Guarda il webinar in cui parlo di questo nuovo indicatore,L’indicatore mancante per il successo della Recovery informatica. Leggi il libro bianco completo,Ridefinire il Recovery informatico: introduzione al Mean Time to Clean Recovery, per ulteriori informazioni su questo indicatore fondamentale.Darren Thomson è Field CTO presso Commvault. Non perdetevi la sua partecipazione alla serie di podcast, STRIVE.

More related posts


CleanroomRecovery_Thumbnail_888x500

Commvault Cleanroom

Read more about Commvault Cleanroom

La quinta edizione delRapporto “Stato di Readiness dei dati” in Australia e Nuova Zelanda, un rapporto di Tech Research Asia Insights commissionato da Commvault, offre uno sguardo critico sull’attuale panorama della gestione dei dati, della sicurezza informatica e delle pressioni normative che devono affrontare le organizzazioni in Australia e Nuova Zelanda (ANZ).Basato su una ricerca condotta su 408 aziende della regione, il rapporto rivela le tendenze chiave e le dure realtà relative al modo in cui le aziende stanno affrontando un ambiente digitale sempre più complesso. Dato che spesso esaminiamo i risultati delle ricerche su scala globale, è particolarmente utile avere una prospettiva locale sulla disponibilità dei dati. Sebbene i tassi di crescita dei dati abbiano registrato un leggero rallentamento, le sfide relative alla gestione, alla sicurezza e al recupero dei dati si sono intensificate. Ecco alcune delle informazioni più significative contenute nel rapporto.

Il contesto normativo e dei dati: una rete intricata

Le organizzazioni si trovano a dover affrontarevasti archivi di dati e un quadro normativo sempre più rigido.

  • Rallentamento della crescita, espansione persistente: il tasso di crescita annuale dei dati in ANZ ha subito un leggero rallentamento, passando dal 28% dello scorso anno al 27% di quest’anno. La maggioranza, pari al 62%, continua a operare in ambienti dati misti ( cloud multiplo o ibrido) e si prevede che questa percentuale aumenterà fino al 71% entro il 2026.
  • Divario di fiducia: un numero preoccupante di organizzazioni non ha fiducia nella propria capacità di ripristinare le operazioni aziendali dopo una violazione, con il 54% delle aziende australiane e il 63% di quelle neozelandesi che si sentono impreparate.
  • Complessità normativa: il panorama normativo sta diventando sempre più difficile da gestire. Il 55% delle aziende australiane e il 53% di quelle neozelandesi sono ora tenute a conservare copie dei dati in cloud separati per garantire la resilienza. Inoltre, oltre un terzo delle organizzazioni deve affrontare normative sui dati contrastanti in diverse aree geografiche.
  • L’ascesa della regolamentazione dell’IA: la conformità specifica per l’IA è una preoccupazione crescente, con il 28% delle aziende già soggette a tali normative e un altro 40% che prevede di esserlo entro il prossimo anno.

Il paradosso dell’intelligenza artificiale: elevata diffusione nonostante l’alto rischio

L’entusiasmo per l’intelligenza artificiale è forte,yet it’s coupled with significant security concerns.

  • Rischio contro ricompensa: mentre il 73% delle organizzazioni ANZ utilizza soluzioni di IA incentrate sul business, il 68% di esse ritiene che tale adozione aumenti la probabilità di una violazione della sicurezza informatica.
  • Mancanza di due diligence: ben il 63% delle organizzazioni ha ammesso di non aver condotto audit di sicurezza approfonditi ed estesi sui propri strumenti di IA prima della loro implementazione.
  • Deficit normativo: solo il 29% delle aziende dispone di politiche complete per proteggere i dati e i contenuti generati dalle soluzioni di IA.

Recupero: un divario tra aspettative e realtà

The gap between business leaders’ recovery expectations and the on-the-ground reality for IT teams remains a major issue.

  • Il divario tra aspettative e realtà: l’80% dei dirigenti aziendali prevede di riprendersi da un incidente di sicurezza informatica entro cinque giorni. Tuttavia, la cruda realtà è che occorrono in media quattro settimane per ripristinare un livello minimo di operatività aziendale.
  • Ransomware’s reach: Seventy percent of ANZ organisations have received a ransomware demand, and of those, 20% admitted to paying it. Interestingly, of the companies with a stated “no payment” policy, 15% still ended up paying the ransom when faced with an actual attack.
  • Il potere dell’esperienza: il rapporto rivela un dato interessante: l’esperienza è un insegnante severo ma efficace. Le aziende che hanno subito violazioni sono 1,5 volte più propense a condurre revisioni approfondite degli strumenti di IA e due volte più propense a testare tutti i carichi di lavoro mission-critical come parte dei loro piani di risposta agli incidenti. Al contrario, le aziende che non hanno subito attacchi sono 1,5 volte più propense a credere di poter ripristinare la normalità in un solo giorno.

The 2025 State of Data Readiness report underscores a challenging environment for ANZ organisations. From regulatory hurdles to the double-edged sword of AI and the persistent disconnect in recovery expectations, the path to true cyber resilience is complex.To gain a deeper understanding of these findings, download the rapporto completo.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

I’m thrilled to share that we were just announced as a winner in Udemy’s Premi per l’eccellenza nell’apprendimento 2025nella categoria “Leading With Learning Science”. In questo programma di premiazione, Udemy ha riconosciuto le organizzazioni che hanno ottenuto risultati significativi nell’ambito della formazione e dello sviluppo professionale attraverso l’aggiornamento delle competenze supportato dall’intelligenza artificiale. Come uno dei vincitori nella categoria Leading With Learning Science, Commvault è stata premiata per aver dato priorità all’integrazione dell’apprendimento nel flusso di lavoro, coinvolgendo gli studenti attraverso il micro-apprendimento e creando esperienze di apprendimento personalizzate.

Siamo onorati di essere stati inseriti in un elenco di leader visionari che stanno trasformando l’apprendimento su larga scala e fornendo ai propri dipendenti gli strumenti necessari per prosperare in un futuro all’insegna dell’intelligenza artificiale.

L’investimento nelle nostre persone è importante

Over the past year, we’ve expanded on our investment in learning and development by implementing an all-new, comprehensive learning platform, Pathfinder, to provide our Vaulters with the tools, resources, and opportunities they need to enhance their skills and advance their careers.

Our new platform has a wealth of learning modules, ranging from live instructor led sessions to on-demand and self-paced learning modules, including Udemy Business’ 30,000+ expert-led courses covering topics across technology, business, leadership, productivity, cybersecurity, and GenAI. Udemy Business isn’t just another online training tool – it’s a strategic driver of capability building within Commvault, and we’re delighted to offer our global Vaulter community access to Udemy Business.

We’ve also developed curated learning paths tailored for our teams, with a focus on the power of AI. The development of our Vaulters is key to Commvault’s success, and with Udemy Business, we’re giving them the tools to build their future growth, all while harnessing the potential of AI.

To learn more about what it’s like to work at Commvault, clicca qui.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

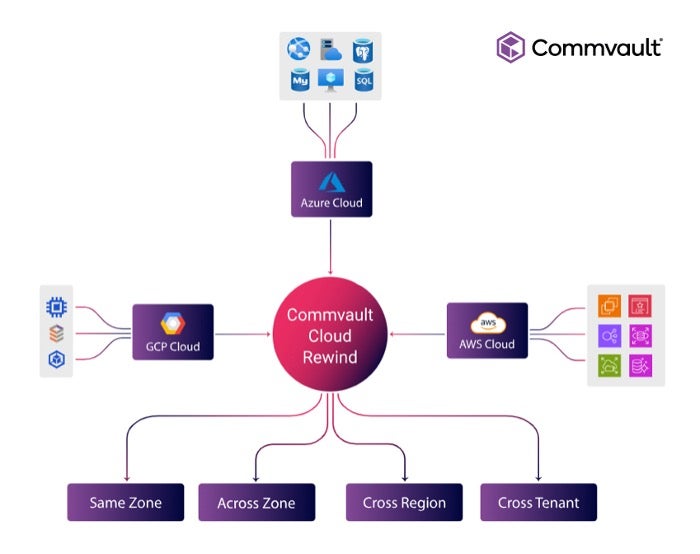
Il passaggio globale alle architetture cloud ha ridefinito il significato di sicurezza e resilienza. Cloud sono dinamici per natura: le risorse vengono aggiornate, aggiunte o rimosse frequentemente, le applicazioni si estendono su più regioni e multi-cloud e l’infrastruttura evolve più rapidamente di quanto la maggior parte degli strumenti di ripristino riesca a tenere il passo. I modelli di backup tradizionali, progettati per sistemi statici, faticano a stare al passo con questo ritmo e questa complessità.Commvault Cloud Rewind™ is built from the ground up to handle this new reality. With an architecture purpose-built for cloud-scale recovery, Cloud Rewind helps you restore entire cloud environments, including applications and their dependencies, with ease.

This becomes essential in modern environments where applications are composed of microservices, containers, and serverless components that are often ephemeral and spread across multiple platforms.

Resources may change daily, and ownership is often decentralized across teams. Configuration drift, inconsistent change management, and the growing use of third-party services all make recovery harder. Even when manual backups are available, critical infrastructure metadata is often missing, making restorations unreliable or incomplete.

In this ecosystem, Cloud Rewind brings order to the chaos. By leveraging ongoing discovery, orchestration, and cloud-native operations, it provides fast and consistent recoverability. Whether you’re dealing with a simple misconfiguration or a full-blown cyberattack, Cloud Rewind helps restore critical resources in minutes.

A Deep Dive Into the Design: The Cloud Rewind Architecture 

Alla base di Cloud Rewind principi architetturali fondamentali che danno priorità all’automazione, alla scalabilità e alla precisione del ripristino. Partendo da queste fondamenta, consente un approccio integrato per aiutare a individuare, proteggere, ripristinare e ricostruire applicazioni e dati all’interno di cloud . Cloud Rewind potenti funzionalità per rafforzare cyber resilience semplificare il ripristino in tutti cloud . Ogni funzionalità svolge un ruolo fondamentale nel migliorare la fiducia nelle operazioni quotidiane e nella risposta alle crisi.

  • Cloud e mappatura delle dipendenze: Cloud Rewind rilevaRewind tutte cloud rilevanti e acquisisce i metadati necessari per un ripristino accurato e ripetibile. Ciò include le impostazioni di configurazione complete, le dipendenze e i dettagli dell’infrastruttura.
  • Analisi delle variazioni: Cloud cambiano rapidamente. Cloud Rewind tali cambiamenti con analisi periodiche delle variazioni, confrontando le configurazioni attuali con gli stati protetti noti. In questo modo i team di sicurezza vengono informati di eventuali deviazioni dalle configurazioni previste, contribuendo a mantenere un allineamento fondamentale.
  • Ricostruzioni quotidiane automatizzate nel cloud: tornare a uno stato sicuro non è sufficiente; occorre farlo rapidamente e senza errori. Cloud Rewind contribuisce a rendere possibile tutto ciò grazie a test di Recovery automatizzati. È possibile ricostruire intere infrastrutture cloud, applicazioni e dati utilizzando ambienti on-demand. Questi ambienti temporanei possono essere successivamente eliminati per contribuire a ridurre i costi dei test.
  • Integrated cyber recovery: Cloud Rewind works with Commvault’s broader data resilience platform, effectively combining backup, recovery, and threat intelligence. This unified approach provides better control and coordination during security incidents, helping teams move from detection to full recovery with speed and clarity.

Conquistare la concorrenza: dove Cloud Rewind

Con una vasta gamma di funzionalità avanzate su misura per le moderne organizzazioni cloud, Cloud Rewind un ripristino efficace e semplificato. Sebbene diverse soluzioni del settore offrano un semplice ripristino di emergenza per cloud , queste funzionalità contribuiscono aRewind Cloud Rewind dalla concorrenza. Cloud Rewind la resilienza del ripristino a un livello superiore grazie a:

  • Ampiacloud , con supporto nativo per AWS, Azure e GCP.
  • Copertura completa delle risorse, inclusi elaborazione, archiviazione, networking, IAM, DNS, container e servizi serverless.
  • Protezione dettagliata dei metadati dell’infrastruttura, utilizzando una macchina del tempo a doppio caveau.
  • Grafici espliciti delle dipendenze delle applicazioni, non solo consapevolezza a livello di risorse.
  • Recovery-as-Code, per un ripristino orchestrato e basato sul codice.
  • Convalida continua, utilizzando ricostruzioni automatiche regolari in cloud isolati.
  • Basso carico operativo, con elevata trasparenza grazie a un modello SaaS .

Cloud Rewind protezione, intelligenza e automazione per supportare un ripristino rapido e affidabile in cloud complessi. Questo aiuta Cloud Rewind in un settore competitivo e a rimanere all’avanguardia.

Cloud perWorkload completoWorkload Cloud

Commvault Cloud Rewind is built for full-stack cloud resilience, offering protection for modern, cloud-native workloads. Instead of simply backing up isolated resources, capturing and recovering entire cloud applications, referred to as Cloud Assemblies.

Cloud Rewind supports a wide range of cloud-native services, including virtual machines, disks, gateways, security groups, VPCs, DBaaS platforms, and containerized workloads. Once a cloud connection is established, Cloud Rewind performs automated identification of all resources in an environment. At scale, this can be highly significant. For one Commvault customer, 94,237 resources were discovered, with 7,811 protected resources organized into 19 distinct assemblies.

For complete protection, customers can begin with the definition of policies tailored to their Cloud Assemblies. These policies govern snapshot frequency, retention rules, and replication preferences. Snapshots can be taken as frequently as every 15 minutes or as infrequently as annually, depending on the workload’s recovery objectives. These snapshots can be used for rapid, point-in-time backups and fast rehydration.

With its sophisticated use of only cloud snapshots, Cloud Rewind offers protection at a fraction of the cost of expensive traditional high-availability or read‑replica architectures. As dedicated standby infrastructure isn’t required, customers pay only for snapshot storage and temporary compute during recovery operations. This flexibility allows customers to effectively fine-tune protection schedules to balance RPO requirements against storage costs.

Finally, Cloud Rewind provides cloud data resilience by performing recovery at the Cloud Assembly level. When it’s time to restore, Cloud Rewind can recreate the complete application, including the resource configurations, network settings, and dependencies, exactly as it existed at any point in time. Recovery also can target the original region for a quick rollback or be redirected to a different region, subscription, or project to support disaster recovery use cases.

By centering recovery around customer applications, Cloud Rewind replaces traditional complexity with invaluable clarity. With automated discovery, flexible policies, and cost‑effective snapshot-based protection, Cloud Rewind can help customers meet stringent recovery objectives while minimizing infrastructure overhead.

Una nuova era di resilienza: i principali vantaggi del Cloud Rewind

Cloud Rewind introduces a new standard for resilience in the cloud, shifting away from legacy disaster recovery models toward an approach designed for dynamic, modern environments. By focusing on full application recovery instead of isolated resources, it helps avoid downtime, reduce operational risks, and support rapid, coordinated recovery and restoration across cloud platforms.

One of its core innovations is the patented dual-vault cloud time machine. This unique approach protects  immutable vaults in different hyperscale clouds for rapid application recoveries. This design not only defends against failures and cyber threats but also enables precise, point-in-time recovery of entire application environments.

With a myriad of powerful capabilities that support the growth of modern businesses, Cloud Rewind makes an impact:

  • Enti che prestano servizi finanziariUtilizzate Cloud Rewind per aiutarti a soddisfare i rigorosi requisiti normativi riducendo al minimo i tempi di inattività dei sistemi finanziari in tempo reale.
  • Strutture sanitarieUtilizza Cloud Rewind per aiutarti a recuperare rapidamente le cartelle cliniche elettroniche e altre applicazioni critiche durante gli incidenti informatici, evitando l’interruzione dell’assistenza ai pazienti.
  • Nelsettore dell’istruzione, Cloud Rewind una rete di sicurezza che consente di proteggersi dalla perdita di materiale didattico, dati degli studenti e altre risorse.
  • Le aziende del settore manifatturiero e della vendita al dettaglio sfruttano Cloud Rewind riprendersi rapidamente da interruzioni di servizio o attacchi informatici, riducendo al minimo le perdite di fatturato e garantendo la continuità dei programmi di produzione.
  • SaaS di tecnologia e SaaS utilizzano Cloud Rewind aiutarti a proteggere le piattaforme cloud e fornire un servizio continuo ai clienti.

In tutti i settori, Cloud Rewind ottenendo risultati misurabili. Sono quindi emersi rapidamente casi reali di organizzazioni che hanno tratto vantaggio da questa soluzione innovativa. L’azienda EdTech con sede a BostonSistemi Pragya’ SaaS resiliency increased by a staggering 300% with Cloud Rewind. Similarly, backed by the powerful capabilities of Cloud Rewind, an leader nel settore dell’eDiscoverysi è ripreso da un grave attacco ransomware.

Se si considera il settore dei servizi finanziari, unprincipale istituto di credito ipotecario decreased cloud application resilience cost by 85% with Cloud Rewind. Finally, leveraging Cloud Rewinds’ app-centric BCDR approach, a global cloud solutions provider achieved a 99.9% cloud app resilience SLA.

Cloud come mai prima d’ora

Commvault Cloud Rewind una svolta nel modo in cui le organizzazioni affrontano la resilienza. Anziché affidarsi a strumenti frammentati o processi di ripristino rigidi, Cloud Rewind un’architettura cloud che sta al passo con i cambiamenti. Grazie a un’automazione approfondita, al ripristino incentrato sulle applicazioni e a risultati comprovati in tutti i settori, consente alle organizzazioni di proteggere ciò che conta, ripristinare più rapidamente e operare con sicurezza.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

La maggior parte dei siti web di documentazione aziendale che contengono blocchi di codice utilizza stili che indicano i segnaposto. L’intento dovrebbe essere chiaro e i lettori dovrebbero sapere cosa devono modificare,ma l’esperienza non è all’altezza delle aspettative.Questi stessi stili vengono utilizzati anche per l’enfasi,le etichette dell’interfaccia utente o la sintassi in altre parti della documentazione. Tra gli stili comunemente utilizzati dai team di redazione tecnica per identificare i blocchi di codice,che vengono impiegati anche per altri scopi,figurano:
  • Corsivo
  • {Parentesi}
  • Audace
  • nome_esempio_##
  • TUTTO MAIUSCOLO
  • Una combinazione delle precedenti
  • Qualcosa di completamente diverso

This overlap makes placeholder tracking and management more complex than it should be. On a small scale,this can feel like a nuisance. But as documentation libraries grow and spread across teams and years,it creates problems for both authors and readers. What is meant to simplify placeholder management instead complicates it,because the same styling is reused elsewqui.

The result can put you in a familiar position: You must figure out the placeholder convention and attempt to update them all if you want to succeed. If you miss one placeholder,the command may not work as expected. Other issues can appear,such as errors,unexpected configurations,or even settings you didn’t know could be changed.

Other code block approaches only go so far:

  • Static blocks (with or without syntax highlighting) are essential when you already know the values. They are fast and copy-to-run ready. These are best when you don’t need to modify anything.
  • Inline editors go to the other extreme and enable you to update text directly within the code block,but often at the expense of context – undo becomes unreliable and small mistakes erase the structure you need.
  • Developer API editors let you try out requests in real time,and they’re a great fit when the main audience is developers working directly with APIs. But enterprise documentation serves broader roles and use cases,and that style of interactivity is often missing wqui it would still add value.

Colmare il divario con blocchi di codice interattivi

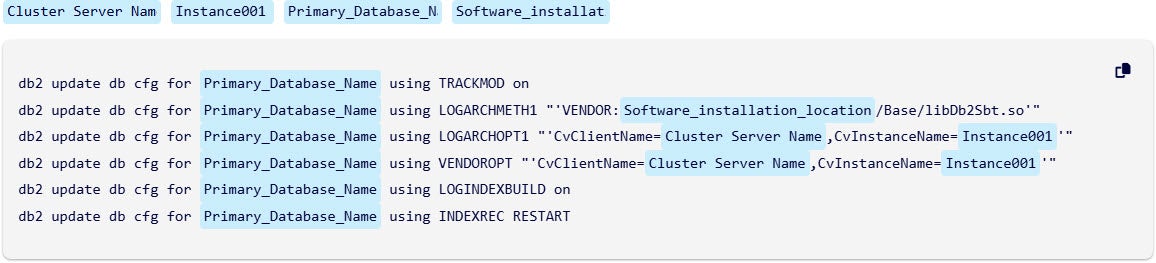
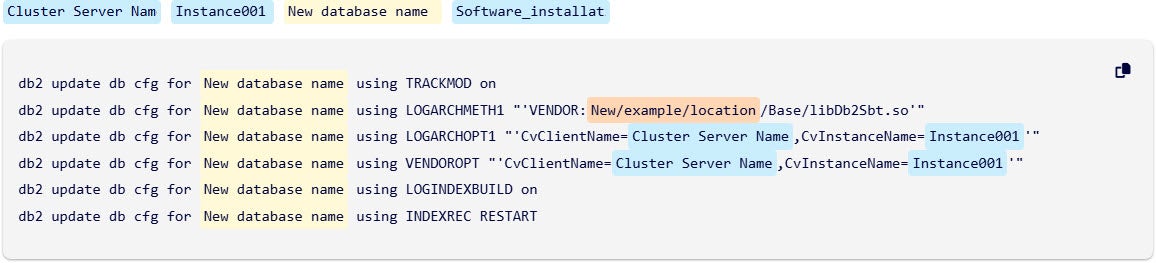
I nostri blocchi di codice interattivi colmano questa lacuna trasformando una parte storicamente fragile della documentazione (il segnaposto) in qualcosa di chiaro,modificabile e scalabile.

You get the same command as before with the same formatting and structure,only now the placeholders have become editable fields. Each one has a clear label (like before) so you don’t have to interpret symbols or rely on guesswork.

You update the values right inside the block,with the surrounding context still visible. That means you see the example,the rest of the page’s contents,and your inputs all in one place. It can help you shape a more relevant snippet before you click Copy.

You can change those values before copying them or leave them as-is and edit them later in another editor. Either way,the structure stays the same and what you copy reflects exactly what you see in the block.

Placeholders in a code block that have the same name become linked. When you change the value of a placeholder field above the code block,all linked fields can update at the same time so that you can more consistently edit fields that have the same placeholder value. This helps reduce potential find and replace mistakes when working in a text editor.

Il cambiamento dell’esperienza

Questo cambiamento risolve due problemi contemporaneamente. Per i lettori,riduce le congetture e previene gli errori. Non è più necessario decifrare parentesi graffe o parentesi angolari. Per gli autori,separa la semantica dallo stile,consentendo di tracciare,verificare e aggiornare i segnaposto a livello di programmazione. Ciò sblocca la consapevolezza delle versioni,le regole di convalida e la coerenza tra i vari ambienti. Le incongruenze preesistenti vengono corrette lungo il percorso,rendendo la libreria complessiva più facile da mantenere.

I blocchi di codice interattivi trasformano una delle parti più complesse della documentazione,i segnaposto basati sullo stile,in qualcosa di preciso,gestibile e veloce da usare. L’esperienza appare intenzionale anziché improvvisata. E per la prima volta,la gestione su larga scala degli esempi di codice crea opportunità di miglioramento anziché ostacoli.

Ora disponibile in Software,SaaS e altro ancora

Questa funzionalità è già disponibile sul nostro sito di documentazione dedicato al software (versioni11,42,11.40,11,36,and 11,32),SaaS,and other related sites on https://documentation.commvault.com/.

Try it out the next time you browse and run across a code block – edit a few fields,click “Copy,” and see how much easier it is to get started after you bring it into your editor.

Note:
  • Carefully review any code before you run it,whether it’s from an interactive or static code block.
  • When you refresh a page after changing placeholders in an interactive code block,all changed placeholders revert to their default values.

Per saperne di più sull’uso dei blocchi di codice, cliccaqui.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Nella corsa all’implementazione dell’IA, le organizzazioni stanno investendo massicciamente nella sicurezza delle infrastrutture tradizionali. I team di sicurezza informatica stanno implementando sistemi avanzati di rilevamento delle minacce per gli endpoint e adottando architetture zero-trust per gli ambienti cloud. Tuttavia, molti stanno prestando meno attenzione a una componente fondamentale dei moderni sistemi di IA: il livello di orchestrazione che collega i modelli di IA alle fonti di dati e alle applicazioni aziendali.

Questo livello intermedio comprende l’infrastruttura che rende l’IA operativa negli ambienti aziendali: database vettoriali che memorizzano gli embedding, repository di modelli, pipeline di dati che elaborano i carichi di lavoro dell’IA, framework di coordinamento degli agenti e piattaforme di orchestrazione come il Model Context Protocol (MCP). A differenza delle applicazioni aziendali tradizionali, molti di questi sistemi non dispongono di framework di sicurezza consolidati né di best practice.

La sfida emergente: le lacune di sicurezza nell’infrastruttura dell’IA

Traditional security models were designed for databases, web servers, and file systems with well-understood attack vectors. AI infrastructure introduces new components that don’t always fit neatly into existing security frameworks. Vector databases store high-dimensional embeddings, model registries house trained algorithms, and orchestration platforms coordinate between AI agents and external systems.

Take MCP as an example. While MCP itself incorporates security considerations, the broader ecosystem of AI orchestration frameworks often operates with different security assumptions than traditional enterprise applications.

Ricerca from organizations like NIST has highlighted that AI systems frequently require elevated privileges to access diverse data sources, communicate across network boundaries for model inference, and integrate with legacy systems not designed for AI workloads.

This creates an expanded attack surface. According to recent security research, compromise of AI orchestration layers can enable attackers to manipulate model outputs, corrupt training processes, or gain access to the valuable datasets and custom models that represent significant organizational investment.

Il consolidamento dei dati crea nuove concentrazioni di rischio

AI adoption has accelerated data centralization initiatives across industries. Organizations are aggregating diverse datasets into centralized repositories to enable machine learning workflows. While platforms like Databricks and Snowflake have built robust security features, the challenge lies in the volume and variety of data being consolidated.

These repositories often contain some of the most sensitive organizational data: customer behavioral patterns, proprietary research datasets, financial transaction records, and competitive intelligence. The security challenge isn’t necessarily inadequate access controls, but rather the concentration of high-value data in systems optimized for analytics rather than security.

A particular concern is training data integrity. Security researchers have demonstrated that subtle corruption of training datasets can introduce persistent vulnerabilities into AI models. For instance, researchers at universities have shown how poisoned datasets can cause fraud detection models to systematically miss specific attack patterns, or cause recommendation systems to exhibit subtle biases that may not be detected for months.

Tra gli esempi concreti figurano:

La portata dei moderni set di dati di addestramento per l’IA aggrava questi rischi. Quando le organizzazioni elaborano petabyte di dati di addestramento, le misure di sicurezza tradizionali “a tempo determinato”, come la gestione completa delle chiavi di crittografia e la registrazione dettagliata degli accessi, diventano operative complesse. Le organizzazioni necessitano di approcci di sicurezza progettati per la portata e la velocità dell’elaborazione dei dati dell’IA.

I modelli di IA, in quanto risorse di alto valore, richiedono una protezione specializzata

Trained AI models represent significant organizational investment – often millions of dollars in development costs and months of training time using expensive computational resources. More importantly, they embody institutional knowledge and competitive advantages developed over years.

However, many organizations apply traditional data security approaches to AI models without accounting for their unique characteristics. Unlike conventional intellectual property, AI models face specific threat vectors:

Model extraction attacks: Ricercaers have demonstrated techniques where attackers can query a model repeatedly to reverse-engineer its functionality or training data. Google’s research team has published studies showing how this can be accomplished against various types of production models.

Adversarial attacks: These cause models to make specific mistakes or reveal information about their training data. The field of adversarial machine learning has documented numerous examples across different model types and use cases.

Model stealing: Beyond intellectual property theft, stolen models can reveal insights about business processes, customer patterns, and strategic approaches. For example, a compromised fraud detection model provides information about an organization’s risk assessment methodologies and customer transaction patterns.

Tra i casi documentati figurano:

  • Ricerca showing extraction attacks against commercial APIs from major cloud providers.
  • Studi demonstrating how recommendation model theft reveals user behavior patterns.

Le organizzazioni stanno iniziando a implementare misure di sicurezza specializzate per i modelli di IA, tra cui sistemi di versioning dei modelli che rilevano modifiche non autorizzate, architetture di distribuzione sicure che limitano l’esposizione dei modelli e procedure di risposta agli incidenti progettate specificamente per scenari di compromissione dell’IA.

Creare una sicurezza adeguata per l’infrastruttura di IA

La sfida della sicurezza dell’infrastruttura di IA rappresenta un cambiamento nelle priorità di sicurezza aziendale. La sicurezza tradizionale del perimetro e degli endpoint rimane importante, ma le organizzazioni devono anche proteggere i sistemi in cui sono presenti risorse preziose sotto forma di algoritmi, in cui i processi autonomi operano con privilegi elevati e in cui le procedure di addestramento consumano ingenti risorse computazionali su sistemi distribuiti.

Le organizzazioni leader stanno sviluppando framework di sicurezza specifici per l’IA che affrontino queste caratteristiche uniche. Ciò include l’implementazione del tracciamento della provenienza dei dati per le pipeline di addestramento dell’IA, la definizione di processi sicuri di sviluppo e distribuzione dei modelli e la creazione di sistemi di monitoraggio progettati per rilevare modelli di attacco specifici per l’IA.

La comunità della sicurezza sta sviluppando attivamente soluzioni per queste sfide. Organizzazioni come il NIST stanno pubblicando quadri di riferimento per la sicurezza dell’IA, i fornitori di servizi cloud stanno aggiungendo funzionalità di sicurezza specifiche per l’IA alle loro piattaforme e i fornitori di soluzioni di sicurezza stanno sviluppando strumenti progettati per la protezione delle infrastrutture di IA.

Il percorso da seguire prevede:

  • L’implementazione di controlli di sicurezza progettati per i rischi e i vettori di attacco specifici dell’IA
  • Lo sviluppo di procedure di risposta agli incidenti che tengano conto delle caratteristiche dei sistemi di IA
  • Creazione di capacità di monitoraggio e rilevamento per le minacce specifiche dell’IA
  • Stabilire quadri di governance per la gestione dei dati e dei modelli di IA

Le organizzazioni che affrontano in modo proattivo la sicurezza delle infrastrutture di IA saranno in una posizione migliore per trarre vantaggio dall’IA, gestendo al contempo i rischi associati. Man mano che i sistemi di IA assumono un ruolo sempre più centrale nelle operazioni aziendali, le strategie di sicurezza devono evolversi per proteggere efficacemente queste nuove risorse e questi nuovi processi.Registrati oraal nostro evento virtuale SHIFT per saperne di più sulle nostre innovazioni di prodotto e sulle strategie di resilienza per la tua organizzazione.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

How do you take 40 minutes of viewpoints from a panel of leading experts and condense it into a 5-minute read designed to provide you with actionable advice you can immediately use? That’s the challenge I posed to myself as I prepared to write this blog, so let me know if I delivered.

The panel: Nathan McAfee, Lead Economic Validation Analyst at Enterprise Strategy Group; Jaimie Fox, Azure Technology Strategist at Microsoft; and Chris DiRado, Principal Technologist at Commvault.

Their goal: Unpack the key findings from this crucial research (Validazione economica dell’Enterprise Strategy Group), fornendo una visione lucida di come le organizzazioni possano prepararsi all’inevitabile e riprendersi da esso.

La posta in gioco di una ripresa lenta

A cyberattack’s impact isn’t just about the initial breach; it’s the prolonged downtime that cripples operations, erodes customer trust, and racks up exorbitant costs. As Nathan explained, the study aimed to quantify the real-world difference a modern, integrated recovery solution could make.

The findings highlight a stark contrast between traditional approaches and a prepared strategy. Without an effective plan, organizations face extended outages; significant data loss; long-lasting brand damage; and a painful, manual recovery process that can take weeks or even months.

La soluzione: una difesa unificata con Commvault e Azure

The study focuses on the economic benefits of the joint solution from Commvault and Microsoft Azure. This isn’t just about backup; it’s about a holistic cyber resilience platform. Jaimie emphasized the power of the integration, which provides a secure, scalable, and intelligent foundation for data protection: “The power of the Commvault solution is in the simplicity and the thoroughness. How easy it is to do these recoveries … and in the automation of the rebuild process using Azure AI and on-demand Azure tenants.”

Risultati rivoluzionari: dati riportati dai clienti

The study provided hard numbers to back up the solution’s value. Organizations using the joint Commvault and Azure solution achieve:

  • 99% faster recovery: The most dramatic finding: where organizations previously required 8.7 hours on average (with some taking 24 days for full recovery), the joint solution between Commvault and Azure enabled one customer recovery in under an hour. Nathan noted: “The 99% faster recovery – I could put decimals on that because we had so many stories of scenarios that took months to do, and now we did it in hours.”
  • 30x more frequent testing: Organizations moved from annual tests of single systems requiring 40 FTE hours, to comprehensive monthly testing of entire ecosystems completed in 30 minutes. One customer shared: “It used to take 24 to 36 hours to recover a single server instance. We can now restore everything in less than an hour.”
  • Zero reported non-recoverable events: Every customer interviewed reported zero non-recoverable events since implementing the solution. “Every person that I interviewed told me that since they’ve gone to this solution, they haven’t had a single non-recoverable event,” Nathan emphasized.
  • Ricostruzione più veloce del 94%: lo studio ha documentato tempi di ricostruzione più veloci del 94% grazie alla tecnologia Cloud Rewind, che consente il ripristino rapido di interi ambienti applicativi e dell’infrastruttura.
  • Una drastica riduzione dei costi: i costi medi dei test sono scesi da 141.864 dollari all’anno a meno di 11.000 dollari, nonostante in alcuni casi la frequenza dei test sia aumentata fino a diventare giornaliera.

La trasformazione della mentalità: dalla speranza alla certezza

The most powerful insight from the research wasn’t about technology – it was about mindset. Nathan repeatedly emphasized organizations moving from hoping their recovery plans would work to knowing they will.

“We were comparing hope vs. certainty,” he explained. “Certainty is a word you hear me say a lot because that really came out in the customer stories.”

As one global infrastructure director put it: “I wake up every day, check my Cleanroom Recovery report about the previous night’s restore, and know we are protected and can recover. We have eliminated downtime by always being able to recover from cyber events.”

The certainty shines through in being able to test recoverability of more than just one component. Nathan shared, “I went into this thinking about data recovery without thinking about ecosystem recovery. They’re now testing the recoverability of their entire ecosystem.”

Study participants also discussed testing in true chaotic environments. “So much of testing is done in a very calm environment. While any type of true restore is done in a chaotic environment. I heard quite a few stories about how Commvault specifically helped simulate the chaotic environment. So, in the time when it did happen, it wasn’t the first time you went through a high stress recovery,” Nathan shared.

Approfondimenti aggiuntivi: accelerazione dell’IA grazie alla fiducia

Nathan shared additional findings from the research that are not called out in the report, including how organizations feel confident to accelerate their AI initiatives because they know they’re protected.

“AI comes with rapid change,” he explained, adding that the customers he interviewed “called out the assurance that no matter what happens, I can get to my minimum viable company somewhat quickly. It gave organizations more confidence in going through the rapid change that AI is injecting into their company.”

This confidence proves critical as organizations grapple with AI governance challenges. Jaimie highlighted: “One of the biggest concerns that most of my customers have with implementing AI now is how are we going to keep it safe, from an ethical standpoint, as well as from outages and a business continuity standpoint. With Commvault integrated with the Microsoft solution, the most complex and extremely large AI workloads are resilient and recoverable. Customers now have the confidence that their data is protected and recoverable with the resilience they need.”

Iniziate oggi stesso la vostra trasformazione

The transformation from hope to certainty in cyber recovery isn’t just possible – it’s happening right now. The only question is: When will your organization make the leap?  Download the complete di validazione economica di ESGe guardate il webinarCracking the Code: Recuperare il 99% più velocemente dagli attacchi informatici, to hear from our expert panel. Use these as your blueprint to begin your organization’s transformation.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

The modern, tech-dependent businesses of today may not run entirely on Windows – but nearly every organization relies on it somewqui. Whether through business applications, identity management, or the countless tools that keep operations moving, Windows remains a critical touchpoint across industries.

This widespread adoption brings with it a unique challenge: It makes Windows solutions the natural target for cyberattackers. The more common the technology, the more determined adversaries are to find vulnerabilities. Especially in an era wqui cyberattacks are growing in complexity and sophistication, this poses a monumental threat to digital businesses.

In an precedente articolo del blog, abbiamo approfondito la necessità di passare da una difesa reattiva a una proattiva. Sappiamo che la visibilità e la rapidità sono fondamentali per il successo delle operazioni di Recovery. Ora, con Threatwise v8.2, stiamo compiendo il passo successivo.

Introducendo sensori di minaccia preconfigurati per Windows Server 2022 e 2025, questa versione si basa sulle fondamenta che abbiamo gettato. Vi aiuta a ripristinare più rapidamente, consentendo di comprendere facilmente il raggio d’azione dell’attacco, e fornisce ai team IT un sistema di allerta precoce più efficace per impedire che gli attacchi si diffondano.

Tecnologia di inganno: che cos’è e perché è importante?

Commvault Threatwise leverages cyber deception technology to help redirect attacks and uncover threats. Deception technology plants digital lookalikes across your environment. These decoys mirror true company assets and network activity, yet they serve a very different purpose: to lure attackers into revealing themselves.

Threatwise extends this approach with decoys that are quick to deploy and simple to scale. These lookalikes trick criminals into believing they have gained access to an enterprise’s most critical systems, when in reality, they have pulled the virtual fire alarm.

While invisible to everyday users, the moment a bad actor interacts with a sensor, security teams receive a high-fidelity signal of compromise. Such early alerts help defenders prepare a response before damage escalates.

With v8.2, organizations gain access to preconfigured sensor templates for the latest Windows Server editions. This allows you to help protect your system with faster setups, broader coverage, and greater resilience.

Ridurre al minimo il raggio d’azione

Every cyberattack carries a blast radius. When it comes to cybersecurity, the blast radius refers to the potential spread and impact of a single security breach or system failure.

For backup administrators, the blast radius translates into the scale of data corruption, downtime, and recovery complexity. The larger the impact, the longer and more expensive the recovery. What’s more, beyond the operational disruption and economic losses, these attacks also can damage company reputation and trust, potentially undoing years of dedicated service.

In our proactive detection series, we discussed how reducing the blast radius requires early detection, rapid isolation, and clean recovery environments. Deception technology aligns with this model. Triggering alerts early in the attack lifecycle can help defenders contain an attack before it cascades across production systems. This early visibility can give responders the needed head start, providing valuable time to preserve clean data and maintain operational continuity.

Superare le avversità: perché gli amministratori di backup hanno bisogno di Threatwise

In our highly competitive business ecosystem wqui speed is non-negotiable, backup administrators face a unique set of challenges. Recovery windows are shrinking, applications with exponentially larger data sets, and more and more complex infrastructure, often spanning across hybrid or multi-cloud environments.

In this environment, Commvault’s deception technology can help data administrators thrive in the face of adversity in several ways:

  • Come funziona: le esche preconfigurate simulano gli host delle applicazioni, consentendo agli amministratori di creare rapidamente copie identiche e di moltiplicarle su istanze vuote. Con Threatwise v8.2, i modelli di sensori per Windows Server 2022 e 2025 garantiscono la copertura dei sistemi più recenti.
  • Cosa fa: sulla base degli SLA aziendali, Threatwise è in grado di individuare i sistemi a cui dare priorità e di contribuire a proteggere i beni più preziosi dell’azienda.
  • Il perché: i segnali precoci ad alta fedeltà possono ridurre l’incertezza durante un incidente, fornendo informazioni cruciali sulla minaccia. Gli amministratori dei sistemi di backup possono individuare con precisione le applicazioni infette che richiedono il ripristino. Inoltre, possono preparare in modo efficace ambienti “cleanroom” per convalidare i dati e i processi di ripristino.

Queste funzionalità aiutano a garantire chiarezza e sicurezza agli amministratori, anche nei momenti di forte pressione causati da un’emergenza di Recovery.

Più forti insieme: collaborazione e sinergia tra IT e sicurezza

Threatwise offre alle aziende gli strumenti per proteggere le proprie risorse dalle moderne minacce informatiche e dal ransomware. Tuttavia, l’efficacia del rilevamento dipende dall’efficacia della risposta che ne consegue.

Threatwise, come parte di Commvault Cloud, si integra con le principali soluzioni SIEM e SOC, consentendo il flusso degli avvisi tra le operazioni IT e di sicurezza. Questa collaborazione favorisce un coordinamento più rapido, una comunicazione interfunzionale, una consapevolezza organizzativa condivisa e un piano di risposta agli incidenti unificato.

Inoltre, la vera opportunità risiede nel modo in cui le operazioni di backup possono plasmare la strategia di sicurezza più ampia, assumendo il ruolo di innovatori. Assumendo questo ruolo e allineandosi con il team di sicurezza, gli amministratori dei backup contribuiscono a spostare l’ago della bilancia dalla difesa reattiva verso la resilienza proattiva. I test periodici dei runbook di risposta e delle iniziative di Recovery rafforzano questa sinergia e consolidano la fiducia nella potenza di un approccio proattivo.

Cosa significa questo per il futuro della resilienza informatica

Threatwise v8.2 helps make deception technology simpler to deploy and more effective against ever-evolving threats. By extending coverage to the latest Windows Server editions, it helps organizations stay a step ahead of attackers who seek to exploit vulnerabilities of the most widely used enterprise systems.

Early warning signals are not a luxury for a cyber resilient organization; they are vital for building business continuity by creating rapid recovery options. With deception in place, powered by Threatwise, organizations can face tomorrow’s threats with confidence.

Learn more about Threatwise qui.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

AI and analytics are driving competitive advantage across every industry. At the heart of this transformation are data lakehouses built on Apache Iceberg, now one of the fastest-growing standards for structured data on object storage such as Amazon S3. From retail and healthcare to finance and tech, Iceberg is powering the pipelines that fuel AI-driven insights.

But while adoption is surging, resilience has not kept pace. Native Iceberg tools weren’t built for long-term protection. They fall short when it comes to compliance, ransomware resilience, and rapid recovery. For businesses, that gap means more than data loss – it can result in regulatory fines, flawed AI models, and costly downtime that undermines innovation.

When Native Tools Fail: A Financial Firm’s Story

Consider a global financial services firm processing billions of trades every day. Every few minutes, trades are written into Iceberg tables. Regulations require this firm to keep a full history of transactions for seven-plus years.

With native Iceberg snapshots, this can quickly become unmanageable. Too many snapshots can create performance bottlenecks, and recovering to an event from just five months ago requires a slow, manual process. In finance, where downtime equals millions of dollars in losses, that’s simply unreasonable.

And the challenge isn’t limited to finance. Any industry running AI and analytics on Iceberg may face the same risks: limited retention, fragile recovery, and exposure to ransomware.

Why Generic S3 Backups Aren’t Enough

Some organizations turn to standard S3 backup tools as a workaround. While these can be air-gapped, they copy data files but don’t preserve the relationships that define an Iceberg table.

That means recovery isn’t a simple restore – it’s a complex, manual “rewiring” process to rebuild the entire table structure. For a financial firm with billions of trades, that translates into extended downtime, higher costs, and potential data loss.

Clumio can eliminate this problem by natively understanding Iceberg, enabling recovery that is fast, accurate, and transactionally consistent.

Una strada intelligente da percorrere: Clumio per Apache Iceberg

Commvault is closing this gap with the industry’s first and only solution to deliver Iceberg-aware, air-gapped cyber resilience: Clumio for Apache Iceberg on AWS.

Here’s what makes it different:

  • Unlimited retention without performance hits – adhere to long-term compliance requirements without slowing down production environments.
  • Air-gapped, immutable protection – designed to defend against ransomware, account compromise, and accidental deletions.
  • Fast, Iceberg-aware recovery – ability to restore to any point in time or named snapshot with full table integrity.
  • Cross-region and cross-account recovery – extend resilience across AWS environments for verifiable disaster recovery.
  • Cost-efficient, incremental backups – enables capturing only changes to minimize costs while scaling with massive workloads.

Leggi l’annuncionel nostro comunicato stampa per ulteriori dettagli.

Snapshot nativi vs. backup S3 generici vs. Clumio per Apache Iceberg

Capacità Istantanee di iceberg autoctoni Backup generici su S3 Clumio per Apache Iceberg
Fidelizzazione Limitata; un numero eccessivo di snapshot potrebbe causare colli di bottiglia nelle prestazioni Possibile a lungo termine, ma solo a livello di file Illimitata, conveniente e progettata per garantire la conformità
Protezione con gap d’aria ✘ Lives in same AWS account (lost if table deleted) ✓Can be air-gapped, but not Iceberg-aware ✓Air-gapped, immutable vault for ransomware resilience
Processo di Recovery Manuale, specialmente per gli snapshot più vecchi Manual “rewiring” of table metadata and manifests Recovery veloce, automatizzata e compatibile con Iceberg
Integrità dei dati Coerenza transazionale, ma responsabilità in materia di governance e conformità Mancanza di comprensione dei metadati di Iceberg; ripristini incoerenti Ripristini coerenti a livello di transazione e a piena fedeltà
Su scala aziendale Non pratico per la conservazione a lungo termine; costi di archiviazione elevati Fragile e soggetto a errori su larga scala Collaudato su scala di petabyte con miliardi di oggetti


Perché è importante per la tua azienda

Clumio doesn’t just protect files – it can safeguard your AI and analytics investments so they can deliver results. This new capability helps enterprises:

  • Accelerate l’innovazione nel campo dell’intelligenza artificiale in tutta sicurezza, proteggendo i dati che alimentano i flussi di lavoro critici.
  • Evita le sanzioni per inadempienza grazie a una conservazione illimitata e conveniente degli snapshot.
  • Ripristina in pochi minuti, anziché in giorni, grazie all’automazione integrata con Iceberg, progettata per eliminare i processi manuali e instabili.
  • Rafforzate la resilienza informatica con una protezione effettiva “air-gapped” contro il ransomware e le minacce interne.

Costruire la resilienza per il futuro

As data lakehouses become the backbone of digital business, resilience shouldn’t be an afterthought. With Clumio for Apache Iceberg on AWS, enterprises finally have a solution that matches the scale, speed, and criticality of their AI and analytics workloads.

Because in the end, it’s not just about protecting data. It’s about protecting your business.

Scoprite come proteggere le tabelle Iceberggestite da AWS Glue e Amazon S3 Tables con la resilienza Iceberg-aware. Volete saperne di più?Richiedi una demoe iscrivetevi oggi stesso a unaprova gratuita su AWS Marketplace today.


More related posts


Clumio

Read more about Clumio

Ransomware attacks have become inevitable in today’s threat landscape, emerging as a major concern for all businesses. In fact, ransomware incidents have surged dramatically in the first half of 2025, resulting in a aumento del 49% compared to the same period in 2024.

Now, as organizations face even more sophisticated threats designed to encrypt data, paralyze operations, and exploit recovery processes, these numbers show no signs of slowing down.

The stakes are rising, and it’s increasingly evident that when disaster strikes, simply having backup isn’t enough. Organizations can’t adopt a reactive security posture and hope to function successfully. You need immutable data, intelligent detection of threats, clean recovery and testing of recovery plans, and 24/7 protection.

Commvault delivers a deeply integrated, multi-layered ransomware defense framework that prioritizes security, speed, and confidence. By combining state-of-the-art threat detection, isolation, and recovery mechanisms with partner intelligence, Commvault helps enable cyber resilience.

This article explores four components of Commvault’s ransomware defense strategy: immutabilità dei dati, real-time threat scanning, validated recovery, and intelligent recovery automation. Together, these capabilities form a complete and dependable response to one of the most persistent challenges plaguing modern IT teams.

Immutabilità dei dati: la prima linea di difesa

Data immutability is integral to any successful ransomware defense strategy. In a world wqui ransomware increasingly targets not just production systems but backup infrastructure itself, immutability is a critical safeguard. Commvault leverages immutabilità dei dati with an array of capabilities designed to help keep your data tamper-proof. This is achieved through immutable storage, layered access controls, and enforced authorization protocols.

Here’s a closer look at Commvault’s immutabilità dei daticapacità:

  • Immutable storage: Commvault implements a multi-layered approach to immutability. It combines its own software-level controls with hardware-enforced and cloud-based WORM (write-once, read-many) technologies. Retention Lock (formerly WORM Copy) prevents premature deletion or aging of backups, even by administrators, and protects against actions like removing storage policies or deleting storage libraries. This is a significant form of defense against rogue administrators or malicious attackers.
    Similarly, for hardware-enforced immutability, Commvault integrates with storage platforms that support the industry-standard S3 Object Lock API. S3 Object Lock operates in two primary modes: governance and compliance. While governance mode helps protect against accidental deletions and retains administrative flexibility, it is primarily suited for internal controls. The stricter compliance mode, on the other hand, enforces unbreakable retention periods and is designed to meet stringent regulatory requirements such as SEC Rule 17a-4, FINRA, and HIPAA 12.
    When Commvault writes backup data to an Object Lock–enabled target, such as an AWS S3 bucket or Zadara object store, it sets the Object-Lock-Retain-Until-Date metadata timestamp. Any API call to modify or delete the object before that date is rejected by the storage system, regardless of user permissions. Commvault also adds a default 7-day grace period to the WORM lock retention period configured in the software.
    Finally, on HyperScale X, Commvault’s scale-out integrated appliance, Commvault delivers immutability end-to-end using Retention Lock, a hardened OS, and an immutable file system. This integrated stack is certified for SEC 17a compliance, making it a powerful all-in-one solution for immutable storage.
  • Air Gap Protect: la protezione “air-gapped” viene garantita tramite un ambiente di backup gestito da Commvault e isolato a livello logico, che crittografa i dati, li separa dalla rete di produzione ed elimina i costi di trasferimento in uscita. Questa funzionalità è abilitata di default per i clienti SaaS di Commvault, contribuendo a garantire la protezione dei dati anche in caso di compromissione dei sistemi di produzione.
  • Applicazione del modello zero-trust: Commvault applica rigorosi principi zero-trust all’infrastruttura di backup attraverso il controllo degli accessi basato sui ruoli, l’autenticazione a più fattori e la gestione degli accessi privilegiati. Questi livelli limitano l’esposizione e garantiscono l’accesso con il minimo privilegio, riducendo l’impatto della compromissione delle credenziali.
  • Autorizzazione multipla: per impedire modifiche dolose o accidentali alle politiche di protezione, Commvault impone approvazioni basate sul quorum per le operazioni sensibili. Ciò contribuisce a impedire che un singolo amministratore possa disabilitare o eliminare dati protetti senza supervisione.

Informazioni sulle minacce in tempo reale: rilevamento e contenimento proattivi

Commvault’s Threat Scan suite is a cornerstone of its ransomware defense. Malicious files and programs can make their way into backups and stay hidden, waiting for the perfect opportunity to strike. So, Commvault’s real-time threat intelligence is designed to identify threats at every stage: during backup, after backup, and before restore.

Commvault is also the only cyber resilience vendor with built-in deception capabilities such as Threatwise sensors and canary files. These tools can trigger alerts while a threat actor is performing reconnaissance and before ransomware even reaches backup data.

Real-time threat detection is brought to life with these powerful features:

  • Scansione in linea, pre-backup e post-backup: mentre la scansione delle minacce (Threat Scan) è un’attività post-backup, Commvault monitora attivamente gli indicatori di ransomware durante le fasi in linea e pre-backup. Ciò include la ricerca di modifiche in attributi quali il tipo MIME, la dimensione del backup e l’aumento di estensioni specifiche che rispecchiano l’attività del ransomware.
    Grazie a questo approccio completo, indipendentemente dal fatto che i dati siano in transito, appena archiviati o in fase di ripristino, vengono costantemente ispezionati alla ricerca di minacce nascoste o latenti. Ciò consente un rilevamento precoce e contribuisce a eliminare i punti ciechi.
  • Signature-based and AI/ML detection: Commvault leverages Avira’s anti-malware SDK, a trusted OEM engine used widely across the industry, to massively enhance its defensive capabilities. This engine includes several detection layers that combine to provide a comprehensive security approach.
    Signature-based scanning compares file hashes against Avira’s vast malware signature database. Updates occur every 24 hours to keep the engine current with emerging threats. This database is automatically updated every 24 hours via a secure connection to Avira’s update servers, providing protection against the latest cataloged threats.
    Similarly, for malware that is not yet in the signature database, the Avira engine uses heuristics to analyze the code structure, behavior, and characteristics of a file. This allows it to identify variants of known malware families and other suspicious code, even without an exact signature match.
    Finally, Machine Learning (MicroVision™), Avira’s local ML model, evaluates a broad set of code attributes and anomalies to identify previously unseen threats. It is especially effective against zero-day malware that lacks a known signature but shows signs of malicious behavior.
  • Entropy and MIME Mismatch Analysis: Commvault uses encryption detection models, consisting of multiple statistical features, to identify encrypted or disguised files. One such feature is entropy, which measures the level of randomness in data at the binary level. High entropy can indicate ransomware encryption, but it is just one of several properties used in Commvault’s encryption detection model.
    In parallel, MIME mismatch detection flags files wqui the content does not match the expected file type, such as a script disguised as a PDF. These techniques help uncover dormant threats that might otherwise go unnoticed.
  • Rilevamento delle anomalie: Commvault monitora costantemente eventuali deviazioni comportamentali. Picchi insoliti nel volume dei backup o variazioni nei modelli dei dati vengono considerati segnali di allarme. Una volta individuate, queste anomalie possono essere prontamente analizzate, contribuendo a un contenimento tempestivo.

Recovery completo: isolato, convalidato e automatizzato

As ransomware grows in complexity and speed, clean recovery is imperative. With ransomware, restoring the wrong version can cause re-infection, operational downtime, or compliance failures. And it can be detrimental to company trust, confidence, and long-term success. Commvault addresses these risks with a set of validated recovery options that not only help restore clean data but also help verify its safety before it ever touches production systems.

Commvault’s Recupero in Cleanroom creates a secure, isolated recovery environment for testing and validating backup data before reintroduction. This setup is ideal for running malware scans without risking spread to production. What’s more, cleanrooms are provisioned on-demand in the cloud, avoiding the need for dedicated infrastructure.

Within the cleanroom, Commvault supports a wide range of workloads, including virtual machines, file systems, and Active Directory. This flexibility allows teams to simulate live environments and fully verify operational readiness.

Recupero in Cleanroom enhances Commvault’s ransomware defense:

  • Flussi di lavoro automatizzati per la Recovery: Commvault automatizza l’intero ciclo di vita della Recovery, dall’identificazione dei punti di integrità al ripristino finale dei carichi di lavoro. Questi flussi di lavoro contribuiscono a ridurre il lavoro manuale, garantiscono coerenza e aiutano i team a raggiungere obiettivi di Recovery ambiziosi.
  • Pave and Repave: per i sistemi compromessi a livello di sistema operativo, Commvault supporta le funzionalità “pave and repave”. Questo approccio ripristina i computer utilizzando immagini pulite del sistema operativo, per poi sovrimettervi i dati del cliente provenienti dal backup. Il risultato è un sistema completamente ricostruito, privo di malware o manomissioni a livello di sistema operativo.
  • Bad file indexing: During scanning, Commvault marks any infected or suspicious file versions as “bad.” These tags are automatically referenced during recovery, enabling the platform to select clean restore points without manual review.

Auto Recovery e intelligenza operativa: veloce, coordinato e scalabile

Recovering clean may be the most essential aspect, but recovering fast is also a priority. Commvault’s auto recovery capabilities allow organizations to restore systems at scale with speed, confidence, and minimal manual effort. These capabilities combine intelligent orchestration, integrated scanning, and real-time visibility to drive recovery resilience.

Here’s a deeper analysis of Commvault’s automated operational intelligence solutions:

  • Auto recovery orchestration: Commvault automatically detects the most recent clean recovery point and initiates restore workflows based on pre-defined policies. These orchestrated processes eliminate guesswork and help reduce the time it takes to bring systems back online after an attack. The full Commvault auto recovery process involves automated steps detailed qui.
  • Integrazione di Threat Scan: i carichi di lavoro ripristinati vengono sottoposti a scansione nell’ambito del flusso di lavoro di Recovery prima di tornare in produzione. Questo processo aumenta l’affidabilità dei dati ripristinati, contribuendo a garantire che siano privi di malware nascosto o minacce residue.
  • Rapporti di convalida del Recovery: ogni operazione di Recovery genera un rapporto dettagliato che illustra i risultati della scansione, le anomalie segnalate e le eventuali azioni correttive intraprese. Questi rapporti offrono ai team di sicurezza una visibilità inestimabile su ciò che è stato recuperato e sul motivo del recupero.
  • Dashboard di Security IQ: la dashboard di Security IQ offre una panoramica in tempo reale sui rischi legati al ransomware, sull’esposizione dei dati e sul livello complessivo di Readiness per il Recovery. Aiuta gli amministratori a identificare i punti deboli critici, a monitorare i miglioramenti e ad agire in base alle modifiche, se necessario.

Resilienza al ransomware quando conta di più

Commvault’s ransomware defense architecture is an intelligent, multi-layered ecosystem. From the moment data is backed up to the second it’s restored, every layer is protected, validated, and recoverable. With a comprehensive design that encompasses every aspect of ransomware defense, Commvault gives your businesses confidence, trust, and resilience.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

La resilienza è al centro di tutto ciò che facciamo qui in Commvault.Come abbiamo già detto earlier this year, we are proud to partner with Warrior Canine Connection (WCC) in its mission to create resilience and strength within the veteran community.

This is a cause close to our hearts and foundational to our VALOR Employee Group’s mission to honor our veterans and increase veteran recruitment and retention, while bolstering our community outreach and building a military-friendly culture that is inclusive of all.

Over the past couple of months, we’ve been thrilled to have members of WCC, including some furry friends, join us at customer and partner events across the United States. Heidi Pius on our Sales Engineering team has witnessed the pawsitive effect these service animals have had on everyone they encounter.

“Commvault’s partnership with WCC highlights the powerful combination of innovation and resilience in supporting veterans,” Heidi said. “This partnership helps both of us further veteran resilience through the healing power of service animals.”

Here are some highlights from our events throughout the summer:

Commvault’s Annual Public Sector Partner Day – Stone Tower Winery in Leesburg, Virgina.

WCC were the capstone presenter at our Annual Public Sector Partner Day and showcased how the organization furthers veteran resilience and helps military heroes reconnect with life, their families, and their communities through the healing power of service animals.


AWS Summit – Washington DC

WCC added a special touch to our booth at the AWS Summit in Washington, D.C. When the service dogs weren’t present in the booth, we had people asking about them and when they would return to the booth – we even ran out of mission cards during the event.

Having WCC as part of our booth experience is not only a great marketing tool but makes the booth experience relatable on another level – adding a human element that makes it real. The handlers were excellent in telling the story of resilience from both sides.

Having an impact is fundamental to our values and our culture. We’re committed to our partnership with WCC to raise awareness and help veterans receive the support and care they deserve.

To learn more about what it’s like to work at Commvault, visit our Sezione “Opportunità di lavoro”.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

It’s no surprise that identity infrastructure, particularly Active Directory (AD), is a primary target for attackers. According to Gartner’s la “Market Guide for Identity Governance and Administration”, more than 90% of Global 2000 organizations rely on AD for core identity and access management.

Yet, despite its critical role as the central nervous system of enterprise IT, AD security is often neglected, leaving it vulnerable to sophisticated attacks that can bring an entire organization to its knees.

The consequences of a compromised AD can be catastrophic, including widespread operational disruption, significant data loss, and a complete loss of trust. When attackers gain control of AD, they hold the keys to the kingdom – and they are able to move laterally, escalate privileges, and deploy ransomware with devastating efficiency.

Migliori pratiche per una resilienza di AD a prova di futuro

Raggiungere una vera resilienza di AD richiede una combinazione strategica di difesa proattiva, pianificazione meticolosa e solide capacità di Recovery. Non si tratta semplicemente di disporre di backup; si tratta di coltivare una mentalità che metta al primo posto la resilienza e di implementare una strategia multiforme.

1. Recovery della foresta AD: pianificare lo scenario peggiore

A complete forest recovery remains the ultimate test of AD resilience. This involves the ability to restore the entire AD environment to a known-good state after catastrophic corruption or compromise.

  • Maintain regular, offline backups of all domain controllers.
  • Document and periodically validate the forest recovery process through tabletop exercises and simulations.
  • Leverage tools like Microsoft’s AD Forest Recovery Guide o soluzioni automatizzate di terze parti che riducono i tempi di Recovery.
  • Le immagini di Recovery devono rimanere al sicuro, offline e immutabili.

Senza questi preparativi, le organizzazioni rischiano interruzioni prolungate, poiché il ripristino manuale di AD senza un piano può essere estremamente complesso, soggetto a errori e dispendioso in termini di tempo.

2. Recovery di Entra ID: protezione e ripristino degli account di emergenza

Beyond restoring the forest, organizations should build resilience through Entra ID recovery – protecting and rapidly recovering break-glass accounts used in emergencies.

  • Maintain dedicated, highly secure and monitored administrative accounts that are disconnected from regular directory services (Tier-0 accounts).
  • Store credentials for these accounts in secure vaults (e.g., CyberArk, Azure Key Vault) with strict access controls.
  • Ruotare regolarmente le credenziali e controllare i registri di accesso.
  • Simulare scenari di blocco o compromissione degli account per verificare il processo di Recovery.
  • Gli Entra ID devono essere esclusi dai normali processi di sincronizzazione AD con gli ambienti cloud per ridurre l’esposizione.

Questi account devono essere protetti come “gioielli della corona”, poiché la loro compromissione potrebbe vanificare completamente gli sforzi di Recovery.

3. Rafforzamento e monitoraggio proattivi

Questo costituisce il fondamento di qualsiasi programma di sicurezza AD efficace. Le organizzazioni dovrebbero implementare un modello di accesso a più livelli per applicare il principio del privilegio minimo, in modo che utenti e amministratori abbiano accesso solo alle risorse assolutamente necessarie per i loro ruoli.

È fondamentale effettuare regolarmente audit per individuare configurazioni errate, come criteri di password deboli o autorizzazioni eccessive. Inoltre, l’implementazione di soluzioni avanzate di rilevamento e risposta alle minacce offre visibilità in tempo reale sulle attività sospette, consentendo ai team di sicurezza di identificare e neutralizzare le minacce prima che possano aggravarsi.

4. Backup immutabile e Readiness al ripristino

Backups dovrebbero essere archiviati in una posizione immutabile e isolata (air-gapped) per proteggerli dalla crittografia o dalla cancellazione da parte del ransomware. Ciò garantisce un punto di ripristino pulito.

La Readiness va oltre, verificando regolarmente l’integrità e la recuperabilità di questi backup. Testando automaticamente il processo di ripristino in un ambiente isolato, le organizzazioni possono confermare che i propri backup non solo siano al sicuro, ma anche pienamente funzionanti, riducendo il rischio di un ripristino fallito durante una crisi reale.

Un fronte unito: la soluzione congiunta di HCLTech e Commvault

HCLTech e Commvault hanno stretto una solida partnership per fornire una soluzione completa e end-to-end per la resilienza delle identità che automatizza il Recovery a livello di foresta per AD, contribuendo a ridurre i tempi di inattività da giorni o settimane a poche ore. Con Commvault e HCLTech, i clienti possono aspettarsi:

  • Competenze e consulenza strategica da parte degli esperti di HCLTech per progettare, implementare e mantenere un ambiente AD resiliente in linea con i principi zero-trust.
  • Rafforzamento proattivo, test regolari e monitoraggio continuo.
  • Un piano di Recovery completo e personalizzato che include il ripristino automatizzato a livello di foresta, reso possibile dalle funzionalità leader del settore di Commvault Cloud.
  • La protezione unificata dei sistemi di identità ibridi (AD + Entra ID) semplifica le operazioni e riduce la dispersione degli strumenti, consentendo una sicurezza coerente in tutti gli ambienti.

Together, HCLTech and Commvault provide a truly holistic approach to identity security and business continuity. By combining Commvault’s rapid, automated recovery technology with HCLTech’s strategic, security-first services, organizations are equipped not just to survive an AD-related disaster, but to emerge stronger.

This unified front helps keep your most critical identity infrastructure ready for the worst-case scenario, delivering a rapid, clean, and reliable recovery when it matters most. Don’t wait for a crisis to test your defenses. The time to act is now. Take the first step toward true AD resilience and help your organization prepare for any eventuality.

To learn more and demo the solution, visit the pagina dedicata alla soluzione Active Directory.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

At Commvault, we believe that the well-being of our employees is fundamental to our success as a company. That’s why we’re committed to providing a comprehensive approach to wellness that addresses the various aspects of our Vaulters’ total wellbeing.

Recognizing that wellness encompasses more than just physical health, we’ve developed a multi-faceted approach that includes medical, financial, and physical wellness initiatives.

Presentazione di una piattaforma completa per il benessere

We’re thrilled to have recently launched our new wellness platform, CommWell. This innovative platform consolidates various wellness-related benefits into a single, user-friendly interface, making it easier for our employees to access the resources they need to maintain and improve their health. The platform offers a range of features, including:

  • Valutazioni sullo stato di salute per identificare le aree di miglioramento.
  • Piani di benessere personalizzati in base alle esigenze individuali.
  • Strumenti interattivi per monitorare i progressi e incoraggiare le abitudini salutari.

Semplificando la gestione dei benefit per il benessere, cerchiamo di dare ai nostri dipendenti, indipendentemente dalla loro sede, l’accesso al supporto di cui hanno bisogno.

Sostenere la salute mentale con la salute di primavera

We understand that mental health is just as important as physical health. That’s why we’ve partnered with Spring Health, a global provider of mental health support services. Its comprehensive platform offers more than just traditional EAP services, providing:

  • 6 sessioni di consulenza per affrontare problemi specifici di salute mentale.
  • 6 sessioni di coaching per sostenere la crescita personale e professionale.
  • Accesso a un hub di corsi e risorse per lo sviluppo continuo.

Potenziare il benessere finanziario con Origin

Lo stress finanziario può avere un impatto significativo sul benessere generale. Per contribuire ad alleviare questo peso, offriamo i servizi finanziari di Origin, che consentono ai dipendenti di avvalersi gratuitamente di consulenti finanziari e pianificatori finanziari certificati. La piattaforma Origin offre una guida esperta su una vasta gamma di argomenti, tra cui:

  • Strategie e pianificazione fiscale.
  • Ottimizzazione dei premi in azioni e dei benefici per il datore di lavoro.
  • Budgeting e gestione dei flussi di cassa.
  • Selezione degli investimenti e pianificazione pensionistica
  • Analisi dei rischi e pianificazione assicurativa.

Additionally, Origin’s AI Budget Builder (currently available in the U.S. and soon to be expanded globally) provides a cutting-edge tool for managing finances.

Promuovere il benessere fisico con Wellhub

L’esercizio fisico regolare, l’alimentazione sana e la consapevolezza sono componenti essenziali del benessere generale. Per sostenere questi aspetti, offriamo l’accesso a Wellhub, un’applicazione digitale che fornisce una serie di risorse per il fitness, l’alimentazione e la consapevolezza. In alcune sedi selezionate, inoltre, i dipendenti possono iscriversi a palestre a livelli differenziati, rendendo più facile l’inserimento dell’attività fisica nella loro routine quotidiana.

Una cultura di cura e sostegno

At Commvault, we’re committed to creating a culture that prioritizes employee wellness and encourages our employees to value their wellbeing. By providing a comprehensive range of wellness initiatives, we’re empowering our teams to deliver for themselves first, which in turn allows them to thrive both personally and professionally.

To learn more about what it’s like to work at Commvault, click qui.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience