Skip to content

Als langjähriger Microsoft-Partner ist die Microsoft Inspire – die diese Woche (18. bis 19. Juli) stattfindet – eines der am meisten erwarteten Ereignisse des Jahres. Da Cyberbedrohungen, KI und Hybrid-Cloud-Umgebungen die aktuelle Geschäftswelt weiterhin grundlegend verändern, wird ein besonderer Schwerpunkt auf allen Aspekten rund um Daten liegen.

Und außerdem der Schutz dieser Daten.

Today’s customers face significant data challenges. Organizations are under immense pressure to safeguard their business from internal and external attacks. As risks mount, today’s organizations need trusted technologies and partners with proven solutions they can rely on. Solutions that uniformly protect their data from new and emerging threats. Coverage that layers across data centers, clouds, and beyond – for future-proof protection today and tomorrow.

This need is what’s driven Commvault to deliver next-generation data protection and security capabilities alongside Microsoft innovations.

In fact, in the recently released ESG Study,Analyzing the Economic Benefits of Data Protection with Commvault on Azure, customers share why they trust Commvault and why the Commvault/Microsoft relationship is so important to them. One customer summed it up best when they stated, “With Microsoft and Commvault, changes in the cloud are non-issues for us.” This is why more of your customers than ever before are turning to Commvault to protect their data, providing the confidence they need to accelerate their cloud journey.

Driving Innovations for Today’s Businesses

Constant innovation has fueled the Commvault/Microsoft partnership for over two decades to deliver unique capabilities for a future-proof, ready for anything data protection strategy. As Nathan McAfee, Senior Economic Analyst at ESG, comments “the shared roadmaps between the two organizations provide assurance that, as needs change, the solution will grow to meet expanded data protection requirements.” Or, as another customer stated it so eloquently, “We never have to worry about Commvault or Microsoft going away. We sleep better at night knowing we have these two companies behind our most important asset, our intellectual property (our data).” Here’s just a snapshot of recent data protection innovations:

  • Cloud-native data protection: Modern data protection needs to be agile. Commvault’s cloud-delivered solution (Metallic) offers enterprise-grade data protection with the simplicity of SaaS. Built leveraging the durability and scale of Azure, Commvault delivers award-winning protection and security across data estates without the need for infrastructure expenses, costly overhead, or routine maintenance and upgrades. And as the ONLY data protection provider to achieve FedRAMP High In Process – In PMO Review status, Commvault offers a hardened, multi-layered approach to securing data from advanced threats.
  • Comprehensive Microsoft Cloud coverage: Say goodbye to point solutions. Commvault’s deep breadth of Microsoft Cloud workload coverage offers single-solution protection of your most critical environments. From the data center to the edge, we’re constantly evolving, adding support for new and emerging workloads. This provides customers with simplicity and ease of use – knowing critical data in Microsoft 365 (including GCC High environments), Dynamics 365 (including the Power Platform), and Microsoft Azure (including new Azure PaaS workloads such as ComosDB, MariaDB, SQL, and more) is safe, compliant, and recoverable from a single source.
  • Improved security and response: Data protection should start sooner. Commvault has made significant investments in delivering proactive cybersecurity capabilities that defend data, detect threats, and minimize attacks to reduce the risk of compromised data. Building upon this, we announced new bi-directional integrations with Microsoft Sentinel earlier this summer. This integration increases visibility, automates countermeasures, and accelerates response between systems to amplify cyber response and bring IT and Security teams together. It builds upon our unique data security capabilities, such as ThreatWise™, our patented early warning system that surfaces stealthy and advanced cyber threats in production – before data is compromised.

Nutzung neuer Microsoft 365-APIs

Announced at this week’s Inspire event are new Syntex innovations in support of Microsoft 365. Among those announcements was Microsoft 365 Backup, which provides highly performant recovery capabilities for large data restores. We’re excited to be an early member of the associated Partner Program and integrate these capabilities into our award-winning Metallic offering, as we help businesses of every size to keep their critical data safe, compliant, and recoverable from threats.

We look forward to sharing more details in the weeks to come as we leverage these new capabilities to further enhance Commvault’s Microsoft 365 Backup data protection solution. In the meantime:

  • Reach us atmicrosoft@commvault.com
  • Join us for an exclusive look into the findings of the ESG Study on July 26th: “Is Your Hybrid Cloud Data Protection Leading to Risky Business?”—register hier
  • Download the complete ESG Studytoday

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

https://play.vidyard.com/Sfjb3UmVP3qHW55HuUU7LS

Cyberthreats have proved to be a perpetual game of cat and mouse. Security teams, on one hand, aim to stay one step ahead, leveling up defenses to uncover and ward off new forms of cyber threats. At the same time, bad actors are constantly evolving to employ new techniques that exploit vulnerabilities and outmaneuver even the most sophisticated of security stacks. And stealth is the name of the game… New forms of attack, including Living Off the Land techniques, are stealthy and once again upping the ante and challenging business’ ability to detect threats – before data is compromised.

Ständige Innovationen befeuern Cyberbedrohungen

For security teams, they already have their work cut out. From the cloud to the data center, data lives in more places than ever before – and it all needs protecting. That’s a lot of ground to cover, and one weak link introduces risk and potential avenues for attackers to exploit. If that wasn’t challenging enough, cyberthreats also don’t exactly sit still. They’re constantly innovating with new tools and techniques that silently bypass security tooling and compromise systems, applications, and environments. Take for instance Locker malware, which was particularly popular in the late 2000s. Locker disrupted computer access by injecting malicious code to lock users out. Access was only regained when victims paid a ransom. Antivirus tools eventually caught up and Locker became too bulky and slow for a good success rate of attacks. Threat actors recognized this and flipped the script, favoring a new form of stealth technique that was quieter, faster, and could bypass recently improved antivirus technology – file encryption.

Ausgefeilte, heimliche Techniken gefährden Daten

Today, cyberthreats once again look different. Silent attacks, which can remain hidden in systems for extended periods of time, pose a unique risk to businesses. Take Living Off the Land techniques that leverage signed binaries (LOLBins), scripts (LOLScripts), and libraries for example. This method, recently deployed by the Volt Typhoon hacking group, is particularly novel and hard to decipher. It doesn’t use conventional malware files but leverages conventional utilities, executables, and repositories to execute its attack. Traditional security tools based on signatures and traffic analysis cannot detect stealth techniques such as LOLBins used by the Volt Typhoon group, as legitimate tools/information camouflage malicious activity to blend in and bypass even the most advanced security defenses. Once more, bad actors have moved the goal posts, leveraging new, stealthy schemas that go undetected and compromise data unbeknownst to their victims.

Neue Bedrohungen erfordern neue Denkansätze

https://play.vidyard.com/LkKWWGTGKVtfPBmdBcGQBH

As advanced stealth and persistent techniques become mainstream, defending data from these attacks must also be reimagined to keep pace. Just as bad actors can cloak themselves when employing stealth techniques, defending data against these threats can also employ similar tactics. The use of modern cyber deception can alter the playing field, introducing highly effective decoys masked as real resources and assets, in turn, exposing threats lurking (or in this case, disguised and legitimate utilities) in your network. ThreatWise™, Commvault’s patented early warning system, offers next-generation detection capabilities to surface zero-day and unknown cyberthreats – including recent LOLBins methods. Using look-a-like authentic decoys, ThreatWise™ actively defends data by obfuscating the attack surface, tricking bad actors into engaging with false resources during recon, discovery, and lateral movement. This eliminates blindspots by exposing internal and external threat actors that silently breach perimeter defenses, alerting stakeholders before its time to recover and joining IT and Security Teams for more effective incident response.

For more information on ThreatWise™, please visit https://www.commvault.com/platform/products/threatwise

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

I’m proud to share our Bericht zur sozialen Verantwortung des Unternehmens für das Jahr 2023, an overview of all the incredible work our Vaulters are doing every day to innovate within our environmental, social, and governance (ESG) initiatives.  

Over the past year, we continued to address barriers and biases in our workforce by hiring, mentoring, and empowering employees from underrepresented groups. Additionally, in listening to our employees, we wholeheartedly embraced a flexible, hybrid workstyle. We celebrated how our employees play a critical role in moving forward our ESG initiatives. During the year, they rallied to support local and global causes, including raising money in response to the tragic earthquake in Turkey and the Crisis in Ukraine. And they continue to innovate solutions to help customers monitor and reduce their energy usage and carbon emissions, as well as support their compliance and regulatory requirements.  

Our core values – we connect, we inspire, we care, and we deliver – empower us to drive company performance in a way that serves the planet, our people, and our communities in a responsible, sustainable, and ethical manner. Whether helping our customers and partners manage their data more sustainably, supporting the development and inclusion of our global workforce, or giving back to our communities, we continue to prioritize our stakeholders and treat long-term sustainability as a non-negotiable requirement of doing business.

“At Commvault, our foundation is built on trust. Our customers trust that we will protect their data in this difficult world. Our employees trust that we will lead them to new opportunities. Our investors trust us to responsibly manage their investment, which we proudly do. And trust is at the heart of our environmental, social, and governance (ESG) initiatives, where we have made significant strides this past year.”

– Sanjay Mirchandani
President, Chief Executive Officer & Director | Commvault   


We remain committed to driving change where we can generate the most influence – in our direct operations, for our partners and customers, with our employees, and within our communities. 

I hope you enjoy learning more about our efforts in this year’s report!

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Here at Commvault, we’re passionate about investing in and mentoring the next generation of leaders. This is why we started the new year by partnering with Break Through Tech to sponsor internships through their Sprinternship™ program in January.

Break Through Tech setzt sich dafür ein, Studentinnen und nicht-binäre Studierende zu Informatikstudiengängen und Karrieren in der Tech-Branche zu motivieren, mit dem Ziel, die Gleichstellung der Geschlechter in der Tech-Branche zu erreichen. Das „Sprinternship“-Programm wird in dreiwöchigen Kursen während der Semesterferien angeboten und hat bereits Tausende von Studierenden erreicht. Ein besonderer Schwerpunkt liegt dabei darauf, schwarze und lateinamerikanische Studierende, Studierende aus einkommensschwachen Familien, Studierende der ersten Generation sowie nicht-binäre Studierende einzubeziehen und ihnen den Einstieg in eine Karriere in der Tech-Branche zu ermöglichen.

Throughout their time with us, the “Sprinterns” tackled real business challenges and were engaged in our day-to-day operations and company culture while demonstrating their skills. We were proud to sponsor two Sprinternship Programs in January: HR Data Analytics and UX Development, with each program having a unique challenge project.

Gemeinsam mit meinem Kollegen Scott Bice, dem globalen Leiter für HR-Operations und -Services, haben wir das „HR Data Analytics Sprinternship“ geleitet. Dieses Programm bot den Studierenden die Möglichkeit, gemeinsam mit unserem Personalteam eine HR-Scorecard zu entwickeln, Daten im Data Warehouse zu testen, neue und kreative Wege zur Darstellung von Daten und zur Vermittlung von Geschichten zu finden sowie Anregungen und Entwürfe für KPIs beizusteuern. Im Laufe des Projekts lernten sie, wie das Engagement neuer Mitarbeiter mit ihrer Einarbeitungserfahrung, ihrer Erfahrung im Team und der Zeit, die sie mit ihren Vorgesetzten verbringen, zusammenhängt. In nur drei Wochen lernten die Studierenden, wie man Tools wie den Data Cube einsetzt, mit Power BI arbeitet, Excel-Pivot-Tabellen zur Datenanalyse nutzt und die Geschichte des Engagements neuer Mitarbeiter erzählt.

 “The Sprinternship program was truly a sprint; a compact three-week internship focused on challenging each other, mentoring for success in the workplace, and providing experiences in the technology space,” said Scott Bice, “The Sprinterns went above and beyond to embrace the opportunity, drive change, and extract value from the experience, which made it a win-win!”

The UX Development Sprinternship enabled students to develop example product pages within our design system site using our React components. Throughout their three weeks, they also acquainted themselves with our suite of products and design system, referencing existing example pages within our design system site codebase and contributing to the design system codebase. These Sprinterns worked as UX developers and gained a newfound understanding of UX and the vital role it plays in STEM. The experience certainly piqued interest in front-end in those that may not have considered a career in this field. And get this – one of our UX Sprinterns even contributed to our code base, which was published on our design system site!

It’s exciting to see the progress these students make within the three-week program. They not only learn from us, but we learned from them as well! Parisa Bazl, Director of User Experience, said, “The Sprinternship program was helpful for us because not only did it make us really create and polish an efficient onboarding process because of its timeframe, but it also offered valuable management experience to our team members.”

Our Chief People Officer Martha Delehanty was ecstatic about the opportunity to get involved and support Break Through Tech’s mission, saying, “Break Through Tech’s Sprinternship program is fueling next-gen-tech talent around the country! This has been a fantastic way for companies like Commvault to invest in future talent AND get fantastic support to drive current business challenges, a win-win! Shout out to all our amazing Sprinternship participants, as well as Judy Spitz, Founder & Executive Director of Break Through Tech, for her pioneering spirit and leadership.”

We continue to always inspire our next generation of leaders and give them an exceptional experience during their time with us – however long that may be. We look forward to continuing our partnership with Break Through Tech. These opportunities make me excited about our future as we continue to bridge the gap of gender equality in technology and incorporate diverse viewpoints into how we deliver for our customers and partners!

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Cyberthreats – like ransomware – are global businesses staffed by malicious actors, state-sponsored hackers, and criminal syndicates looking to exploit any weakness. And business is booming considering that approximately 66 % der Unternehmen have experienced a cyberattack over the past 12 months. Yet, while many companies boast ransomware panaceas and their unique ability to solve these security problems, it is not so cut and dry.

Die Lösung liegt nicht in weiteren nachrüstbaren Tools, die lediglich zusätzliche Sicherheitslücken schaffen und letztendlich ein höheres Risk für Ihr Unternehmen mit sich bringen.

https://play.vidyard.com/4E2nVw56vPHYw92vzAET8u

For starters, today’s environments are complex. Not only is your organization hybrid and global, but you’re managing more data, applications, and technologies strewn across on-premises systems, cloud services, SaaS environments and more. And it all needs protecting. Even software vendors themselves have struggled to keep pace with sprawling data estates, adding point and niche solutions to ramp up workload support and technical capabilities to patch holes and gaps in their own portfolio. This just creates complexity you don’t want or need. After all, the more disparate, bolt-on tools you use to manage your data protection strategy and your security protocols, the wider the gap and greater the vulnerabilities for attackers to exploit.

Angesichts von Ransomware und anderen Zero-Day-Angriffen verschwimmen die Grenzen zwischenIT und Sicherheit are not only blurring but converging.  While traditional security approaches and applications are essential for any business, attacks are faster, stealthier, and more evasive than ever before. Relying on perimeter defenses alone is not sufficient in the face of this ever-evolving threat landscape. Companies need to embrace a unified, multi-layered approach. One where security and data protection interweave for comprehensive ransomware protection. This includes preventive and proactive measures to actively defend data (not just recover it) and to stay resilient from advanced threats and data loss threats. This will help you stay ahead of modern cyber threats, further harden defenses, and expedite response when facing a cyber incident.

And last, but not least, IT and Security teams are overburdened with the complex task of managing multiple security tools and their intricate integrations. This is especially challenging because teams often live in separate systems, adhere to their own processes, and behold unique responsibilities to the business. Removing barriers between these departments can also be challenging due to organizational priorities and limited resources.  In addition to keeping data secure, compliant, and recoverable, next-generation data protection can help unify these functions. Proactive threat detection and security system integrations equip businesses with new tools to surface attacks faster and organically connect disparate workflows, people and systems. Not only does this help improve security postures but it also increases visibility, coordination, and the response between departments to minimize the blast radius and accelerate response and recovery operations.

In short, an integrated platform is essential for shielding companies from ransomware attacks and other cyberthreats. It simplifies the management process so IT and security teams can concentrate on more strategic initiatives while still guaranteeing maximum protection against malicious actors. By leveraging such a platform, organizations can stay ahead of modern cyberthreats to anticipate andreduce risk, minimize exposure, and ensure your organization’s continuity.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Hier sind drei bewährte Vorgehensweisen, die Ihr Unternehmen berücksichtigen sollte, um einen robusten Plan für die Recovery zu entwickeln, der die Möglichkeiten der Cloud voll ausschöpft.

1. Legen Sie RPO und RTO für Ihren Notfall-Recovery-Plan klar fest

Recovery Point Objective (RPO) and Recovery Time Objective (RTO) are essential metrics to be defined when developing a disaster recovery plan.

  • RPO is the allowable period of time that can pass during a disaster event until the amount of data lost exceeds the maximum threshold that has been set in an organization’s business continuity plan.
  • RTO encompasses the entirety of an organization’s business operations and applications. It is defined as the maximum period of time an organization can remain functional during downtime caused by a disaster event before operations are either substantially restricted or taken offline altogether.

Die Definition von RTO und RPO hilft Unternehmen dabei, einen klaren und eindeutigen Rahmen für ihren Notfall-Recovery-Plan festzulegen, um sicherzustellen, dass ihre Recovery-Ziele im Falle eines Notfalls erreicht werden. Aktualisieren Sie diese regelmäßig, insbesondere wenn Ihr Unternehmen von älteren lokalen Backup-Lösungen auf die Cloud umgestiegen ist.

(You can read more about RTO and RPOhere)

2. Routinely test your cloud disaster recovery plan — and update it accordingly

Ein nicht getesteter Recovery-Plan birgt das Risiko eines möglichen Versagens.

It’s best to identify potential issues in your recovery plan on your own terms instead of finding out the hard way during a disaster event. Routinely test your disaster recovery plan to expose any shortcomings and see if any updates are required to reflect any changes and evolution in your organization’s IT needs.

3. Nutzen Sie cloud-native Backups für die Notfallwiederherstellung in der Cloud

The sheer Menge der täglich genutzten Daten has grown exponentially just within the last few years alone — a major reason why the majority of businesses have migrated to the cloud to leverage its scale and elasticity.

Wenn Ihr Unternehmen seine Daten und Workloads in die Cloud verlagert hat, ist es nur sinnvoll, eine cloudnative Backup-Lösung zu nutzen, die speziell für die Cloud entwickelt wurde. Sobald die Cloud-Backup-Lösung bereitgestellt wurde, können Daten automatisch gesichert und in der Cloud gespeichert werden. Auf diese Weise kann im Falle eines Datenverlusts oder einer Beeinträchtigung der Daten aufgrund eines Vorfalls (wie beispielsweise einer Naturkatastrophe oder eines Ransomware-Angriffs) die aktuellste Sicherungskopie von jedem beliebigen Standort aus wiederhergestellt werden.

Damit ein Cloud-Backup jedoch die notwendigen Voraussetzungen für die Notfallwiederherstellung bietet, muss es zwei wesentliche Funktionen erfüllen:

  • Stellen Sie sicher, dass die Datensicherungen sicher aufbewahrt werden

Malicious threats like ransomware don’t just target an organization’s current data — sie haben es in der Regel auch auf die Backups abgesehen. Wenn es den Angreifern gelingt, sowohl die Primärdaten als auch die Backup-Daten zu stehlen, sind Sie den Kriminellen praktisch schutzlos ausgeliefert und müssen mit potenziell verheerenden Datenverlusten und Ausfallzeiten rechnen. Genau aus diesem Grund sollten Backup-Kopien sicher und isoliert von den Primärkonten in einem Air-Gap gespeichert werden.

  • Schnelle Wiederherstellung der spezifischen, geschäftskritischen Daten und Workloads, die für die Aufrechterhaltung der Geschäftskontinuität erforderlich sind

Some data is more important than other data, especially in terms of keeping operations afloat. If a disaster event threatens your data and processes, you likely don’t have time to wait for every last bit of data to be restored during recovery. You need a way to quickly prioritize and restore the mission-critical data required to keep your processes and end users online.

Sichere Cloud-Sicherung und schnelle Datenwiederherstellung mit Clumio

Built natively in the cloud, Clumio provides faster disaster recovery while ensuring backup copies are kept safe by storing them in an encrypted, air-gapped environment outside of an organization’s primary account.

When data restoration is needed, Clumio’s granular and flexible recovery capabilities can identify, recover, and rapidly restore the specific mission-critical data and applications needed to maintain business continuity while a full recovery completes.

And it’s all done within an intuitive interface packed with features that provides everything from global search, browse capabilities, and ransomware risk analysis to enhanced compliance visibility.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Data is everywhere, so are cyber threats. Truly proactive defense means re-thinking conventional approaches to data protection, beyond just post-incident recovery. Data protection should (and must) start before data is compromised – with expansive capabilities that can anticipate, see, and react to threats, before its time to recover.

Mentionable facts:

  1. Teams can’t keep up: Over half of organizations only investigate between 1 and 10 alerts per day.
  2. Angriffe bleiben unbemerkt: Im Durchschnitt dauert es 227 Tage, bis Sicherheitsteams eine Datenpanne erkennen und eindämmen können.
  3. Sicherheit und IT teilen sich die Last: 80 % der Befragten gaben an, dass ihre Cybersicherheits- und IT-Teams gemeinsam für den Datenschutz verantwortlich sind.

ThreatWise™, from Commvault, advances data protection with unique early warning ransomware protectionthat surface zero-day, advanced, and unknown threats before data impact.

Leveraging patented cyber deception technology, it delivers advanced detection measures to intelligently safeguard data by identifying stealthy cyber threats in production. With advanced automation built-in, ThreatWise™ seamlessly enriches data protection strategies, connects IT and Security teams, and reduces cognitive load for admins and users.

https://play.vidyard.com/WgUpqDPrj983PLmCvmVG8H

Automated Decoys

To shield business data and systems from malicious intent and activity, ThreatWise™ blankets tripwires across on-prem, multi-cloud, and SaaS instances. Off-the-shelf, preconfigured decoys or threat sensors that replicate real network assets (such as critical workloads, IT/OT assets, etc…) rapidly cover surface areas and spot threats along the path to your data. This includes the critical moments of recon, discovery, and lateral movement – critical moments where detection provides material impact on containing a breach. From the start of an attack, data protection stakeholders can foresee malicious activity traversing environments and targeting data. ThreatWise can even coat backup infrastructure themselves, hiding these environments from threats directly aiming to neutralize backup and recovery utilities. These preconfigured decoys include baked-in recommendations, helping automate the configuration process and offering user setting recommendations and templates. This removes any expertise needed for administrators to set up decoys, offering high-fidelity fake assets that look (and behave) like real assets at the flick of a switch. 

Automated Configuration

Unlike honeypot technology, ThreatWise™ employs a lightweight and highly scalable architecture. This enables users to quickly blanket environments with hundreds or thousands of fake assets to rapidly harden data estates, mask data, and muddle bad actor attempts. But how do I know what preconfigured decoys to use for my unique environment? The ThreatWise™ Advisor intelligently connects backup environments and decoys to reduce cognitive load for users. By assessing data that’s actively being protected within Commvault backup environments, ThreatWise™ Advisor logically recommends decoy types (and their placement) to further safeguard critical workloads. By connecting the dots between backups and cyber deception users can intelligently blend decoys into the existing environments without any deception or security expertise to optimize early warning detection and lead threat actors down a rabbit hole, away from their targets (your data).

Automated Alerts

When it comes to cyber events, IT teams must seamlessly integrate with their Security counterparts. Minutes matter and visibility, telemetry, and coordination are paramount for proper and effective response. Through seamless integration with existing security stacks, ThreatWise™ automatically circulates urgent event data to key stakeholders and security teams without human intervention. And because decoys are only visible to bad actors, notifications are clear and precise, eliminating false positives. This automation amplifies Commvault’s threat detection capabilities by removing silos and prioritizing data itself, connecting IT and Security teams to streamline operations without burden. This enables organizations of every size to flag latent threats earlier and respond faster. The result? Improved observability and accelerated response to minimize impact and mitigate loss— for less risk, less recoveries, less downtime.

Weitere Informationen zu Threatwise und unseren neuen Advisor-Funktionen finden Sie auf der folgendenSeiteoder in diesemOn-Demand-Webinar zum Thema „Threatwise: Frühwarnung, Datenschutz und deren Rolle bei der Cyber-Reaktion.

References

1.WatchTower, SIEMs are Great, But They’re Also a Pain, 2022.– 2.IBM und Ponemon Institute, „Kosten einer Datenpanne 2022“, Juli 2022.– 3. TechTarget Inc., „Von Commvault in Auftrag gegebene ESG-Studie“, September 2022

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

I can’t imagine a better way to head into our new, upcoming partner program year than to take some time to recognize and thank the Americas partners that are at the heart of everything we do at Commvault.

Our ecosystem is full of exceptional partners who regularly go beyond in delivering services and solutions that make real world differences in solving some of the biggest challenges in IT like securing, protecting, defending, and recovering data and applications. Earlier today at our invitation-only Partner Summit, we had the opportunity to take it one step further with the unveiling of Commvault’s inaugural 2023 Americas Partners of the Year awards.

The awards presented at this event celebrate the accomplishments of partners who have invested their time and trust into Commvault’s Partner Advantage Program and its ability to provide reliable, innovative, and secure data protection solutions that protect their customers’ business critical data.

The top prize and bragging rights for the overall award for Americas Partner of the Year for 2023 goes to CDW, which saw a huge demand for SaaS solutions this past year and an even bigger acceleration of customer adoption of Commvault’s SaaS technologies.

Marking another win for CDW, CDW Canada was named Canada Partner of the Year for its impressive year-on-year growth, dedication to being a truly collaborative partner, and ability to grow our long list of joint customers.

On the Commvault and Metallic SaaS front, Verinext saw outstanding growth, taking home the Managed Services Partner of the Year award for being the fastest growing Metallic SaaS managed service provider of 2023. And Insight was named winner in the SaaS market, too, taking home the award for Commvault SaaS Partner of the Year for its consistent growth and remarkable performance that outshined its competition, including the onboarding of 125+ new, joint customers.

The categories for this year’s awards also centered around geography and vertical focus. Congratulations are in order for:

  • Ahead, Technischer Partner des Jahres
  • Carahsoft, Vertriebspartner des Jahres
  • Data Pivot Technologies, Regionalpartner des Jahres für den Osten der USA
  • Eagle Technologies, Regionalpartner des Jahres für den Westen Amerikas
  • Hitachi Vantara, „Partner des Jahres“ in Lateinamerika
  • Kelyn Technologies, „Fed-Partner des Jahres“
  • SHI, SLED-Partner des Jahres

This year’s award winners have adopted best practices for protecting customer data and security while providing valuable feedback on continuously enhancing the Commvault platform. This recognition serves as a testament to these partners’ hard work and dedication in providing excellent services with secure SaaS solutions through Commvault’s Partner Advantage Program.

Commvault ist stolz darauf, diejenigen zu würdigen, die in unserer Region Amerika die Erwartungen übertroffen haben. Diese herausragenden Partner verkörpern, was es bedeutet, Teil eines innovativen Teams zu sein, das sich dafür einsetzt, Kunden beim Schutz ihrer Daten zu unterstützen und dabei höchste Standards für die Qualität der Dienstleistungen einzuhalten. Wir freuen uns darauf, unsere Mission gemeinsam mit unseren geschätzten Partnern fortzusetzen, während wir in unserem Bereich nach Spitzenleistungen streben.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Hier bei Commvault feiern wir unsere vielfältige Vaulter-Community und würdigen die Geschichte derer, die vor uns da waren.

This Monday is Juneteenth, a day which honors the emancipation of enslaved African Americans in the United States. We’re proud to observe the Juneteenth holiday on Monday, June 19, to commemorate history and celebrate African American culture.

Auch wenn der Juneteenth in den Vereinigten Staaten gefeiert wird, sind unsere Bemühungen, Bewusstsein zu schaffen und Gespräche über Themen zu führen, die uns am Herzen liegen, nach wie vor ein wesentlicher Bestandteil unserer globalen Kultur und unserer Grundwerte.

Im vergangenen Februar nahm ich gemeinsam mit Vorstandsmitglied Shane Sanders an einer Podiumsdiskussion im Rahmen des Webinars„Courageous Conversation“ webinar panel hosted by our Diversity, Equity, and Inclusion (DEI) team and Multi-Culture Employee Resource Group (ERG) to celebrate Black History Month. During our conversation, he shared his perspectives on how the theme of “equity in action” has impacted him as a Black man and the social cost of not embracing diversity and inclusion in the workplace.

Bei Commvault setzen wir uns dafür ein, unsere Bemühungen im Bereich DEI und Zugehörigkeit in Zusammenarbeit mit unseren großartigen ERGs weiter voranzutreiben, um Möglichkeiten zu schaffen, das Bewusstsein zu schärfen, offene Gespräche zu führen und zum Nachdenken anzuregen.

Ich möchte euch dazu ermutigen, euch heute einen Moment Zeit zu nehmen, um nachzudenken, zuzuhören und euch inspirieren zu lassen!

Um mehr über unsere DEI-Maßnahmen bei Commvault zu erfahren,klicken Sie hier.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

In der Welt von Big Data suchen Unternehmen ständig nach Möglichkeiten, riesige Informationsmengen zu speichern, zu verarbeiten und zu analysieren. Zwei gängige Lösungen für den Umgang mit Big Data sind Data Lakes und Data Warehouses. Auch wenn sie auf den ersten Blick ähnlich erscheinen mögen, dienen diese beiden Paradigmen der Datenspeicherung unterschiedlichen Zwecken und weisen unterschiedliche Merkmale auf.

Was sind Data Lakes und Data Warehouses?

Data Lakes

Ein Data Lake ist ein großer Datenspeicher, in dem rohe, unverarbeitete Daten in ihrem nativen Format gespeichert werden können. Data Lakes können strukturierte, semistrukturierte und unstrukturierte Daten speichern, was sie äußerst vielseitig macht. Sie sind auf hohe Skalierbarkeit ausgelegt und können so dem exponentiellen Datenwachstum gerecht werden. Data Lakes ermöglichen die Datenerfassung in Echtzeit und eignen sich ideal für Unternehmen, die große Mengen unterschiedlicher Datentypen schnell speichern und analysieren müssen.

Data Warehouses

Ein Data Warehouse hingegen ist ein strukturiertes Repository, das für die Speicherung, Verarbeitung und Analyse strukturierter Daten konzipiert ist. Data Warehouses speichern Daten auf eine streng organisierte, schemabasierte Weise, was die Abfrage und die Gewinnung von Erkenntnissen erleichtert. In der Regel werden die Daten bereinigt, transformiert und aggregiert, bevor sie in ein Data Warehouse geladen werden. Diese Systeme werden in erster Linie für Business-Intelligence- und Analysezwecke eingesetzt und ermöglichen es Unternehmen, datengestützte Entscheidungen zu treffen.

Anwendungsbeispiele für Data Lakes und Data Warehouses

Data-Lake-Anwendungen
  • Sentiment Analysis: Data lakes can be used to store and analyze large volumes of unstructured data, such as social media posts and customer reviews. This data can then be processed using natural language processing and machine learning (ML) algorithms to determine customer sentiment towards a product or service.
  • IoT Data Processing: Data lakes are ideal for storing and processing massive amounts of data generated by IoT devices. The real-time ingestion capabilities of data lakes allow for the processing and analysis of streaming data, enabling organizations to monitor and optimize their IoT networks.
  • Data Storage for ML/AI Training: In the medical and biotech fields, data lakes can be used to store data from diverse sources, such as genetic sequences, patient records, and clinical trial results. Machine learning algorithms can be applied to this unstructured data to identify patterns or correlations, aiding in uses from the development of personalized treatments to predicting disease outbreaks. Furthermore, algorithms can analyze real-time data from medical devices to monitor patient health and alert caregivers to any significant changes (See IoT above).
Data-Warehouse-Anwendungen
  • Sales Analytics: Data warehouses can be used to store and analyze sales data, allowing organizations to identify trends, track performance, and make data-driven decisions to improve sales strategies. The structured nature of data warehouses makes it easy to create sales reports, dashboards, and visualizations.
  • Customer Segmentation: By analyzing customer data stored in a data warehouse, organizations can segment their customer base and tailor marketing efforts to target specific demographics. Data warehouses can store structured customer data, such as purchase history and demographic information, enabling organizations to create detailed customer profiles.
Anwendungsbeispiel der Finanzaufsichtsbehörde (FINRA)

Ein hervorragendes Beispiel für ein Unternehmen, das AWS-Dienste zum Aufbau eines Data Lake nutzt, ist die FINRA. Die FINRA nutzt AWS, um täglich über 500 Milliarden Marktereignisse zu speichern und zu analysieren, wodurch sie Betrugsfälle und Marktmanipulationen aufdecken kann.

FINRA’s data lake, built on AWS, processes and stores vast amounts of diverse data types, including trade data, order data, and reference data. By using Amazon S3, FINRA can store and manage their data cost-effectively and securely, while Amazon EMR and AWS Glue enable them to process and analyze the data to identify potential violations.

You can learn more about this use case by reading the AWS-Fallstudie zur FINRA.

Schlussfolgerung

Data Lakes und Data Warehouses dienen unterschiedlichen Zwecken und eignen sich für verschiedene Arten der Datenspeicherung und -analyse. Für Unternehmen ist es unerlässlich, die Unterschiede zwischen diesen beiden Speicherparadigmen zu verstehen.

Once you’ve determined which path is right for you, be sure to build data resilience into your strategy. Keep an eye out for my next blog, which discusses advanced techniques for data resilience in RDS data warehouses and S3 data lakes.

Viel Spaß beim Lesen!

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

The digital landscape is evolving. Cyberthreats have become more sophisticated, data estates are growing, and IT resources are shrinking. Today’s organizations need a more proactive approach to protecting their data in an ever-changing threat landscape. And while traditional data protection solutions may play a pivotal role in recovering post-attack, they are reactionary, narrowly focused, and no longer sufficient.

Heutige Cyberbedrohungen sind darauf ausgelegt, Perimeter-Abwehrmaßnahmen unbemerkt zu umgehen und Schaden anzurichten, dem herkömmliche Lösungen für Backup and Recovery nichts entgegenzusetzen haben. Die Gefahr von Datenexfiltration, Datendiebstahl und Datenbeschädigung ist heute größer denn je und kann für Unternehmen verheerende Folgen haben, wenn sie nicht bekämpft wird.

Proaktiver, mehrstufiger Datenschutz

To address these cyber threats, organizations must look beyond conventional security tools and take steps to ensure data resiliency. This requires a proactive approach with layered protection, also known as defense in depth. It is the practice of implementing multiple tools and measures to protect against a wide range of threats. Each layer has a specific function, working in unison for multi-faceted protection for your environment. Commvault applies this very principle to data protection, uniquely delivering the right breadth of detection, security, and recovery capabilities to actively secure, defend, andrecover data broadly across production and backup environments.

Layered protection that actively defends data and its recoverability across the industry’s
broadest set of workloads

Secure

Eine robuste, auf dem Zero-Trust-Prinzip basierende, unveränderliche Architektur mit integrierten Sicherheitskontrollen zum Schutz von Daten, zur Verhinderung unerwünschter Zugriffe und Datenlecks sowie zur Gewährleistung der Compliance angesichts sich ständig weiterentwickelnder Cyberbedrohungen.

Defend

Patented early warning and in-depth monitoring to surface and neutralize zero-day and insider threats before they cause harm; containing breaches, limiting windows of exposure, and flagging malicious activity sooner to reduce recoveries.  

Recover

Eine proaktive und zuverlässige Wiederherstellbarkeit für On-Premise-, Cloud- und SaaS-Workloads reduziert nachweislich Ausfallzeiten, verhindert erneute Infektionen und verkürzt die Reaktionszeiten – für eine unübertroffene Geschäftskontinuität.

Innovativer Datenschutz mit neuen
Produkten und Dienstleistungen

We are pushing the boundaries of data protection in this modern world, and redefining how businesses of every size combat risk, minimize threats, secure entire data estates, and drive better business outcomes. We are setting a higher standard for customers’ security posture and delivering the best value in data protection. New products and features include:

  • Commvault Auto Recovery delivers complete cyber recovery and business continuity, both on-premises and in the cloud, providing secure, reliable, and near real-time cyber resiliency.
    • Recovery orchestration with one-click recovery of clean copies across workloads to production after validating and sanitizing recovery points.
    • Recovery validation to continuously validate backups, demonstrate recovery readiness, and reduce recovery testing complexities.
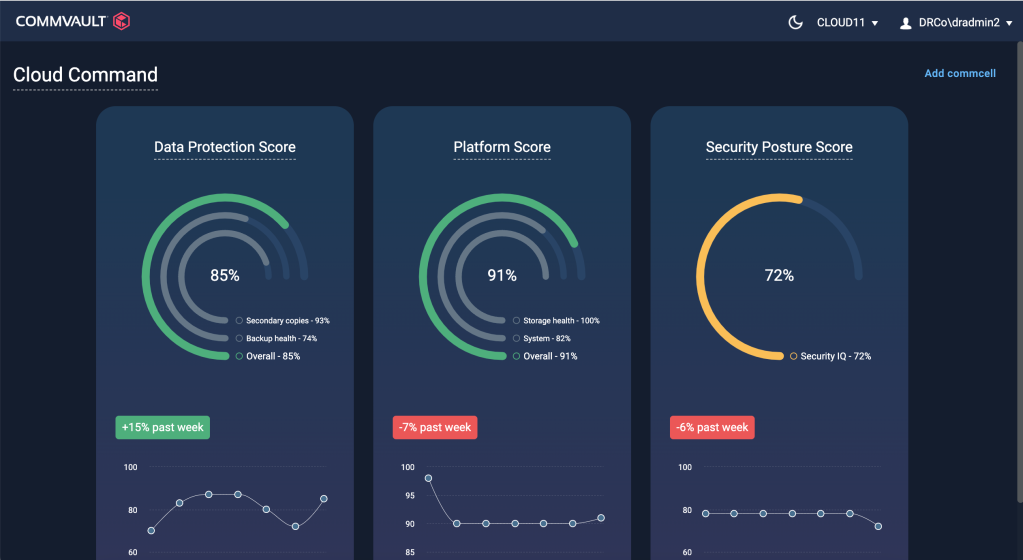
  • Commvault Cloud Command provides customers global visibility and actionable insights across SaaS, cloud, and on-premises through a SaaS-delivered unified platform. It enables standardization of security postures and simplifies data risk management to make optimal decisions for recovery readiness.
  • Commvault Risk Analysis identifies, categorizes, and classifies sensitive data such as personal, financial information, and intellectual property to prioritize security efforts and take action to reduce data exfiltration.
  • Commvault Threat Scan allows organizations to scan backup content to identify malware and files that have been encrypted, corrupted, or significantly changed to recover clean data and avoid file reinfection.
  • Security ecosystem expansion with bidirectional integrations with SIEM & SOAR platforms to meet compliance and improve your security posture by helping to align your response time through automatic actions.
  • Dynamic Credential Management integration with CyberArk to minimize the risk of stored credentials for workload protection on demand, allowing organizations to securely manage credentials within CyberArk rather than within the backup environment.
  • ThreatWise Advisor assesses backup environments and intelligently recommends decoy placement to further harden critical workloads and reduce the cognitive load for users.

Delivering a proactive and reliable recovery across the industry’s broadest workload coverage is proven to reduce downtime, thwart data loss, and accelerate response times. Businesses will benefit from our end-to-end insights and observability across the entire data protection lifecycle to anticipate risk, proactively minimize threats, control data (and its access), and drive more informed recovery outcomes.

Organizations of all sizes can feel confident that with the help of Commvault’s advanced data protection and recovery solutions, you can become the face of the next generation of data protection: Data, Secured. Data, Defended. Data, Recovered.

Um mehr zu erfahren, nutzen Sie unserenbuyer’s guideum Ihren aktuellen Stand in Bezug auf Cybersicherheit und Recovery-Fähigkeiten zu erfassen und zu ermitteln, wie Sie Ihren Plan für Readiness für Hybrid-, Cloud- oder SaaS-Umgebungen am besten optimieren können.

Watch our video on Data Protection Redefined as our mission is to secure, protect, and recover all your data with the world’s only unified data protection platform, which has the lowest TCO of any solution that even comes close.

Besuchen Sie unsereWebsite,um mehr zu erfahren.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

As a leader in data protection and security, Commvault values its partnerships with industry leaders, including Dell Technologies. Together, we are committed to designing, integrating, and delivering innovative solutions that meet the needs of customers. An open and extensible ecosystem is essential for the 100,000+ organizations that rely on Commvault solutions. Sanjay Mirchandani, Commvault’s CEO, explains it simply, “Integration needs to be built-in, not bolted on.” This philosophy provides that Commvault’s solutions work seamlessly with other technologies.

Die neue Integration zwischen Commvault und PowerProtect Data Domain bietet PowerProtect Data Domain-Kunden unmittelbare Vorteile durch:

  • Vereinfachte Konfiguration durch native API-basierte Integration
  • Verbesserte Sicherheitslage
  • Kunden können ihre bestehenden Datensicherungskonzepte nutzen, ohne neue Vollsicherungen erstellen zu müssen

Die Integration von Commvault und PowerProtect Data Domain ermöglicht eine vereinfachte, native API-basierte Anbindung. Dank dieser neuen Funktion können Kunden eine nahtlose Anbindung an bestehende PowerProtect Data Domain-Systeme herstellen, ohne dass das BoostFS-Plugin erforderlich ist. Dies verringert die Komplexität und verkürzt den Zeitaufwand, den Kunden benötigen, um mit der Sicherung ihrer Daten zu beginnen, erheblich.

Dank der neuen API-basierten Integrationen können Commvault-Kunden weiterhin ihre bestehenden Datensicherungsrichtlinien nutzen und müssen weder neue Vollsicherungen erstellen noch sich Gedanken über größere Sicherungssätze machen. Um diese neue Funktion zu aktivieren, muss lediglich im Commvault Command Center eine neue Speichereinheit für Data Domain Boost mit gültigen Anmeldedaten hinzugefügt werden.

Bisher hat Commvault PowerProtect Data Domain-Systeme als Speicherorte unterstützt, allerdings mussten diese als Common Internet File System (CIFS) oder Network File System (NFS) konfiguriert werden. Die neue Integration erhöht die Sicherheit bei Backups durch native Verschlüsselung und direkte Datenübertragungen, ohne dass ein CIFS- oder NFS-Dateisystem auf der Appliance eingebunden werden muss, wodurch die Angriffsfläche für Ransomware verringert wird.

Kunden, die Security Enhanced Linux (SELinux) nutzen, können die neuen Integrationen ebenfalls nativ nutzen. Dadurch entsteht eine sicherere Umgebung, in der Nutzer darauf vertrauen können, dass ihre Daten vor unbefugtem Zugriff oder Manipulation geschützt sind.

Having a reliable and secure backup solutions is key when it comes to protecting your business’ data from cyber threats. We’re thrilled to be joining the Data Domain Boost ecosystem and continue to look for other opportunities to enhance this integration even further in the future. For organizations looking for a powerful combination of tools to protect their data, Commvault & Dell Technologies have the complete solution you need!

Abonnieren Sie unbedingt unseren Blog, um regelmäßig auf dem Laufenden zu bleiben, denn wir werden in den kommenden Wochen die einzelnen Schritte des Integrationsprozesses ausführlich beschreiben. Melden Sie sich in unserenCommunity-Forenan, um über alle aktuellen Ankündigungen informiert zu bleiben, Fragen zu stellen und sich mit unserer lebendigen Online-Community auszutauschen.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Last week, we hosted our FY24 Global Company Kickoff – a time when our entire Vaulter community comes together to kick off the start of our fiscal year, hear from our leadership team on our strategy, and celebrate how we’re going to continue to win together!

Yet here’s the thing – winning together can only happen if we are able to support and show up for each other. We show up for each other in bigger moments, but also (just as importantly) in smaller moments each day. Here at Commvault we always have each other’s backs, and this type of culture defines who we are.

During our Kickoff event, we had the opportunity to hear from our Vaulters across the world on how they’ve felt supported at Commvault. These are the moments that matter!


As I listened to their perspective, I realized that all our efforts – from connecting, inspiring, caring, and delivering – are rooted in trust. The trust we’ve built with each other, the trust we’ve built through our relationships with our customers and partners, and the trust we’ve built through our outreach and support of the communities we live in.  

The foundation of trust is knowing that someone is going to show up for you. They have your back. So that’s why in FY24, we are recommitting to showing up for each other and continuing to strengthen the incredible foundation we’ve laid over the past 27 years.  

Here’s to an amazing FY24!

Check out your next opportunity by visiting our careers site here https://careers.commvault.com/us/en  

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

The threat from ransomware continues to be an unfortunate daily reality for technologists and security professionals. But, before we talk about “doom and gloom” we should recognize how far the industry has come. I would argue in the not too distant past, most companies were susceptible to what we would consider a relatively unsophisticated ransomware attack. Open Email -> Malware -> Network spread -> Ransomware ->

Dank der Fortschritte vor allem im Bereich der Endgeräte, der zunehmenden Verbreitung des „Work from Anywhere“-Konzepts und der Zero-Trust-Prinzipien hat die Branche erhebliche Fortschritte beim Schutz vor dieser Art von Angriffen erzielt.

Still, every week we see new articles on successful ransomware attacks. Many ransomware report trackers actually show an uptick in 2023. For instance Black Fog’s The State of Ransomware report shows an 8% uptick year over year. In addition, we see actors starting to target data storage outside of what traditionally is attacked, such as cloud storage and cloud databases.

“”If we truly have made advances against ransomware, why the increase in successful attacks?“”

Es kommt ganz auf die Prioritäten an

In analyzing these successful attacks, I’ve identified two primary categories where the system breaks down, allowing malicious actors to succeed in ransom style attacks.

  1. Lack of investment in an information security program. At the surface this seems obvious, and it is. You pay for what you get. Organizations with big-budget security teams suffer fewer ransomware attacks (with exception discussed in the next category).It’s easy to put on your curmudgeon hat and say “Well people just need to take this more seriously, and spend more on security!” The reality is most attacks we see in the news resulting from a lack of investment are against public services. Many of these organizations are simply not financially equipped to invest in the staff, time, and “cutting edge” technologies that can stop attacks. I’m going to end the thought there as it’s a different blog on politics, public policy, and unification. Public spending is not a topic that can be glazed over. But, the next category we as an industry can tackle more easily.
  2. We have on blinders. I understand this is a big statement, but when the topic is approached correctly, I often hear vigorous agreement that this is the case.
    Wenn ich sage, wir haben Scheuklappen auf, meine ich damit, dass wir das Risikomodell von Ransomware nicht vollständig durchleuchten. Wir konzentrieren uns zu sehr darauf, wie gängige Angriffe erfolgreich waren, um zu erkennen, wo Lücken in unseren Sicherheitsprogrammen bestehen. Wir legen den Schwerpunkt auf den Schutz von Endgeräten, Servern und herkömmlichen Datenspeichertechnologien (SAN, NAS usw.) und schaffen es dadurch, diese Ressourcen erfolgreich vor Angriffen zu schützen.

At the end of day, a threat actor who wishes to hold data for ransom only has to accomplish one task: deny availability of critical business data.

Many companies are more focused on controls for preventing attacks than implementing a holistic strategy to protect availability. In other words, don’t focus only on the ransomware attack, focus on a more general availability protection strategy inclusive of “data encryption for impact” (ATT&CK ID T1486) umfasst.

For example, many ransomware playbooks are focused on the idea that an actor could execute a binary payload and encrypt data. But the same effect could be achieved, given sufficient access, by simply swapping encryption keys on a critical database. The degree of difficulty for an attacker to pull this off varies wildly, but for many organizations it is a valid attack path. Don’t be too quick to point out that native DB backups, multi-versioning etc. can solve this. It’s not wrong by any means, but the reality is that due to performance impacts on large databases, these controls are often disabled and you may or may not be informed. In addition, management of these protection methods are often done from the same privileged credentials as normal admin activity, which are the credentials targeted by threat actors.

Okay…. but what does that mean…

All in all, it means you should revisit your ransomware playbook and consider making a top-level availability playbook if you don’t have one already (If you do, revisit it with a ransom lens). This should be a cross-functional effort. The security team should take a first pass, then sit down with data owners, infrastructure teams, and DR/BC teams to brainstorm on the most realistic protection and recovery methods. Many protection and recovery methods come with a performance trade off. Security can not ignore this reality, and IT can’t ignore security in favor of performance. There is no one size fits all answer.

Folgendes kann als grober Anhaltspunkt dafür dienen, worüber man bei diesen Bemühungen nachdenken sollte:

  1. Verstehen Sie alle wichtigen Geschäftsdatenspeicher, darunter:
    • “Private” managed data stores, NAS SAN
    • Mitarbeitergeräte
    • Databases (both on-prem, traditional cloud abstraction, and  as-a-service
    • Cloud-Speicher
  2. Erstellen Sie eine Liste von Taktiken, Techniken und Vorgehensweisen, die dazu genutzt werden können, die Verfügbarkeit Ihrer kritischen Datenspeicher zu beeinträchtigen, und ordnen Sie diese dem MITRE ATT&CK-Modell zu. (https://attack.mitre.org/tactics/TA0040/)
    • Beispiel 1: Massenverschlüsselung von Endgeräten
    • Beispiel 2: Diebstahl und Löschung kritischer Datenspeicher (Cloud und lokal)
  3. Ordnen Sie Taktiken den Datenquellen zu und stufen Sie diese nach ihrer Eintrittswahrscheinlichkeit ein.
    • Priorisierung anhand rechtlicher, operativer und strategischer Risiken
  4. Kontrollen und Prozesse bewerten
    • Ermitteln Sie nach Datenquelle, wo Möglichkeiten zur Einführung von Kontrollmaßnahmen zur Prävention, Erkennung, Reaktion und Recovery bestehen.
    • Lücken ermitteln
    • Neue Prozesse und Kontrollmaßnahmen schaffen
  5. Ergänzen Sie Ihren Leitfaden zur Reaktion auf Ransomware um Maßnahmen für alle Angriffstechniken, die auf Ihren Reaktions- und Recovery-Verfahren aus Schritt 4 basieren.
  6. Führen Sie gleichzeitig eine gemeinsame Table-Top-Übung (TTX) und eine DR-Übung durch.
    • This is a real challenge. Combining the two to perform a “open book” TTX with some random injects will really show how the teams work under the pressure of a real ransomware incident.

Zusammenfassung

Threat actors keep evolving to stay relevant and protect their income. Although we have gotten pretty good at protecting against traditional ransomware threats as an industry, every organization likely has a few blind spots. 

  • Ransomware attacks keep succeeding. 
  • As we get better at stopping traditional attacks, threat actors change their tactics to maintain success 
  • Threat actors are targeting data stores such as DBs and cloud storage 
  • Ergänzen Sie Ihr Reaktionshandbuch um Maßnahmen zur Erkennung, Prävention, Reaktion und Recovery für nicht-traditionelle Verfügbarkeits-Recovery.
  • Implementieren Sie unveränderliche und leistungsstarke Backup-Lösungen für Datenbanken und Cloud-Ressourcen.

Wie Clumio hilft

Clumio focuses on helping customers build resilience into their cloud applications and data. When it comes to ransomware, recovery is a key backstop to maintaining your business application availability. With Clumio’s backup options for databases like Amazon RDS, MS-SQL on EC2, and DynamoDB as well as Amazon S3, EC2, EBS, and Microsoft 365, you can create performant recovery strategies to make both infrastructure and security teams happy. 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Muss ich meine AWS-Umgebung sichern?

As businesses rely on AWS for their critical operations, it becomes imperative to protect the underlying data against threats and keep up to date with compliance and user requirements. While AWS is well-known for its infrastructure resilience, it is the customer’s responsibility to protect their data. AWS does provide many resources and services to help protect data, but for many organizations, going with a specialized vendor works out simpler and cheaper. A robust backup strategy can provide peace of mind by ensuring that the company’s data is safe and can restore in the event of data loss.

A cloud shaped drawer full of files being pulled out of a server stack. Represents the customer responsibility for backing up and protecting data within the resilient AWS infrastructure.

Welche AWS-Dienste sollte ich sichern?

While your application architecture may be dependent upon many services, the ones housing your critical data should in most cases, enterprises emphasize the protection of Amazon S3, used for storing objects and files, and Amazon EBS, used for storing data on virtual disks. Amazon RDS, a managed relational database service, and Amazon DynamoDB, which offers a NoSQL database solution, are the other critical services to backup. Each of these services may play a vital role in the operations of your business, and backing them up will ensure that you can recover from any data loss or corruption.

Was sind die bewährten Sicherheitsverfahren in AWS?

The most effective approach to backup AWS services depends on the application dependencies and its retention and recovery policies.

For business-critical services, it is important to backup data every few minutes, and keep them for as long as the most stringent compliance requirements. Amazon provides some ways to do this. For example, Amazon EBS snapshots can backup Amazon EBS volumes, while Amazon RDS snapshots can backup Amazon RDS databases. Also, some AWS services, such as Amazon S3 Glacier, support cross-region replication, which allows you to maintain a secondary copy of your data in another region. But, snapshotting or replicating each AWS service might not meet your applications recovery time and recovery point objectives. AWS also offers more granular backup tools such as AWS Backup and versioning, but the data from these services will live within your organization’s AWS account, putting it at risk in case there is a breach

A holistic way to do AWS backup is to identify a SaaS backup software vendor that backs up a large suite of AWS services, does so without the need for snapshot replication, identifies potential risks and events, scales no matter how much data you want to protect, and does so at a competitive price-point. Whichever approach you choose, it’s important to test your backups to ensure that they can be restored

Schützt AWS meine Daten?

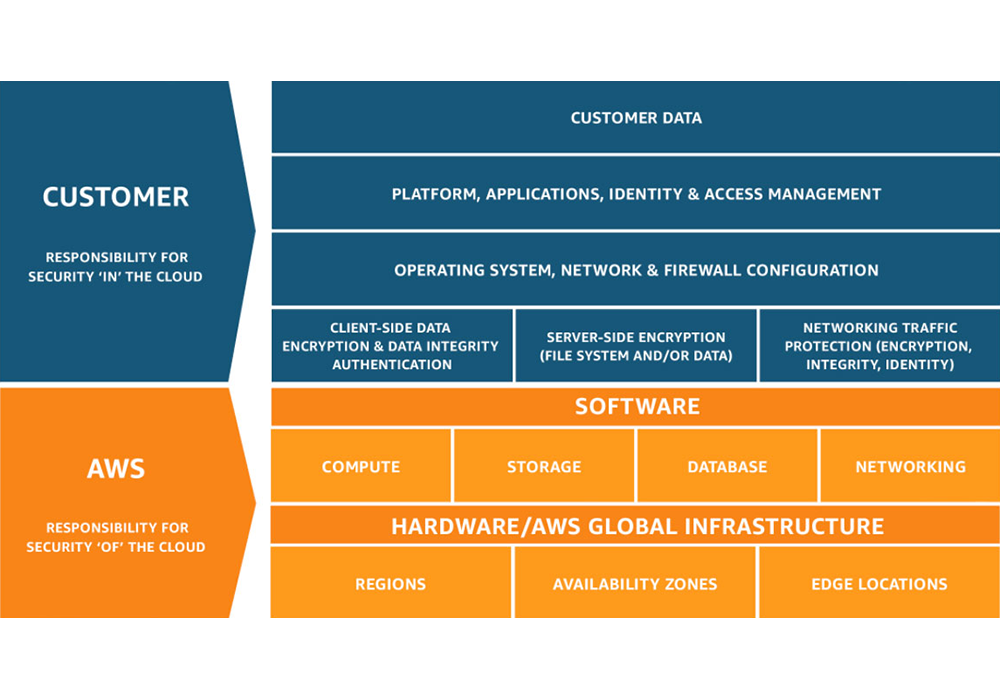
While AWS handles securing the underlying physical and network infrastructure that supports your workloads and data, You are responsible for securing the workloads and data you deploy in AWS. This is called the Shared Responsibility Model, and is a fundamental part of how AWS operates. Data security is the responsibility of the customer. This includes ensuring that sensitive data is encrypted and backed up, as well as implementing proper access controls to restrict who can access your data. Also, customers must also ensure that their applications and systems are patched against known vulnerabilities AWS provides a number of services and features to help customers secure their data, but it is the customer’s responsibility to implement these properly. AWS takes security very seriously and works hard to protect customer data. Yet, it is important to remember that customers have the primary responsibility in ensuring their data is secure.

Was ist das Modell der geteilten Verantwortung bei AWS?

Das Modell der geteilten Verantwortung bedeutet, dass AWS für die Sicherheit der Cloud verantwortlich ist und der Kunde für die Sicherheit innerhalb der Cloud. Einfach ausgedrückt bedeutet dies, dass die Verantwortung für die Daten beim Kunden liegt. Das Modell der geteilten Verantwortung gibt Kunden die Kontrolle über ihre eigenen Daten und ermöglicht es ihnen, eigene Schutzrichtlinien und Air-Gaps zu implementieren sowie die Tools zu nutzen, mit denen sie ihre Daten im Falle eines Datenverlusts bestmöglich wiederherstellen können. Das Modell der geteilten Verantwortung basiert auf drei Säulen:

  • Security of Data: The customer is responsible for securing their data. This includes encrypting data and backing it up regularly, as well as ensuring access control.
  • Security of Infrastructure: AWS is responsible for securing the underlying infrastructure that customers use to run their applications. This includes physical security, network security, and host hardening.
  • Operational Security: both AWS and the customer are responsible for operational security. This includes tasks such as patch management and log monitoring.

Was ist der Unterschied zwischen AWS-Snapshots und Backups?

Backups are a copy of data that can be used to restore lost or damaged files, while snapshots are a copy of the state of a system at a particular point in time. Both have their own advantages and disadvantages, and it’s important to understand the difference before deciding which to use. AWS snapshots are incremental, meaning that only changed blocks are copied since the last snapshot. This makes them very efficient in terms of storage space, but it also means that more work is required to restore a system from scratch using incremental snapshots. Backups, on the other hand, are full copies of data that can be quickly restored in the event of data loss. However, this also makes them more expensive to store and can result in a longer recovery time if a lot of data has been lost. There are multiple AWS partners – such as Clumio – that provide extreme efficiency in backups that provide all the benefits of backups at a price point that’s comparable to snapshots.

Was sind die wichtigsten Faktoren, die bei der Datensicherung in AWS zu beachten sind?

When it comes to backing up data in the cloud, there are a few key things to keep in mind. First, recovery time and recovery point are essential. How quickly do you need to be able to access your data in the event of an outage, and how much data can you afford to lose? Second, your choice of backup solution should be simple to use and understand; the last thing you want is a complex system that’s difficult to manage in a time of crisis. Third, price is always a factor. How much are you willing to spend on backing up your data? And if you want to build it yourself, can you afford the engineering costs and complexity associated with it? Keeping these factors in mind, you can ensure that your AWS S3 backup is as effective as possible.

Ist die Datensicherung bei AWS schwierig?

Backing up data is a nuanced process, and if building a backup solution on AWS, users must have a deep understanding of the platform in order to properly configure their backup plan. Additionally, because AWS offers so many different storage and computing options, it can be difficult to know which service is best for backing up data. For this reason, many businesses choose to use turnkey SaaS backup tools from AWS partners, such as Clumio. These tools provide an easy-to-use interface for configuring backup plans and can automate many of the complex tasks involved in data protection. Moreover, they provide an air gap against ransomware attacks, as well as extreme storage efficiency and scale. Backing up AWS services need not be complex, but the right solution depends on the application, expertise of the user, and the services being protected.

Wie kann ich AWS sichern?

AWS provides a first-party tool called AWS Backup that backs up many services such as DynamoDB, Amazon EBS, Amazon EC2, Amazon RDS, and Amazon S3. You can use AWS backup to protect your databases, storage volumes, and file systems. AWS backup uses incrementally updated snapshots to provide point-in-time recovery for your data. However, if you want to simplify your backup infrastructure to free up your engineers to focus on driving business value, you may want to consider using a turnkey third-party backup solution such as Clumio.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

We live in interesting times, don’t we? Data has reshaped business, how organizations operate, and what customers expect. It’s a hybrid cloud world, where companies have more data in more places, on more apps and different platforms than ever before. And AI is on the verge of changing everything in profound ways. 

All of which makes data the most critical asset you own, the heartbeat of your organization. In short, there’s nothing more important than ensuring its security and protection. 

Too bad the space is full of hype and me-too claims that all sound alike. To make smart decisions requires clarity. But some vendors seem more dedicated to throwing shade than grasping the dimensions of the problem. Trying to convince you that the only answer is a volume play—multiple solutions, more tools, more backup or a new partnership marketed heavily as solving a customer problem, but in reality, is only solving a gap in vendor capability or a workload coverage issue.

But are these claims really true? Or are they just relying on a lot of flashy buzzwords to make up for the shortcomings in their own offerings? It’s kind of insulting if you think about it—as a smart tech buyer, aren’t you going to see through this stuff?

Questions well worth asking. I did when I first joined Commvault. My take on marketing technology is simple: you find out what your product does better than your competitors and find a smart, compelling way to talk about it. You don’t lie. You don’t exaggerate. You explain.

Let’s start by explaining that Commvault protects the broadest range of workloads of any vendor. As the ultimate data protection for today’s hybrid cloud world, we cover on-premise, private and public cloud, SaaS, and almost anywhere your data lives.

1st and Only

Fully managed DPaaS to support multiple clouds.

1>6

syncreon saved $500K by consolidating six backup solutions into one.

So, when some new competitor starts labeling us as “legacy data protection”, you’re smart enough to know that really means they’re trying desperately to keep up with our multi-cloud SaaS Data Protection, cloud air-gap, and integrated threat deception technology. 

When they call our protection of a broad range of workloads  “complex”, you’re not about to confuse flexibility with complexity. Flexibility, good. Complexity, bad. Ironically, the same vendors doing this are also forcing customers to adopt and manage separate point solutions. And what does that bring with it (in addition to cost and risk)? Say it with me: complexity.

100% Protected

Commvault supports all types of workloads; it is literally universal. Metallic runs in the cloud, but Commvault has not forgotten the importance of protecting on-prem workloads.1

Now let’s talk about security. I’ve seen companies sell their products as the “only” or “best” Zero Trust security. Well, for one, Zero Trust is a comprehensive approach. Not some bolt on capability. In a hybrid world, data security only works, as it does in Commvault, when it’s built in, pervasive, has the capability to also defend beyond breaches, and guards backups, as well.

5 min vs. 24 hours

Commvault detects threats faster.

3x Lower

TCO in the Cloud than Rubrik and Cohesity.

Which brings me to my last point. A lot of what some competitors label as “unique” to them—immutability, zero trust, backup monitoring—are actually just table stakes in a robust data protection solution, like Commvault.

Verlassen Sie sich nicht nur auf unser Wort. Hören Sie sich an, was unsere Kunden zu sagen haben:

We were looking for an offering that could protect the many key platforms deployed across our environment, and Cohesity couldn’t check either of those boxes.

– Jeffrey Day, IT-Sicherheitsarchitekt beim Verkehrsministerium von Nevada


We hear this a lot actually; “To scale you need more boxes, more, more”.  But in data protection, bigger doesn’t mean better, and it certainly doesn’t mean smarter.  It adds more of the things you don’t need: cost, complexity and risk via a bigger cyberattack surface. 

With something as critical to the success of your business, there really isn’t room for fuzzy claims and fudged execution. A hybrid cloud world demands comprehensive data protection that gives you options (not complexity), delivers proactive security, active data defense, and rapid recovery through a single, gap-free platform. Without add-ins, bolt-ons, and upsells. It’s time to cut through the noise and deliver effective solutions, so you can focus on what really matters—running your business.

Besuchen Siewww.commvault.com/questionit

Sources:

1. ESG-Forschung (Von der Datensicherung zur Datenintelligenz, Januar 2022)

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

“We’re #1! We’re #1!”

When the dust settles on championships, that chant is heard in stadiums worldwide. High score wins, the trophy is held aloft (tossed, if you’re Tom Brady), and the celebration begins alongside Queen racking up more well-deserved royalties.

But how do you determine who’s at the top of the mountain in the data protection world? Ensuring the integrity of your crown jewels in the cloud or on-prem is not a game that ends after a preset period – it’s an ongoing battle that rages 24 x 7 and is fought by CISOs, IT Managers, Database Administrators…the list goes on. It’s complicated, requires adaptable strategy, dedication to the cause, and relentless ambition to best bad actors.

As a result, it’s always an interesting exercise to unpack claims of dominance in this market. Some are true (but come with asterisks), some are highly debatable, some are false, and others are flat-out hyperbole. Let’s look at how one vendor positions their claim of being the best.

Subjective vs. Objective…vs. the Real World

Right out of the gate, we need to understand that many cloud claims rely on two dimensions: subjective (open to opinion) and objective (factual). However, let’s not forget about what we call “real-world” claims – this is what directly impacts your business, and how you use the cloud to run it. Examples:

  • Objective claim: “81% of the Fortune 500”
    • Angenommen, dies trifft in gewisser Weise zu, so fehlt jedoch jeglicher Kontext, der diese Aussage stützt. Haben 81 % das Produkt ausprobiert? Haben sie das Produkt einmal gekauft? Nutzen sie es seit mehr als einem Jahr?
    • Is your company in the Fortune 500? If not, the message is “If it’s good enough for them, it’s good enough for you.” See? Now it’s become a subjective claim.
    • Verfügen Sie über die Ressourcen bzw. das Budget eines Fortune-500-Unternehmens? Wenn nicht, wie hilft Ihnen das?
  • Subjective claim: “We protect everything”
    • „Alles“ bedeutet jede einzelne Art von Daten, die es gibt, von jedem Anbieter. Das umfasst sicherlich jede Cloud-Workload.
    • In diesem Fall sichert der Anbieter, der diese Behauptung aufstellt, bestimmte Workloads für Azure-Datenbanken tatsächlich nicht.
    • Nutzen Sie die Azure-Cloud? Wenn ja, wie stehen Sie zu dieser Aussage?

Which brings us to the real-world aspect. We know that 80% of all enterprises have a hybrid cloud strategy1…and once you are in the cloud, you’re going to stay in the cloud. You may be multi-cloud, public cloud, or hybrid cloud, but make no mistake, you’re invested. So why do broad claims like the above exist?

Denn in der realen Welt ist es schwer, Gewissheit zu erlangen.

Und weil es einfacher ist, zu vertrauen, als zu überprüfen.

14M M365 users? Ever wonder how many of those are using the free version of the app? It’s a significant number – which means you’re not being given the complete picture.

Fact: peace of mind means different things to different businesses. Different clouds, different workloads, different skill sets, different levels of security in place. They all come together to form your personal cloud strategy. And at the end of the day, what matters is that your data can be restored to its pre-attack/incident state and is 100% intact, regardless of where it resides or what workload(s) are being made whole again.

That’s the claim that matters. That’s the real-world cloud claim. Full stop.

At Commvault, we make assertions about how we stack up very, very seriously. Any claims we make are objective and rooted in 3rd-party validation, and of course, fact. There’s no better way to be transparent, and we’ve been doing so for over 26 years. Our customers and partners rely on that to defend, secure, and protect their data, day in and day out.

Treffen Sie Entscheidungen, die sich auf Ihr Unternehmen auswirken, auf der Grundlage von Behauptungen, die im besten Fall nicht auf Sie zutreffen und im schlimmsten Fall völlig falsch sind?

“Just the Facts, Ma’am”

The concept of Data Protection has evolved. It’s no longer sufficient to just provide backup – data protection solutions/services/platforms must now include features such as data security, analytics/insights, governance, compliance, data management, data mobility/migration, transformation, and of course, recovery. Many less capable vendors have been forced to approach this via acquisition partnerships/OEM, or via other more fragmented approaches with multiple tools.


Commvault ist anders.

There is an extensive list of achievements in the data protection space pioneered by us as the first to deliver on them – and in some instances, still the only vendor to do so. Consider the following:

  • First to launch fully managed DPaaS offering supporting multiple clouds (Metallic®).
  • First to launch cloud air-gapping (Metallic® Recovery Reserve™).
  • Erste Lösung für die Datensicherung in Unternehmen, die Container und Kubernetes unterstützt (2017).
  • Der einzige Anbieter, der zahlreiche Cloud-native Anwendungen (AuroraDB, CosmosDB, OCI und weitere) unterstützt, die andere Anbieter nicht schützen können.
  • Der einzige Anbieter, der den Schutz aller Azure-PaaS-Datenbanken unterstützt.
Being #1 Means Cloud Security is Built-In–Not Bolted On

Many vendors overplay their support for immutability (either directly or via third parties) as sufficient data security, but if you don’t know you even have corrupted data, how can you truly be “protected”?

Immutability is table stakes, but it’s not enough. Without air-gapping, detection, and other layers of data security you end up with ransomware-infected immutable files. You need more than just immutability as part of your solution – things like:

  • Metallic® ThreatWiseTM cyber deception and early warning solution.
  • Unterstützung für Air-Gapping – einschließlich Band.
  • Granular “clean” recovery, ensuring ONLY the bad data is “purged,” but the good data is still available.
  • Keine zusätzlichen Tools oder Unterstützung durch Drittanbieter erforderlich.
  • Cloud-Erweiterung für Unveränderlichkeit ohne den Einsatz von Appliances.
  • No need to LOCK the entire backup copy when corrupted data is found – which means that good data is getting thrown out with the bad, which equals data loss.
Being #1 Means Reducing TCO (or “Show me the money”)

Finally, let’s cut through the marketecture and jargon/rhetoric around TCO used by some vendors to lay claim to that #1 positioning. Today, TCO is a close second to security in terms of what you need. So, while saying things like “1.1M average cost savings” is (again) highly subjective depending on your company size, consider what real TCO looks like in any given situation:

  • Echtes SaaS bedeutet, dass keinerlei Infrastruktur verwaltet werden muss; eine Steuerungsebene in der Cloud ist noch kein SaaS.
  • Durch Deduplizierung lassen sich Gebühren für den Dateneingang und -ausgang einsparen.
  • Komprimierung bedeutet weniger Datenverkehr und höhere Einsparungen.
  • Die Möglichkeit, Ihre Lösung je nach Bedarf sowohl nach oben als auch nach unten zu skalieren – und nicht nur nach oben, wenn die Nachfrage sinkt oder sich die Arbeitslasten auf andere Clouds oder Plattformen verlagern.
Being #1 Means Complementing Cloud Native Capabilities

The cloud offers data resilience, which is important to ensure that your data and applications are always available, but does not protect you from data corruption, malware, or other related incidents – you end up with highly resilient “bad data.” Data protection is critical for cloud native and SaaS-based applications.

And because being able to protect any application is the name of the data protection game, how does one claim to be #1 in modern data protection without that? Commvault offers best-in-class data protection for traditional, hybrid, cloud, modern, and containerized applications as part of a unified service and console – eliminating the need for multiple, overlapping tools. Offering the broadest spectrum of workload coverage in the industry, Commvault drives “hard cost savings for Microsoft customers” according to Und da es beim Datenschutz vor allem darauf ankommt, jede beliebige Anwendung schützen zu können – wie kann man da ohne diese Fähigkeit behaupten, die Nummer 1 im modernen Datenschutz zu sein? Commvault bietet erstklassigen Datenschutz für traditionelle, hybride, Cloud-, moderne und containerisierte Anwendungen als Teil eines einheitlichen Dienstes und einer einheitlichen Konsole – wodurch der Bedarf an mehreren, sich überschneidenden Tools entfällt. Mit dem branchenweit breitesten Spektrum an abgedeckten Workloads sorgt Commvault laut. And theGartner® Magic Quadrant™? A leader the last 11 years in a row. Add to that leader status for the most recentGigaOm Radar Hybrid Cloud Data Protection report, and you know you’re in good hands.

Wrapping up, we’re not here to debate our position on the data protection leaderboard, although we do think our case for sitting at the top is strong. The way our 100,000+ customers see it, with over 3.8EB having been moved to the cloud, Commvault is the global leader in hybrid cloud data protection. We’ve been doing this for 26 years, nearly all of it with our foundational partner Microsoft.

The TL; DR? Ask your vendor if your data is being secured, defended, and recovered with 100% efficiency, for the right workloads, in the right places, by the right vendor – both now AND in the future. You might be surprised by what you find.

Testen Sie Commvault noch heute unterhttps://www.commvault.com/request-demo

Reference
: „State of the Cloud“-Bericht, Flexera, 2022

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Here at Commvault, our four values – we connect, we inspire, we care, we deliver – are foundational to everything we do.

Diese Woche haben wir unsere vierteljährliche interne „Global Town Hall“-Veranstaltung abgehalten und die „Living Our Values Awards“ unseres CEO verliehen. Dieses vierteljährliche Auszeichnungsprogramm hilft uns dabei, unsere „Vaulters“ weltweit für ihre großartige Arbeit zu würdigen und zu feiern, da sie unsere Werte jeden Tag vorleben.

I’m so proud to announce our FY23 Q4 CEO Living Our Values Award winners:

Stephanie​ Cunliffe
Leiterin | Analyse von Geschäftssystemen

Jennifer​ Kelly
Verwaltungsassistentin/Rezeptionistin

Leah​ Flynne
Leiterin | Compliance

David ​Stupar
Leiter | Kundenerfolg

Metallic Site​ Reliability Team

Justin Avignone​
Manager | SRE – Anwendung

Karunakar Bojjireddy​
Leiter | Cloud-Betrieb SaaS

Peter Coviello​
Leitender Direktor | Anwendungsentwicklung, Technik

Prashant Jayram
Leitender Architekt für Datenlösungen

Alex Piccolo
Datenwissenschaftler 2

Reddi Prasad​
SRO-Ingenieur

Firoz Sahib​
SRE-Manager

Siddhant Saini​
Direktor | SaaS-Betrieb

Shankaar Thiagarajan​
leitender Architekt


All diese Gewinner sind ein inspirierendes Vorbild und verkörpern, was es wirklich bedeutet, ein „Vaulter“ zu sein!

To learn more about what it’s like to work at Commvault, check out our Karriereseite.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements