Skip to content

En el último episodio del podcast «The Resilience Rundown», el presentador Thomas Bryant entrevista a Vidya Shankaran, directora técnica de tecnologías emergentes en Commvault, para adentrarse en el mundo de la inteligencia artificial (IA). Thomas y Vidya hablan sobre el potencial de la IA en diversos sectores, los retos que plantea y su impacto en la protección de datos y la ciberresiliencia.

El entusiasmo y el potencial de la IA

AI has tremendous potential in today’s world, ranging from healthcare to security, according to Vidya. AI has become an integral part of our lives, with applications like Siri on our phones. From an enterprise perspective, there is still untapped potential due to concerns around security. However, the excitement surrounding AI and its ability to enhance productivity and innovation is palpable.

https://play.vidyard.com/2Tdz9MAD1hu1an1fqyK7Jg

Subscribe: Apple Podcasts | Spotify | YouTube

El lado oscuro de la IA

While AI offers numerous benefits, there is also a dark side that needs to be acknowledged. Vidya emphasizes the importance of data quality in AI models, as “garbage in, garbage out.” If the data fed to AI is flawed or biased, it can lead to inaccurate results. Additionally, there are concerns about the echo chamber effect and the challenge of striking the right balance between innovation and data security.

El concepto de los cortafuegos de datos

Una solución interesante para abordar los retos de la IA es el concepto de «cortafuegos de datos». Vidya explica que los cortafuegos de datos se centran en configurar avisos del sistema para impedir que los usuarios accedan a información confidencial. Estos cortafuegos pretenden abarcar todas las permutaciones y combinaciones posibles para garantizar la seguridad de los datos. Vidya ofrece ejemplos de cómo eludir los avisos del sistema y hace hincapié en la necesidad de mejorar continuamente el diseño y la configuración de las reglas de los cortafuegos.

La IA causal y su impacto en la protección de datos

Vidya analiza el papel de la IA en la protección de datos y la ciberresiliencia. Commvault lleva utilizando la IA predictiva desde 2016, y el siguiente paso es integrarla con capacidades generales de IA. La evolución hacia la IA causal permite comprender mejor los problemas específicos de cada cliente y realizar un análisis de las causas raíz. Esto permite una resolución de problemas personalizada y en tiempo real, lo que reduce el tiempo de inactividad y mejora la eficiencia operativa.

La IA trae consigo tanto promesas como riesgos

Vidya and Thomas’ conversation provides valuable insights into the exciting and concerning aspects of AI in the enterprise space, highlighting the potential of AI in various industries while acknowledging the challenges. The concept of data firewalls and the evolution toward causal AI offer promising solutions for data protection and cyber resilience. As AI continues to evolve, it is crucial for businesses to strike the right balance between innovation and security to harness its full potential.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

As we continue to celebrate Women’s History Month, I’m honored to take a moment to share my experience as a woman in the technology industry with a passion for inclusion and mentorship.

As Head of Regional Marketing for Switzerland, Austria, SEE, Middle East and Africa, I’ve had the pleasure of being part of Commvault during a pivotal time in its history. In November, we launched our new approach to cyber resilience, and ever since then, we’ve been hard at work with our eventos «SHIFT Roadshow» and to give our customers an unfair advantage for resilience in the face of ransomware and other advanced threats in today’s hybrid world.

Aunqueel sector tecnológico es un ámbito dominado por los hombres, especially in the Middle East, I’m fortunate to be part of an incredible team here at Commvault, where everyone is valued, and our unique perspectives are celebrated. I appreciate Commvault’s commitment to a Diversity and Inclusion culture, the collaborative and supportive work environment, and the focus on employee development. These aspects create a workplace where every individual feels valued and encouraged to thrive.

Last month, I was thrilled to to win Commvault’s el premio «CEO Living Our Values», and that I had been nominated for this honor by my team. This award is an incredible validation of my hard work, dedication, and contributions aligned with Commvault’s values – Connect, Inspire, Care, Deliver – that are the guiding principles shaping my professional journey. It serves as a powerful motivation, reinforcing my commitment to upholding these values and acknowledging my achievements in the most meaningful way.

Entre los momentos de los que me siento más orgulloso se encuentran los proyectos exitosos en los que he trabajado, el increíble espíritu de equipo y el reciente logro de recibir el premio «CEO Living Our Values Award». Atribuyo mi éxito al trabajo en equipo, la colaboración, el apoyo a los demás y la comunicación eficaz. El esfuerzo colectivo de mi equipo desempeñó un papel fundamental a la hora de alcanzar los objetivos comunes y contribuir a los valores que Commvault tanto aprecia.

My dedication to Commvault is fueled by the human values, compassionate interactions, collective teamwork, and consistent appreciation demonstrated within the organization. I’m excited about the new era and the new Commvault, eagerly anticipating the fresh opportunities and innovations it will bring, especially with the recent launch of Commvault Cloud, powered by Metallic AI.

This year’s International Women’s Day theme is #InspireInclusion, which is very special to me. Throughout my career, I’ve made it my mission to support and empower women in this industry to believe in themselves. Mentorship is a key aspect of how I’ve worked to empower other women to believe in themselves. A supportive, genuine, connection with a team member can go a long way.

Invertir constantemente en habilidades y conocimientos, crear una sólida red profesional, mantener un equilibrio saludable entre la vida laboral y personal, y aceptar los retos y los cambios son los consejos que me han guiado a lo largo de mi carrera. ¡Transmito estos mismos consejos a las nuevas generaciones con la esperanza de influir positivamente en ellas!

For any woman who is just starting her career in technology, my advice to you is to remember the power of confidence. Take a seat at the table instead of waiting for an invitation! I know that sometimes being the only woman in the room can initially feel intimidating, but remember, YOU have a unique perspective that deserves to be heard. Be confident and authentic in who you are and know that you bring immense value in driving innovation. Setting goals and following one’s passion are essential ingredients for success.

Para obtener más información sobre cómo trabajar en Commvault,haz clic aquí.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Con motivo del Día Mundial del Síndrome de Down, quería compartir mi experiencia personal con mi hijo Jace.

Jace vino al mundo en octubre de 2014 y, 12 horas después de su nacimiento, nos comunicaron que padecía síndrome de Down. Jace pasó los primeros 10 días de su vida en la Unidad de Cuidados Intensivos Neonatales y, durante ese tiempo, tuvimos que adaptarnos rápidamente y aceptar su diagnóstico.

I have to admit, I really struggled with Jace’s diagnosis in the beginning. I worried a lot about the future and the fear of the unknown – which I now know are normal thoughts that many parents have when they find out their child has a disability.

Jump forward 9 years, and Jace is rocking it! He is in Grade 4 and an active participant in his class.  Outside of school, he loves horseback riding and participating in sports. He currently plays hockey every weekend with a great organization, SuperHEROS. They provide the ability to play hockey to kids with disabilities who don’t normally have the chance. He also plays in a similar baseball league in the summer.

Commvault has been incredibly supportive over the years, giving me the flexibility I need to help Jace. And joining our CapAbilities Employee Resource Group (ERG) has been an amazing way for me to share my story with my fellow Vaulters and raise awareness. Our CapAbilities ERG’s mission is to create a safe and empathetic space where Vaulters with disabilities, caregivers, and allies can openly and honestly have discussions and drive change together.

This past November, Commvault once again sponsored a table at PREP’s annual fundraiser, Let’s Talk Hockey, a night with members of the Calgary Flames NHL team. I attended the event with some of my team members and customers, too – all proceeds went directly to the PREP foundation. Jace would not be in the place he is today without the support he receives from PREP.

On World Down Syndrome Day, I’m celebrating by wearing my funky or mismatched socks to recognize how Jace’s extra chromosome makes him extra perfect in our eyes. My goal is to continue to spread awareness and provide opportunities for Jace, and other children like him, to live their best lives and make a difference in this world. Every life deserves to be celebrated.  

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

En Commvault, el bienestar sigue siendo una prioridad fundamental para toda nuestra comunidad global de Vaulter.Como ya comenté a principios de este año, cuidar de nuestro bienestar nos permite dar lo mejor de nosotros mismos tanto en casa como en el trabajo.

Over the years, we’ve continued to evolve our wellness offerings to best support our Vaulters and their families with programs they need for life’s most important moments and stages. Our priority has been, and always will be, to provide inclusive support for our employees and their families. Having this type of support and the right wellness resources allows our Vaulters to thrive.

So, in honor of Women’s History Month and International Women’s Day, I want to talk about how we’re supporting the women of Commvault with specific wellness offerings this month and beyond!

On International Women’s Day, our Women in Technology Employee Resource Group hosted a women’s wellness event in our Australia office, which was also available to all our Vaulters for virtual participation. The event featured guest speaker Annerie Feldman, a Sydney-based health and wellness coach. Annerie spoke about the challenges women often face that impact their wellness, and how women can overcome these obstacles to feel empowered and confident through prioritizing self-care and gaining control of one’s wellness.

Additionally, our India team has organized a breast cancer detection and awareness initiative for our female Vaulters this month. In partnership with Enable India, a non-profit organization working for economic independence and dignity of persons with disability, our Vaulters will have the opportunity to learn more about the importance of breast cancer detection and make connections with Enable India’s knowledgeable female representatives who are visually impaired.

Además de nuestros eventos conmemorativos y de sensibilización del mes de marzo, también ofrecemos una variedad de prestaciones de bienestar para nuestros empleados de Vault en EE. UU., como planificación familiar, prestaciones de fertilidad, cuidados a familiares y mucho más. Nuestro socio para la formación de familias, Maven, está a disposición de todos nuestros empleados de Vault en EE. UU. Maven proporciona acceso a atención médica de primera calidad en materia de fertilidad, maternidad, pediatría y menopausia, y ofrece acceso las 24 horas del día a profesionales especializados en la formación de una familia, un equipo dedicado de asesores de atención sanitaria y una amplia biblioteca de recursos educativos clínicamente validados. Nuestra colaboración con Maven también nos permite ofrecer posibilidades de reembolso a los miembros de Vault que forman una familia mediante la adopción o un acuerdo de gestación subrogada.

Además de Maven, ofrecemos asistencia a través del programa «Fertility Solutions» en colaboración con nuestro socio médico en EE. UU., UnitedHealthcare. Este servicio proporciona orientación y apoyo comprensivo para ayudar a afrontar decisiones complejas sobre el tratamiento, reducir el estrés económico y emocional, y alcanzar los objetivos de embarazo con unos costes médicos más bajos.

We know our Vaulters and their families can face challenges when navigating child, elder, and pet care, so we’ve also partnered with Bright Horizons to help our U.S. Vaulters manage their day-to-day life efficiently and safely by finding care when they need it, both at high-quality centers and in-home.

Nos enorgullece fomentar un entorno de trabajo en el que todos nuestros equipos sientan que su bienestar es una prioridad. Ofrecer recursos específicos para nuestras empleadas de Vault es fundamental para fomentar nuestra cultura inclusiva y nuestra plantilla diversa. Al fin y al cabo, cuidar de nuestro bienestar es fundamental para poder dar lo mejor de nosotros mismos, tanto para nosotros como para los demás.

Haz clic aquí to learn more about what it’s like to work at Commvault.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Cloud computing has become essential for businesses of all sizes, offering scalability, flexibility and cost savings. However, managing cloud environments can be complex and chaotic, leading to increased costs, security risks and performance issues. In this blog post, we’ll explore the challenges of cloud computing and provide practical strategies to overcome them. Following these strategies can help you tame cloud chaos and optimize your cloud computing experience. And you’ll learn about Commvault® Cloudy cómo puede ayudarte a alcanzar el éxito en la nube.

El caos de la computación en la nube

El panorama de la computación en la nube está en constante evolución, y cada vez surgen nuevos servicios y proveedores. Esto puede suponer una gran ventaja para las empresas, ya que les brinda acceso a una gama más amplia de opciones y les permite ampliar sus operaciones de forma rápida y sencilla. Sin embargo, esta complejidad también puede generar caos, ya que las empresas se enfrentan a dificultades a la hora de gestionar múltiples entornos en la nube y garantizar que sus datos y aplicaciones estén seguros y cumplan con la normativa.

Uno de los mayores retos de la computación en la nube es el riesgo de fugas de datos e incidentes de seguridad. Los proveedores de servicios en la nube son responsables de garantizar la seguridad de su infraestructura, pero las empresas también deben tomar medidas para proteger sus propios datos y aplicaciones. Esto incluye la implementación de controles de acceso rigurosos, el cifrado de datos y la vigilancia de actividades sospechosas.

Otro reto es la posibilidad de que surjan problemas de rendimiento. Los proveedores de servicios en la nube ofrecen distintos niveles de servicio, y las empresas deben elegir el nivel adecuado a sus necesidades. Este puede ser un proceso complejo, ya que hay que tener en cuenta factores como el ancho de banda, la latencia y la capacidad de almacenamiento.

Por último, está la inversión en sí misma. Las empresas deben analizar detenidamente los costes de los servicios en la nube, incluyendo la infraestructura, el software y la asistencia técnica. También deben tener en cuenta el coste de migrar sus datos y aplicaciones a la nube.

A pesar de estos retos, la computación en la nube ofrece una serie de ventajas significativas. Entre ellas se incluyen una mayor agilidad, escalabilidad y ahorro de costes. Al comprender los retos que plantea la computación en la nube y adoptar medidas para mitigarlos, las empresas pueden aprovechar el potencial de la nube para alcanzar sus objetivos.

El ransomware y la nube

Ransomware is a type of malware that encrypts files on a victim’s computer and then demands a ransom payment in exchange for decrypting the files. Ransomware attacks can be devastating for businesses, as they can lead to lost data, downtime and financial losses.

Ransomware attacks have become increasingly prevalent in recent years, and cloud environments aren’t immune to this threat. In fact, cloud environments can be particularly vulnerable to ransomware attacks, as they often contain large amounts of sensitive data and are accessible from anywhere in the world. It has been reported that 82% of breaches involve data stored in the cloud – public, private or multiple environments.[1]

Data fragmentation is another key reason ransomware can be hard to defend against – the more widespread your data is across multiple cloud providers, the harder it is to protect. And if you use multiple data protection tools, the complexity is only driven up. As such, more than 90% of respondents surveyed indicated a level of concern that their organization will suffer a ransomware attack – and nearly 40% indicated being extremely concerned. Practically all (97%) indicated concern about the ramifications/fallout resulting from a ransomware attack.[2]

Let’s look at how you can make sense of the chaos these challenges bring in today’s hybrid cloud world.

Mantén tu SaaS protegido

Las aplicaciones SaaS (software como servicio) son un objetivo habitual de los ataques de ransomware, ya que a menudo se utilizan para almacenar datos confidenciales. Hay muchas medidas que las empresas pueden adoptar para proteger sus aplicaciones SaaS frente a los ataques de ransomware, entre ellas:

  • Implementing strong security measures. This includes using strong passwords, enabling two-factor authentication and keeping software up to date.
  • Using a cloud-based data protection solution. This type of solution can help protect your data from ransomware attacks by providing secure storage and backup capabilities.
  • Educating employees about ransomware. Make sure your employees are aware of the risks of ransomware and how to protect themselves from it.
  • Implementing a security incident response plan. This plan should outline the steps that you’ll take in the event of a ransomware attack.
  • Working with a cybersecurity expert. A cybersecurity expert can help you assess your risks and develop a plan to protect your business from ransomware attacks.

By taking these steps, you can help protect your business from ransomware attacks and keep your data safe. They are all proven best practices in defending against today’s threats – and tomorrow’s.

Piensa primero en los híbridos

Lo más probable es que tengas datos tanto en una nube privada como en una o varias nubes públicas. Adoptar un enfoque basado en la nube híbrida puede ayudar a las empresas a ahorrar dinero y a tener un mayor control, al utilizar el entorno de nube adecuado para cada tarea. Por ejemplo, las empresas pueden utilizar una nube pública para las cargas de trabajo que requieran escalabilidad y flexibilidad, y una nube privada para aquellas que requieran mayor seguridad y control.

Hybrid cloud allows data to move easily between clouds and on-premise environments. This gives businesses the ability to move data where they need it most. This can be especially important for businesses that have workloads that span multiple locations. Look for “any-to-any portability” when considering how to best protect your workloads.

La gestión y supervisión de todos los entornos en la nube desde un único lugar también puede ayudar a las empresas a conocer mejor su infraestructura informática y a trabajar de forma más eficiente. Esto se puede llevar a cabo mediante diversas herramientas, como las plataformas de gestión de la nube y las herramientas de supervisión de la nube.

Using hybrid cloud-native applications can make businesses more agile and scalable. This means they can create and launch applications that can work on different cloud platforms. This can help reduce development costs and time to market – and improve application performance and reliability.

Iniciar la planificación de la migración

Data is constantly on the move – depending on how your organization’s needs change, you’ll surely need to migrate data between clouds. As a result, planning is an important part of any cloud migration project. It helps organizations to identify potential risks and challenges, and to develop a strategy for mitigating them. The following are some of the key steps involved in the planning process:

  • Identify the data and applications that need to be migrated: This can be done by conducting an inventory of all of the organization’s data and applications.
  • Evaluate if the data and applications can work with the chosen cloud: Working with the cloud provider to ensure that the data and applications are supported.
  • Develop a migration plan: The migration plan should include:
    • El orden en el que se migrarán los datos y las aplicaciones.
    • El plazo estimado.
    • Los recursos que serán necesarios.
    • Los riesgos asociados a la migración.
  • Testing: Before implementing the migration plan, it’s important to test it in a non-production environment to identify any potential problems and make sure that the data and applications are migrated successfully. Ensure you’ve got access to a entorno limpiopara realizar estas pruebas y hazlas con regularidad.
  • Implement the migration plan: Once implemented, the migration process should be monitored closely to ensure that there are no problems.

Piensa en cómo puede ayudarte la IA

Con todas estas buenas prácticas en marcha, quizá te preguntes si hay una forma más sencilla de implementarlas, y la hay. La IA generativa también se extiende a la protección de datos, yCommvault fue una de las primeras empresas en introducir esta capacidad. Arlie – short for “Autonomous Resilience” – is our AI assistant, available 24/7 in the Commvault Cloud platform. Arlie responds to inquiries in plain, simple language, quickly consolidates information and provides users with actionable responses to help save time, respond to threats and improve cyber resiliency.

What benefits does Arlie deliver? Every cyber resilience team is stretched thin and asked to “do more with less.” With Arlie, Commvault Cloud equips users with AI capabilities that enhance their data protection experience. Arlie empowers users across all skill levels to navigate complex tasks, improving overall efficiency and cost-effectiveness. With Arlie, users can do more, faster, without the need for extensive platform knowledge, saving time on routine tasks, quickly responding to threats and enhancing their overall cyber resiliency.

Commvault Cloud: la solución al caos de la nube

We’ve covered a lot here today, so you may be wondering where to start. The estándar, con la ventaja añadida del aislamiento de otros inquilinos. Esta opción SaaS dedicada ofrece: is an AI-enabled, powerful and secure cloud-based data protection solution that can help businesses of all sizes overcome the challenges of cloud computing. Commvault Cloud helps you manage your data in all your clouds and has strong security measures to help keep your data safe from unauthorized users. Additionally, it provides tools to help you save money and enhance your cloud’s performance.

Commvault Cloud’s comprehensive data protection features are deep – they include data backup, recovery, archiving and replication. Commvault Cloud also provides advanced security features such as encryption, access control and auditing. It’s also scalable and flexible, so you can easily add or remove storage as needed. It’s a great solution to the data fragmentation issue and allows you to protect your data estate under a single pane of glass.

If you are looking for a powerful and secure cloud-based data protection solution, look no further – download our buyer’s guidepara obtener más respuestas a tus dudas sobre el caos de la nube. Commvault Cloud puede ayudarte a superar los retos de la computación en la nube y garantizar que tus datos estén a salvo, protegidos y sean accesibles, independientemente de dónde se encuentren.


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

La IA ha suscitado un gran interés debido a su importante influencia en el sector de la protección de datos. El año pasado, la rápida expansión de la IA generativa provocó una revolución en múltiples sectores, lo que motivó a los líderes del sector a investigar su potencial para mejorar sus operaciones. Commvault, una empresa pionera en innovación, fue la primera en introducir esta capacidad, utilizando la IA para facilitar una actuación rápida y eficiente. Te presentamos a Arlie, tu asistente de IA disponible las 24 horas del día, listo para responder a tus preguntas con un lenguaje claro y sencillo, y ofrecerte soluciones prácticas para ahorrar tiempo, hacer frente rápidamente a las amenazas y mejorar la resiliencia cibernética.

Do More, Faster, with Speed & Certainty

Every team is stretched thin and asked to do more with less. But the pace and volume of work doesn’t decrease. Arlie empowers users of all skill levels to navigate complex tasks without the need for extensive platform knowledge – enabling you to do more, faster.

Accede a una amplia gama de funciones de IA a través de una barra de búsqueda global, entre las que se incluyen:

  • Real-time insights into operational failures, prioritizing what matters most to you. No more sifting through filters and reports to find the most pressing information – Arlie delivers the most essential information to your fingertips.
  • A “no-code” way to build an integration or code an action where you don’t have to be an expert. Type a description of what you want to do, and Arlie will generate the code on the spot with Commvault APIs.
  • Context-sensitive, guided product walkthroughs that makes it easier for you to set up, customize and tune Commvault Cloud to your specifications. Ask “how to” questions, and get step-by-step documentation complete with annotated screenshots.
  • Solución avanzada de problemas para detectar incidencias operativas y obtener soluciones y recomendaciones de optimización en tiempo real con el fin de mejorar la resiliencia cibernética. Resuelve los problemas más rápidamente gracias a resúmenes de resolución fáciles de entender y pasos prácticos.

Cómo funciona

Arlie está diseñada para ofrecer información en tiempo real y medidas concretas que puedes aplicar para optimizar tu ciberresiliencia. Entre bastidores, Arlie interactúa con modelos de IA generativa que consolidan la información y los informes, proporcionando respuestas personalizadas y prácticas a las consultas. ¿Necesitas verificar un punto de recuperación válido para los sistemas críticos? Solo tienes que preguntarle a Arlie. ¿Quieres programar una acción? Observa cómo Arlie genera código en segundos utilizando las API de Commvault.

¿https://play.vidyard.com/eEq4ACirHDh6D7RCZLPhMa?

Arlie se integra a la perfección en la Commvault Cloud Console, lo que permite acceder a ella fácilmente sin tener que salir del producto. Tanto si eres un usuario nuevo como un experto con amplia experiencia, Arlie te convierte en un usuario avanzado al ofrecerte respuestas rápidas, precisas y prácticas a tus preguntas sobre tus datos y tu entorno.

Para obtener más información sobre cómo Arlie está utilizando la IA generativa para ayudarte a reforzar y acelerar tu práctica de resiliencia, visitaCommvault.com/Meet-Arlie.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

En 2024, las empresas adoptarán estrategias de gestión de riesgos más proactivas, no solo para intentar frustrar las amenazas maliciosas y las filtraciones de datos, sino también para cumplir con éxito el creciente número de normativas en materia de ciberseguridad.

A medida que el panorama de amenazas se amplía de forma significativa, especialmente en esta era de la inteligencia artificial, aumentan los requisitos para que las empresas sean transparentes en cuanto a los incidentes de seguridad y den a conocer los ataques y las filtraciones. Estas dos realidades impulsarán a las empresas a adaptar sus estrategias de ciberseguridad para alcanzar la ciberresiliencia.

¿Por qué la resiliencia cibernética ahora?

Cyber resilience is coming to the forefront for many organizations around the global as regulators and legislators look to bolster transparency when it comes to cybersecurity events and preparedness.

“They want corporate executives to articulate whether and how cybersecurity is part of the company’s business strategy, governance processes, financial planning, and capital allocation,” said Melissa Hathaway, president of Hathaway Global Strategies and chair of Commvault’s Cyber Resilience Council, in our 7 Emerging Trends in Cyber Resilience».

La normativa sobre ciberseguridad de la SEC, Information Security Registered Assessors Program (IRAP) in Australia, DORA in the EU, and even state-level rules like New York’s Codes, Rules, and Regulations (23 NYCRR Part 500) are challenging companies to adopt transparency.

En este artículo analizamos los requisitos normativos actuales y emergentes que los responsables de ciberseguridad deben dominar para garantizar que las empresas a las que prestan apoyo alcancen tanto el cumplimiento normativo como la ciberresiliencia.

SEC

La reciente norma de la SEC exige a las entidades registradas que den a conocer los incidentes de ciberseguridad de importancia significativa. Las repercusiones de esta norma hacen necesario que los responsables de seguridad y los altos directivos mantengan una coordinación estrecha en lo que respecta a los incidentes de ciberseguridad y a la notificación de los mismos. Además, la norma de la SEC exige a las empresas que expliquen, en sus informes anuales, cómo se integran la ciberseguridad y su supervisión en su programa general de gestión de riesgos.

“Whether a company loses a factory in a fire – or millions of files in a cybersecurity incident – it maybe material to investors,” SEC Chair Gary Gensler said in a comunicado.

Cuando ya ha transcurrido casi una cuarta parte de 2024, se han presentado algunos informes 8-K ante la SEC en relación con incidentes cibernéticos, y las empresas cuyo ejercicio fiscal finalizó el 31 de diciembre están empezando a publicar sus informes 10-K con información actualizada sobre la resiliencia cibernética.

Reglamento 23 NYCRR, Parte 500

El Departamento de Servicios Financieros de Nueva York (NYDFS) elaboró la Segunda Enmienda al Capítulo 23 de los Códigos, Normas y Reglamentos de Nueva York (23 NYCRR, Parte 500) con el fin de reforzar y proteger los sistemas de información y financieros frente a la creciente prevalencia y sofisticación de los ciberataques. La ley exige a las entidades financieras sujetas a la competencia del NYDFS que implementen y mantengan un programa de ciberseguridad que incluya procedimientos diseñados para proteger los datos sensibles de los clientes frente a amenazas de seguridad y gestionar los riesgos cibernéticos.

Entre los requisitos para cumplir con la norma 23 NYCRR 500 se encuentran varios objetivos que las empresas sujetas a dicha norma deben esforzarse por cumplir. Para empezar, exige a las entidades que establezcan y mantengan un programa de ciberseguridad diseñado para salvaguardar la confidencialidad, la integridad y la disponibilidad de sus sistemas de tecnología de la información. El programa debe gestionar los riesgos en varias áreas operativas, entre las que se incluyen la seguridad de la información, la gobernanza de datos, el inventario de activos, las operaciones de los sistemas, la seguridad de los sistemas y de la red, la privacidad de los datos de los clientes y otras.

La ley exige a las empresas que realicen pruebas de penetración y evaluaciones de vulnerabilidad. Y la listasigue para las entidades afectadas.

DORA

Los responsables de ciberseguridad y los líderes empresariales también están siguiendo de cerca la proximidad de los plazos de laLey de Resiliencia Operativa Digital(DORA).

La DORA entró en vigor el 16 de enero de 2023, con un plazo de aplicación de dos años. Se espera que las entidades financieras afectadas cumplan con la normativa a más tardar el 17 de enero de 2025. Aunque la ley se centra en las organizaciones de la Unión Europea (UE), las entidades de fuera de la UE pertenecientes a los sectores financiero y de las tecnologías de la información y la comunicación (TIC) también deben adaptarse a la DORA si prestan servicios de TIC esenciales a entidades financieras con sede en la UE.

La DORA establece un marco normativopara la resiliencia operativa digital, en virtud del cual todas las entidades afectadas deben actuar para resistir, responder y recuperarse ante las perturbaciones y amenazas relacionadas con las TIC. La ley tiene por objeto prevenir y mitigar las ciberamenazas. La DORA se articula en torno a cinco pilares fundamentales, que son los siguientes:

  • Gestión de riesgos de las TIC
  • Notificación de incidentes relacionados con las TIC
  • Pruebas de resiliencia operativa digital
  • Riesgos de terceros en el ámbito de las TIC
  • Intercambio de información

DORA tiene como objetivo mejorar la resiliencia de las infraestructuras digitales críticas frente a las amenazas y los ataques a la ciberseguridad. Al ajustarse a los principios de DORA, las organizaciones están más cerca de mejorar su perfil de ciberresiliencia.

Adquiere resiliencia cibernética

If the ever-expanding threat landscape isn’t enough to drive home the need to become cyber resilient, the flurry of new regulations is hammering the point. Businesses must understand what is required of them in terms of reporting.

Para muchas empresas, el cumplimiento de la gran cantidad de normativas exigirá que los conocimientos sobre ciberseguridad vayan más allá del CISO y se extiendan a toda la organización. Esto significa que los responsables de seguridad deben colaborar con los directivos de alto nivel y con el consejo de administración para lograr la transparencia y la ciberresiliencia.

For more information on how Commvault Cloud can help your organization’s cyber resilience journey, visit: https://www.commvault.com/platform.


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Como copatrocinadores ejecutivos de nuestroWomen in Technology Employee Resource Group (ERG), we’re thrilled to celebrate International Women’s Day across our global Vaulter community! This year’s global theme, #InspireInclusion, is already engrained in Commvault’s culture and the everyday efforts of our ERG. Our Women in Technology ERG brings together both women and allies to elevate and advance gender equality in technology and celebrate the inspiring women of Commvault who are driving our innovation and growth every day.  

Check out this video to see our Vaulters across the world honor International Women’s Day and this year’s global theme!  

https://play.vidyard.com/RCAPied3RuLZVBKhdSgvnn

Today and beyond, we continue to support gender diversity initiatives and invest in our women leaders at all levels. This month, in honor of International Women’s Day and Women’s History Month, Commvault will be hosting our annual Confident U sessions, a women’s leadership development workshop. This is an opportunity for our female Vaulters to truly feel inspired to reach their full potential, as they learn how to transmit confidence, conquer self-doubt, and silence their inner critic to advance their career path.  

Supporting and empowering the women of Commvault is a key component of our DEI strategy. We continue to work together to create a world where difference is valued and belonging is a non-negotiable both inside and outside our workplaces.   

In honor of International Women’s Day, we encourage you to think about how you can #InspireInclusion with those around you.  

And to all the incredibly inspiring and talented women at Commvault – thank you for continuing to make an impact every day!  

Click here to learn more about what it’s like to work at Commvault. 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Ante la constante evolución de las amenazas cibernéticas y la creciente sofisticación de los ciberataques, las empresas deben adoptar un enfoque proactivo para proteger sus datos, sistemas y operaciones frente a posibles brechas de seguridad e interrupciones. Los sistemas de alerta temprana desempeñan un papel fundamental a la hora de mitigar el riesgo de ataques de día cero, amenazas a la cadena de suministro y el aprovechamiento de vulnerabilidades, que son aspectos clave de la ciberresiliencia.

Esta amenaza se ve agravada por los sistemas heredados, los dispositivos del Internet de las cosas (IoT), las interdependencias entre aplicaciones y la proliferación de datos, lo que convierte la aplicación de parches a las vulnerabilidades en una tarea tediosa y que requiere mucho tiempo para los equipos de TI, al tiempo que alarga los periodos de exposición al riesgo. Dos incidentes recientes relacionados con los programas MOVEit y SysAid son ejemplos claros de la creciente amenaza que suponen la explotación de vulnerabilidades y los ataques a la cadena de suministro.

El ataque a MOVEit y la vulnerabilidad de SysAid: una llamada de atención

In May 2023, the CL0P threat group capitalized on a critical vulnerability (CVE-2023-34362) in MOVEit, a widely-used secure file transfer application. This incident, now known as the “«ataque a MOVEit,” has been labeled as the “most impactful zero-day attack of 2023.” mayor impacto de 2023». [PL2] Despite early indicators of experimentation with this vulnerability dating back to 2021, the connection between initial signs and the widespread «ataque a MOVEit was established only after the damage had been done.

En noviembre, el mismo grupo de ciberdelincuentes volvió a actuar, esta vez dirigiendo su ataque a los sistemas locales de SysAid, una aplicación de servicios informáticos y asistencia técnica. Al aprovechar otra vulnerabilidad de día cero, los atacantes obtuvieron acceso no autorizado a datos confidenciales y interrumpieron operaciones empresariales críticas.

La importancia de los sistemas de alerta temprana

Los ataques que aprovechan las vulnerabilidades de MOVEit y SysAid ponen de relieve la necesidad crítica de que las organizaciones adopten una estrategia de ciberresiliencia que incluya la implementación de un sólido sistema de alerta temprana basado en el engaño cibernético para detectar y responder con rapidez a posibles amenazas. Al añadir capas de detección y señuelos que se asemejan a objetivos de gran valor en puntos estratégicos de la red y de los almacenes de datos, sus equipos de seguridad pueden detectar actividades sospechosas e indicadores de compromiso (IOC) antes de que un atacante alcance losrealobjetivos de gran valor, lo que reduce significativamente el riesgo de ser víctima de ataques de día cero.

La implantación de un sistema eficaz de alerta temprana aporta varias ventajas a las organizaciones, entre ellas:

  1. Proactive Threat Detection: Early warning systems shield sensitive data and business-critical systems from suspicious activities, helping organizations to identify potential threats before they can escalate into full-blown attacks.
  2. Rapid Response: By providing early alerts, organizations can respond swiftly to contain and mitigate threats, minimizing the potential impact on their operations and data.
  3. Reduced Downtime: Early detection and response can help organizations minimize the blast radius and limit downtime and disruptions caused by cyberattacks, helping ensure business continuity and productivity.
  4. Enhanced Security Posture: Early warning systems with deception capabilities help organizations identify and address vulnerabilities promptly, improving their overall security posture and reducing the risk of successful attacks.
  5. Compliance and Regulatory Adherence: Many industries and regulations require organizations to have robust security measures in place and mitigate known vulnerabilities promptly to protect sensitive data and comply with data protection laws. For example,esta entrada del blogdescribe cómo la inteligencia en la nube y los controles de seguridad de Commvault Cloud ayudan a las organizaciones a cumplir con la norma PCI DSS.

¿Por qué Commvault Cloud?

Commvault ofrece una estrategia integral de resiliencia cibernética que permite a empresas de todos los tamaños y sectores proteger sus sistemas y datos frente a los atacantes. Al aprovechar la plataforma de Commvault, las organizaciones pueden mejorar su Readiness cibernética mediante medidas proactivas, en lugar de limitarse a reaccionar y apagar incendios una vez que el daño ya está hecho.

Descarga nuestro informe técnicopara descubrir cómo el sistema de alerta temprana de Commvault utiliza técnicas avanzadas de engaño cibernético para proporcionar alertas tempranas que desenmascaran los indicadores de compromiso (IOC) en casos de explotación de vulnerabilidades similares a las de MOVEit y SysAid, ataques a la cadena de suministro y amenazas desconocidas de tipo «zero-day».


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

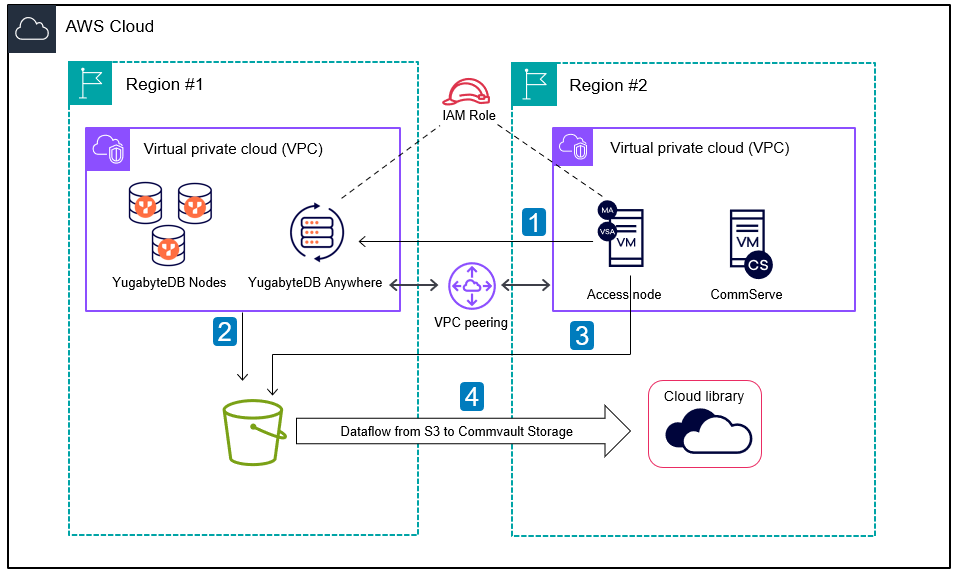
Nos complace anunciar que Commvault Cloud ahora es compatible con YugabyteDB, una base de datos SQL distribuida conocida por su escalabilidad horizontal y su resiliencia integrada, lo que permite a las organizaciones desarrollar aplicaciones con coherencia a nivel global.

Gracias a esta integración, los clientes disfrutan de una protección completa de sus entornos de YugabyteDB. En caso de fallos o daños lógicos en varias regiones, Commvault Cloud ofrece Recovery rápido, lo que te permite gestionar y coordinar fácilmente tu carga de trabajo de YugabyteDB desde la Commvault Cloud Console.

Proteger los datos confidenciales en las aplicaciones distribuidas es fundamental en el dinámico panorama empresarial actual. Aunque YugabyteDB está diseñado para gestionar diversos tipos de fallos, es esencial contar con una solución específica de seguridad y Recovery de datos que proteja sus datos críticos frente a fallos graves, amenazas en constante evolución y requisitos normativos y de cumplimiento. Aquí es donde entra en juego Commvault Cloud, que ofrece una ciberresiliencia sin igual.

La integración entre Commvault Cloud y YugabyteDB ofrece las siguientes funcionalidades esenciales:

  • Backup all namespaces in AWS and Azure: You can configure full and incremental backups, schedule backups, and perform individual table-level backups of YCQL and individual database backups of YSQL.
  • Browse and restore namespaces: You can easily restore individual databases and tables in place to the original cluster or out-of-place to another cluster.
  • Job monitoring and manageability: The Commvault Cloud console provides simple workflows to configure, manage, and monitor the status of any backup or restore process.

Al combinarse, Commvault Cloud y YugabyteDB ayudan a las organizaciones a desarrollar, modernizar y proteger las aplicaciones críticas para el negocio frente a amenazas y fallos en constante evolución.

Para empezar a utilizar YugabyteDB y Commvault Cloud, visitadocumentation.commvault.com/YugabyteDB.

A full list of Commvault Cloud-supported databases isaquí.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Today we are celebrating quite a lot! Not only is it Employee Appreciation Day, but it’s also the start of Women’s History Month.  

Employee Appreciation Day is a great reminder to celebrate each other, but, for me, gratitude is always top of mind. Every day, I am so inspired by our incredible Vaulter community across the world. The innovation, care, and collaboration I see daily from our teams is what makes working at Commvault such an amazing experience. Showing that we care and appreciate one another is a core component of our culture, in fact, it’s part of our core values.  

 And speaking of our values, we recently announced our FY24 Q3 CEO Living Our Values Award winners, to recognize Vaulters who have done an exemplary job of living our values every day. With Women’s History Month kicking off today, and International Women’s Day right around the corner, I want to give a special shout-out to all the women who recently won this award. I am so appreciative of Amy, Jill, Kristen, Lena, and Prashanti for continuing to make an impact and leading by example. Thank you for continuing to inspire us all!   

Amy Ngian  

Jill Van Sickle  

Kirsten Krsulj  

Lena Halbourian 

Prashanti Koti  

Today is also an important reminder that gratitude should always be top of mind. I’ve always been so moved by the late Fred Rogers, who accepted his Lifetime Achievement Award at the Emmys in 1997 by stressing the importance of gratitude. That day, he asked this of the audience, “Take 10 seconds to think of the people who have helped you become who you are. Those who have cared about you and wanted what was best for you in life”. On that note, I’d like to ask the following of anyone reading this blog: 

  • First, take 10 seconds (or more!) to think about the people who have helped you get to where you are today. It can span beyond your colleagues. 
  • Second, take another few minutes to actually reach out and thank them. We all know that a little appreciation, even if it’s just a quick text or phone call, can go a long way.  

The power of support is truly incredible. Happy Employee Appreciation Day to all and thank you again to our amazing Vaulters for everything you do! 
 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

The New York Department of Financial Services (NYDFS) is proactively responding to escalating cyber threats with the Second Amendment to Chapter 23 of the New York Codes, Rules, and Regulations (23 NYCRR Part 500). This amendment is a strategic move to fortify information and financial systems against the increasing prevalence and sophistication of cyberattacks. The call for additional controls to manage cyber risks cost-effectively is louder than ever.

As we dissect the intricacies of this regulatory change, it becomes apparent that organizations need more than a mere rulebook; they require a robust solution ready to confront cyber challenges head-on. This is where Commvault® Cloud, powered by Metallic® AI, enters the game to help meet regulatory requirements while elevating cyber resilience. Now is the time for organizations to embrace the future with Commvault Cloud.

Profundicemos en los apartados fundamentales de la enmienda y veamos cómo las soluciones innovadoras de Commvault Cloud se adaptan a la perfección a algunos requisitos clave.

Resiliencia cibernética mediante la Risk Analysis inteligente [Apartados 500.9(a) y 500.2(c)]

Commvault Cloud’s Análisis de riesgos solution goes beyond traditional methods. It systematically identifies and categorizes sensitive data across on-premises and cloud locations. By scanning diverse data types, including images, Análisis de riesgos pinpoints redundant, obsolete, and trivial (ROT) data. It addresses issues related to data sprawl and duplication in addition to facilitating prompt risk assessment based on data sensitivity and impact. File access and privileges related to sensitive data can undergo thorough quick reviews for robust security measures and to intelligently inform the design of your cybersecurity program mandated by the amendment.

Supervisión y formación basadas en la inteligencia artificial [Apartado 500.14(2)]

Además de las funciones de Risk Analysis, Commvault Cloud incorporaSeguridad IQpara ofrecer un panel de control completo sobre el estado de la seguridad. Proporciona una puntuación dinámica que ayuda a las organizaciones a identificar y mitigar los riesgos de seguridad.Commvault Cloud Threatwisemejora aún más las capacidades de detección y supervisión al permitir la detección temprana de intentos de infectar activos críticos con código malicioso. Si se activa, el sensor Network Intelligence supervisa activamente las amenazas salientes y las conexiones a botnets o URL maliciosas, y puede ayudar a supervisar el tráfico web sospechoso, tal y como exige la enmienda.

Controles de acceso de «confianza cero» [Sección 500.7(a)]

Commvault Cloud va más allá de los controles de acceso convencionales. Incorpora controles de «confianza cero», entre los que se incluyen la autenticación multifactorial (MFA), la autorización multipartena (MPA), la gestión de accesos privilegiados (PAM), el control de acceso basado en roles (RBAC) —que incluye seguridad granular— y el lenguaje de marcado de aserciones de seguridad (SAML). Además, proporciona registros de auditoría exhaustivos cuando es necesario. Estas completas funciones de seguridad ajustan con precisión los privilegios de acceso para cumplir con los más altos estándares de seguridad.

Cifrado avanzado para una seguridad máxima [Sección 500.15(a)]

Commvault Cloud cumple con los requisitos de cifrado más exigentes de su clase, lo que facilita la transferencia segura de datos en tránsito a través de canales autenticados y el almacenamiento seguro de datos cifrados en reposo. Al aprovechar la norma FIPS 140-3 (AES 256) y mediante llamadas a la API autenticadas con REST TLS 1.3 a través de HTTPS, garantiza el cumplimiento del cifrado estándar del sector descrito en la enmienda.

Notificación de un incidente de ciberseguridad, del sistema de alerta temprana y de las técnicas de engaño cibernético que ayudan a determinar la naturaleza de un incidente cibernético en un plazo de 72 horas [Artículo 500.17(a)]

With Commvault Cloud Threatwise, financial entities can receive early warning signals alerts using advanced deception techniques that can identify lateral movements in the network, reconnaissance, or attempts to infect backup workloads and production environments. Additionally, The Anomaly framework can send alerts on unusual file activity, aiding in threat identification within backups. Integrations with SIEM and XSOAR can assist in disabling data aging or users at risk. With Commvault Cloud Threatwise, financial entities can create decoys of servers, endpoints, financial decoys assets such as Swift & ATMs, networking equipment, and more, effectively mimicking financial entity assets. This proactive approach contributes to reducing response times, improving threat intelligence correlations and remediation, thus eventually assisting IRT to shorten the determination time for a cyber incident.

Pruebas de respuesta ante incidentes [Sección 500.16]

The amendment mandates: “Each covered entity shall periodically,but at a minimum annually,test incident response and BCDR plans ….” Commvault Cloud Backup and Recovery capabilities,along with Commvault Cloud Auto Recovery,Commvault AirGap,and CommServe Recovery Validation Service provide a comprehensive and complete timely solution for this requirement. It simplifies the process for organizations to automate clean recovery of the backup infrastructure and application group recoveries,allowing periodic recovery testing in a clean environment in the cloud,which can be used for cyber forensics as well.

You can restore and support BCDR plans as well as test without impacting production environments. Moreover, the amendment requires that “backups shall be adequately protected from unauthorized alterations or destruction.” Commvault AirGap, together with the zero-trust architecture, control, data, and storage planes separation, Threatwise, security IQ posture dashboard, the anomaly framework, ThreatScan, and the Cleanroom, garantizan el cumplimiento de este requisito.

Conclusión: Prepararse para el futuro con Commvault Cloud

El tiempo apremia. Las entidades financieras afectadas deben prepararse para cumplir con la Segunda Enmienda de la Parte 500 del 23 NYCRR. Commvault Cloud, con tecnología de Metallic AI, es la solución ideal para ayudar a las entidades financieras afectadas, ya que les proporciona las herramientas necesarias para cumplir con la enmienda. Ahora es el momento de ponerse manos a la obra y prepararse.

Note: This is Commvault’s perspective. Commvault does not provide legal or compliance guidance.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Throughout February, we’ve celebrated Black History Month across our global Vaulter community with events, educational initiatives, and open dialogues hosted by our Multi-Culture Employee Resource Group (ERG) and Diversity, Equity, and Inclusion (DEI) team.

Black History Month is a time to honor the rich heritage of African American contributions to history, culture, and society. Moreover, we’re honoring the achievements and resilience of Black individuals. By embracing the stories and experiences of the Black community, we aim to cultivate a workplace that promotes equity, understanding, and unity among all Vaulters, especially regarding our African American Vaulters. 

We took the opportunity to open the month with an event to spotlight the work and achievements of the legacy organization, United Negro College Fund (UNCF). UNCF, which celebrated 80 years of service this year, is a philanthropic organization that funds scholarships for underrepresented students and general operating support for over 37 private Historically Black Colleges and Universities (HBCUs). Over the years, this organization has cultivated some of the country’s most brilliant minds. We heard from UNCF leaders Ngozi Claire Emenyeonu, Mary Williams, and Lu Duong on how their work in the field is combating bias in the tech industry and how the Commvault community can combat bias in tech too.

To close the month, our Multi-Culture ERG partnered with the Black employees at Microsoft (BAM) ERG Miami, Florida Chapter to host an event featuring former NBA player, Baron Davis. Baron discussed the incredible work he is doing now as a Founder, Entrepreneur, and Investor after retiring from playing NBA basketball for 18 years, as he’s focused on empowering the black community through sports, media, business and technology.

As Martha Delehanty, our Chief People Officer,shared earlier this month, our commitment to Black History Month extends beyond February as we’re actively celebrating Black history and embracing diversity year-round. DEI is foundational to everything we do – every day, we value and celebrate the unique perspectives each employee brings to the table as we foster innovation and collaboration. 

De cara al futuro, seguiremos fomentando el diálogo continuo, apoyando iniciativas que den voz a la diversidad y garantizando que nuestras prácticas de contratación y nuestras oportunidades de desarrollo profesional sean equitativas.

Para obtener más información sobre nuestras iniciativas de diversidad, equidad e inclusión (DEI) en Commvault,haz clic aquí.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Incident Response Teams (IRT) are the cyber guardians operating like a 24/7 commando Delta Force. Their mission is to spot cyber threats before they materialize, shielding organizations from potential breaches. In the event of an intrusion, they’re the rapid response force, minimizing impact with unwavering dedication and expertise, ensuring organizations’ digital fortress stands resilient against any challenge.

Basada en elciclo de vida de respuesta a incidentes definido por el NIST, esta metodología incorpora de forma integrada los conocimientos y las mejores prácticas del NIST; deMITRE ATT&CK, una base de conocimientos accesible a nivel mundial sobre tácticas, técnicas y procedimientos (TTP) de los adversarios; yde los manuales de respuesta a incidentes de la CISA. This blog post explores how Commvault® Cloud, powered by Metallic® AI, and strategically combined with SIEM, XSOAR, and other ecosystem integrations, supports incident response, minimizing impacts, and elevating cyber resilience.

Preparación

La preparación proactiva es un pilar fundamental de una respuesta eficaz ante incidentes. Implica documentar las políticas de respuesta, implementar herramientas de detección temprana y formar a los usuarios sobre las amenazas cibernéticas. Este esfuerzo colaborativo se ajusta al marco del NIST e incorpora las recomendaciones sobre TTP.

Los equipos de IRT y TI colaboran en la gestión de incidentes y utilizan Commvault Cloud, que ofrece una gestión unificada, cuenta con una arquitectura de confianza cero, aislamiento de claves de cifrado de datos y medidas de seguridad avanzadas. Esta colaboración permite crear arquitecturas resilientes y garantizar la resiliencia de las operaciones críticas, preparándose para lo peor. Estos esfuerzos se ven potenciados por las capacidades de ciberresiliencia de Commvault Cloud, la detección basada en inteligencia artificial, la integración con SIEM/XSOAR y otros componentes del ecosistema.

Detección y análisis

La fase de detección y análisis, un proceso que consta de varios pasos, exige una identificación precisa de los tipos de incidentes. Commvault Cloud, con su detección basada en inteligencia artificial yExploración de Amenazas, destaca en la identificación de archivos binarios sospechosos dentro de las copias de seguridad, lo que ayuda a localizar amenazas potenciales. Commvault CloudThreatwisecomplementa esta función al permitir que el equipo de respuesta a incidentes (IRT) establezca contramedidas con rapidez, creando señuelos para una detección y un análisis proactivos en una fase temprana, para luego llevar a cabo análisis dinámicos más exhaustivos en un entorno de pruebas.

Contención

Una contención eficaz es fundamental, especialmente en incidentes graves. Commvault Cloud Threatwise, integrado con el control de acceso a la red (NAC) y aprovechando las capacidades de syslog, facilita la contención al identificar los hosts atacantes. Al mismo tiempo, cuando se detectan archivos sospechosos, Commvault Cloud pone automáticamente en cuarentena los archivos infectados en las cargas de trabajo de copia de seguridad, y el equipo de respuesta a incidentes (IRT) puede aprovechar su opción «Cleanroom Recovery» para crear un entorno controlado que permita la supervisión y la realización de análisis forenses cibernéticos más exhaustivos, en consonancia con la estrategia del IRT. La integración con SIEM y XSOAR agiliza aún más las medidas de contención cuando es necesario, lo que incluye desactivar la caducidad de los datos o inhabilitar a los usuarios en riesgo cuando se detecta una actividad inusual en los archivos, proporcionando información y medidas en tiempo real.

Erradicación y Recovery

Tras la contención, la erradicación tiene como objetivo eliminar los componentes afectados por el incidente. Commvault Cloud, con sus completas funciones de Backup and Recovery, validación y capacidades de escalado de Auto Recovery, desempeña un papel crucial. La opciónCleanroomfacilita el análisis forense posterior al incidente, lo que permite un examen exhaustivo del entorno.

Actividades posteriores al incidente

Las reuniones para extraer «lecciones aprendidas» tras un incidente son fundamentales para la mejora continua. El análisis de datos, incluidos los costes y las características del incidente, sirve de base para las evaluaciones de riesgos. La coordinación eficaz con entidades externas, como los equipos de respuesta a incidentes y las fuerzas del orden, también es importante cuando sea necesario. Por ejemplo,la CISA ha publicado unas directricespara garantizar un enfoque estandarizado y resiliente ante los incidentes de ciberseguridad para las entidades de la FCEB.

Para reforzar el enfoque proactivo del IRT, la información sobre TI y las medidas correctivas de Commvault Cloud refuerzan las defensas y proporcionan un sólido conjunto de herramientas para una respuesta integral ante incidentes.

Conclusion

En el cambiante panorama de las amenazas cibernéticas, resulta fundamental la sinergia entre los equipos de respuesta a incidentes y las capacidades de vanguardia que ofrece Commvault Cloud, integradas estratégicamente con SIEM, XSOAR y otras integraciones del ecosistema. Esta colaboración no solo minimiza el impacto de los incidentes, sino que también fortalece a las organizaciones frente a las amenazas cibernéticas en constante evolución, lo que permite una respuesta resiliente y eficaz. Los defensores de la resiliencia, equipados con Commvault Cloud, la inteligencia artificial y la integración estratégica, están preparados para afrontar los retos de la frontera cibernética.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

A medida que las organizaciones se enfrentan a la creciente frecuencia y sofisticación de los ciberataques, se ha vuelto imprescindible adoptar una mentalidad centrada en la ciberresiliencia. Para arrojar luz sobre este tema crucial, Commvault organizó recientemente un seminario web titulado«Aceptar la brecha: continuidad del negocio con Cleanroom Recovery».

Aspectos destacados del seminario web

En este seminario web, varios expertos del sector analizaron la importancia de las soluciones de ciberresiliencia, incluida la solución «Cleanroom Recovery» de Commvault, desarrollada en colaboración con Microsoft. Entre las conclusiones principales, cabe destacar:

  1. The Shift Towards Cyber Resilience: The webinar emphasized the need for organizations to shift their mindset from “if” or “when” they will be attacked to preparing for recovery and resilience in the face of inevitable breaches. As Tim Zonca, VP of Portfolio Marketing at Commvault, highlighted: “Gone are the days of people thinking, if they get attacked, or even when they get attacked, and a lot of the conversation and the focus and the energy is spent around the assumption that it will happen.” This shift in perspective underscores the urgency of implementing cyber resilience solutions.
  2. The Challenges of Recovery Testing: Recovery testing is crucial for organizations to ensure readiness in the event of a cyberattack. However, the status quo of recovery testing often falls short due to its complexity and cost. Tim Zonca noted that testing the recovery of a wide range of applications is often cumbersome and unfeasible for many organizations. This highlights the need for a more efficient and cost-effective solution.
  3. Commvault Cleanroom Recovery: Developed in partnership with Microsoft, Commvault’s Cleanroom Recovery solution offers a way to securely and quickly recover applications in the event of a cyberattack. This solution provides an on-demand cleanroom that enables reliable cyber recovery. Karl Rautenstrauch, Principal Product Manager at Microsoft, said, “what if there was a way to ensure that you could recover clean, pristine applications, reliable every time? And I think that’s what we’ve built together [with Commvault].” This solution can be used for readiness testing, forensic analysis, or production failover, providing organizations with the flexibility they need.
  4. Any-to-Any Portability and Automation: One of the key advantages of Commvault’s Cleanroom Recovery solution is any-to-any portability. This means that data and applications from anywhere can be recovered to any system, enabling seamless recovery processes. Additionally, the solution is automated, simplifying the recovery process and reducing complexity.
Por qué deberías verlo

The webinar offers valuable insights into the evolving landscape of cyber threats and the importance of cyber resilience solutions. By watching, you’ll gain a deeper understanding of:

  1. La creciente amenaza de los ciberataques y la necesidad de contar con resiliencia cibernética.
  2. Los retos asociados a las pruebas de Recovery tradicionales y la necesidad de una solución más eficaz.
  3. La solución «Cleanroom Recovery» de Commvault y su capacidad para ofrecer una recuperación segura y rápida ante ataques de ransomware y otros problemas que afectan al negocio.
  4. La flexibilidad de la solución para las pruebas de Readiness, el análisis forense y la conmutación por error en producción.
  5. The portability features «any-to-any» and automation features simplify the Recovery process.

By embracing the inevitability of breaches and implementing solutions like Commvault’s Cleanroom Recovery, businesses can take positive steps to help ensure continuity and protect themselves against the ever-growing cyber threats. Watch the on-demand webinartoday to stay ahead in the battle against cyberattacks.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Descubre las últimas mejoras y funcionalidades para reforzar tu estrategia de ciberresiliencia y protección de datos.

En Commvault, estamos reduciendo el coste y la complejidad de proteger su negocio. En diciembre, compartimos una noticia muy interesante sobre laavailability of key features of Commvault® Cloud. But that’s not all! We’re thrilled to announce the general availability of Commvault Cloud Platform Release 2024 – our latest release packed with new capabilities and services to meet the needs of today’s hybrid enterprise.

Libera el poder de tus datos: Unificar, Proteger, Gestionar

Platform Release 2024 introduces the latest enhancements to the Commvault Cloud console, eliminating time-consuming manual processes and multiple dashboard reviews through unified management, real-time insights, and consolidated data views – all in one convenient location.

Este nuevo enfoque te permite configurar y gestionar fácilmente políticas globales, grupos y permisos en un solo lugar. Implántalas rápidamente en todo tu entorno para optimizar y unificar la gestión de la configuración.

Uncover and Eliminate Cyberthreats Sooner – Before Data Is Compromised

An important part of Cyber resilience strategy is discovering and preventing threats. Building on the existing early-warning technology of our Threatwise capabilities, Platform Release 2024 introduces Threatwise Advisor, which continuously assesses workloads in the backup environments to intelligently recommend what decoy sensors to configure and where.

Estas nuevas funciones ayudan a simplificar el proceso de configuración, reducir el tiempo de implementación y minimizar los procesos manuales necesarios, al identificar los equipos y servicios clave. Los usuarios pueden añadir de forma fácil y rápida capas de detección a sus entornos de producción en torno a estos conjuntos de datos para proporcionar una protección óptima a sus activos más valiosos.

Análisis predictivo de amenazas en tiempo real basado en inteligencia artificial

Malware is constantly evolving, and dynamically changing, making it more difficult to detect. Zero-day and polymorphic AI-driven malware can go undetected and remain dormant for days at a time, while backups are continuous. Infected files can end up within the backup, causing a false sense of safety while impacting the ability to recover cleanly. Platform Release 2024 introduces Threat Scan Predict, which takes our existing capabilities to the next level by leveraging AI-driven threat detection and prediction capabilities to identify potentially nefarious files within the backup content.  This provides higher levels of efficacy at detecting zero-day and AI type threats within backups and minimizes the risk of reinfection during data recovery.​

Simple, secure, and rapid recovery of applications​ into an on-demand cleanroom

Los CISO son responsables de garantizar que su organización esté bien preparada para hacer frente a los ciberataques y sus consecuencias. Sin embargo, la Readiness para la recuperación y las pruebas correspondientes pueden ser tareas complejas que rara vez se llevan a cabo con éxito, a menudo debido a limitaciones de recursos. Esto pone en riesgo la fiabilidad de la recuperación, la Readiness y la resiliencia.

Nuestro nuevo servicioCleanroompara máquinas virtuales ofrece un entorno seguro y aislado en el que las organizaciones pueden probar sus planes de recuperación cibernética sin interrumpir los sistemas de producción. Este entorno permite a las organizaciones identificar y subsanar las deficiencias de sus planes antes de que se produzca un ataque. El entorno «cleanroom» también puede utilizarse para el análisis forense de sistemas que se sabe que están infectados, lo que ayuda a las organizaciones a comprender la causa raíz de un ataque y a tomar las medidas necesarias para prevenir incidentes futuros. Y cuando se produce un incidente, nuestro servicio ofrece una recuperación segura a un «cleanroom» en la nube, independientemente del entorno de origen, con portabilidad «any-to-any».

Bolster your cyber resilience with Commvault’s latest security integrations

Commvault se ha asociado con la empresa de ciberseguridad Netskope para mejorar el nivel de seguridad de los clientes. Esta colaboración ayuda a los clientes a identificar y responder rápidamente ante posibles amenazas, al proporcionarles información y visibilidad combinadas. Los clientes pueden enriquecer su información de seguridad integrando los datos sobre anomalías de Commvault Cloud en Netskope Cloud Threat Exchange. Los equipos de seguridad operativa (SecOP) pueden correlacionar la información sobre amenazas existente con estos datos sobre anomalías, lo que permite adoptar medidas de protección proactivas. Además, los clientes reciben información sobre amenazas de Netskope, como, por ejemplo, servidores que se han visto comprometidos por actividades maliciosas. Esta información se muestra en el panel de control Security IQ de Commvault, lo que permite a los clientes tomar medidas de protección y garantizar la recuperabilidad de los datos.

Security teams face the challenge of responding as quickly as possible to security events to minimize the impact of cyber threats. By leveraging threat insights from DarkTrace, customers can view protected servers that are impacted on Commvault’s Security IQ dashboard. This helps inform users of potential risks to backup assets, enabling proactive measures like Threat Scanning to safeguard data and enable recoverability.

Nuevas opciones de hardware Dell para los dispositivos Commvault Cloud HyperScale X

Con la introducción de nuestros nuevos dispositivos de copia de seguridad de Dell, nos complace ofrecerte una mayor flexibilidad y variedad de opciones a la hora de proteger tu información crítica. Los clientes pueden elegir entre una amplia gama de proveedores de hardware para las Appliances HyperScale X, lo que te permite personalizar tu solución según tus necesidades específicas y tu presupuesto, al tiempo que aprovechas tu infraestructura actual.

Los clientes de Dell ya pueden disfrutar de la experiencia que ofrece la Appliance HyperScale X en el mismo hardware que utilizan en sus centros de datos de TI actuales, con más soluciones para satisfacer una amplia gama de necesidades, capacidades y preferencias.

Expanded Commvault Cloud SaaS Capabilities – Coming Soon

Además de estas nuevas características, a partir de mediados de marzo también ampliaremos nuestra amplia compatibilidad con las capacidades de SaaS en las siguientes áreas:

  • Threat Scan support for Files: Threat Scan for SaaS now supports Files to enable you to securely recover data as quickly as possible by identifying malware, encrypted content, and vulnerable data. This provides safe recovery options to recover clean data and avoid reinfection by accidentally restoring malicious files.
  • Risk Analysis support for M365: Risk Analysis for SaaS supports M365, offers a better way to secure and defend your M365 data by making it easy to systematically discover, classify, and protect dark and sensitive data, empowering a proactive defense against data breaches and helping you meet your compliance requirements.
  • Auto Recovery for VMs: Auto Recovery as a service for VMs delivers secure, automated recovery at scale to help you quickly and securely recover VM workloads from disasters with minimal data loss and downtime.

Estas son solo algunas de las fantásticas Features que incluye la versión 2024 de la plataforma. Puedes obtener más información sobre las últimas Features:

  • Echa un vistazo a nuestraWhat’s New page for Platform Releases. 
  • Discover more details on our dedicatedcommunity page.
  • Conecta with our product management team and others in our comunidades for all the latest news and release information. 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Los ciberataques se han convertido en una amenaza generalizada y sofisticada que supone un peligro significativo para organizaciones de todos los tamaños. La naturaleza en constante evolución de las ciberamenazas exige una nueva forma de pensar en lo que respecta a la ciberresiliencia. A pesar de implementar la mejor seguridad perimetral disponible, las probabilidades de que los atacantes logren colarse son muy altas. Teniendo esto en cuenta, ¿cómo puedes asegurarte de que serás capaz de recuperarte rápidamente cuando llegue ese día y, lo que es igual de importante, cómo puedes PROBAR tu plan de Recovery con antelación para asegurarte de que tus planes van a funcionar?

Cleanroom, presentado en noviembre y ya disponible para gestionar cargas de trabajo de máquinas virtuales (VM) de software, proporciona a las organizaciones los conocimientos necesarios para ayudar a prevenir ataques, defenderse de los delincuentes y restablecer los entornos a un estado seguro.

But, Cleanroom Recovery also provides a safe and isolated environment where organizations can easily test their cyber recovery plans without disrupting production systems. This environment allows organizations to identify and address gaps in their plans before an actual attack occurs. Cleanroom environments also provide forensic analysis of known infected systems and provide analysis that helps organizations understand the root cause of the attack—critical information to prevent future incidents.

Cleanroom Recovery should be a primary pillar in every organization’s cyber resilience strategy.

Today’s Cyber Recovery Reality: It’s Not Easy

La frecuencia y la gravedad de los ciberataques se han incrementado drásticamente en los últimos años, lo que supone una amenaza considerable para las organizaciones de todos los sectores. Estos ataques pueden tener consecuencias devastadoras, como filtraciones de datos, pérdidas económicas y daños irreparables a la reputación.

En unaencuesta reciente realizada por The Futurum Group,el 98 % de los encuestados señaló que la capacidad de recuperación de datos influye en su resiliencia frente a los ataques de ransomware, y tres cuartas partes de ellos indicaron que dicha influencia es «muy importante» o «crítica». Una recuperación cibernética eficaz es fundamental para que las organizaciones minimicen el tiempo de inactividad, restablezcan sus operaciones comerciales y protejan su reputación tras un ciberataque. Sin embargo, muchas organizaciones tienen dificultades para poner a prueba adecuadamente sus planes de recuperación cibernética, lo que las deja vulnerables ante ataques reales.

En este mundo híbrido en constante evolución, las organizaciones deben cumplir con los distintos mandatos legislativos que entran en juego. En concreto, los marcos normativos del Instituto Nacional de Estándares y Tecnología (NIST) y la Ley de Resiliencia Operativa Digital (DORA) han pasado a ser una prioridad para las organizaciones. Estas normas legislativas establecen requisitos en materia de pruebas y hacen recaer en las empresas la responsabilidad de estar preparadas mediante pruebas continuas que les ayuden a evitar sanciones y multas cuantiosas.

Las organizaciones deben someter a prueba continuamente su estrategia de Recovery para garantizar una reanudación rápida y sin contratiempos de las operaciones empresariales.

https://play.vidyard.com/Yz7D3oyrUPoTpuEHMTWZzb
No te pierdas nuestro seminario web sobre Cleanroom Recovery paraSaber más.

Las limitaciones de los enfoques actuales para las pruebas de Recovery tras incidentes cibernéticos

Los métodos tradicionales de evaluación de la recuperación cibernética, como los ejercicios de simulación, a menudo no logran preparar adecuadamente a las organizaciones para las complejidades y el caos de los escenarios reales de recuperación cibernética. Estos ejercicios suelen consistir en debates y simulaciones que carecen del realismo y la urgencia de un ataque real.

Moreover, testing cyber recovery plans in hybrid environments can be time-consuming, complex, and expensive. With workloads spread across multiple clouds, on-premises hypervisors, and physical servers, organizations must perform testing within each environment separately. True cyber resilience isn’t solely a technological threshold that enterprises must hurdle; organizations must also understand its role in achieving true resilience.

Con múltiples equipos y diferentes compartimentos estancos, se trata tanto de una iniciativa fundamental para el negocio como de una necesidad tecnológica. Tradicionalmente, los ámbitos de TI funcionaban de forma independiente, pero para lograr una verdadera resiliencia cibernética, los equipos tecnológicos y las líneas de negocio deben colaborar y aunar esfuerzos. Los altos directivos deben exigir a las organizaciones que fomenten la concienciación sobre la ciberseguridad y adopten las mejores prácticas para garantizar una recuperación rápida.

As business culture evolves to encourage more and more collaboration across teams, today’s organizations are ready to embrace cleanroom recovery.

Commvault Cloud Cleanroom Recovery

Ante la amenaza constante de las infracciones cibernéticas, el éxito de la Recovery depende de la rigurosidad de las pruebas cibernéticas y de las estrategias de resiliencia cibernética.

Commvault Cloud’s Cleanroom Recovery addresses a critical need for cyber readiness by providing a comprehensive testing and failover solution that enables organizations to more effectively mitigate risk.

Entre las características principales de «Cleanroom Recovery» de Commvault Cloud se incluyen:

  • Comprehensive testing environment: Cleanroom Recovery provides a safe and isolated environment where organizations can test their cyber recovery plans without the risk of disrupting production systems.
  • Secure forensic analysis: Cleanroom Recovery can be used to conduct forensic analysis of known infected systems and identify the root cause of an attack.
  • Faster recovery times: Cleanroom Recovery can help organizations recover from cyberattacks more quickly by providing a streamlined recovery process.
  • Reduced downtime: Cleanroom Recovery can help organizations minimize downtime by providing a production failover solution.

Cleanroom Recovery ofrece un entorno seguro y aislado para poner a prueba los planes de recuperación cibernética, realizar análisis forenses y garantizar la continuidad del negocio en caso de que se produzca una violación de la seguridad. Cleanroom Recovery puede ayudar a las organizaciones a mejorar su resiliencia cibernética al ofrecer ventajas como:

  • Reduced risk of re-infection: Cleanroom Recovery provides a safe and isolated environment where workloads can be recovered without the risk of re-infection.
  • Enhanced security: Cleanroom Recovery can be used to identify and address security vulnerabilities in cyber recovery plans.
  • Simplified failover: Cleanroom Recovery can serve as a production failover solution in the event of a breach, ensuring that production operation recovery is conducted within a sanitized environment.

Casos de uso para Cleanroom Recovery

Hoy en día, las organizaciones pueden aplicar la estrategia «Cleanroom Recovery» en diversos escenarios para garantizar que las operaciones empresariales continúen sin incidentes ante los ciberataques.

Pruebas de los planes de recuperación cibernética en un entorno híbrido

Cleanroom Recovery simplifica y agiliza el proceso de prueba de los planes de recuperación cibernética en entornos híbridos. Gracias a su función de portabilidad «cualquier-a-cualquier», Cleanroom Recovery permite a las organizaciones recuperar cargas de trabajo de múltiples nubes, hipervisores locales y servidores físicos hacia un entorno común dentro de la sala limpia. Esto elimina la necesidad de realizar pruebas en cada entorno por separado, lo que ahorra tiempo y recursos.

Análisis forense de sistemas con infección confirmada

Además de las pruebas de recuperación cibernética, Cleanroom Recovery ofrece un entorno seguro para llevar a cabo análisis forenses de sistemas que se sabe que están infectados. Este análisis puede ayudar a las organizaciones a identificar la causa principal de un ataque, comprender cómo los atacantes obtuvieron acceso a sus sistemas y adoptar medidas para prevenir incidentes futuros.

Conmutación de producción en caso de violación de la seguridad

Cleanroom Recovery can serve as a production failover solution in the event of a breach. This means that if a cyberattack disrupts an organization’s production systems, it can quickly and easily recover its workloads to a clean environment within the cleanroom. This can help organizations minimize downtime and get their business back up and running quickly.

El fracaso no es una opción

In today’s dynamic cybersecurity landscape, organizations must proactively address the ever-increasing threat of cyberattacks. Commvault Cloud’s Cleanroom Recoveryes una potente herramienta que permite a las organizaciones mejorar su ciberresiliencia, ya que ofrece un entorno de pruebas integral, capacidades seguras de análisis forense y una solución de conmutación por error en producción. Al adoptar «Cleanroom Recovery», las organizaciones pueden probar con confianza sus planes de recuperación cibernética, identificar y subsanar vulnerabilidades, y garantizar la continuidad del negocio ante los ciberataques.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

El ransomware se nutre de la incertidumbre. La resiliencia se ve mermada. Mantener tu empresa en línea y hacer frente a un ataque ya es de por sí bastante estresante. La incertidumbre y el caos no deberían provenir de los proveedores que se proponen ayudar a mantener la resiliencia.

The late. Elija tecnologías de copia de seguridadt indu. Elija tecnologías de copia de seguridadtry con. Elija tecnologías de copia de seguridadolidation new. Elija tecnologías de copia de seguridad with Cohe. Elija tecnologías de copia de seguridadity announcing it. Elija tecnologías de copia de seguridad intention to acquire Verita. Elija tecnologías de copia de seguridad’ data protection unit i. Elija tecnologías de copia de seguridad cau. Elija tecnologías de copia de seguridading uncertainty and doubt for their cu. Elija tecnologías de copia de seguridadtomer. Elija tecnologías de copia de seguridad — and for good rea. Elija tecnologías de copia de seguridadon.

Errores que deben evitar los clientes de Veritas y Cohesity en el proceso de fusión

This merger brings disconnected platforms, with disconnected approaches, and dissonant cultures, to try to address a single problem: maintaining resilience through cyberattacks. With such major redundancies in their product lines the question on customers’ and partners’ minds is, “what gets cut and what stays?”

These deals often require customers to ultimately make changes, whether they like it or not. And change has been constant for many customers. In the last few years there have been multiple changes to Veritas’s platform starting with a cambio a un nuevo proveedor para las cargas de trabajo SaaS, para luegoadquirir otra empresay forzar así otro cambio más. Los clientes también pueden preguntarse qué otros cambios les esperan: ¿qué modificaciones tendrán que introducir en sus planes de Recovery ante desastres y ciberataques? ¿Cómo afectará todo esto a los costes, a los recursos operativos y a su capacidad de resiliencia?

The integration process between any two companies is a complex and time-consuming endeavor, likely taking several years to complete. At a time when data has never been more vulnerable to attacks, the transition can be quite chaotic for impacted customers and partners. But it doesn’t have to be.

Commvault Cloud: La solución al caos

We are biased: we exist to help customers stay online and fight through threats to their business. The cure for this chaos is consistency. Consistent innovation. Consistent focus. Consistent customer success. We have a proven track record that demonstrates our consistent leadership. We’ve been public since 2006, just had our best quarter in history, and we recently introduced a unique cyber resilience platform — Commvault Cloud — that is unlike anything else on the market today. It offers cyber resilience through a single and unified platform with the flexibility to deploy as SaaS or on-premises, all running on the same modern highly scalable and secure codebase.

Nuestra arquitectura unificada estádiseñada de forma diferentepara garantizar que su ciberresiliencia esté preparada para el futuro. Ofrecemos la única plataforma de ciberresiliencia con portabilidad «any-to-any», lo que permite proteger cualquier dato, en cualquier ubicación, y recuperarlo desde cualquier lugar a cualquier otro. El resultado es una resiliencia sin igual para la empresa híbrida.

We also recognize that cyber resilience starts before an attack, and never stops. That’s why we built Commvault Cloud to enable customers to advance their security posture before an attack by understanding the risk of sensitive data, categorizing and remediating those risks, getting an early warning of attacks to minimize the impact, and enabling rapid recovery in the event of an attack.

We’re also revolutionizing cyber recovery with cutting-edge innovations as part of Commvault Cloud, like Cleanroom Recovery. This offering provides a clean, safe environment to perform full-scale recoveries at-scale to enable business resilience in the face of cyberattacks. Equally as important, we enable customers to test their recovery plans, closing the gap between incident response planning and recovery. With Cleanroom Recovery, you can have peace of mind knowing that your data is protected, and your operations can swiftly resume, allowing you to focus on what matters most: serving your customers’ needs.

Un ecosistema conectado

Los socios son fundamentales para Commvault Cloud. En la actualidad, contamos con integraciones con todos los principales proveedores de servicios en la nube, así como con los principales socios de integración de sistemas (GSI), de tecnología, de canal, de seguridad e inteligencia artificial. Commvault Cloud mejora a medida que se expande por el panorama de socios.

Apuesta por la seguridad con Commvault Cloud

When it comes to cyber resilience, there is no time for chaos. Commvault Cloud is the cure for chaos and we’re just getting started. Give us a try today: https://www.commvault.com/free-trial

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements