Skip to content

Every year on October 24, the world pauses for the International Day of Climate Action, reminding us that protecting the planet is no longer a choice, but a shared responsibility. Climate change isn’t coming – it’s here. And how we respond today will shape the future of our communities, our businesses, and our planet.

At Commvault, resilience is what we do – not just for data, but for the world we all share.

Sustainability: The Core of Resilience

Our mission to safeguard data goes hand in hand with our commitment to safeguard the environment. In FY25, we made meaningful progress toward our climate resilience goals:

  • Les émissions de scope 2 ont diminué de plus de 13 %, grâce à une utilisation plus intelligente de l’énergie et à l’efficacité des opérations des centres de données.
  • Emissions intensity fell from 12.7 to 9.6 metric tons CO₂e per million USD revenue, showing that growth and sustainability can move forward together.
  • Notre siège social certifié LEED continue d’être à l’avant-garde en matière d’intégration des énergies renouvelables, de systèmes économes en eau et de programmes de recyclage solides.

In everything from how we power our offices to how we design our technology, we consider sustainability a key driver of business continuity.

Data That Works for the Planet

The same innovation that drives Commvault’s cyber resilience is helping advance climate resilience.

By optimizing data storage, reducing redundancies, and improving workload efficiency, our cloud solutions enable customers to use less energy and achieve their own sustainability goals. Less waste. Lower energy use. More resilience.

Because when data works smarter, the planet breathes easier.

Collective Action, Shared Progress

We know climate action is not a solo mission. That’s why Commvault collaborates with partners who share our environmental values and participates in community initiatives like the Net Zero Institute to help accelerate the transition to a low-carbon economy.

We also align our climate governance with the Task Force on Climate-Related Financial Disclosures (TCFD), driving accountability from the top down.

From Awareness to Action

The path to a sustainable future begins with small, intentional choices, like turning off a light, optimizing a server, rethinking a commute. Every decision matters.

This International Day of Climate Action, let’s all take a step toward progress. Because resilience – whether in data, business, or the environment – is built together.

Aakanksha Kashyap est spécialiste ESG chez Commvault.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Points clés à retenir

  • As few as 250 poisoned samples can compromise a large AI model – turning your data lake into a prime attack surface.
  • Les échantillons empoisonnés peuvent implanter des portes dérobées qui persistent même après un réentraînement ou un réglage fin.
  • A practical defense centers on “protect, detect, roll back,” treating data protection as core to AI integrity.
  • Les sauvegardes, les ensembles de données versionnés et les restaurations granulaires permettent une récupération rapide vers un état propre et fiable.
  • Commvault + Satori ajoutent la découverte des données, le contrôle d’accès en temps réel, la surveillance des activités LLM et la politique unifiée avec restauration pour renforcer la résilience de l’IA.

I’ve been thinking a lot about Anthropic’s latest research – and it’s unsettling. It found that as few as 250 poisoned samples can compromise a massive AI model.
👉 [Read les résultats de cette recherche yourself.]

That’s right – a few hundred corrupted files can undo months of training and billions of parameters. Not thousands. Not millions. Just hundreds.

For anyone building or managing AI, this changes everything. Your AI data lake has become your primary attack surface – and if you can’t trust your data, you can’t trust your models.

💣 Small Samples, Big Consequences

Anthropic a démontré que :

  • Une poignée d’échantillons empoisonnés peut implanter des portes dérobées cachées.
  • Ces vulnérabilités peuvent persister malgré le réentraînement et le réglage fin.
  • Attackers don’t need to flood your system – they just need a foothold.

AI integrity isn’t only a model problem – it’s a data protection problem.

🧩 The Practical Defense: Protect. Detect. Roll Back.

Chez Commvault, nous constatons que les entreprises se précipitent pour mettre en placedes pipelines d’IA sans en sécuriser pleinement les fondations. When data is compromised, your best defense is the ability to roll back to a clean, trusted state.

That’s why backups, ensembles de données versionnés, et les restaurations granulaires deviennent aussi indispensables à l’IA que les GPU et les poids de modèles.

Commvault peut vous aider à :

  • Capturez des instantanés immuables de votre lac de données.
  • Restaurer une version connue pour être fonctionnelle.
  • Vérifier la lignée, la provenance et l’historique des modifications.
  • Verrouillez les sauvegardes contre toute altération (via le stockage WORM).

Because when it comes to AI, protection isn’t just about avoiding failure – it’s about being able to recover fast and clean when it happens.

🔐 The Power of Satori: Smarter, Safer AI Data

Satori faisant désormais partie de Commvault, nous proposons désormais des fonctionnalités plus étendues en matière de sécurité des données et de gouvernance de l’IA qui peuvent vous aider à :

  • Détectez automatiquement les données sensibles dans les clouds, les entrepôts et les lacs de données.
  • Control access in real time – who sees what, when, and how.
  • Surveillez l’activité de l’IA et du LLM afin de détecter rapidement les anomalies.
  • Unify policy and rollback – restoring data and supporting compliance from one place.

Ensemble, Commvault et Satori fournissent des capacités de base de données résilientes et intelligentes qui permettent de détecter, protéger et récupérer les données face aux menaces liées à l’évolution de l’IA.

🚀 The Future of AI Resilience

This is exactly what we’ll be discussing at Commvault Shift | Virtual – how to secure, protect, and recover the data that drives AI.

Join us to hear from industry leaders about building trusted, resilient AI systems that can help withstand data corruption, cyber threats, and human error.

👉 Register here: commvault.com/SHIFT-VirtualProtégez votre IA. Protégez vos données. Bâtissez un avenir plus résilient.

FAQ

Q: What does “250 poisoned files” actually mean for my models?
A: The blog cites Anthropic’s finding that only a few hundred corrupted samples can meaningfully compromise a massive model – no flood required. It highlights that attackers need only a small foothold to degrade behavior or implant triggers.

Q: Why might retraining fail to remove poisoning?
A: Some backdoors survive standard retraining and fine-tuning because the malicious signal is subtle and reinforced by the broader dataset. The result is a model that behaves normally until a hidden trigger appears.

Q: What immediate defenses should we prioritize?
A: Adopt a “protect, detect, roll back” strategy: Secure your data pipeline, monitor for anomalies, and maintain the ability to revert to a known-good state. Treat data protection as foundational – on par with model weights and GPUs.

Q: How do backups and versioned datasets help in practice?
A: Immutable snapshots, version history, and fine-grained restores enable you to quickly recover clean data, verify lineage and provenance, and continue operations without carrying hidden compromises forward.

Q: What additional value does Satori bring with Commvault?
A: Satori expands capabilities with automatic discovery of sensitive data across clouds and lakes, real-time access control, LLM activity monitoring for early anomaly detection, and unified policy plus rollback to support compliance and recovery.

Q: Isn’t model security enough without data protections?
A: Model-centric controls are necessary but incomplete. The post argues that AI integrity is as much a data protection problem as a model problem; without trusted data, even well-secured models can be subverted.

Thomas Bryant est directeur principal du marketing produit chez Commvault.

Blogs connexes :

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

La deuxième édition deL’état de Readiness des données en AsieCe rapport, un rapport complet réalisé par Tech Research Asia à la demande de Commvault, offre un aperçu saisissant des défis et des réalités auxquels sont confrontées les organisations à travers le continent. Basé sur une enquête menée auprès de 1 218 entreprises en Indonésie, à Hong Kong, en Corée, en Malaisie, aux Philippines, à Singapour, en Thaïlande et au Vietnam, le rapport révèle les tendances critiques en matière de croissance des données, de pressions réglementaires, d’adoption de l’IA et de cyber-résilience.
Voici quelques-uns des points clés qui méritent l’attention des dirigeants d’entreprise et des responsables informatiques :

Croissance sans précédent des données et complexité croissante des infrastructures

Les parcs de données connaissent une croissance accélérée.

  • L’entreprise typeAu cours des 12 derniers mois, les données asiatiques ont vu leurs données augmenter de 40 %, soit une hausse significative par rapport aux 31 % enregistrés l’année précédente.
  • Cette explosion de données, dont 66 % sont non structurées, réside dans des environnements de plus en plus complexes.
  • Une majorité d’entreprises (63 %) opèrent désormais dans cloud cloud hybrides, créant ainsi un écosystème tentaculaire et interdépendant, difficile à gérer et à sécuriser.
  • Cette complexité a des conséquences néfastes, 38 % des organisations admettant qu’elles ne sont pas sûres de pouvoir rétablir leurs activités après une violation.


Le paradoxe de l’IA : une adoption élevée malgré un risque élevé

L’IA connaît un essor fulgurant : 74 % des entreprises asiatiques utilisent actuellement des solutions d’IA destinées aux entreprises. Cependant,on a une vision lucide des risques encourus.

  • Cette complexité a des conséquences néfastes, 38 % des organisations admettant qu’elles ne sont pas sûres de pouvoir rétablir leurs activités après une violation.
  • Pas moins de 73 % de ces organisations estiment que le déploiement de l’IA augmente le risque de violation de la cybersécurité.
  • Malgré cette prise de conscience, la diligence raisonnable fait défaut. Il est préoccupant de constater que 58 % des organisations n’ont pas procédé à des audits de sécurité approfondis de leurs outils d’IA avant leur déploiement, et moins de la moitié (46 %) ont mis en place des politiques complètes pour protéger les données générées par l’IA.

The Tangled Web of Regulations

The regulatory landscape across Asia is becoming increasingly intricate and, at times, contradictory.

  • Exigences contradictoires : 53 % des organisations déclarent être confrontées à des exigences réglementaires contradictoires concernant leurs données dans différentes zones géographiques.
  • Charge réglementaire : 52 % des entreprises doivent se conformer à au moins quatre lois réglementaires majeures.
  • Conformité en matière d’IA : le défi est aggravé par les réglementations spécifiques à l’IA, auxquelles près de 60 % des entreprises sont désormais soumises et auxquelles 27 % supplémentaires s’attendent à être soumises dans l’année à venir.

La triste réalité des cyberattaques et de la reprise après sinistre

There remains a significant disconnect between the expectations of business leaders and the reality of IT recovery after a cyber incident. While 72% of business leaders expect to be back in business within five days of an incident, the reality is that 70% of businesses take more than a week to recover.
The report also sheds light on the direct impacts of attacks:

  • Parmi les entreprises qui ont été victimes d’une violation, 83 % ont subi une exfiltration de données.
  • Moins de la moitié (41 %) ont réussi à récupérer 100 % de leurs données.
  • Alors que 57 % des entreprises ont une politique interdisant le paiement de rançons, 34 % de celles qui ont une telle politique ont payé la rançon lorsqu’elles ont été attaquées.

Apprendre à la dure

Interestingly, organisations that have experienced a breach demonstrate a more mature and realistic understanding of their capabilities. They are more likely to have comprehensive incident response plans and a clearer grasp of the complexities involved in recovery. For instance, breached companies are almost twice as likely to view their internal AI tools as a high cybersecurity risk compared to those that have not been breached.
To gain a deeper understanding of these findings and benchmark your organisation against your peers, download the full État de Readiness des données en AsieRapport. Le rapport complet propose une analyse détaillée, des données spécifiques à chaque pays et des recommandations concrètes pour vous aider à améliorer vos stratégies de gestion des données, de Recovery et de cyber-résilience, afin d’assurer la continuité de vos activités.

More related posts


Cyber Resilience

Read more about Cyber Resilience

Cyber Security

Read more about Cyber Security

In conversations with three Chief Medical Information Officers across different healthcare systems, each was asked about their most recent cybersecurity incident. The answer was unanimous and telling: None had experienced a direct attack on their own systems. Instead, all three were grappling with the aftermath of third-party vendor breaches that cascaded through their operations.

This isn’t coincidence – it’s the new reality of healthcare cybersecurity.

The Vendor’s Vendor Problem

“We are big enough to have these experts on staff that are our experts to protect us,” one CMIO explained. “Sometimes I feel that that can be a barrier to agility because of how strict we are and how thorough we are in those evaluations. But I think that we can’t ensure that our partners do the same.”

Here’s the challenge: Healthcare organizations have become incredibly sophisticated at vetting direct vendors. The contracting process is rigorous, security assessments are thorough, and compliance requirements are non-negotiable.

But what happens when your vendor makes a deal with another vendor? Suddenly, you’re exposed to risks you never evaluated, from companies you’ve never heard of, through relationships you don’t control.

One security leader illustrated this perfectly: “I’m going to make a deal to use Vendor X to do something for me here. But Vendor X may make a deal with Vendor Y that lets them do their job. So if there’s a problem with Vendor Y who I’m not technically contracted with, but my vendor needs them to function, I can’t control that.”

When the Ecosystem Fails

LeChange Healthcare incident provides a stark example. When its systems went down due to a cyberattack, it wasn’t just Change Healthcare that suffered – it was every healthcare organization that relied on its prescription processing services.

One CMIO described the impact: “We had a lot of issues sending prescriptions, receiving them, having issues being unclear of what went through, what didn’t go through, and who didn’t have their medications.”
Ledownstream clinical impact was immediate and severe. Patients couldn’t get medications, providers couldn’t verify prescription statuses, and healthcare teams scrambled to identify which patients might be affected. This was a direct patient safety issue caused by a vendor incident completely outside the control of healthcare providers.

But the clinical impact was just the beginning. The compliance implications were equally severe, highlighting a fundamental challenge in healthcare’s regulatory landscape.

The Compliance Trap: When Vendor Failures Become Your Regulatory Problem

Healthcare organizations face a harsh regulatory reality: Vendor incidents don’t absolve them of compliance responsibilities. In fact, they often amplify them.

HIPAA requires covered entities to establish Business Associate Agreements with vendors handling protected health information. While these agreements theoretically transfer some liability, the practical reality is different. When a vendor suffers a breach, the healthcare provider still faces potential penalties, regulatory scrutiny, and mandatory reporting requirements.
Lereporting burden alone creates significant operational strain. HIPAA’s proposed 72-hour reporting mandates, similar to regulations like EU NIS2 and DORA for cross-border institutions, require healthcare providers to disclose incidents quickly, regardless of whether the breach originated from their own systems or a vendor’s.

As one CMIO noted: “We actually have to communicate to the state, to the Centers for Medicaid and Medicare Services: ‘This is what’s going on. This is where we are with our recovery.’”

This means that during an active incident – when clinical teams are scrambling to maintain patient care and IT teams are coordinating recovery efforts – compliance teams must simultaneously investigate, document, and report on incidents they didn’t cause and may have limited visibility into.
Ledata sovereignty challenge adds complexity. Vendors storing healthcare data outside approved regions can trigger compliance violations that organizations may not even know exist until an incident forces a comprehensive audit of their vendor ecosystem.

“We require [vendors] to give us anything and everything we asked for to review,” explained one security leader who’s experienced a vendor ransomware attack. “So, there was actually no limitations on what we could ask.”

But this level of oversight is typically only possible with the largest vendor relationships, leaving many smaller but still critical vendor dependencies in compliance blind spots.

The CrowdStrike Wake-Up Call

LeCrowdStrike incident drove home another reality: When critical infrastructure providers fail, the entire healthcare ecosystem fails simultaneously.

“We did [tabletop exercises] with the assumption that it would be a ransomware attack… a very kind of localized event,” one leader reflected. “And this was affecting the entire ecosystem. And that’s where we [learned] that we needed to have more resiliency practices that would incorporate where the ecosystem itself would be widely affected.”
Lechallenge wasn’t just technical – it was operational and regulatory. When everyone is down at once, the usual backup plans (like calling vendors for support or switching to alternate providers) simply don’t work.

Healthcare organizations faced not only interrupted patient care and massive downtime costs but also complex compliance reporting requirements for an incident that originated entirely outside their control.

Beyond Traditional Risk Assessment

Healthcare organizations are discovering that their traditional approach to vendor risk management isn’t enough. The standard process – sending questionnaires, reviewing documentation, checking compliance certifications – only covers direct relationships.

But post-incident, the conversation is changing. Instead of just asking “Do you do this? Do you do that?” organizations are demanding to see exactly how vendors execute security and recovery plans. They’re asking for evidence of testing, requiring contractual rights to review sub-vendor relationships, and building in financial protections.

The New Vendor Relationship Model

Forward-thinking healthcare organizations are taking several concrete steps to address ecosystem risk:

  • Data sovereignty: “We want to start taking more ownership over the data… so that we have something we can rebuild or even switch over to another third party if possible,” one leader said.
    Rather than letting vendors hold all the data, organizations are requiring regular data exports and maintaining their own copies of critical information. This approach helps address data residency requirements and enables compliance continuity even when vendors fail.
  • Enhanced contractual evolution: Post-incident contract negotiations now address compliance obligations explicitly. Organizations are demanding notification timelines that meet regulatory requirements, recovery guarantees that minimize downtime costs, and financial compensation for both direct losses and compliance penalties resulting from vendor-caused outages.
  • Compliance-aware update management: The CrowdStrike incident highlighted how vendor updates can create both operational and compliance risks. Many organizations have implemented “two versions behind” policies for critical security updates, balancing the risk of delayed patches against the risk of compliance violations from untested updates that could cause widespread outages.
  • Regulatory integration in vendor management: Organizations are building compliance considerations directly into vendor evaluation and ongoing oversight. This includes knowing vendors can meet the same 72-hour reporting requirements, maintain appropriate data residency, and provide the documentation needed for regulatory reporting.

The Insurance Industry’s Perspective

Perhaps most telling is how the insurance industry views these risks. As one security leader shared from a colleague in insurance risk modeling: “The number one risk that we have is the kind of outage like CrowdStrike, where we’re so dependent upon these technology platforms that when we’re out, there’s massive disruptions in services and in operations. She says that’s the number one risk in our risk model. It’s not ransomware attacks.”

This shift in risk assessment reflects a fundamental change. Traditional cybersecurity focused on preventing bad actors from getting in. Modern cybersecurity also must address the reality that critical vendors – with the best of intentions and strong security practices – still can bring down entire ecosystems through operational failures.

The Minimum Viability Challenge in an Ecosystem World

Traditional recovery planning often assumes you can restore everything systematically, but when entire ecosystems fail simultaneously, organizations must focus on minimum viable recovery (MVR).
Leconcept of minimum viability becomes critical when your vendors, their vendors, and potentially your backup vendors are all affected. As we’ve explored in our analysis of healthcare cyber threats and MVR, the question isn’t just “How do we recover everything?” but “What are the bare essentials we need to keep patient care running while the ecosystem rebuilds itself?”

This ecosystem reality makes organizational recovery readiness more complex than ever. When you can’t rely on your usual vendors or backup providers, your MVR plan must account for true independence from the broader ecosystem – at least temporarily.

Moving Forward

Organizations can’t just secure their own perimeter; they need to understand and plan for the interconnected web of dependencies that modern healthcare relies on. This means fundamentally rethinking business continuity planning to account for simultaneous ecosystem failures. It means maintaining data sovereignty even when using SaaS providers. And it means accepting that some risks simply can’t be eliminated – only managed and planned for.
Lehealthcare leaders we spoke with weren’t pessimistic about these challenges; they were pragmatic. They understand that the benefits of interconnected, cloud-based healthcare systems far outweigh the risks.

Test Your Ecosystem Resilience

Understanding the risks is just the first step. The next is honestly assessing whether your organization is prepared for the new reality of interconnected failures. How confident are you that your MVR plan would work when your usual vendors and backup systems also are compromised?

Healthcare organizations serious about ecosystem resilience should evaluate their readiness across three critical areas: business-critical prioritization, measurable technical response, and organizational recovery readiness. Commvault’s Minimum Viability Healthcare Assessment helps evaluate your current capabilities and offers actionable recommendations for closing any gaps.

Don’t wait for the next ecosystem-wide incident to discover whether your recovery plans account for the reality of interconnected healthcare IT. Take the assessment today and build true resilience for tomorrow’s challenges.


Blogs connexes :

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

A powerful go-to-market strategy is what separates leaders from the pack in the competitive cyber resilience market. At Commvault, we’re dedicated to providing our partners with the strategic resources needed to help grow revenue, build customer trust,etsolidify your reputation as a market leader with Commvault.
That’s why we are excited to announce two game-changing resources designed to elevate your salesetmarketing efforts: a reimagined Centre des campagnes Commvaultrepensé et les nouveauxguides de vente pour partenaires At-A-Glance.

Optimisez votre marketing grâce au centre de campagnes

Based on partner feedback, our newly imagined Campaigns Hub is your destination for ready-to-use, results-driven marketing. The Campaigns Hub is a powerful, intuitive platform that simplifies the creation of targeted campaigns, helping you build awareness, generate leads,etupsell Commvault’s suite of solutions. And now our platform integrates seamlessly with your existing strategies, enabling cohesive brand messagingetmaximum impact.
With the Campaigns Hub, you’ll find:

  • Targeted campaigns you can launch in minutes. Choose from a library of pre-built multi-language campaigns – from “Securing Continuity for Minimum Viable Business” to “Microsoft Active Directory Protection” –etcustomize the content to fit your audience’s unique needs.
  • A new, powerful webcast program. Leverage Commvault’s best speakersetcontent directly from the Campaigns Hub using our on-demand webcasts along with the promotional materials to drive leadsetawareness.
  • A new, co-branded assessment tool. Contact our Marketing Conciergeetrequest a co-branded minimum viability assessment tool that provides benchmarks to your customers in minutesetputs leads directly in your inbox.  
  • High-value customer assets to use on your platform or the hub. You can now access key Commvault customer contentetpromotional campaigns through the Campaigns Hubetintegrate these valuable assets into your broader marketing initiatives on the hub, or downloadetuse on your platform.
  • Our complimentary Marketing Concierge service that makes campaigns even easier. You don’t need to use MDF or pay for our Marketing Concierge service to help you customizeetrun the latest Commvault campaigns to grow your business. Try out the service with a session d’activation de campagne individuelle.

Boostez vos ventes grâce à des guides pratiques faciles à consulter

To complement your marketing efforts, Commvault also has launched our new guides de vente pour partenaires At-A-Glance. We’ve condensed our most popular les guides de vente pour les partenaires into a concise, easy-to-use one-page format, packed with the essential tools you need to articulate valueetenhance customer engagement.
Each playbook includes:

  • Concise call scripts: Confidently articulate the unique value propositions of Commvault’s productsetsolutions.
  • Objection handling: Turn potential roadblocks into opportunities with prepared responses to common customer challenges.
  • Customer-ready materials: Accelerate sales cycles by sharing curated whitepapers, solution briefs, case studies, eBooks,etmore.

By combining the power of the Centre des campagnes Commvault with the strategic guidance of the At-A-Glance Sales Playbooks, you can create impactful, end-to-end campaigns that drive customer engagementetachieve greater sales success.

Libérez votre potentiel avec Commvault

Ready to transform your go-to-market strategyetmaximize the value of Commvault’s offerings? Explore the Centre des campagnes Commvaultetles guides de vente pour les partenairessur le portail des partenaires. Lancez-vous par vous-même ou planifiez unesession d’activation de campagne individuelleavec notre « Marketing Concierge » gratuit pour bénéficier d’un accompagnement personnalisé.

More related posts


Cyber Resilience

Read more about Cyber Resilience

When cyber attackers strike, speed isn’t everything. Restoring quickly from compromised data simply reintroduces the threat, creating a vicious cycle of infection and reinfection.

I recently wrote a whitepaper with my colleagues fromKyndryltitled,Redéfinir la reprise après incident informatique : présentation du « Mean Time to Clean Recovery » (MTCR) where we introduced a fundamental shift: measuring how fast you can restore from clean, verified data rather than just any available backup.

Here are the five critical steps that determine your organization’s MTCR:


  1. Establish a clean environment to recovery into.

The problem: Recovery to an infected infrastructure will simply reinfect your restored systems.

The solution: Isolated Recovery Environments (IREs) or cleanrooms – compute and storage infrastructure physically or virtually separated from production environments where attackers never had access.

Reality check: Without an IRE, modern forensic teams need 24 to 72 hours to certify complex hybrid environments as “clean.” Your MTCR automatically becomes measured in days, not hours.


  1. Find clean data to recover from.

The hidden threat: Modern attackers operate in stealth for weeks before launching attacks, seeding malicious payloads throughout your environment – including backup systems.

The breakthrough: Automated scanning for Indicators of Compromise can help identify clean backup sets without the trial-and-error cycle of testing each backup until you find one that works.

Collaboration required: This step demands tight integration between SysOps teams (who manage backups) and SecOps teams (who understand current threats). Forensic analysis reveals attack signatures that must be fed into the scanning process.


  1. Recover data in acceptable time.

The uncomfortable truth: Enterprise backup solutions often deliver “10+ hours per terabyte” recovery performance. Scale this to typical enterprise services requiring hundreds of terabytes, and you’re looking at weeks of recovery time.

The reality: Most backup infrastructure was designed for nightly incremental backups (5% data change), not full-scale business restoration (100% recovery).

The solution: Purpose-built cyber resilience platforms with high-performance recovery capabilities, combined with minimum viable company (MVC) prioritization – focusing on the critical 20% of services that enable 80% of business function.


  1. Maintain data integrity across the platform.

The challenge: Enterprise systems don’t exist in isolation. During recovery, systems restored from backups taken at different times create data integrity nightmares.

Example scenario:

  • Customer database: Tuesday 3 a.m. backup
  • Billing system: Monday 11 p.m. backup
  • Inventory system: Wednesday 6 a.m. backup

Result: Orders for customers who don’t exist, invoices for products not in inventory.

The Process: Restoration sequencing based on dependencies, data reconciliation across integrated systems, and comprehensive consistency checks before production return.


  1. Test before production return.

The rush trap: Under pressure, IT teams often rush systems back online without comprehensive testing, leading to partially functional systems or reintroduction of attack remnants.


Comprehensive validation:
  • Functional testing of core business processes
  • Security validation through vulnerability scanning
  • Data integrity verification across platforms
  • Business process validation by application teams

Critical success factor: Pre-define your MVC acceptance criteria – the specific functionality that must work before you’re truly “recovered.”


The Integration Challenge

These aren’t sequential steps – they’re interconnected capabilities that must work together. Your MTCR is only as fast as your slowest step and only as reliable as your weakest validation point.

The investment reality: Clean recovery requires purpose-built cyber resilience platforms, isolated recovery environments, automated scanning tools, and dedicated recovery networks. But the cost of prolonged downtime and reinfection is far greater.


Next steps:
  1. Assess how long each step would take in your current environment.
  2. Identify your biggest gap.
  3. Calculate the cost of extended downtime vs. infrastructure investment.
  4. Start with your most critical business services.

The era of “backup and pray” is over. Organizations that master these five steps don’t just recover faster – they recover once, cleanly, and with confidence.


En savoir plus

Watch as I discuss this new metric in the webinar,The Missing Metric for Cyber Recovery Success.

Read the full whitepaper,Redéfinir la cyber-Recovery : présentation du « Mean Time to Clean Recovery » (temps moyen de récupération complète), for more about this critical metric.Darren Thomson is a Field CTO at Commvault. Be sure to catch him in the podcast series, STRIVE.

More related posts


CleanroomRecovery_Thumbnail_888x500

Commvault Cleanroom

Read more about Commvault Cleanroom

La cinquième édition du rapport «State of Data Readiness in ANZ», un rapport Tech Research Asia Insights commandé par Commvault, offre un regard critique sur le paysage actuel de la gestion des données, de la cybersécurité et des pressions réglementaires auxquelles sont confrontées les organisations en Australie et en Nouvelle-Zélande (ANZ). S’appuyant sur une étude menée auprès de 408 entreprises de la région, ce rapport met en lumière les principales tendances et les réalités frappantes concernant la manière dont les entreprises font face à un environnement numérique de plus en plus complexe. Étant donné que nous examinons souvent les résultats d’études à l’échelle mondiale, il est particulièrement utile de disposer d’une perspective locale sur la Readiness des données. Si les taux de croissance des données ont légèrement ralenti, les défis liés à la gestion, à la sécurité et à la récupération des données se sont intensifiés. Voici quelques-unes des conclusions marquantes du rapport.

L’environnement réglementaire et les données : un enchevêtrement complexe

Les organisations sont confrontées àdes volumes de données toujours plus importants et à un cadre réglementaire de plus en plus strict.

  • Slowing growth, persistent sprawl: The annual data growth rate in ANZ has marginally slowed from 28% last year to 27% this year. A majority, 62%, continue to operate in blended (multi- or hybrid cloud) data environments, and this is projected to increase to 71% by 2026.
  • Confidence gap: A concerning number of organisations lack confidence in their ability to restore business operations after a breach, with 54% of Australian and 63% of New Zealand businesses feeling unprepared.
  • Regulatory complexity: The regulatory landscape is becoming more difficult to navigate. Fifty-five percent of Australian and 53% of New Zealand companies are now required to maintain data copies in separate cloud environments for resiliency. Furthermore, more than a third of organisations face conflicting data regulations across different geographies.
  • The rise of AI regulation: AI-specific compliance is a growing concern, with 28% of companies already subject to such regulations and another 40% expecting to be within the next year.

Le paradoxe de l’IA : une adoption élevée malgré un risque élevé

L’enthousiasme pour l’IA est grand,yet it’s coupled with significant security concerns.

  • Risk vs. reward: While 73% of ANZ organisations are using business-focused AI solutions, 68% of them believe this adoption increases the likelihood of a cybersecurity breach.
  • Lack of due diligence: A significant 63% of organisations admitted to not conducting thorough and extensive security audits of their AI tools before deployment.
  • Policy deficit: Only 29% of companies have comprehensive policies in place to protect the data and content generated by AI solutions.

Reprise : un décalage entre les attentes et la réalité

The gap between business leaders’ recovery expectations and the on-the-ground reality for IT teams remains a major issue.

  • The expectation-reality gap: Eighty percent of business leaders expect to recover from a cybersecurity incident within five days. However, the stark reality is that it takes an average of four weeks to restore a minimal level of business operation.
  • Ransomware’s reach: Seventy percent of ANZ organisations have received a ransomware demand, and of those, 20% admitted to paying it. Interestingly, of the companies with a stated “no payment” policy, 15% still ended up paying the ransom when faced with an actual attack.
  • The power of experience: The report reveals a fascinating insight: Experience is a harsh but effective teacher. Companies that have been breached are 1.5 times more likely to conduct thorough reviews of AI tools and twice as likely to test all mission-critical workloads as part of their incident response plans. Conversely, companies that have not been attacked are 1.5 times more likely to believe they can recover within a single day.

The 2025 State of Data Readiness report underscores a challenging environment for ANZ organisations. From regulatory hurdles to the double-edged sword of AI and the persistent disconnect in recovery expectations, the path to true cyber resilience is complex.To gain a deeper understanding of these findings, download the full report.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

I’m thrilled to share that we were just announced as a winner in Udemy’s Learning Excellence Awards 2025dans la catégorie « Leading With Learning Science ». Dans le cadre de ce programme de récompenses, Udemy a distingué les organisations qui ont obtenu des résultats significatifs en matière d’apprentissage et de développement grâce à la mise à niveau des compétences soutenue par l’IA. En tant que l’un des lauréats dans la catégorie « Leading With Learning Science » (Diriger grâce à la science de l’apprentissage), Commvault a été récompensé pour avoir donné la priorité à l’intégration de l’apprentissage dans le flux de travail, pour avoir suscité l’intérêt des apprenants grâce au micro-apprentissage et pour avoir conçu des expériences d’apprentissage personnalisées.

Nous sommes honorés de figurer sur une liste de leaders visionnaires qui transforment l’apprentissage à grande échelle et donnent à leurs employés les moyens de prospérer dans un avenir axé sur l’IA.

L’investissement dans notre personnel est important

Over the past year, we’ve expanded on our investment in learning and development by implementing an all-new, comprehensive learning platform, Pathfinder, to provide our Vaulters with the tools, resources, and opportunities they need to enhance their skills and advance their careers.

Our new platform has a wealth of learning modules, ranging from live instructor led sessions to on-demand and self-paced learning modules, including Udemy Business’ 30,000+ expert-led courses covering topics across technology, business, leadership, productivity, cybersecurity, and GenAI. Udemy Business isn’t just another online training tool – it’s a strategic driver of capability building within Commvault, and we’re delighted to offer our global Vaulter community access to Udemy Business.

We’ve also developed curated learning paths tailored for our teams, with a focus on the power of AI. The development of our Vaulters is key to Commvault’s success, and with Udemy Business, we’re giving them the tools to build their future growth, all while harnessing the potential of AI.

To learn more about what it’s like to work at Commvault, cliquez ici.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

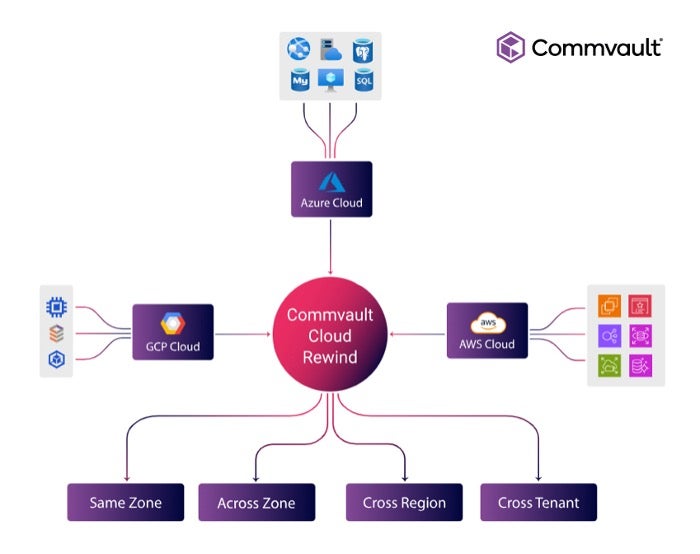
La transition mondiale vers les architectures cloud a redéfini ce que signifient la sécurité et la résilience. Cloud sont dynamiques par nature : les ressources sont fréquemment mises à jour, ajoutées ou supprimées ; les applications s’étendent sur plusieurs régions et plusieurs clouds ; et l’infrastructure évolue plus rapidement que la plupart des outils de récupération ne peuvent le suivre. Les modèles de sauvegarde traditionnels, conçus pour des systèmes statiques, ont du mal à suivre ce rythme et cette complexité.Commvault Cloud Rewind™ is built from the ground up to handle this new reality. With an architecture purpose-built for cloud-scale recovery, Cloud Rewind helps you restore entire cloud environments, including applications and their dependencies, with ease.

This becomes essential in modern environments where applications are composed of microservices, containers, and serverless components that are often ephemeral and spread across multiple platforms.

Resources may change daily, and ownership is often decentralized across teams. Configuration drift, inconsistent change management, and the growing use of third-party services all make recovery harder. Even when manual backups are available, critical infrastructure metadata is often missing, making restorations unreliable or incomplete.

In this ecosystem, Cloud Rewind brings order to the chaos. By leveraging ongoing discovery, orchestration, and cloud-native operations, it provides fast and consistent recoverability. Whether you’re dealing with a simple misconfiguration or a full-blown cyberattack, Cloud Rewind helps restore critical resources in minutes.

A Deep Dive Into the Design: The Cloud Rewind Architecture 

Au cœur de Cloud Rewind des principes architecturaux clés qui privilégient l’automatisation, l’évolutivité et la précision de la récupération. À partir de cette base, il permet une approche intégrée pour aider à découvrir, protéger, récupérer et reconstruire des applications et des données dans cloud . Cloud Rewind des fonctionnalités puissantes pour renforcer la cyber-résilience et simplifier la reprise dans cloud . Chaque fonctionnalité joue un rôle essentiel dans l’amélioration de la confiance dans les opérations quotidiennes et la réponse aux crises.

  • Cloud et cartographie des dépendances : Cloud Rewind détecteRewind toutes cloud pertinentes et capture les métadonnées nécessaires à une restauration précise et reproductible. Cela inclut les paramètres de configuration complets, les dépendances et les détails de l’infrastructure.
  • Analyse des dérives : Cloud évoluent rapidement. Cloud Rewind ces changements grâce à une analyse régulière des dérives, en comparant les configurations actuelles aux états protégés connus. Les équipes de sécurité sont ainsi informées de tout écart par rapport aux configurations attendues, ce qui permet de maintenir une cohérence essentielle.
  • Reconstructions quotidiennes automatisées dans le cloud : il ne suffit pas de revenir à un état sûr ; cela doit être fait rapidement et sans erreur. Cloud Rewind y contribue grâce à des tests de Recovery automatisés. Vous pouvez reconstruire des infrastructures cloud, des applications et des données dans leur intégralité à l’aide d’environnements à la demande. Ces environnements temporaires peuvent ensuite être supprimés afin de réduire les coûts liés aux tests.
  • Integrated cyber recovery: Cloud Rewind works with Commvault’s broader data resilience platform, effectively combining backup, recovery, and threat intelligence. This unified approach provides better control and coordination during security incidents, helping teams move from detection to full recovery with speed and clarity.

Conquérir la concurrence : ce quiRewind Cloud Rewind

Avec une multitude de fonctionnalités avancées adaptées aux organisations modernes cloud, Cloud Rewind une récupération efficace et simplifiée. Alors que plusieurs solutions industrielles offrent une simple reprise après sinistre pour cloud , ces capacités permettent à Cloud Rewind . Cloud Rewind la résilience de la récupération à un niveau supérieur grâce à :

  • cloud étendue, avec prise en charge native d’AWS, Azure et GCP.
  • Couverture complète des ressources, y compris le calcul, le stockage, la mise en réseau, l’IAM, le DNS, les conteneurs et les services sans serveur.
  • Protection détaillée des métadonnées d’infrastructure, à l’aide d’une machine à remonter le temps à double coffre-fort.
  • Graphiques explicites des dépendances des applications, et pas seulement une connaissance au niveau des ressources.
  • Recovery-as-Code, pour une reprise orchestrée et pilotée par le code.
  • Validation continue, à l’aide de reconstructions automatisées régulières dans cloud isolés.
  • Faible charge opérationnelle et grande transparence grâce à un modèle SaaS .

Cloud Rewind protection, intelligence et automatisation pour prendre en charge une récupération rapide et fiable dans cloud complexes. Cela permet à Cloud Rewind démarquer dans un domaine concurrentiel et de rester en tête.

Cloud pour une récupération complète Cloud

Commvault Cloud Rewind is built for full-stack cloud resilience, offering protection for modern, cloud-native workloads. Instead of simply backing up isolated resources, capturing and recovering entire cloud applications, referred to as Cloud Assemblies.

Cloud Rewind supports a wide range of cloud-native services, including virtual machines, disks, gateways, security groups, VPCs, DBaaS platforms, and containerized workloads. Once a cloud connection is established, Cloud Rewind performs automated identification of all resources in an environment. At scale, this can be highly significant. For one Commvault customer, 94,237 resources were discovered, with 7,811 protected resources organized into 19 distinct assemblies.

For complete protection, customers can begin with the definition of policies tailored to their Cloud Assemblies. These policies govern snapshot frequency, retention rules, and replication preferences. Snapshots can be taken as frequently as every 15 minutes or as infrequently as annually, depending on the workload’s recovery objectives. These snapshots can be used for rapid, point-in-time backups and fast rehydration.

With its sophisticated use of only cloud snapshots, Cloud Rewind offers protection at a fraction of the cost of expensive traditional high-availability or read‑replica architectures. As dedicated standby infrastructure isn’t required, customers pay only for snapshot storage and temporary compute during recovery operations. This flexibility allows customers to effectively fine-tune protection schedules to balance RPO requirements against storage costs.

Finally, Cloud Rewind provides cloud data resilience by performing recovery at the Cloud Assembly level. When it’s time to restore, Cloud Rewind can recreate the complete application, including the resource configurations, network settings, and dependencies, exactly as it existed at any point in time. Recovery also can target the original region for a quick rollback or be redirected to a different region, subscription, or project to support disaster recovery use cases.

By centering recovery around customer applications, Cloud Rewind replaces traditional complexity with invaluable clarity. With automated discovery, flexible policies, and cost‑effective snapshot-based protection, Cloud Rewind can help customers meet stringent recovery objectives while minimizing infrastructure overhead.

Une nouvelle ère de résilience : les principaux avantages du Cloud Rewind

Cloud Rewind introduces a new standard for resilience in the cloud, shifting away from legacy disaster recovery models toward an approach designed for dynamic, modern environments. By focusing on full application recovery instead of isolated resources, it helps avoid downtime, reduce operational risks, and support rapid, coordinated recovery and restoration across cloud platforms.

One of its core innovations is the patented dual-vault cloud time machine. This unique approach protects  immutable vaults in different hyperscale clouds for rapid application recoveries. This design not only defends against failures and cyber threats but also enables precise, point-in-time recovery of entire application environments.

With a myriad of powerful capabilities that support the growth of modern businesses, Cloud Rewind makes an impact:

  • Les entités de services financiersexploitent Cloud Rewind vous aider à respecter les exigences réglementaires strictes tout en minimisant les temps d’arrêt des systèmes financiers en temps réel.
  • Les organismes de santéutilisent Cloud Rewind vous aider à récupérer rapidement les dossiers médicaux électroniques et autres applications critiques lors d’incidents cybernétiques, évitant ainsi toute interruption des soins prodigués aux patients.
  • Dans lesecteur de l’éducation, Cloud Rewind un filet de sécurité qui permet de se prémunir contre la perte de didacticiels, de données sur les étudiants et d’autres ressources.
  • Les entreprises de vente au détail et de fabrication utilisent Cloud Rewind se remettre rapidement des pannes ou des cyberattaques, ce qui leur permet de minimiser les pertes de revenus et de respecter leurs calendriers de production.
  • SaaS de technologies et SaaS utilisent Cloud Rewind vous aider à protéger les plateformes cloud et à fournir un service continu à vos clients.

Dans tous les secteurs, Cloud Rewind des résultats mesurables. Ainsi, des cas concrets d’organisations tirant profit de cette solution innovante ont rapidement vu le jour. SaaS deSystèmes Pragya’ SaaS resiliency increased by a staggering 300% with Cloud Rewind. Similarly, backed by the powerful capabilities of Cloud Rewind, an leader du secteur de l’eDiscoverya pu se remettre d’une ransomware majeure ransomware.

Dans le secteur des services financiers, unimportant organisme de crédit hypothécaire decreased cloud application resilience cost by 85% with Cloud Rewind. Finally, leveraging Cloud Rewinds’ app-centric BCDR approach, a global cloud solutions provider achieved a 99.9% cloud app resilience SLA.

Cloud comme jamais auparavant

Commvault Cloud Rewind un tournant dans la manière dont les entreprises abordent la résilience. Au lieu de s’appuyer sur des outils fragmentés ou des processus de récupération rigides, Cloud Rewind une architecture cloud qui s’adapte au rythme des changements. Grâce à une automatisation poussée, une récupération centrée sur les applications et des résultats éprouvés dans tous les secteurs, il permet aux entreprises de protéger ce qui compte, de récupérer plus rapidement et de fonctionner en toute confiance.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

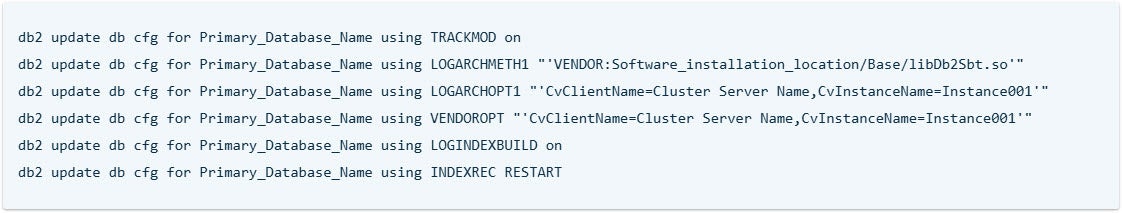
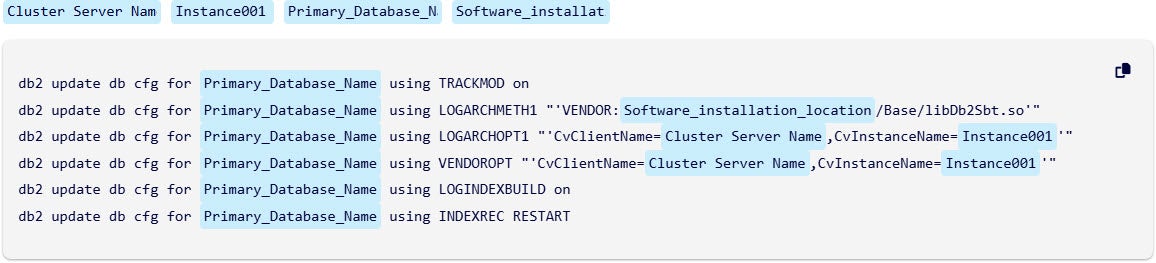
La plupart des sites web de documentation d’entreprise qui comportent des blocs de code utilisent des styles indiquant qu’il s’agit de marques de position. L’intention est censée être claire,et les lecteurs sont censés savoir ce qu’ils doivent modifier,mais l’expérience n’est pas à la hauteur.Ces mêmes styles sont également utilisés pour mettre en évidence des éléments,des libellés d’interface utilisateur ou la syntaxe à d’autres endroits de la documentation. Parmi les marques de position couramment utilisées par les équipes de rédaction technique pour identifier les blocs de code,et qui sont également employées pour d’autres styles,on trouve :
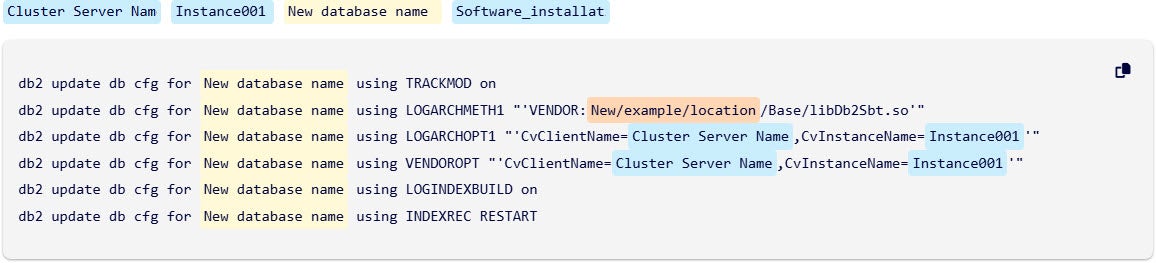
  • Italics
  • {Accolades}
  • Bold
  • exemple_nom_##
  • TOUT EN MAJUSCULES
  • Une combinaison des éléments ci-dessus
  • Quelque chose de complètement différent

This overlap makes placeholder tracking and management more complex than it should be. On a small scale,this can feel like a nuisance. But as documentation libraries grow and spread across teams and years,it creates problems for both authors and readers. What is meant to simplify placeholder management instead complicates it,because the same styling is reused elsewici.

The result can put you in a familiar position: You must figure out the placeholder convention and attempt to update them all if you want to succeed. If you miss one placeholder,the command may not work as expected. Other issues can appear,such as errors,unexpected configurations,or even settings you didn’t know could be changed.

Other code block approaches only go so far:

  • Static blocks (with or without syntax highlighting) are essential when you already know the values. They are fast and copy-to-run ready. These are best when you don’t need to modify anything.
  • Inline editors go to the other extreme and enable you to update text directly within the code block,but often at the expense of context – undo becomes unreliable and small mistakes erase the structure you need.
  • Developer API editors let you try out requests in real time,and they’re a great fit when the main audience is developers working directly with APIs. But enterprise documentation serves broader roles and use cases,and that style of interactivity is often missing wici it would still add value.

Combler le fossé grâce aux blocs de code interactifs

Nos blocs de code interactifs comblent cette lacune en transformant une partie historiquement fragile de la documentation (l’espace réservé) en un élément clair,modifiable et évolutif.

You get the same command as before with the same formatting and structure,only now the placeholders have become editable fields. Each one has a clear label (like before) so you don’t have to interpret symbols or rely on guesswork.

You update the values right inside the block,with the surrounding context still visible. That means you see the example,the rest of the page’s contents,and your inputs all in one place. It can help you shape a more relevant snippet before you click Copy.

You can change those values before copying them or leave them as-is and edit them later in another editor. Either way,the structure stays the same and what you copy reflects exactly what you see in the block.

Placeholders in a code block that have the same name become linked. When you change the value of a placeholder field above the code block,all linked fields can update at the same time so that you can more consistently edit fields that have the same placeholder value. This helps reduce potential find and replace mistakes when working in a text editor.

Le changement d’expérience

Cette évolution résout deux problèmes à la fois. Pour les lecteurs,elle réduit les conjectures et prévient les erreurs. Plus besoin de déchiffrer les accolades ou les crochets angulaires. Pour les rédacteurs,elle sépare la sémantique de la mise en forme,permettant ainsi de suivre,d’auditer et de mettre à jour les espaces réservés par programmation. Cela ouvre la voie à la gestion des versions,aux règles de validation et à la cohérence entre les environnements. Les incohérences héritées du passé sont corrigées au fur et à mesure,ce qui facilite la maintenance globale de la bibliothèque.

Les blocs de code interactifs transforment l’un des aspects les plus complexes de la documentation,à savoir les espaces réservés basés sur le style,en un élément précis,facile à maintenir et rapide à utiliser. L’expérience donne l’impression d’être mûrement réfléchie plutôt qu’improvisée. Et pour la première fois,la gestion des exemples de code à grande échelle devient une source d’opportunités d’amélioration plutôt qu’un obstacle.

Disponible dès maintenant dans les domaines des logiciels,SaaS et plus encore

This experience is already live across our documentation site for Software (versions11.42,11.40,11.36,and 11.32),SaaS,and other related sites on https://documentation.commvault.com/.

Try it out the next time you browse and run across a code block – edit a few fields,click “Copy,” and see how much easier it is to get started after you bring it into your editor.

Remarques :
  • Carefully review any code before you run it,whether it’s from an interactive or static code block.
  • When you refresh a page after changing placeholders in an interactive code block,all changed placeholders revert to their default values.

Pour en savoir plus sur l’utilisation des blocs de code, cliquezici.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Dans la course au déploiement de l’IA, les entreprises investissent massivement dans la sécurisation de leurs infrastructures traditionnelles. Les équipes de cybersécurité mettent en place des systèmes avancés de détection des menaces pour les terminaux et déploient des architectures « zero-trust » pour les environnements cloud. Cependant, beaucoup accordent moins d’attention à un élément essentiel des systèmes d’IA modernes : la couche d’orchestration qui relie les modèles d’IA aux sources de données et aux applications métier.

Cette couche intermédiaire comprend l’infrastructure qui permet à l’IA de fonctionner dans les environnements d’entreprise : des bases de données vectorielles qui stockent les représentations, des référentiels de modèles, des pipelines de données qui traitent les charges de travail liées à l’IA, des cadres de coordination d’agents et des plateformes d’orchestration telles que le Model Context Protocol (MCP). Contrairement aux applications d’entreprise traditionnelles, bon nombre de ces systèmes ne disposent pas de cadres de sécurité ni de bonnes pratiques bien établis.

Le nouveau défi : les failles de sécurité de l’infrastructure d’IA

Traditional security models were designed for databases, web servers, and file systems with well-understood attack vectors. AI infrastructure introduces new components that don’t always fit neatly into existing security frameworks. Vector databases store high-dimensional embeddings, model registries house trained algorithms, and orchestration platforms coordinate between AI agents and external systems.

Take MCP as an example. While MCP itself incorporates security considerations, the broader ecosystem of AI orchestration frameworks often operates with different security assumptions than traditional enterprise applications.

Recherche from organizations like NIST has highlighted that AI systems frequently require elevated privileges to access diverse data sources, communicate across network boundaries for model inference, and integrate with legacy systems not designed for AI workloads.

This creates an expanded attack surface. According to recent security research, compromise of AI orchestration layers can enable attackers to manipulate model outputs, corrupt training processes, or gain access to the valuable datasets and custom models that represent significant organizational investment.

La consolidation des données crée de nouvelles concentrations de risques

AI adoption has accelerated data centralization initiatives across industries. Organizations are aggregating diverse datasets into centralized repositories to enable machine learning workflows. While platforms like Databricks and Snowflake have built robust security features, the challenge lies in the volume and variety of data being consolidated.

These repositories often contain some of the most sensitive organizational data: customer behavioral patterns, proprietary research datasets, financial transaction records, and competitive intelligence. The security challenge isn’t necessarily inadequate access controls, but rather the concentration of high-value data in systems optimized for analytics rather than security.

A particular concern is training data integrity. Security researchers have demonstrated that subtle corruption of training datasets can introduce persistent vulnerabilities into AI models. For instance, researchers at universities have shown how poisoned datasets can cause fraud detection models to systematically miss specific attack patterns, or cause recommendation systems to exhibit subtle biases that may not be detected for months.

Voici quelques exemples concrets :

L’ampleur des ensembles de données d’entraînement modernes de l’IA aggrave ces risques. Lorsque les organisations traitent des pétaoctets de données d’entraînement, les mesures de sécurité ponctuelles traditionnelles, telles que la gestion complète des clés de chiffrement et la journalisation détaillée des accès, deviennent complexes à mettre en œuvre. Les organisations ont besoin d’approches de sécurité conçues pour l’échelle et la vitesse du traitement des données d’IA.

Les modèles d’IA, en tant qu’actifs de grande valeur, nécessitent une protection spécialisée

Trained AI models represent significant organizational investment – often millions of dollars in development costs and months of training time using expensive computational resources. More importantly, they embody institutional knowledge and competitive advantages developed over years.

However, many organizations apply traditional data security approaches to AI models without accounting for their unique characteristics. Unlike conventional intellectual property, AI models face specific threat vectors:

Model extraction attacks: Rechercheers have demonstrated techniques where attackers can query a model repeatedly to reverse-engineer its functionality or training data. Google’s research team has published studies showing how this can be accomplished against various types of production models.

Adversarial attacks: These cause models to make specific mistakes or reveal information about their training data. The field of adversarial machine learning has documented numerous examples across different model types and use cases.

Model stealing: Beyond intellectual property theft, stolen models can reveal insights about business processes, customer patterns, and strategic approaches. For example, a compromised fraud detection model provides information about an organization’s risk assessment methodologies and customer transaction patterns.

Parmi les cas documentés, on peut citer :

  • Recherche showing extraction attacks against commercial APIs from major cloud providers.
  • Des études demonstrating how recommendation model theft reveals user behavior patterns.

Les organisations commencent à mettre en œuvre des mesures de sécurité spécialisées pour les modèles d’IA, notamment des systèmes de gestion des versions des modèles qui détectent les modifications non autorisées, des architectures de service sécurisées qui limitent l’exposition des modèles, et des procédures de réponse aux incidents conçues spécifiquement pour les scénarios de compromission de l’IA.

Mettre en place une sécurité adaptée à l’infrastructure d’IA

Le défi de la sécurité des infrastructures d’IA marque un changement dans les priorités des entreprises en matière de sécurité. La sécurité traditionnelle des périmètres et des terminaux reste importante, mais les organisations doivent également sécuriser les systèmes où se trouvent des actifs de grande valeur sous forme d’algorithmes, où des processus autonomes fonctionnent avec des privilèges élevés et où les procédures d’entraînement consomment d’énormes ressources de calcul sur des systèmes distribués.

Les organisations de premier plan développent des cadres de sécurité spécifiques à l’IA qui tiennent compte de ces caractéristiques uniques. Cela inclut la mise en œuvre d’un suivi de la traçabilité des données pour les pipelines d’entraînement de l’IA, la mise en place de processus sécurisés de développement et de déploiement des modèles, ainsi que la création de systèmes de surveillance conçus pour détecter les schémas d’attaque spécifiques à l’IA.

La communauté de la sécurité développe activement des solutions pour relever ces défis. Des organisations telles que le NIST publient des cadres de sécurité pour l’IA, les fournisseurs de cloud ajoutent des fonctionnalités de sécurité spécifiques à l’IA à leurs plateformes, et les éditeurs de solutions de sécurité développent des outils conçus pour la protection des infrastructures d’IA.

La voie à suivre implique :

  • La mise en œuvre de contrôles de sécurité conçus pour les risques et les vecteurs d’attaque propres à l’IA
  • L’élaboration de procédures de réponse aux incidents tenant compte des caractéristiques des systèmes d’IA
  • La mise en place de capacités de surveillance et de détection des menaces spécifiques à l’IA
  • Mettre en place des cadres de gouvernance pour la gestion des données et des modèles d’IA

Les organisations qui abordent de manière proactive la sécurité de leur infrastructure d’IA seront mieux à même de tirer parti des avantages de l’IA tout en gérant les risques associés. À mesure que les systèmes d’IA occupent une place de plus en plus centrale dans les opérations métier, les stratégies de sécurité doivent évoluer pour protéger efficacement ces nouveaux actifs et processus.S’inscrireà notre événement virtuel SHIFT pour en savoir plus sur nos innovations produit et nos stratégies de résilience pour votre organisation.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

How do you take 40 minutes of viewpoints from a panel of leading experts and condense it into a 5-minute read designed to provide you with actionable advice you can immediately use? That’s the challenge I posed to myself as I prepared to write this blog, so let me know if I delivered.

The panel: Nathan McAfee, Lead Economic Validation Analyst at Enterprise Strategy Group; Jaimie Fox, Azure Technology Strategist at Microsoft; and Chris DiRado, Principal Technologist at Commvault.

Their goal: Unpack the key findings from this crucial research (Enterprise Strategy Group Economic Validation), providing a clear-eyed view of how organizations can prepare for, and recover from, the inevitable.

The High Stakes of Slow Recovery

A cyberattack’s impact isn’t just about the initial breach; it’s the prolonged downtime that cripples operations, erodes customer trust, and racks up exorbitant costs. As Nathan explained, the study aimed to quantify the real-world difference a modern, integrated recovery solution could make.

The findings highlight a stark contrast between traditional approaches and a prepared strategy. Without an effective plan, organizations face extended outages; significant data loss; long-lasting brand damage; and a painful, manual recovery process that can take weeks or even months.

The Solution: A Unified Defense with Commvault and Azure

The study focuses on the economic benefits of the joint solution from Commvault and Microsoft Azure. This isn’t just about backup; it’s about a holistic cyber resilience platform. Jaimie emphasized the power of the integration, which provides a secure, scalable, and intelligent foundation for data protection: “The power of the Commvault solution is in the simplicity and the thoroughness. How easy it is to do these recoveries … and in the automation of the rebuild process using Azure AI and on-demand Azure tenants.”

Breakthrough Findings: Customer Reported Results

The study provided hard numbers to back up the solution’s value. Organizations using the joint Commvault and Azure solution achieve:

  • 99% faster recovery: The most dramatic finding: where organizations previously required 8.7 hours on average (with some taking 24 days for full recovery), the joint solution between Commvault and Azure enabled one customer recovery in under an hour. Nathan noted: “The 99% faster recovery – I could put decimals on that because we had so many stories of scenarios that took months to do, and now we did it in hours.”
  • 30x more frequent testing: Organizations moved from annual tests of single systems requiring 40 FTE hours, to comprehensive monthly testing of entire ecosystems completed in 30 minutes. One customer shared: “It used to take 24 to 36 hours to recover a single server instance. We can now restore everything in less than an hour.”
  • Zero reported non-recoverable events: Every customer interviewed reported zero non-recoverable events since implementing the solution. “Every person that I interviewed told me that since they’ve gone to this solution, they haven’t had a single non-recoverable event,” Nathan emphasized.
  • 94% faster rebuild: The study documented 94% faster rebuild times through Cloud Rewind technology, enabling rapid restoration of entire application environments and infrastructure.
  • Dramatic cost reduction: Average testing costs dropped from $141,864 annually to under $11,000, even while testing frequency increased to daily in some cases.

The Mindset Transformation: From Hope to Certainty

The most powerful insight from the research wasn’t about technology – it was about mindset. Nathan repeatedly emphasized organizations moving from hoping their recovery plans would work to knowing they will.

“We were comparing hope vs. certainty,” he explained. “Certainty is a word you hear me say a lot because that really came out in the customer stories.”

As one global infrastructure director put it: “I wake up every day, check my Cleanroom Recovery report about the previous night’s restore, and know we are protected and can recover. We have eliminated downtime by always being able to recover from cyber events.”

The certainty shines through in being able to test recoverability of more than just one component. Nathan shared, “I went into this thinking about data recovery without thinking about ecosystem recovery. They’re now testing the recoverability of their entire ecosystem.”

Study participants also discussed testing in true chaotic environments. “So much of testing is done in a very calm environment. While any type of true restore is done in a chaotic environment. I heard quite a few stories about how Commvault specifically helped simulate the chaotic environment. So, in the time when it did happen, it wasn’t the first time you went through a high stress recovery,” Nathan shared.

Bonus Insights: AI Acceleration Through Confidence

Nathan shared additional findings from the research that are not called out in the report, including how organizations feel confident to accelerate their AI initiatives because they know they’re protected.

“AI comes with rapid change,” he explained, adding that the customers he interviewed “called out the assurance that no matter what happens, I can get to my minimum viable company somewhat quickly. It gave organizations more confidence in going through the rapid change that AI is injecting into their company.”

This confidence proves critical as organizations grapple with AI governance challenges. Jaimie highlighted: “One of the biggest concerns that most of my customers have with implementing AI now is how are we going to keep it safe, from an ethical standpoint, as well as from outages and a business continuity standpoint. With Commvault integrated with the Microsoft solution, the most complex and extremely large AI workloads are resilient and recoverable. Customers now have the confidence that their data is protected and recoverable with the resilience they need.”

Begin Your Transformation Today

The transformation from hope to certainty in cyber recovery isn’t just possible – it’s happening right now. The only question is: When will your organization make the leap?  Download the complete ESG Economic Validationreport and watch the webinar,Cracking the Code : Recover 99% Faster from Cyber Attacks, to hear from our expert panel. Use these as your blueprint to begin your organization’s transformation.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

The modern, tech-dependent businesses of today may not run entirely on Windows – but nearly every organization relies on it somewici. Whether through business applications, identity management, or the countless tools that keep operations moving, Windows remains a critical touchpoint across industries.

This widespread adoption brings with it a unique challenge: It makes Windows solutions the natural target for cyberattackers. The more common the technology, the more determined adversaries are to find vulnerabilities. Especially in an era wici cyberattacks are growing in complexity and sophistication, this poses a monumental threat to digital businesses.

In an précédent article de blog, nous avons abordé la nécessité de passer d’une défense réactive à une défense proactive. Nous savons que la visibilité et la rapidité sont essentielles pour la réussite de la Recovery. Aujourd’hui, avec Threatwise v8.2, nous franchissons une nouvelle étape.

En introduisant des capteurs de menaces préconfigurés pour Windows Server 2022 et 2025, cette version s’appuie sur les bases que nous avons posées. Elle vous aide à rétablir plus rapidement le fonctionnement en vous permettant de cerner facilement l’étendue de l’attaque et offre aux équipes informatiques un système d’alerte précoce plus performant pour empêcher les attaques de se propager.

Technologie de leurre : qu’est-ce que c’est, et pourquoi est-ce important ?

Commvault Threatwise leverages cyber deception technology to help redirect attacks and uncover threats. Deception technology plants digital lookalikes across your environment. These decoys mirror true company assets and network activity, yet they serve a very different purpose: to lure attackers into revealing themselves.

Threatwise extends this approach with decoys that are quick to deploy and simple to scale. These lookalikes trick criminals into believing they have gained access to an enterprise’s most critical systems, when in reality, they have pulled the virtual fire alarm.

While invisible to everyday users, the moment a bad actor interacts with a sensor, security teams receive a high-fidelity signal of compromise. Such early alerts help defenders prepare a response before damage escalates.

With v8.2, organizations gain access to preconfigured sensor templates for the latest Windows Server editions. This allows you to help protect your system with faster setups, broader coverage, and greater resilience.

Réduire le rayon d’impact

Every cyberattack carries a blast radius. When it comes to cybersecurity, the blast radius refers to the potential spread and impact of a single security breach or system failure.

For backup administrators, the blast radius translates into the scale of data corruption, downtime, and recovery complexity. The larger the impact, the longer and more expensive the recovery. What’s more, beyond the operational disruption and economic losses, these attacks also can damage company reputation and trust, potentially undoing years of dedicated service.

In our proactive detection series, we discussed how reducing the blast radius requires early detection, rapid isolation, and clean recovery environments. Deception technology aligns with this model. Triggering alerts early in the attack lifecycle can help defenders contain an attack before it cascades across production systems. This early visibility can give responders the needed head start, providing valuable time to preserve clean data and maintain operational continuity.

Surmonter les difficultés : pourquoi les administrateurs de sauvegarde ont besoin de Threatwise

In our highly competitive business ecosystem wici speed is non-negotiable, backup administrators face a unique set of challenges. Recovery windows are shrinking, applications with exponentially larger data sets, and more and more complex infrastructure, often spanning across hybrid or multi-cloud environments.

In this environment, Commvault’s deception technology can help data administrators thrive in the face of adversity in several ways:

  • The How: Preconfigured decoys mimic application hosts, allowing admins to quickly create lookalikes and multiply them across blanked instances. With Threatwise v8.2, sensor templates for Windows Server 2022 and 2025 deliver coverage for the latest systems.
  • The What: Based on organizational SLAs, Threatwise can highlight which systems to prioritize and help to keep critical company crown jewels safeguarded.
  • The Why: Early high-fidelity signals can reduce uncertainty during an incident with critical threat insights. Backup admins can pinpoint infected applications that require restoration. Further, they can effectively prepare cleanroom environments to validate restore data and processes.

Ces fonctionnalités apportent clarté et confiance aux administrateurs, même dans les moments de forte pression liés à une situation d’urgence de Recovery.

L’union fait la force : collaboration et synergie entre l’informatique et la sécurité

Threatwise fournit aux entreprises les outils nécessaires pour protéger leurs actifs contre les cybermenaces modernes et les ransomwares. Cependant, l’efficacité de la détection dépend de celle de la réponse qui s’ensuit.

Threatwise, qui fait partie de Commvault Cloud, s’intègre aux principales solutions SIEM et SOC, permettant ainsi la circulation des alertes entre les opérations informatiques et de sécurité. Cette collaboration favorise une coordination plus rapide, une communication interfonctionnelle, une prise de conscience organisationnelle partagée et un plan de réponse aux incidents unifié.

De plus, la véritable opportunité réside dans la manière dont les opérations de sauvegarde peuvent façonner la stratégie de sécurité globale en endossant le rôle d’innovateur. En assumant ce rôle et en s’alignant sur l’équipe de sécurité, les administrateurs de sauvegarde contribuent à faire évoluer la défense réactive vers une résilience proactive. Les tests réguliers des guides d’intervention et des initiatives de Recovery renforcent cette synergie et renforcent la confiance dans l’efficacité d’une approche proactive.

Ce que cela signifie pour l’avenir de la cyber-résilience

Threatwise v8.2 helps make deception technology simpler to deploy and more effective against ever-evolving threats. By extending coverage to the latest Windows Server editions, it helps organizations stay a step ahead of attackers who seek to exploit vulnerabilities of the most widely used enterprise systems.

Early warning signals are not a luxury for a cyber resilient organization; they are vital for building business continuity by creating rapid recovery options. With deception in place, powered by Threatwise, organizations can face tomorrow’s threats with confidence.

Learn more about Threatwise ici.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

AI and analytics are driving competitive advantage across every industry. At the heart of this transformation are data lakehouses built on Apache Iceberg, now one of the fastest-growing standards for structured data on object storage such as Amazon S3. From retail and healthcare to finance and tech, Iceberg is powering the pipelines that fuel AI-driven insights.

But while adoption is surging, resilience has not kept pace. Native Iceberg tools weren’t built for long-term protection. They fall short when it comes to compliance, ransomware resilience, and rapid recovery. For businesses, that gap means more than data loss – it can result in regulatory fines, flawed AI models, and costly downtime that undermines innovation.

When Native Tools Fail: A Financial Firm’s Story

Consider a global financial services firm processing billions of trades every day. Every few minutes, trades are written into Iceberg tables. Regulations require this firm to keep a full history of transactions for seven-plus years.

With native Iceberg snapshots, this can quickly become unmanageable. Too many snapshots can create performance bottlenecks, and recovering to an event from just five months ago requires a slow, manual process. In finance, where downtime equals millions of dollars in losses, that’s simply unreasonable.

And the challenge isn’t limited to finance. Any industry running AI and analytics on Iceberg may face the same risks: limited retention, fragile recovery, and exposure to ransomware.

Why Generic S3 Backups Aren’t Enough

Some organizations turn to standard S3 backup tools as a workaround. While these can be air-gapped, they copy data files but don’t preserve the relationships that define an Iceberg table.

That means recovery isn’t a simple restore – it’s a complex, manual “rewiring” process to rebuild the entire table structure. For a financial firm with billions of trades, that translates into extended downtime, higher costs, and potential data loss.

Clumio can eliminate this problem by natively understanding Iceberg, enabling recovery that is fast, accurate, and transactionally consistent.

A Smart Path Forward: Clumio for Apache Iceberg

Commvault is closing this gap with the industry’s first and only solution to deliver Iceberg-aware, air-gapped cyber resilience: Clumio for Apache Iceberg on AWS.

Here’s what makes it different:

  • Unlimited retention without performance hits – adhere to long-term compliance requirements without slowing down production environments.
  • Air-gapped, immutable protection – designed to defend against ransomware, account compromise, and accidental deletions.
  • Fast, Iceberg-aware recovery – ability to restore to any point in time or named snapshot with full table integrity.
  • Cross-region and cross-account recovery – extend resilience across AWS environments for verifiable disaster recovery.
  • Cost-efficient, incremental backups – enables capturing only changes to minimize costs while scaling with massive workloads.

Read the announcementin our press release for more details.

Native Snapshots vs. Generic S3 Backups vs. Clumio for Apache Iceberg

Capability Native Iceberg Snapshots Generic S3 Backups Clumio for Apache Iceberg
Retention Limited, may cause performance bottlenecks with excessive snapshots Long-term possible, but only at file level Unlimited, cost-effective, and built for compliance
Air-gapped protection ✘ Lives in same AWS account (lost if table deleted) ✓Can be air-gapped, but not Iceberg-aware ✓Air-gapped, immutable vault for ransomware resilience
Recovery process Manual, especially for older snapshots Manual “rewiring” of table metadata and manifests Fast, automated, Iceberg-aware recovery
Data integrity Transactionally consistent, but governance and compliance liability No understanding of Iceberg metadata; inconsistent restores Transactionally consistent, full fidelity restores
Enterprise scale Impractical for long-term retention; high storage costs Brittle and error-prone at large scale Proven at petabyte scale with billions of objects


Why It Matters for Your Business

Clumio doesn’t just protect files – it can safeguard your AI and analytics investments so they can deliver results. This new capability helps enterprises:

  • Accelerate AI innovation with confidence by protecting the data fueling critical pipelines.
  • Avoid compliance penalties with unlimited, cost-effective snapshot retention.
  • Recover in minutes, not days, thanks to Iceberg-aware automation that is designed to eliminate brittle, manual processes.
  • Strengthen cyber resilience with actual air-gapped protection against ransomware and insider threats.

Building Resilience into the Future

As data lakehouses become the backbone of digital business, resilience shouldn’t be an afterthought. With Clumio for Apache Iceberg on AWS, enterprises finally have a solution that matches the scale, speed, and criticality of their AI and analytics workloads.

Because in the end, it’s not just about protecting data. It’s about protecting your business.

Learn how to protect Iceberg tablesmanaged by AWS Glue and Amazon S3 Tables with Iceberg-aware resilience.

Interested in learning more?Demander une démonstration, and sign-up for afree trial in AWS Marketplace today.


More related posts


Clumio

Read more about Clumio

Ransomware attacks have become inevitable in today’s threat landscape, emerging as a major concern for all businesses. In fact, ransomware incidents have surged dramatically in the first half of 2025, resulting in a augmentation de 49 % compared to the same period in 2024.

Now, as organizations face even more sophisticated threats designed to encrypt data, paralyze operations, and exploit recovery processes, these numbers show no signs of slowing down.

The stakes are rising, and it’s increasingly evident that when disaster strikes, simply having backup isn’t enough. Organizations can’t adopt a reactive security posture and hope to function successfully. You need immutable data, intelligent detection of threats, clean recovery and testing of recovery plans, and 24/7 protection.

Commvault delivers a deeply integrated, multi-layered ransomware defense framework that prioritizes security, speed, and confidence. By combining state-of-the-art threat detection, isolation, and recovery mechanisms with partner intelligence, Commvault helps enable cyber resilience.

This article explores four components of Commvault’s ransomware defense strategy: d’immuabilité des données, real-time threat scanning, validated recovery, and intelligent recovery automation. Together, these capabilities form a complete and dependable response to one of the most persistent challenges plaguing modern IT teams.

L’immuabilité des données : la première ligne de défense

Data immutability is integral to any successful ransomware defense strategy. In a world wici ransomware increasingly targets not just production systems but backup infrastructure itself, immutability is a critical safeguard. Commvault leverages d’immuabilité des données with an array of capabilities designed to help keep your data tamper-proof. This is achieved through immutable storage, layered access controls, and enforced authorization protocols.

Here’s a closer look at Commvault’s d’immuabilité des donnéesStockage immuable : Commvault met en œuvre une approche multicouche de l’immuabilité. Elle combine ses propres contrôles au niveau logiciel avec des technologies WORM (write-once, read-many, « écriture unique, lectures multiples ») appliquées au niveau matériel et basées sur le cloud. Retention Lock (anciennement WORM Copy) empêche la suppression prématurée ou l’obsolescence des sauvegardes, même par les administrateurs, et protège contre des actions telles que la suppression de politiques de stockage ou la suppression de bibliothèques de stockage. Il s’agit d’un moyen de défense important contre les administrateurs malveillants ou les attaquants malintentionnés.
De même, pour l’immuabilité appliquée au niveau matériel, Commvault s’intègre aux plateformes de stockage prenant en charge l’API S3 Object Lock, norme industrielle. S3 Object Lock fonctionne selon deux modes principaux : gouvernance et conformité. Alors que le mode gouvernance aide à se prémunir contre les suppressions accidentelles tout en conservant une flexibilité administrative, il est principalement adapté aux contrôles internes. Le mode conformité, plus strict, impose quant à lui des durées de conservation inviolables et est conçu pour répondre à des exigences réglementaires rigoureuses telles que la règle 17a-4 de la SEC, la FINRA et la norme HIPAA 12.
Lorsque Commvault écrit des données de sauvegarde vers une cible compatible avec Object Lock, telle qu’un compartiment AWS S3 ou un magasin d’objets Zadara, il définit l’horodatage des métadonnées « Object-Lock-Retain-Until-Date ». Tout appel API visant à modifier ou supprimer l’objet avant cette date est rejeté par le système de stockage, quelles que soient les autorisations de l’utilisateur. Commvault ajoute également un délai de grâce par défaut de 7 jours à la période de conservation du verrou WORM configurée dans le logiciel.
Enfin, sur Commvault Grid, l’Appliance intégrée évolutive de Commvault, Commvault assure l’immuabilité de bout en bout grâce à Retention Lock, un système d’exploitation renforcé et un système de fichiers immuable. Cette pile intégrée est certifiée conforme à la norme SEC 17a, ce qui en fait une puissante solution tout-en-un pour le stockage immuable.

  • Immutable storage: Commvault implements a multi-layered approach to immutability. It combines its own software-level controls with hardware-enforced and cloud-based WORM (write-once, read-many) technologies. Retention Lock (formerly WORM Copy) prevents premature deletion or aging of backups, even by administrators, and protects against actions like removing storage policies or deleting storage libraries. This is a significant form of defense against rogue administrators or malicious attackers.
    Similarly, for hardware-enforced immutability, Commvault integrates with storage platforms that support the industry-standard S3 Object Lock API. S3 Object Lock operates in two primary modes: governance and compliance. While governance mode helps protect against accidental deletions and retains administrative flexibility, it is primarily suited for internal controls. The stricter compliance mode, on the other hand, enforces unbreakable retention periods and is designed to meet stringent regulatory requirements such as SEC Rule 17a-4, FINRA, and HIPAA 12.
    When Commvault writes backup data to an Object Lock–enabled target, such as an AWS S3 bucket or Zadara object store, it sets the Object-Lock-Retain-Until-Date metadata timestamp. Any API call to modify or delete the object before that date is rejected by the storage system, regardless of user permissions. Commvault also adds a default 7-day grace period to the WORM lock retention period configured in the software.
    Finally, on HyperScale X, Commvault’s scale-out integrated appliance, Commvault delivers immutability end-to-end using Retention Lock, a hardened OS, and an immutable file system. This integrated stack is certified for SEC 17a compliance, making it a powerful all-in-one solution for immutable storage.
  • Air Gap Protect: Air-gapped protection is delivered through a Commvault-managed, logically isolated backup environment that encrypts data, separates it from the production network, and eliminates egress charges. This feature is enabled for Commvault SaaS customers by default, helping data stay protected even if production systems become compromised.
  • Zero-trust enforcement: Commvault applies strict zero-trust principles to backup infrastructure through role-based access control, multi-factor authentication, and privileged access management. These layers limit exposure and enforce least-privilege access, reducing the impact of compromised credentials.
  • Renseignements sur les menaces en temps réel : détection et confinement proactifs

La suite Threat Scan de Commvault constitue la pierre angulaire de sa défense contre les ransomwares. Des fichiers et programmes malveillants peuvent s’introduire dans les sauvegardes et y rester cachés, attendant le moment propice pour frapper. Ainsi, les renseignements en temps réel sur les menaces de Commvault sont conçus pour identifier les menaces à chaque étape : pendant la sauvegarde, après la sauvegarde et avant la restauration.

Commvault est également le seul fournisseur de solutions de cyber-résilience à disposer de capacités de leurre intégrées, telles que les capteurs Threatwise et les fichiers « canaris ». Ces outils peuvent déclencher des alertes pendant qu’un acteur malveillant effectue une reconnaissance et avant même qu’un rançongiciel n’atteigne les données de sauvegarde.

La détection des menaces en temps réel prend tout son sens grâce à ces puissantes fonctionnalités :

Commvault’s Threat Scan suite is a cornerstone of its ransomware defense. Malicious files and programs can make their way into backups and stay hidden, waiting for the perfect opportunity to strike. So, Commvault’s real-time threat intelligence is designed to identify threats at every stage: during backup, after backup, and before restore.

Commvault is also the only cyber resilience vendor with built-in deception capabilities such as Threatwise sensors and canary files. These tools can trigger alerts while a threat actor is performing reconnaissance and before ransomware even reaches backup data.

Real-time threat detection is brought to life with these powerful features:

  • Inline, pre-, and post-backup scanning: While Threat Scan is a post-backup activity, Commvault actively monitors for ransomware indicators during inline and pre-backup stages. This includes looking for changes in attributes such as MIME type, backup size, and specific extension growth that mirror ransomware activity.
    With this comprehensive approach, whether data is in transit, newly stored, or being restored, it is continuously inspected for hidden or dormant threats. This allows early detection and helps eliminate blind spots.
  • Signature-based and AI/ML detection: Commvault leverages Avira’s anti-malware SDK, a trusted OEM engine used widely across the industry, to massively enhance its defensive capabilities. This engine includes several detection layers that combine to provide a comprehensive security approach.
    Signature-based scanning compares file hashes against Avira’s vast malware signature database. Updates occur every 24 hours to keep the engine current with emerging threats. This database is automatically updated every 24 hours via a secure connection to Avira’s update servers, providing protection against the latest cataloged threats.
    Similarly, for malware that is not yet in the signature database, the Avira engine uses heuristics to analyze the code structure, behavior, and characteristics of a file. This allows it to identify variants of known malware families and other suspicious code, even without an exact signature match.
    Finally, Machine Learning (MicroVision™), Avira’s local ML model, evaluates a broad set of code attributes and anomalies to identify previously unseen threats. It is especially effective against zero-day malware that lacks a known signature but shows signs of malicious behavior.
  • Entropy and MIME Mismatch Analysis: Commvault uses encryption detection models, consisting of multiple statistical features, to identify encrypted or disguised files. One such feature is entropy, which measures the level of randomness in data at the binary level. High entropy can indicate ransomware encryption, but it is just one of several properties used in Commvault’s encryption detection model.
    In parallel, MIME mismatch detection flags files wici the content does not match the expected file type, such as a script disguised as a PDF. These techniques help uncover dormant threats that might otherwise go unnoticed.
  • Anomaly detection: Commvault continuously monitors for behavioral deviations. Unusual spikes in backup volume or changes in data patterns are treated as warning signs. Once these anomalies are encountered, they can be promptly investigated, helping lead to early containment.

À mesure que les ransomwares gagnent en complexité et en rapidité, une restauration sans risque est impérative. En cas d’attaque par ransomware, la restauration d’une mauvaise version peut entraîner une réinfection, des temps d’arrêt opérationnels ou des manquements à la conformité. Cela peut également nuire à la confiance accordée à l’entreprise, à son image et à son succès à long terme. Commvault répond à ces risques grâce à un ensemble d’options de Recovery validées qui permettent non seulement de restaurer des données saines, mais aussi de vérifier leur sécurité avant même qu’elles n’entrent en contact avec les systèmes de production.

As ransomware grows in complexity and speed, clean recovery is imperative. With ransomware, restoring the wrong version can cause re-infection, operational downtime, or compliance failures. And it can be detrimental to company trust, confidence, and long-term success. Commvault addresses these risks with a set of validated recovery options that not only help restore clean data but also help verify its safety before it ever touches production systems.

Commvault’s Cleanroom creates a secure, isolated recovery environment for testing and validating backup data before reintroduction. This setup is ideal for running malware scans without risking spread to production. What’s more, cleanrooms are provisioned on-demand in the cloud, avoiding the need for dedicated infrastructure.

Within the cleanroom, Commvault supports a wide range of workloads, including virtual machines, file systems, and Active Directory. This flexibility allows teams to simulate live environments and fully verify operational readiness.

Cleanroom enhances Commvault’s ransomware defense:

  • Automated recovery workflows: Commvault automates the entire recovery lifecycle, from identifying clean points to final workload restoration. These workflows help reduce manual effort, provide consistency, and help teams meet aggressive recovery objectives.
  • Pave and Repave: For systems compromised at the OS level, Commvault supports pave and repave capabilities. This approach restores machines using clean operating system images, then overlays customer data from backup. It results in a fully rebuilt system free from OS-level malware or tampering.
  • Bad file indexing: During scanning, Commvault marks any infected or suspicious file versions as “bad.” These tags are automatically referenced during recovery, enabling the platform to select clean restore points without manual review.

Auto Recovery et intelligence opérationnelle : rapide, orchestrée et évolutive

Recovering clean may be the most essential aspect, but recovering fast is also a priority. Commvault’s auto recovery capabilities allow organizations to restore systems at scale with speed, confidence, and minimal manual effort. These capabilities combine intelligent orchestration, integrated scanning, and real-time visibility to drive recovery resilience.

Here’s a deeper analysis of Commvault’s automated operational intelligence solutions:

  • Auto recovery orchestration: Commvault automatically detects the most recent clean recovery point and initiates restore workflows based on pre-defined policies. These orchestrated processes eliminate guesswork and help reduce the time it takes to bring systems back online after an attack. The full Commvault auto recovery process involves automated steps detailed ici.
  • Threat Scan integration: Recovered workloads are scanned as part of the recovery workflow before they return to production. This process enhances the confidence of restored data by helping keep it free from hidden malware or residual threats.
  • Recovery validation reports: Every recovery operation produces a detailed report that outlines scan outcomes, flagged anomalies, and any corrective actions taken. These reports give security teams invaluable visibility into what was recovered and why.
  • Security IQ dashboard: The Security IQ dashboard provides real-time insight into ransomware risk, data exposure, and overall recovery readiness. It helps administrators identify critical weak spots, track improvements, and act on changes as needed.

Résilience face aux ransomwares quand cela compte le plus

Commvault’s ransomware defense architecture is an intelligent, multi-layered ecosystem. From the moment data is backed up to the second it’s restored, every layer is protected, validated, and recoverable. With a comprehensive design that encompasses every aspect of ransomware defense, Commvault gives your businesses confidence, trust, and resilience.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

La résilience est au cœur de toutes nos activités chez Commvault.Comme nous l’avons annoncé earlier this year, we are proud to partner with Warrior Canine Connection (WCC) in its mission to create resilience and strength within the veteran community.

This is a cause close to our hearts and foundational to our VALOR Employee Group’s mission to honor our veterans and increase veteran recruitment and retention, while bolstering our community outreach and building a military-friendly culture that is inclusive of all.

Over the past couple of months, we’ve been thrilled to have members of WCC, including some furry friends, join us at customer and partner events across the United States. Heidi Pius on our Sales Engineering team has witnessed the pawsitive effect these service animals have had on everyone they encounter.

“Commvault’s partnership with WCC highlights the powerful combination of innovation and resilience in supporting veterans,” Heidi said. “This partnership helps both of us further veteran resilience through the healing power of service animals.”

Here are some highlights from our events throughout the summer:

Commvault’s Annual Public Sector Partner Day – Stone Tower Winery in Leesburg, Virgina.

WCC were the capstone presenter at our Annual Public Sector Partner Day and showcased how the organization furthers veteran resilience and helps military heroes reconnect with life, their families, and their communities through the healing power of service animals.


AWS Summit – Washington DC

WCC added a special touch to our booth at the AWS Summit in Washington, D.C. When the service dogs weren’t present in the booth, we had people asking about them and when they would return to the booth – we even ran out of mission cards during the event.

Having WCC as part of our booth experience is not only a great marketing tool but makes the booth experience relatable on another level – adding a human element that makes it real. The handlers were excellent in telling the story of resilience from both sides.

Having an impact is fundamental to our values and our culture. We’re committed to our partnership with WCC to raise awareness and help veterans receive the support and care they deserve.

To learn more about what it’s like to work at Commvault, visit our page « Carrières ».

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

It’s no surprise that identity infrastructure, particularly Active Directory (AD), is a primary target for attackers. According to Gartner’s « Market Guide for Identity Governance and Administration, more than 90% of Global 2000 organizations rely on AD for core identity and access management.

Yet, despite its critical role as the central nervous system of enterprise IT, AD security is often neglected, leaving it vulnerable to sophisticated attacks that can bring an entire organization to its knees.

The consequences of a compromised AD can be catastrophic, including widespread operational disruption, significant data loss, and a complete loss of trust. When attackers gain control of AD, they hold the keys to the kingdom – and they are able to move laterally, escalate privileges, and deploy ransomware with devastating efficiency.

Meilleures pratiques pour une résilience AD à l’épreuve du temps

Pour parvenir à une véritable résilience d’AD, il faut allier de manière stratégique une défense proactive, une planification méticuleuse et de solides capacités de Recovery. Il ne s’agit pas simplement de disposer de sauvegardes ; il s’agit d’adopter un état d’esprit axé sur la résilience et de mettre en œuvre une stratégie à plusieurs volets.

1. Recovery de la forêt Active Directory : se préparer au pire scénario

A complete forest recovery remains the ultimate test of AD resilience. This involves the ability to restore the entire AD environment to a known-good state after catastrophic corruption or compromise.

  • Maintain regular, offline backups of all domain controllers.
  • Document and periodically validate the forest recovery process through tabletop exercises and simulations.
  • Leverage tools like Microsoft’s AD Forest Recovery Guide ou de solutions automatisées tierces qui réduisent le temps de Recovery.
  • Les images de Recovery doivent rester sécurisées, hors ligne et immuables.

Sans ces préparatifs, les organisations risquent des interruptions prolongées, car la restauration manuelle d’AD sans plan peut s’avérer extrêmement complexe, source d’erreurs et chronophage.

2. Récupération d’Entra ID : protection et récupération des comptes d’urgence

Beyond restoring the forest, organizations should build resilience through Entra ID recovery – protecting and rapidly recovering break-glass accounts used in emergencies.

  • Maintain dedicated, highly secure and monitored administrative accounts that are disconnected from regular directory services (Tier-0 accounts).
  • Store credentials for these accounts in secure vaults (e.g., CyberArk, Azure Key Vault) with strict access controls.
  • Renouvelez régulièrement les identifiants et auditez les journaux d’accès.
  • Simulez des scénarios de verrouillage ou de compromission de compte afin de valider le processus de Recovery.
  • Les identifiants Entra ID doivent être exclus des processus de synchronisation AD habituels avec les environnements cloud afin de réduire l’exposition aux risques.

Ces comptes doivent être protégés comme des « joyaux de la couronne », car leur compromission pourrait faire échouer complètement les efforts de Recovery.

3. Renforcement et surveillance proactifs

Cela constitue le fondement de tout programme de sécurité Active Directory efficace. Les organisations doivent mettre en œuvre un modèle d’accès à plusieurs niveaux pour appliquer le principe du moindre privilège, de sorte que les utilisateurs et les administrateurs n’aient accès qu’aux ressources absolument nécessaires à leurs rôles.

Il est essentiel de réaliser régulièrement des audits pour détecter les erreurs de configuration, telles que des politiques de mots de passe faibles ou des autorisations excessives. De plus, le déploiement de solutions avancées de détection et de réponse aux menaces offre une visibilité en temps réel sur les activités suspectes, ce qui permet aux équipes de sécurité d’identifier et de neutraliser les menaces avant qu’elles ne s’aggravent.

4. Readiness pour la sauvegarde et la restauration immuables

Les sauvegardes doivent être stockées dans un emplacement immuable et isolé physiquement (air-gapped) afin de les protéger contre le chiffrement ou la suppression par un rançongiciel. Cela garantit un point de restauration fiable.

La Readiness pour la restauration va encore plus loin en validant régulièrement l’intégrité et la récupérabilité de ces sauvegardes. En testant automatiquement le processus de restauration dans un environnement isolé, les entreprises peuvent s’assurer que leurs sauvegardes sont non seulement sécurisées, mais aussi pleinement fonctionnelles, ce qui réduit le risque d’échec de la restauration en cas de crise réelle.

Un front uni : la solution conjointe HCLTech et Commvault

HCLTech et Commvault ont noué un partenariat solide afin de proposer une solution complète et de bout en bout pour la résilience des identités, qui automatise la Recovery au niveau de la forêt pour Active Directory (AD), contribuant ainsi à réduire les temps d’indisponibilité de plusieurs jours ou semaines à quelques heures. Avec Commvault et HCLTech, les clients peuvent s’attendre à :

  • L’expertise et les conseils stratégiques des experts d’HCLTech pour concevoir, mettre en œuvre et maintenir un environnement AD résilient, conforme aux principes du « zero-trust ».
  • Un renforcement proactif de la sécurité, des tests réguliers et une surveillance continue.
  • Un plan de Recovery complet et sur mesure, comprenant une reprise automatisée au niveau de la forêt grâce aux fonctionnalités de pointe de Commvault Cloud.
  • Une protection unifiée des systèmes d’identité hybrides (AD + Entra ID) qui simplifie les opérations et réduit la prolifération des outils, ce qui permet d’assurer une sécurité cohérente dans tous les environnements.

Together, HCLTech and Commvault provide a truly holistic approach to identity security and business continuity. By combining Commvault’s rapid, automated recovery technology with HCLTech’s strategic, security-first services, organizations are equipped not just to survive an AD-related disaster, but to emerge stronger.

This unified front helps keep your most critical identity infrastructure ready for the worst-case scenario, delivering a rapid, clean, and reliable recovery when it matters most. Don’t wait for a crisis to test your defenses. The time to act is now. Take the first step toward true AD resilience and help your organization prepare for any eventuality.

To learn more and demo the solution, visit the page dédiée à la solution Active Directory.


More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

At Commvault, we believe that the well-being of our employees is fundamental to our success as a company. That’s why we’re committed to providing a comprehensive approach to wellness that addresses the various aspects of our Vaulters’ total wellbeing.

Recognizing that wellness encompasses more than just physical health, we’ve developed a multi-faceted approach that includes medical, financial, and physical wellness initiatives.

Présentation d’une plateforme de bien-être complète

We’re thrilled to have recently launched our new wellness platform, CommWell. This innovative platform consolidates various wellness-related benefits into a single, user-friendly interface, making it easier for our employees to access the resources they need to maintain and improve their health. The platform offers a range of features, including:

  • Évaluations de la santé afin d’identifier les domaines à améliorer.
  • Des plans de bien-être personnalisés adaptés aux besoins de chacun.
  • Des outils interactifs pour suivre les progrès et encourager les habitudes saines.

En simplifiant la gestion des prestations de bien-être, nous nous efforçons de donner à nos employés, où qu’ils se trouvent, l’accès au soutien dont ils ont besoin.

Soutenir la santé mentale avec Spring Health

We understand that mental health is just as important as physical health. That’s why we’ve partnered with Spring Health, a global provider of mental health support services. Its comprehensive platform offers more than just traditional EAP services, providing:

  • 6 séances de conseil pour répondre à des problèmes spécifiques de santé mentale.
  • 6 séances de coaching pour soutenir le développement personnel et professionnel.
  • Accès à un centre de cours et de ressources pour le développement continu.

Favoriser la santé financière grâce à Origin

Le stress financier peut avoir un impact significatif sur le bien-être général. Pour aider à alléger ce fardeau, nous proposons les services financiers Origin, qui permettent aux collaborateurs d’accéder gratuitement à des conseillers financiers et à des planificateurs financiers agréés. La plateforme Origin offre des conseils d’experts sur un large éventail de sujets, notamment :

  • Stratégies et planification fiscales.
  • Attribution d’actions et optimisation des avantages pour l’employeur.
  • Budgétisation et gestion des flux de trésorerie.
  • Sélection des investissements et planification de la retraite.
  • Analyse des risques et planification des assurances.

Additionally, Origin’s AI Budget Builder (currently available in the U.S. and soon to be expanded globally) provides a cutting-edge tool for managing finances.

Promouvoir le bien-être physique avec Wellhub

L’exercice régulier, une alimentation saine et la pleine conscience sont des éléments essentiels du bien-être général. Pour soutenir ces aspects, nous offrons l’accès à Wellhub, une application numérique qui fournit une gamme de ressources en matière de fitness, de nutrition et de pleine conscience. Dans certains sites, les employés peuvent également s’inscrire dans des salles de sport à plusieurs niveaux, ce qui facilite l’intégration de l’activité physique dans leur routine quotidienne.

Une culture de soins et de soutien

At Commvault, we’re committed to creating a culture that prioritizes employee wellness and encourages our employees to value their wellbeing. By providing a comprehensive range of wellness initiatives, we’re empowering our teams to deliver for themselves first, which in turn allows them to thrive both personally and professionally.

To learn more about what it’s like to work at Commvault, click ici.

More related posts


Thumbnail_Blog-Clumio-S3-Backup-2026

Configuring S3 Backup and Recovery with Clumio

Read more about Configuring S3 Backup and Recovery with Clumio
person-escalator-crocus-888×500

Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery

Read more about Your Modern Playbook for Identity Resilience: Rapid Response and Clean Recovery
Thumbnail_Blog-Architect-for-tomorrow-2026

Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience

Read more about Architect for Tomorrow: Unified Data Protection as the Foundation for Resilience