Skip to content

Nell’ultima puntata del podcast “The Resilience Rundown”, il conduttore Thomas Bryant intervista Vidya Shankaran, CTO sul campo per le tecnologie emergenti presso Commvault, per approfondire il mondo dell’intelligenza artificiale (IA). Thomas e Vidya parlano del potenziale dell’IA in vari settori, delle sfide che essa comporta e del suo impatto sulla protezione dei dati e sulla resilienza informatica.

L’entusiasmo e le potenzialità dell’intelligenza artificiale

AI has tremendous potential in today’s world, ranging from healthcare to security, according to Vidya. AI has become an integral part of our lives, with applications like Siri on our phones. From an enterprise perspective, there is still untapped potential due to concerns around security. However, the excitement surrounding AI and its ability to enhance productivity and innovation is palpable.

https://play.vidyard.com/2Tdz9MAD1hu1an1fqyK7Jg

Subscribe: Apple Podcasts | Spotify | YouTube

Il lato oscuro dell’intelligenza artificiale

While AI offers numerous benefits, there is also a dark side that needs to be acknowledged. Vidya emphasizes the importance of data quality in AI models, as “garbage in, garbage out.” If the data fed to AI is flawed or biased, it can lead to inaccurate results. Additionally, there are concerns about the echo chamber effect and the challenge of striking the right balance between innovation and data security.

Il concetto di firewall per i dati

Una soluzione interessante per affrontare le sfide poste dall’intelligenza artificiale è il concetto di firewall dei dati. Vidya spiega che i firewall dei dati si concentrano sull’impostazione di messaggi di sistema volti a impedire agli utenti di accedere a informazioni sensibili. Questi firewall mirano a coprire tutte le possibili permutazioni e combinazioni per garantire la sicurezza dei dati. Vidya illustra alcuni esempi di come aggirare i messaggi di sistema e sottolinea la necessità di un miglioramento continuo nella modellizzazione e nella definizione delle regole dei firewall.

L’intelligenza artificiale causale e il suo impatto sulla protezione dei dati

Vidya illustra il ruolo dell’intelligenza artificiale nella protezione dei dati e nella resilienza informatica. Commvault utilizza l’intelligenza artificiale predittiva dal 2016 e il prossimo passo sarà l’integrazione con funzionalità di intelligenza artificiale generale. L’evoluzione verso l’intelligenza artificiale causale consente una comprensione più approfondita delle problematiche specifiche dei clienti e l’analisi delle cause alla radice. Ciò permette una risoluzione dei problemi su misura e in tempo reale, riducendo i tempi di inattività e migliorando l’efficienza operativa.

L’intelligenza artificiale porta con sé sia promesse che pericoli

Vidya and Thomas’ conversation provides valuable insights into the exciting and concerning aspects of AI in the enterprise space, highlighting the potential of AI in various industries while acknowledging the challenges. The concept of data firewalls and the evolution toward causal AI offer promising solutions for data protection and cyber resilience. As AI continues to evolve, it is crucial for businesses to strike the right balance between innovation and security to harness its full potential.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

As we continue to celebrate Women’s History Month, I’m honored to take a moment to share my experience as a woman in the technology industry with a passion for inclusion and mentorship.

As Head of Regional Marketing for Switzerland, Austria, SEE, Middle East and Africa, I’ve had the pleasure of being part of Commvault during a pivotal time in its history. In November, we launched our new approach to cyber resilience, and ever since then, we’ve been hard at work with our eventi SHIFT Roadshow and to give our customers an unfair advantage for resilience in the face of ransomware and other advanced threats in today’s hybrid world.

Sebbeneil settore tecnologico sia prevalentemente maschile, especially in the Middle East, I’m fortunate to be part of an incredible team here at Commvault, where everyone is valued, and our unique perspectives are celebrated. I appreciate Commvault’s commitment to a Diversity and Inclusion culture, the collaborative and supportive work environment, and the focus on employee development. These aspects create a workplace where every individual feels valued and encouraged to thrive.

Last month, I was thrilled to to win Commvault’s CEO Living Our Values Award, and that I had been nominated for this honor by my team. This award is an incredible validation of my hard work, dedication, and contributions aligned with Commvault’s values – Connect, Inspire, Care, Deliver – that are the guiding principles shaping my professional journey. It serves as a powerful motivation, reinforcing my commitment to upholding these values and acknowledging my achievements in the most meaningful way.

Tra i momenti di cui vado più fiero ci sono i progetti portati a termine con successo a cui ho lavorato, l’incredibile spirito di squadra e il recente riconoscimento ricevuto con il “CEO Living Our Values Award”. Attribuisco il mio successo al lavoro di squadra, alla collaborazione, al sostegno reciproco e a una comunicazione efficace. L’impegno collettivo del mio team ha svolto un ruolo fondamentale nel raggiungimento degli obiettivi comuni e nel contribuire ai valori che Commvault ha a cuore.

My dedication to Commvault is fueled by the human values, compassionate interactions, collective teamwork, and consistent appreciation demonstrated within the organization. I’m excited about the new era and the new Commvault, eagerly anticipating the fresh opportunities and innovations it will bring, especially with the recent launch of Commvault Cloud, powered by Metallic AI.

This year’s International Women’s Day theme is #InspireInclusion, which is very special to me. Throughout my career, I’ve made it my mission to support and empower women in this industry to believe in themselves. Mentorship is a key aspect of how I’ve worked to empower other women to believe in themselves. A supportive, genuine, connection with a team member can go a long way.

Investire costantemente nelle competenze e nelle conoscenze, costruire una solida rete professionale, mantenere un sano equilibrio tra vita lavorativa e vita privata e accogliere con entusiasmo le sfide e i cambiamenti: questi sono i consigli che mi hanno guidato nel corso della mia carriera. Trasmetto questi stessi consigli alle nuove generazioni nella speranza di lasciare un segno in loro!

For any woman who is just starting her career in technology, my advice to you is to remember the power of confidence. Take a seat at the table instead of waiting for an invitation! I know that sometimes being the only woman in the room can initially feel intimidating, but remember, YOU have a unique perspective that deserves to be heard. Be confident and authentic in who you are and know that you bring immense value in driving innovation. Setting goals and following one’s passion are essential ingredients for success.

Per saperne di più su come lavorare in Commvault,clicca qui.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

In occasione della Giornata mondiale della sindrome di Down, ho voluto condividere il mio percorso personale insieme a mio figlio Jace.

Jace è venuto al mondo nell’ottobre del 2014 e, 12 ore dopo la sua nascita, ci è stata comunicata la diagnosi di sindrome di Down. Jace ha trascorso i primi 10 giorni della sua vita nell’Unità di Terapia Intensiva Neonatale e, in quel periodo, abbiamo dovuto adattarci rapidamente e fare i conti con la sua diagnosi.

I have to admit, I really struggled with Jace’s diagnosis in the beginning. I worried a lot about the future and the fear of the unknown – which I now know are normal thoughts that many parents have when they find out their child has a disability.

Jump forward 9 years, and Jace is rocking it! He is in Grade 4 and an active participant in his class.  Outside of school, he loves horseback riding and participating in sports. He currently plays hockey every weekend with a great organization, la SuperHEROS. They provide the ability to play hockey to kids with disabilities who don’t normally have the chance. He also plays in a similar baseball league in the summer.

Commvault has been incredibly supportive over the years, giving me the flexibility I need to help Jace. And joining our CapAbilities Employee Resource Group (ERG) has been an amazing way for me to share my story with my fellow Vaulters and raise awareness. Our CapAbilities ERG’s mission is to create a safe and empathetic space where Vaulters with disabilities, caregivers, and allies can openly and honestly have discussions and drive change together.

This past November, Commvault once again sponsored a table at PREP’s annual fundraiser, Let’s Talk Hockey, a night with members of the Calgary Flames NHL team. I attended the event with some of my team members and customers, too – all proceeds went directly to the PREP foundation. Jace would not be in the place he is today without the support he receives from PREP.

On World Down Syndrome Day, I’m celebrating by wearing my funky or mismatched socks to recognize how Jace’s extra chromosome makes him extra perfect in our eyes. My goal is to continue to spread awareness and provide opportunities for Jace, and other children like him, to live their best lives and make a difference in this world. Every life deserves to be celebrated.  

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Qui a Commvault, il benessere continua a essere una priorità assoluta per tutta la nostra comunità globale di Vaulter.Come ho già detto all’inizio di quest’anno, prendersi cura del proprio benessere ci permette di dare il meglio di noi stessi sia a casa che al lavoro!

Over the years, we’ve continued to evolve our wellness offerings to best support our Vaulters and their families with programs they need for life’s most important moments and stages. Our priority has been, and always will be, to provide inclusive support for our employees and their families. Having this type of support and the right wellness resources allows our Vaulters to thrive.

So, in honor of Women’s History Month and International Women’s Day, I want to talk about how we’re supporting the women of Commvault with specific wellness offerings this month and beyond!

On International Women’s Day, our Women in Technology Employee Resource Group hosted a women’s wellness event in our Australia office, which was also available to all our Vaulters for virtual participation. The event featured guest speaker Annerie Feldman, a Sydney-based health and wellness coach. Annerie spoke about the challenges women often face that impact their wellness, and how women can overcome these obstacles to feel empowered and confident through prioritizing self-care and gaining control of one’s wellness.

Additionally, our India team has organized a breast cancer detection and awareness initiative for our female Vaulters this month. In partnership with Enable India, a non-profit organization working for economic independence and dignity of persons with disability, our Vaulters will have the opportunity to learn more about the importance of breast cancer detection and make connections with Enable India’s knowledgeable female representatives who are visually impaired.

Oltre agli eventi celebrativi e di sensibilizzazione organizzati nel mese di marzo, offriamo anche una serie di benefici per il benessere dei nostri Vaulters negli Stati Uniti, quali servizi di pianificazione familiare, assistenza alla fertilità, assistenza ai familiari e altro ancora. Il nostro partner per la creazione di una famiglia, Maven, è a disposizione di tutti i nostri Vaulters negli Stati Uniti. Maven garantisce l’accesso a cure di altissimo livello in materia di fertilità, maternità, pediatria e menopausa, oltre a offrire assistenza 24 ore su 24 da parte di professionisti specializzati nella creazione di una famiglia, un team dedicato di consulenti sanitari e una vasta raccolta di risorse educative clinicamente validate. La nostra partnership con Maven ci consente inoltre di offrire opportunità di rimborso ai membri di Vault che stanno mettendo su famiglia tramite adozione o accordi di genitorialità tramite maternità surrogata.

Oltre a Maven, offriamo assistenza tramite Fertility Solutions attraverso il nostro partner medico statunitense, UnitedHealthcare. Questa offerta fornisce orientamento e sostegno empatico per aiutare a orientarsi nelle complesse decisioni terapeutiche, ridurre lo stress finanziario ed emotivo e raggiungere gli obiettivi di gravidanza con costi medici inferiori.

We know our Vaulters and their families can face challenges when navigating child, elder, and pet care, so we’ve also partnered with Bright Horizons to help our U.S. Vaulters manage their day-to-day life efficiently and safely by finding care when they need it, both at high-quality centers and in-home.

Siamo orgogliosi di promuovere un ambiente di lavoro in cui tutti i nostri team sentano che il loro benessere è una priorità. Offrire risorse specifiche alle nostre colleghe di Vault è fondamentale per promuovere la nostra cultura inclusiva e la diversità della nostra forza lavoro. In fin dei conti, prendersi cura del proprio benessere è essenziale per permetterci di dare il meglio di noi stessi, sia per noi stessi che per gli altri!

Clicca qui to learn more about what it’s like to work at Commvault.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Cloud computing has become essential for businesses of all sizes, offering scalability, flexibility and cost savings. However, managing cloud environments can be complex and chaotic, leading to increased costs, security risks and performance issues. In this blog post, we’ll explore the challenges of cloud computing and provide practical strategies to overcome them. Following these strategies can help you tame cloud chaos and optimize your cloud computing experience. And you’ll learn about Commvault® Cloude come può aiutarti a raggiungere il successo nel cloud.

Il caos del cloud computing

Il panorama del cloud computing è in continua evoluzione, con nuovi servizi e fornitori che emergono regolarmente. Ciò può rappresentare un vantaggio significativo per le aziende, poiché consente loro di accedere a una gamma più ampia di opzioni e di scalare le proprie operazioni in modo rapido e semplice. Tuttavia, questa complessità può anche portare al caos, poiché le aziende faticano a gestire più ambienti cloud e a garantire che i propri dati e le proprie applicazioni siano sicuri e conformi alle normative.

Una delle sfide più grandi del cloud computing è il rischio di violazioni dei dati e di incidenti di sicurezza. I fornitori di servizi cloud hanno la responsabilità di garantire la sicurezza delle proprie infrastrutture, ma anche le aziende devono adottare misure per proteggere i propri dati e le proprie applicazioni. Ciò comporta l’implementazione di controlli di accesso rigorosi, la crittografia dei dati e il monitoraggio delle attività sospette.

Un’altra sfida è rappresentata dal rischio di problemi di prestazioni. I fornitori di servizi cloud offrono diversi livelli di servizio e le aziende devono scegliere quello più adatto alle proprie esigenze. Si tratta di un processo che può rivelarsi complesso, poiché occorre tenere conto di fattori quali la larghezza di banda, la latenza e la capacità di archiviazione.

Infine, c’è l’investimento vero e proprio. Le aziende devono valutare attentamente i costi dei servizi cloud, tra cui quelli relativi all’infrastruttura, al software e all’assistenza. Devono inoltre tenere conto dei costi legati alla migrazione dei propri dati e delle proprie applicazioni sul cloud.

Nonostante queste sfide, il cloud computing offre una serie di vantaggi significativi. Tra questi figurano una maggiore agilità, scalabilità e risparmi sui costi. Comprendendo le sfide poste dal cloud computing e adottando misure per mitigarle, le aziende possono sfruttare la potenza del cloud per raggiungere i propri obiettivi.

Il ransomware e il cloud

Ransomware is a type of malware that encrypts files on a victim’s computer and then demands a ransom payment in exchange for decrypting the files. Ransomware attacks can be devastating for businesses, as they can lead to lost data, downtime and financial losses.

Ransomware attacks have become increasingly prevalent in recent years, and cloud environments aren’t immune to this threat. In fact, cloud environments can be particularly vulnerable to ransomware attacks, as they often contain large amounts of sensitive data and are accessible from anywhere in the world. It has been reported that 82% of breaches involve data stored in the cloud – public, private or multiple environments.[1]

Data fragmentation is another key reason ransomware can be hard to defend against – the more widespread your data is across multiple cloud providers, the harder it is to protect. And if you use multiple data protection tools, the complexity is only driven up. As such, more than 90% of respondents surveyed indicated a level of concern that their organization will suffer a ransomware attack – and nearly 40% indicated being extremely concerned. Practically all (97%) indicated concern about the ramifications/fallout resulting from a ransomware attack.[2]

Let’s look at how you can make sense of the chaos these challenges bring in today’s hybrid cloud world.

Rimani protetto con il SaaS

Le applicazioni SaaS (Software as a Service) sono un bersaglio molto diffuso per gli attacchi ransomware, poiché vengono spesso utilizzate per archiviare dati sensibili. Le aziende possono adottare diverse misure per proteggere le proprie applicazioni SaaS dagli attacchi ransomware, tra cui:

  • Implementing strong security measures. This includes using strong passwords, enabling two-factor authentication and keeping software up to date.
  • Using a cloud-based data protection solution. This type of solution can help protect your data from ransomware attacks by providing secure storage and backup capabilities.
  • Educating employees about ransomware. Make sure your employees are aware of the risks of ransomware and how to protect themselves from it.
  • Implementing a security incident response plan. This plan should outline the steps that you’ll take in the event of a ransomware attack.
  • Working with a cybersecurity expert. A cybersecurity expert can help you assess your risks and develop a plan to protect your business from ransomware attacks.

By taking these steps, you can help protect your business from ransomware attacks and keep your data safe. They are all proven best practices in defending against today’s threats – and tomorrow’s.

Pensa prima all’ibrido

È molto probabile che i vostri dati siano archiviati sia in un cloud privato che in uno o più cloud pubblici. Adottare un approccio basato sul cloud ibrido può aiutare le aziende a risparmiare denaro e ad avere un maggiore controllo, utilizzando l’ambiente cloud più adatto a ciascuna attività. Ad esempio, le aziende possono utilizzare un cloud pubblico per i carichi di lavoro che richiedono scalabilità e flessibilità, e un cloud privato per quelli che richiedono maggiore sicurezza e controllo.

Hybrid cloud allows data to move easily between clouds and on-premise environments. This gives businesses the ability to move data where they need it most. This can be especially important for businesses that have workloads that span multiple locations. Look for “any-to-any portability” when considering how to best protect your workloads.

La gestione e il monitoraggio di tutti gli ambienti cloud da un’unica piattaforma possono inoltre aiutare le aziende ad avere una visione più chiara della propria infrastruttura IT e a lavorare in modo più efficiente. Ciò è possibile grazie a una serie di strumenti, quali le piattaforme di gestione del cloud e gli strumenti di monitoraggio del cloud.

Using hybrid cloud-native applications can make businesses more agile and scalable. This means they can create and launch applications that can work on different cloud platforms. This can help reduce development costs and time to market – and improve application performance and reliability.

Avvia la pianificazione della migrazione

Data is constantly on the move – depending on how your organization’s needs change, you’ll surely need to migrate data between clouds. As a result, planning is an important part of any cloud migration project. It helps organizations to identify potential risks and challenges, and to develop a strategy for mitigating them. The following are some of the key steps involved in the planning process:

  • Identify the data and applications that need to be migrated: This can be done by conducting an inventory of all of the organization’s data and applications.
  • Evaluate if the data and applications can work with the chosen cloud: Working with the cloud provider to ensure that the data and applications are supported.
  • Develop a migration plan: The migration plan should include:
    • L’ordine in cui verranno migrati i dati e le applicazioni.
    • I tempi stimati.
    • Le risorse necessarie.
    • I rischi legati alla migrazione.
  • Testing: Before implementing the migration plan, it’s important to test it in a non-production environment to identify any potential problems and make sure that the data and applications are migrated successfully. Ensure you’ve got access to a ambiente pulitoper eseguire questi test ed effettua verifiche a cadenza regolare.
  • Implement the migration plan: Once implemented, the migration process should be monitored closely to ensure that there are no problems.

Valuta in che modo l’intelligenza artificiale può aiutarti

Con tutte queste best practice in fase di implementazione, potreste chiedervi se esista un modo più semplice per metterle in pratica, e la risposta è sì. L’IA generativa si estende anche alla protezione dei dati eCommvault è stata tra le prime aziende a introdurre questa funzionalità. Arlie – short for “Autonomous Resilience” – is our AI assistant, available 24/7 in the Commvault Cloud platform. Arlie responds to inquiries in plain, simple language, quickly consolidates information and provides users with actionable responses to help save time, respond to threats and improve cyber resiliency.

What benefits does Arlie deliver? Every cyber resilience team is stretched thin and asked to “do more with less.” With Arlie, Commvault Cloud equips users with AI capabilities that enhance their data protection experience. Arlie empowers users across all skill levels to navigate complex tasks, improving overall efficiency and cost-effectiveness. With Arlie, users can do more, faster, without the need for extensive platform knowledge, saving time on routine tasks, quickly responding to threats and enhancing their overall cyber resiliency.

Commvault Cloud: la soluzione al caos del cloud

We’ve covered a lot here today, so you may be wondering where to start. The standard, con l’ulteriore vantaggio dell’isolamento dagli altri tenant. Questa opzione di distribuzione SaaS dedicata fornisce: is an AI-enabled, powerful and secure cloud-based data protection solution that can help businesses of all sizes overcome the challenges of cloud computing. Commvault Cloud helps you manage your data in all your clouds and has strong security measures to help keep your data safe from unauthorized users. Additionally, it provides tools to help you save money and enhance your cloud’s performance.

Commvault Cloud’s comprehensive data protection features are deep – they include data backup, recovery, archiving and replication. Commvault Cloud also provides advanced security features such as encryption, access control and auditing. It’s also scalable and flexible, so you can easily add or remove storage as needed. It’s a great solution to the data fragmentation issue and allows you to protect your data estate under a single pane of glass.

If you are looking for a powerful and secure cloud-based data protection solution, look no further – download our buyer’s guideper trovare ulteriori risposte alle vostre domande sul “caos del cloud”. Commvault Cloud può aiutarvi a superare le sfide del cloud computing e garantire che i vostri dati siano al sicuro, protetti e accessibili, indipendentemente da dove si trovino.


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

L’intelligenza artificiale ha suscitato grande entusiasmo grazie alla sua significativa influenza sul settore della protezione dei dati. Lo scorso anno, la rapida espansione dell’IA generativa ha portato a una rivoluzione in numerosi settori, spingendo i leader del settore a valutare il suo potenziale per migliorare le proprie operazioni. Commvault, forza pionieristica nell’innovazione, è stata la prima ad introdurre questa funzionalità, utilizzando l’IA per facilitare un’azione tempestiva ed efficiente. Vi presentiamo Arlie, il vostro assistente IA disponibile 24 ore su 24, pronto a rispondere alle vostre domande con un linguaggio chiaro e diretto, offrendo soluzioni pratiche per risparmiare tempo, affrontare rapidamente le minacce e migliorare la resilienza informatica.

Do More, Faster, with Speed & Certainty

Every team is stretched thin and asked to do more with less. But the pace and volume of work doesn’t decrease. Arlie empowers users of all skill levels to navigate complex tasks without the need for extensive platform knowledge – enabling you to do more, faster.

Accedi a un’ampia gamma di funzionalità di intelligenza artificiale tramite una barra di ricerca globale, tra cui:

  • Real-time insights into operational failures, prioritizing what matters most to you. No more sifting through filters and reports to find the most pressing information – Arlie delivers the most essential information to your fingertips.
  • A “no-code” way to build an integration or code an action where you don’t have to be an expert. Type a description of what you want to do, and Arlie will generate the code on the spot with Commvault APIs.
  • Context-sensitive, guided product walkthroughs that makes it easier for you to set up, customize and tune Commvault Cloud to your specifications. Ask “how to” questions, and get step-by-step documentation complete with annotated screenshots.
  • Risoluzione avanzata dei problemi per individuare le criticità operative e ottenere soluzioni e consigli di ottimizzazione in tempo reale, al fine di migliorare la resilienza informatica. Risolvi i problemi più rapidamente grazie a riepiloghi delle soluzioni di facile comprensione e a passaggi concreti da seguire.

Come funziona

Arlie è progettato per fornire approfondimenti in tempo reale e indicazioni concrete su come ottimizzare la propria resilienza informatica. Dietro le quinte, Arlie si interfaccia con modelli di IA generativa che consolidano informazioni e report, fornendo risposte personalizzate e concrete alle richieste. Hai bisogno di verificare un punto di Recovery sicuro per i sistemi critici? Basta chiedere ad Arlie. Vuoi programmare un’azione? Guarda come Arlie genera codice in pochi secondi utilizzando le API di Commvault.

https://play.vidyard.com/eEq4ACirHDh6D7RCZLPhMao?

Arlie si integra perfettamente nella Commvault Cloud Console, rendendola facilmente accessibile senza dover uscire dal prodotto. Che tu sia un nuovo utente o un esperto di lunga data, Arlie ti trasforma in un utente avanzato fornendo risposte rapide, accurate e concrete alle domande relative ai tuoi dati e al tuo ambiente.

Per saperne di più su come Arlie sta utilizzando l’IA generativa per aiutarti a rafforzare e accelerare la tua strategia di resilienza, visitail sito Commvault.com/Meet-Arlie.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Nel 2024 le aziende adotteranno strategie di gestione del rischio più proattive, non solo per cercare di contrastare le minacce dolose e le violazioni dei dati, ma anche per conformarsi con successo al numero crescente di normative in materia di sicurezza informatica.

Con il notevole ampliamento del panorama delle minacce, soprattutto in questa era dell’intelligenza artificiale, crescono sempre più le esigenze per le aziende di garantire la trasparenza sugli incidenti di sicurezza e di rendere pubblici attacchi e violazioni. Queste due realtà spingeranno le aziende a evolvere le proprie strategie di sicurezza informatica per diventare resilienti alle minacce informatiche.

Perché proprio ora la resilienza informatica?

Cyber resilience is coming to the forefront for many organizations around the global as regulators and legislators look to bolster transparency when it comes to cybersecurity events and preparedness.

“They want corporate executives to articulate whether and how cybersecurity is part of the company’s business strategy, governance processes, financial planning, and capital allocation,” said Melissa Hathaway, president of Hathaway Global Strategies and chair of Commvault’s Cyber Resilience Council, in our 7 Emerging Trends in Cyber Resilience”.

La normativa sulla sicurezza informatica della SEC, Information Security Registered Assessors Program (IRAP) in Australia, DORA in the EU, and even state-level rules like New York’s Codes, Rules, and Regulations (23 NYCRR Part 500) are challenging companies to adopt transparency.

In questa sede esaminiamo i requisiti normativi, sia quelli già in vigore che quelli emergenti, che i responsabili della sicurezza informatica devono padroneggiare per garantire che le aziende di cui si occupano raggiungano sia la conformità normativa che la resilienza informatica.

SEC

La recente norma della SEC impone ai soggetti registrati di rendere noti gli incidenti rilevanti in materia di sicurezza informatica. Le conseguenze di tale norma rendono necessario che i responsabili della sicurezza e i dirigenti di alto livello agiscano in perfetta sintonia per quanto riguarda gli incidenti di sicurezza informatica e la loro segnalazione. Inoltre, la norma della SEC richiede alle società di illustrare, nei documenti annuali presentati, in che modo la sicurezza informatica e la relativa supervisione si inseriscano nel loro programma generale di gestione dei rischi.

“Whether a company loses a factory in a fire – or millions of files in a cybersecurity incident – it maybe material to investors,” SEC Chair Gary Gensler said in a dichiarazione.

A quasi un quarto del 2024, sono state presentate alla SEC alcune comunicazioni 8-K relative a incidenti informatici, e le società con esercizio finanziario chiuso al 31 dicembre stanno iniziando a pubblicare i bilanci 10-K con formulazioni aggiornate in materia di resilienza informatica.

Regolamento 23 NYCRR, Parte 500

Il Dipartimento dei Servizi Finanziari di New York (NYDFS) ha emanato il Secondo Emendamento al Capitolo 23 del Codice, delle Norme e dei Regolamenti di New York (23 NYCRR Parte 500) al fine di rafforzare e proteggere i sistemi informativi e finanziari dalla crescente diffusione e sofisticazione degli attacchi informatici. La legge impone agli istituti finanziari soggetti alla giurisdizione del NYDFS di attuare e mantenere un programma di sicurezza informatica che includa procedure volte a salvaguardare i dati sensibili dei clienti dalle minacce alla sicurezza e a gestire i rischi informatici.

Tra i requisiti di conformità al 23 NYCRR 500 figurano diversi obiettivi che le aziende soggette al NYCRR 500 devono impegnarsi a soddisfare. Innanzitutto, il regolamento richiede alle entità di istituire e mantenere un programma di sicurezza informatica volto a salvaguardare la riservatezza, l’integrità e la disponibilità dei propri sistemi informatici. Il programma dovrebbe gestire i rischi in diverse aree operative, tra cui la sicurezza delle informazioni, la governance dei dati, l’inventario delle risorse, il funzionamento dei sistemi, la sicurezza dei sistemi e delle reti, la privacy dei dati dei clienti e altro ancora.

La legge impone alle aziende di effettuare test di penetrazione e valutazioni delle vulnerabilità. E l’elenco degli obblighiper i soggetti interessati non finisce qui.

“DORA

Anche i responsabili della sicurezza informatica e i dirigenti aziendali stanno seguendo con attenzione l’avvicinarsi delle scadenze previste dalDigital Operational Resilience Act(DORA).

Il DORA è entrato in vigore il 16 gennaio 2023, con un periodo di attuazione di due anni. Gli enti finanziari interessati dovranno conformarsi al regolamento entro il 17 gennaio 2025. Sebbene la legge sia rivolta alle organizzazioni dell’Unione europea (UE), anche i soggetti al di fuori dell’UE operanti nei settori finanziario e delle tecnologie dell’informazione e della comunicazione (TIC) devono adoperarsi per allinearsi al DORA qualora forniscano servizi TIC essenziali a enti finanziari con sede nell’UE.

Il DORA istituisce un quadro normativoper la resilienza operativa digitale, in base al quale tutti i soggetti interessati devono adoperarsi per resistere, reagire e riprendersi da interruzioni e minacce legate alle tecnologie dell’informazione e della comunicazione (TIC). La legge mira a prevenire e mitigare le minacce informatiche. Il DORA si articola in cinque pilastri fondamentali, che sono i seguenti:

  • Gestione del rischio ict
  • Segnalazione di incidenti relativi alle TIC
  • Test di resilienza operativa digitale
  • Rischio di terzi nel settore delle TIC
  • Condivisione delle informazioni

DORA mira a migliorare la resilienza delle infrastrutture digitali critiche di fronte alle minacce e agli attacchi alla sicurezza informatica. Allineandosi ai principi di DORA, le organizzazioni si avvicinano al miglioramento del proprio profilo di resilienza informatica.

Diventa resiliente alle minacce informatiche

If the ever-expanding threat landscape isn’t enough to drive home the need to become cyber resilient, the flurry of new regulations is hammering the point. Businesses must understand what is required of them in terms of reporting.

Per molte aziende, l’adeguamento alle innumerevoli normative richiederà che le competenze in materia di sicurezza informatica non si limitino al CISO, ma siano diffuse in tutta l’organizzazione. Ciò significa che i responsabili della sicurezza devono collaborare con i dirigenti di livello C e con il consiglio di amministrazione per garantire trasparenza e resilienza informatica.

For more information on how Commvault Cloud can help your organization’s cyber resilience journey, visit: https://www.commvault.com/platform.


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

In qualità di co-sponsor esecutivi del nostroWomen in Technology Employee Resource Group (ERG), we’re thrilled to celebrate International Women’s Day across our global Vaulter community! This year’s global theme, #InspireInclusion, is already engrained in Commvault’s culture and the everyday efforts of our ERG. Our Women in Technology ERG brings together both women and allies to elevate and advance gender equality in technology and celebrate the inspiring women of Commvault who are driving our innovation and growth every day.  

Check out this video to see our Vaulters across the world honor International Women’s Day and this year’s global theme!  

https://play.vidyard.com/RCAPied3RuLZVBKhdSgvnn

Today and beyond, we continue to support gender diversity initiatives and invest in our women leaders at all levels. This month, in honor of International Women’s Day and Women’s History Month, Commvault will be hosting our annual Confident U sessions, a women’s leadership development workshop. This is an opportunity for our female Vaulters to truly feel inspired to reach their full potential, as they learn how to transmit confidence, conquer self-doubt, and silence their inner critic to advance their career path.  

Supporting and empowering the women of Commvault is a key component of our DEI strategy. We continue to work together to create a world where difference is valued and belonging is a non-negotiable both inside and outside our workplaces.   

In honor of International Women’s Day, we encourage you to think about how you can #InspireInclusion with those around you.  

And to all the incredibly inspiring and talented women at Commvault – thank you for continuing to make an impact every day!  

Click here to learn more about what it’s like to work at Commvault. 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Con la costante evoluzione delle minacce informatiche e la crescente sofisticazione degli attacchi informatici, le aziende devono adottare un approccio proattivo per proteggere i propri dati, sistemi e operazioni da potenziali violazioni e interruzioni. I sistemi di allerta precoce svolgono un ruolo fondamentale nel mitigare il rischio di attacchi zero-day, minacce alla catena di approvvigionamento e sfruttamento delle vulnerabilità, che rappresentano aspetti chiave della resilienza informatica.

Ad aggravare la minaccia sono i sistemi legacy, i dispositivi IoT, le interdipendenze tra le applicazioni e la proliferazione dei dati, che rendono l’applicazione delle patch alle vulnerabilità un’attività tediosa e dispendiosa in termini di tempo per i team IT, allungando al contempo i periodi di esposizione al rischio. Due recenti incidenti che hanno coinvolto i software MOVEit e SysAid sono esempi lampanti della crescente minaccia rappresentata dallo sfruttamento delle vulnerabilità e dagli attacchi alla catena di approvvigionamento.

L’attacco a MOVEit e la vulnerabilità di SysAid: un campanello d’allarme

In May 2023, the CL0P threat group capitalized on a critical vulnerability (CVE-2023-34362) in MOVEit, a widely-used secure file transfer application. This incident, now known as the ““attacco MOVEit,” has been labeled as the “most impactful zero-day attack of 2023.” più devastante del 2023”. [PL2] Despite early indicators of experimentation with this vulnerability dating back to 2021, the connection between initial signs and the widespread “attacco MOVEit was established only after the damage had been done.

A novembre, lo stesso gruppo di hacker ha colpito nuovamente, prendendo questa volta di mira i sistemi on-premise di SysAid, un’applicazione per servizi IT e help desk. Sfruttando una vulnerabilità zero-day diversa, gli aggressori hanno ottenuto l’accesso non autorizzato a dati sensibili e hanno compromesso operazioni aziendali critiche.

L’importanza dei sistemi di allerta precoce

Gli attacchi che sfruttano le vulnerabilità di MOVEit e SysAid evidenziano la necessità fondamentale per le organizzazioni di adottare una strategia di resilienza informatica che includa l’implementazione di un solido sistema di allerta precoce basato sul cyber deception, al fine di individuare e rispondere tempestivamente alle potenziali minacce. Aggiungendo livelli di rilevamento ed esche che simulano obiettivi di alto valore in punti strategici della rete e degli archivi di dati, i team di sicurezza possono essere informati di attività sospette e indicatori di compromissione (IOC) prima che un aggressore raggiunga iveriobiettivi di alto valore, riducendo in modo significativo il rischio di cadere vittima di attacchi zero-day.

L’adozione di un sistema di allerta precoce efficace offre alle organizzazioni numerosi vantaggi, tra cui:

  1. Proactive Threat Detection: Early warning systems shield sensitive data and business-critical systems from suspicious activities, helping organizations to identify potential threats before they can escalate into full-blown attacks.
  2. Rapid Response: By providing early alerts, organizations can respond swiftly to contain and mitigate threats, minimizing the potential impact on their operations and data.
  3. Reduced Downtime: Early detection and response can help organizations minimize the blast radius and limit downtime and disruptions caused by cyberattacks, helping ensure business continuity and productivity.
  4. Enhanced Security Posture: Early warning systems with deception capabilities help organizations identify and address vulnerabilities promptly, improving their overall security posture and reducing the risk of successful attacks.
  5. Compliance and Regulatory Adherence: Many industries and regulations require organizations to have robust security measures in place and mitigate known vulnerabilities promptly to protect sensitive data and comply with data protection laws. For example,questo post del blogillustra come i controlli di sicurezza e di intelligence di Commvault Cloud aiutino le organizzazioni a conformarsi allo standard PCI DSS.

Perché Commvault Cloud

Commvault offre una strategia completa di resilienza informatica che consente alle aziende di ogni dimensione e settore di proteggere i propri sistemi e dati dagli attacchi malintenzionati. Grazie alla piattaforma Commvault, le organizzazioni possono migliorare il proprio livello di Readiness informatica adottando misure proattive, anziché limitarsi a reagire a posteriori per riparare i danni già causati.

Scarica il nostro white paperper scoprire come il sistema di allerta precoce di Commvault sfrutti tecniche avanzate di cyber deception per fornire avvisi tempestivi che smascherano gli IOC relativi a sfruttamenti di vulnerabilità simili a quelli di MOVEit e SysAid, attacchi alla catena di fornitura e minacce zero-day sconosciute.


More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

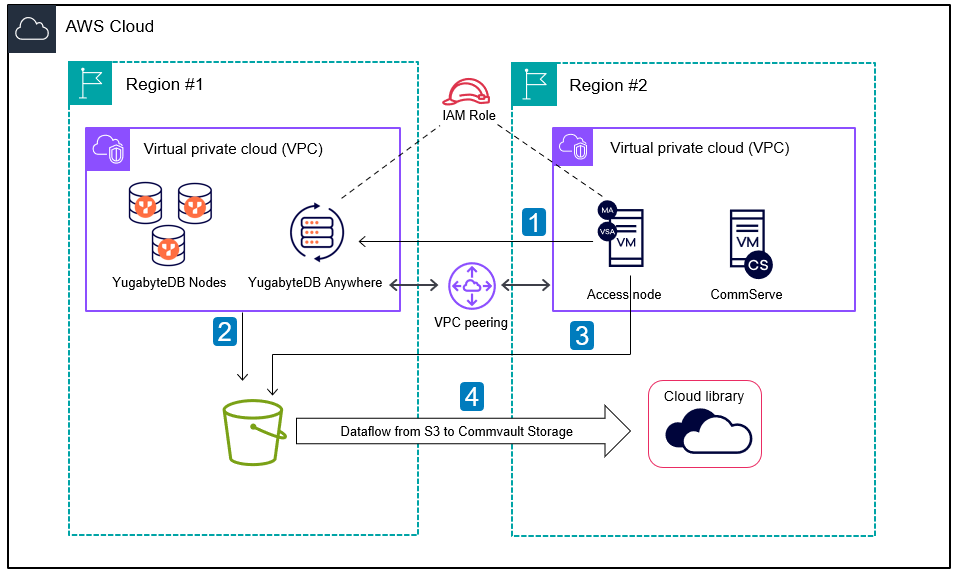
Siamo lieti di annunciare che Commvault Cloud ha aggiunto il supporto per YugabyteDB, un database SQL distribuito noto per la sua scalabilità orizzontale e la resilienza integrata, che consente alle organizzazioni di sviluppare applicazioni coerenti a livello globale.

Grazie a questa integrazione, i clienti possono contare su una protezione completa dei propri ambienti YugabyteDB. In caso di guasti o danneggiamenti logici che interessano più regioni, Commvault Cloud garantisce un Recovery rapido, consentendo di gestire e coordinare facilmente i carichi di lavoro YugabyteDB dalla Commvault Cloud Console.

La protezione dei dati sensibili nelle applicazioni distribuite è fondamentale nell’odierno panorama aziendale in continua evoluzione. Sebbene YugabyteDB sia progettato per gestire una serie di guasti, è essenziale disporre di una soluzione dedicata alla sicurezza e al Recovery dei dati per salvaguardare i dati critici da guasti gravi, minacce in continua evoluzione e requisiti normativi e di conformità. È qui che entra in gioco Commvault Cloud, offrendo una resilienza informatica senza pari.

L’integrazione tra Commvault Cloud e YugabyteDB offre le seguenti funzionalità fondamentali:

  • Backup all namespaces in AWS and Azure: You can configure full and incremental backups, schedule backups, and perform individual table-level backups of YCQL and individual database backups of YSQL.
  • Browse and restore namespaces: You can easily restore individual databases and tables in place to the original cluster or out-of-place to another cluster.
  • Job monitoring and manageability: The Commvault Cloud console provides simple workflows to configure, manage, and monitor the status of any backup or restore process.

Insieme, Commvault Cloud e YugabyteDB aiutano le organizzazioni a sviluppare, modernizzare e proteggere le applicazioni critiche per il business da minacce e guasti in continua evoluzione.

Per iniziare a utilizzare YugabyteDB e Commvault Cloud, visita ilsito documentation.commvault.com/YugabyteDB.

L’elenco completo dei database supportati da Commvault Cloud è disponibilequi.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Today we are celebrating quite a lot! Not only is it Employee Appreciation Day, but it’s also the start of Women’s History Month.  

Employee Appreciation Day is a great reminder to celebrate each other, but, for me, gratitude is always top of mind. Every day, I am so inspired by our incredible Vaulter community across the world. The innovation, care, and collaboration I see daily from our teams is what makes working at Commvault such an amazing experience. Showing that we care and appreciate one another is a core component of our culture, in fact, it’s part of our core values.  

 And speaking of our values, abbiamo recentemente annunciato our FY24 Q3 CEO Living Our Values Award winners, to recognize Vaulters who have done an exemplary job of living our values every day. With Women’s History Month kicking off today, and International Women’s Day right around the corner, I want to give a special shout-out to all the women who recently won this award. I am so appreciative of Amy, Jill, Kristen, Lena, and Prashanti for continuing to make an impact and leading by example. Thank you for continuing to inspire us all!   

Amy Ngian  

Jill Van Sickle  

Kirsten Krsulj  

Lena Halbourian 

Prashanti Koti  

Today is also an important reminder that gratitude should always be top of mind. I’ve always been so moved by the late Fred Rogers, who accepted his Lifetime Achievement Award at the Emmys in 1997 by stressing the importance of gratitude. That day, he asked this of the audience, “Take 10 seconds to think of the people who have helped you become who you are. Those who have cared about you and wanted what was best for you in life”. On that note, I’d like to ask the following of anyone reading this blog: 

  • First, take 10 seconds (or more!) to think about the people who have helped you get to where you are today. It can span beyond your colleagues. 
  • Second, take another few minutes to actually reach out and thank them. We all know that a little appreciation, even if it’s just a quick text or phone call, can go a long way.  

The power of support is truly incredible. Happy Employee Appreciation Day to all and thank you again to our amazing Vaulters for everything you do! 
 

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

The New York Department of Financial Services (NYDFS) is proactively responding to escalating cyber threats with the Second Amendment to Chapter 23 of the New York Codes, Rules, and Regulations (23 NYCRR Part 500). This amendment is a strategic move to fortify information and financial systems against the increasing prevalence and sophistication of cyberattacks. The call for additional controls to manage cyber risks cost-effectively is louder than ever.

As we dissect the intricacies of this regulatory change, it becomes apparent that organizations need more than a mere rulebook; they require a robust solution ready to confront cyber challenges head-on. This is where Commvault® Cloud, powered by Metallic® AI, enters the game to help meet regulatory requirements while elevating cyber resilience. Now is the time for organizations to embrace the future with Commvault Cloud.

Approfondiamo i punti salienti dell’emendamento, analizzando in che modo le soluzioni innovative di Commvault Cloud si allineino perfettamente ad alcuni requisiti fondamentali.

Resilienza informatica attraverso l’intelligente Risk Analysis dei rischi [Sezioni 500.9(a), 500.2(c)]

Commvault Cloud’s Risk Analysisdi Commvault Cloud va oltre i metodi tradizionali. Identifica e classifica sistematicamente i dati sensibili sia nelle sedi locali che in quelle cloud. Analizzando diversi tipi di dati, comprese le immagini, Risk Analysis individua i dati ridondanti, obsoleti e irrilevanti (ROT). Affronta le problematiche legate alla proliferazione e alla duplicazione dei dati, oltre a facilitare una rapida valutazione dei rischi basata sulla sensibilità e sull’impatto dei dati. L’accesso ai file e i privilegi relativi ai dati sensibili possono essere sottoposti a revisioni approfondite e rapide, al fine di garantire misure di sicurezza solide e di orientare in modo intelligente la progettazione del programma di sicurezza informatica richiesto dall’emendamento.

Monitoraggio e formazione basati sull’intelligenza artificiale [Sezione 500.14(2)]

Oltre alle funzionalità di Risk Analysis, Commvault Cloud introduceSicurezza IQper fornire un dashboard completo sullo stato della sicurezza. Fornisce un punteggio dinamico per aiutare le organizzazioni a identificare e mitigare i rischi di sicurezza.Commvault Cloud Threatwisepotenzia ulteriormente le funzionalità di rilevamento e monitoraggio, consentendo l’individuazione tempestiva dei tentativi di infettare risorse critiche con codice dannoso. Se attivato, il sensore Network Intelligence monitora attivamente le minacce in uscita e le connessioni a botnet o URL dannosi e può contribuire al monitoraggio del traffico web sospetto, come previsto dall’emendamento.

Controlli di accesso “zero-trust” [Sezione 500.7(a)]

Commvault Cloud va oltre i controlli di accesso convenzionali. Introduce controlli “zero-trust”, tra cui l’autenticazione a più fattori (MFA), l’autorizzazione multipartner (MPA), la gestione degli accessi privilegiati (PAM), il controllo degli accessi basato sui ruoli (RBAC) con sicurezza granulare e il Security Assertion Markup Language (SAML). Fornisce inoltre registri di audit dettagliati quando necessario. Queste funzionalità di sicurezza complete consentono di regolare con precisione i privilegi di accesso per allinearli ai più elevati standard di sicurezza.

Crittografia avanzata per la massima sicurezza [Sezione 500.15(a)]

Commvault Cloud soddisfa i requisiti di crittografia più rigorosi del settore, garantendo il trasferimento sicuro dei dati in transito tramite canali autenticati e la crittografia dei dati inattivi per un’archiviazione protetta. Grazie alla conformità allo standard FIPS 140-3 (AES 256) e alle chiamate API autenticate tramite REST TLS 1.3 su HTTPS, la soluzione garantisce la conformità agli standard di crittografia del settore indicati nell’emendamento.

Notifica relativa a un evento di sicurezza informatica, al sistema di allerta precoce e alle tecniche di cyber-inganno volte a facilitare l’accertamento di un incidente informatico entro 72 ore [Sezione 500.17(a)]

With Commvault Cloud Threatwise, financial entities can receive early warning signals alerts using advanced deception techniques that can identify lateral movements in the network, reconnaissance, or attempts to infect backup workloads and production environments. Additionally, The Anomaly framework can send alerts on unusual file activity, aiding in threat identification within backups. Integrations with SIEM and XSOAR can assist in disabling data aging or users at risk. With Commvault Cloud Threatwise, financial entities can create decoys of servers, endpoints, financial decoys assets such as Swift & ATMs, networking equipment, and more, effectively mimicking financial entity assets. This proactive approach contributes to reducing response times, improving threat intelligence correlations and remediation, thus eventually assisting IRT to shorten the determination time for a cyber incident.

Test di risposta agli incidenti [Sezione 500.16]

The amendment mandates: “Each covered entity shall periodically,but at a minimum annually,test incident response and BCDR plans ….” Commvault Cloud Backup and Recovery capabilities,along with Commvault Cloud Auto Recovery,Commvault AirGap,and CommServe Recovery Validation Service provide a comprehensive and complete timely solution for this requirement. It simplifies the process for organizations to automate clean recovery of the backup infrastructure and application group recoveries,allowing periodic recovery testing in a clean environment in the cloud,which can be used for cyber forensics as well.

You can restore and support BCDR plans as well as test without impacting production environments. Moreover, the amendment requires that “backups shall be adequately protected from unauthorized alterations or destruction.” Commvault AirGap, together with the zero-trust architecture, control, data, and storage planes separation, Threatwise, security IQ posture dashboard, the anomaly framework, ThreatScan, and the Recupero in Cleanroom, garantisce tale protezione.

Conclusione: Prepararsi al futuro con Commvault Cloud

Il tempo stringe. Gli enti finanziari interessati devono prepararsi ad adeguarsi al Secondo Emendamento alla Parte 500 del 23 NYCRR. Commvault Cloud, basato sulla tecnologia Metallic AI, rappresenta la soluzione ideale per supportare gli enti finanziari interessati, fornendo loro gli strumenti necessari per garantire la conformità all’emendamento. È ora di mettersi all’opera e prepararsi.

Note: This is Commvault’s perspective. Commvault does not provide legal or compliance guidance.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Throughout February, we’ve celebrated Black History Month across our global Vaulter community with events, educational initiatives, and open dialogues hosted by our Multi-Culture Employee Resource Group (ERG) and Diversity, Equity, and Inclusion (DEI) team.

Black History Month is a time to honor the rich heritage of African American contributions to history, culture, and society. Moreover, we’re honoring the achievements and resilience of Black individuals. By embracing the stories and experiences of the Black community, we aim to cultivate a workplace that promotes equity, understanding, and unity among all Vaulters, especially regarding our African American Vaulters. 

We took the opportunity to open the month with an event to spotlight the work and achievements of the legacy organization, United Negro College Fund (UNCF). UNCF, which celebrated 80 years of service this year, is a philanthropic organization that funds scholarships for underrepresented students and general operating support for over 37 private Historically Black Colleges and Universities (HBCUs). Over the years, this organization has cultivated some of the country’s most brilliant minds. We heard from UNCF leaders Ngozi Claire Emenyeonu, Mary Williams, and Lu Duong on how their work in the field is combating bias in the tech industry and how the Commvault community can combat bias in tech too.

To close the month, our Multi-Culture ERG partnered with the Black employees at Microsoft (BAM) ERG Miami, Florida Chapter to host an event featuring former NBA player, Baron Davis. Baron discussed the incredible work he is doing now as a Founder, Entrepreneur, and Investor after retiring from playing NBA basketball for 18 years, as he’s focused on empowering the black community through sports, media, business and technology.

Comeha sottolineato all’inizio di questo mese, our commitment to Black History Month extends beyond February as we’re actively celebrating Black history and embracing diversity year-round. DEI is foundational to everything we do – every day, we value and celebrate the unique perspectives each employee brings to the table as we foster innovation and collaboration. 

In futuro, continueremo a promuovere un dialogo costante, a sostenere iniziative che valorizzino la diversità delle voci e a garantire che le nostre pratiche di assunzione e le opportunità di sviluppo professionale siano eque.

Per saperne di più sulle nostre iniziative in materia di DEI (Diversità, Equità e Inclusione) presso Commvault,clicca qui.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Incident Response Teams (IRT) are the cyber guardians operating like a 24/7 commando Delta Force. Their mission is to spot cyber threats before they materialize, shielding organizations from potential breaches. In the event of an intrusion, they’re the rapid response force, minimizing impact with unwavering dedication and expertise, ensuring organizations’ digital fortress stands resilient against any challenge.

Driven by theNIST defined incident response lifecycle, this methodology seamlessly incorporates insights and best practices from NIST;MITRE ATT&CK, a globally-accessible knowledge base of adversary Tactics, Techniques, and Procedures (TTP); andCISA’s Incident Response Playbooks. This blog post explores how Commvault® Cloud, powered by Metallic® AI, and strategically combined with SIEM, XSOAR, and other ecosystem integrations, supports incident response, minimizing impacts, and elevating cyber resilience.

Preparazione

Una preparazione proattiva è un elemento fondamentale per una risposta efficace agli incidenti. Ciò comporta la documentazione delle politiche di risposta, l’implementazione di strumenti di rilevamento precoce e la formazione degli utenti sulle minacce informatiche. Questo sforzo collaborativo è in linea con il quadro di riferimento del NIST e integra le raccomandazioni relative alle TTP.

I team IRT e IT collaborano alla gestione degli incidenti e utilizzano Commvault Cloud, che offre una gestione unificata, vanta un’architettura zero-trust, l’isolamento delle chiavi di crittografia dei dati e misure di sicurezza avanzate. Tale collaborazione consente di creare architetture resilienti e di garantire la resilienza delle operazioni critiche, preparandosi al peggio. Questi sforzi sono potenziati dalle funzionalità di cyber-resilienza di Commvault Cloud, dal rilevamento basato sull’intelligenza artificiale, dall’integrazione con SIEM/XSOAR e da altri componenti dell’ecosistema.

Rilevamento e analisi

The detection and analysis phase, a multi-step process, demands accurate identification of incident types. Commvault Cloud, with its AI-driven detection andThreat Scan, excels in identifying suspicious binaries within backups, helping pinpoint potential threats. Commvault CloudThreatwisecomplements this by enabling IRT to set countermeasures swiftly, creating decoys for proactive early detection and analysis, then conducting further dynamic analysis in a sandbox environment.

Contenimento

Un contenimento efficace è fondamentale, soprattutto in caso di incidenti gravi. Commvault Cloud Threatwise, integrato con il Network Access Control (NAC) e sfruttando le funzionalità syslog, facilita il contenimento identificando gli host che sferrano gli attacchi. Allo stesso tempo, in caso di rilevamento di file sospetti, Commvault Cloud mette automaticamente in quarantena i file infetti nei carichi di lavoro di backup, e la sua opzione Cleanroom Recovery può essere utilizzata dall’IRT per creare un ambiente controllato per il monitoraggio e ulteriori analisi forensi informatiche, in linea con la strategia dell’IRT. L’integrazione con SIEM e XSOAR semplifica ulteriormente le operazioni di contenimento quando necessario, inclusa la disattivazione della scadenza dei dati o la disabilitazione degli utenti a rischio quando viene rilevata un’attività insolita sui file, fornendo informazioni e azioni in tempo reale.

Eradicazione e Recovery

Dopo il contenimento, l’eradicazione mira a eliminare le componenti coinvolte nell’incidente. Commvault Cloud, con le sue funzionalità complete di Backup and Recovery, la convalida e le capacità di scalabilità dell’Auto Recovery, svolge un ruolo cruciale. L’opzioneRecupero in Cleanroomfacilita l’analisi forense post-incidente, consentendo un esame approfondito dell’ambiente.

Attività successive all’incidente

Le riunioni post-incidente dedicate alle “lezioni apprese” sono fondamentali per il miglioramento continuo. L’analisi dei dati, compresi i costi e le caratteristiche degli incidenti, fornisce informazioni utili per la valutazione dei rischi. È inoltre importante, quando necessario, garantire un coordinamento efficace con soggetti esterni, quali le squadre di risposta agli incidenti e le forze dell’ordine. Ad esempio,la CISA ha pubblicato delle linee guidavolte a garantire un approccio standardizzato e resiliente agli incidenti di sicurezza informatica per gli enti facenti parte del FCEB.

Per rafforzare l’approccio proattivo dell’IRT, le analisi IT e le misure correttive fornite da Commvault Cloud consolidano le difese e offrono un solido set di strumenti per una risposta completa agli incidenti.

Conclusione

Nel panorama dinamico delle minacce informatiche, la sinergia tra i team di risposta agli incidenti e le funzionalità all’avanguardia offerte da Commvault Cloud, strategicamente integrate con SIEM, XSOAR e altre integrazioni dell’ecosistema, è di fondamentale importanza. Questa collaborazione non solo riduce al minimo l’impatto degli incidenti, ma rafforza anche le organizzazioni contro le minacce informatiche in continua evoluzione, garantendo una risposta resiliente ed efficace. I difensori della resilienza, armati di Commvault Cloud, intelligenza artificiale e integrazioni strategiche, sono pronti ad affrontare le sfide della frontiera informatica.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Mentre le organizzazioni si trovano a dover affrontare la crescente frequenza e sofisticazione degli attacchi informatici, è diventato fondamentale adottare una mentalità orientata alla resilienza informatica. Per fare luce su questo tema cruciale, Commvault ha recentemente organizzato un webinar dal titolo“Embrace the Breach: Business Continuity with Cleanroom Recovery”.

Punti salienti del webinar

In questo webinar, alcuni esperti del settore hanno discusso dell’importanza delle soluzioni di resilienza informatica, tra cui la soluzione Cleanroom Recovery di Commvault, sviluppata in collaborazione con Microsoft. Tra i punti chiave emersi:

  1. The Shift Towards Cyber Resilience: The webinar emphasized the need for organizations to shift their mindset from “if” or “when” they will be attacked to preparing for recovery and resilience in the face of inevitable breaches. As Tim Zonca, VP of Portfolio Marketing at Commvault, highlighted: “Gone are the days of people thinking, if they get attacked, or even when they get attacked, and a lot of the conversation and the focus and the energy is spent around the assumption that it will happen.” This shift in perspective underscores the urgency of implementing cyber resilience solutions.
  2. The Challenges of Recovery Testing: Recovery testing is crucial for organizations to ensure readiness in the event of a cyberattack. However, the status quo of recovery testing often falls short due to its complexity and cost. Tim Zonca noted that testing the recovery of a wide range of applications is often cumbersome and unfeasible for many organizations. This highlights the need for a more efficient and cost-effective solution.
  3. Commvault Cleanroom Recovery: Developed in partnership with Microsoft, Commvault’s Cleanroom Recovery solution offers a way to securely and quickly recover applications in the event of a cyberattack. This solution provides an on-demand cleanroom that enables reliable cyber recovery. Karl Rautenstrauch, Principal Product Manager at Microsoft, said, “what if there was a way to ensure that you could recover clean, pristine applications, reliable every time? And I think that’s what we’ve built together [with Commvault].” This solution can be used for readiness testing, forensic analysis, or production failover, providing organizations with the flexibility they need.
  4. Any-to-Any Portability and Automation: One of the key advantages of Commvault’s Cleanroom Recovery solution is any-to-any portability. This means that data and applications from anywhere can be recovered to any system, enabling seamless recovery processes. Additionally, the solution is automated, simplifying the recovery process and reducing complexity.
Perché dovresti guardarlo

The webinar offers valuable insights into the evolving landscape of cyber threats and the importance of cyber resilience solutions. By watching, you’ll gain a deeper understanding of:

  1. La crescente minaccia degli attacchi informatici e la necessità di una resilienza informatica.
  2. Le sfide legate ai test di Recovery tradizionali e la necessità di una soluzione più efficiente.
  3. La soluzione Cleanroom Recovery di Commvault e la sua capacità di garantire un ripristino sicuro e rapido in caso di attacchi ransomware e altri problemi che incidono sull’attività aziendale.
  4. La flessibilità della soluzione per i test di Readiness, l’analisi forense e il failover in produzione.
  5. Le features di portabilità “any-to-any” e di automazione che semplificano il processo di Recovery.

By embracing the inevitability of breaches and implementing solutions like Commvault’s Cleanroom Recovery, businesses can take positive steps to help ensure continuity and protect themselves against the ever-growing cyber threats. Watch the on-demand webinartoday to stay ahead in the battle against cyberattacks.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Scopri gli ultimi miglioramenti e le nuove funzionalità per potenziare la tua strategia di resilienza informatica e protezione dei dati.

Noi di Commvault stiamo riducendo i costi e la complessità della protezione della vostra azienda. A dicembre abbiamo condiviso alcune interessanti novità sullaavailability of key features of Commvault® Cloud. But that’s not all! We’re thrilled to announce the general availability of Commvault Cloud Platform Release 2024 – our latest release packed with new capabilities and services to meet the needs of today’s hybrid enterprise.

Liberate la potenza dei vostri dati: Unificare, proteggere, gestire

Platform Release 2024 introduces the latest enhancements to the Commvault Cloud console, eliminating time-consuming manual processes and multiple dashboard reviews through unified management, real-time insights, and consolidated data views – all in one convenient location.

Questo nuovo approccio consente di configurare e gestire facilmente criteri, gruppi e autorizzazioni globali in un’unica posizione. È possibile distribuirli rapidamente in tutto l’ambiente per ottimizzare e unificare la gestione della configurazione.

Uncover and Eliminate Cyberthreats Sooner – Before Data Is Compromised

An important part of Cyber resilience strategy is discovering and preventing threats. Building on the existing early-warning technology of our Threatwise capabilities, Platform Release 2024 introduces Threatwise Advisor, which continuously assesses workloads in the backup environments to intelligently recommend what decoy sensors to configure and where.

Queste nuove funzionalità contribuiscono a semplificare il processo di configurazione, a ridurre i tempi di implementazione e a minimizzare le operazioni manuali necessarie, grazie all’identificazione delle macchine e dei servizi cruciali. Gli utenti possono aggiungere in modo semplice e rapido livelli di rilevamento ai propri ambienti di produzione basati su questi set di dati, al fine di garantire una protezione ottimale delle loro risorse più preziose.

Analisi predittiva delle minacce in tempo reale basata sull’intelligenza artificiale

Malware is constantly evolving, and dynamically changing, making it more difficult to detect. Zero-day and polymorphic AI-driven malware can go undetected and remain dormant for days at a time, while backups are continuous. Infected files can end up within the backup, causing a false sense of safety while impacting the ability to recover cleanly. Platform Release 2024 introduces Threat Scan Predict, which takes our existing capabilities to the next level by leveraging AI-driven threat detection and prediction capabilities to identify potentially nefarious files within the backup content.  This provides higher levels of efficacy at detecting zero-day and AI type threats within backups and minimizes the risk of reinfection during data recovery.​

Simple, secure, and rapid recovery of applications​ into an on-demand cleanroom

I CISO hanno il compito di garantire che la propria organizzazione sia adeguatamente preparata ad affrontare gli attacchi informatici e le loro conseguenze. Tuttavia, la Readiness al ripristino e i relativi test possono rivelarsi attività complesse, raramente portate a termine con successo, spesso a causa di limitazioni in termini di risorse. Ciò mette a rischio l’affidabilità del ripristino, la Readiness operativa e la resilienza.

Il nostro nuovo servizioRecupero in Cleanroomper macchine virtuali offre un ambiente sicuro e isolato in cui le organizzazioni possono testare i propri piani di ripristino informatico senza interferire con i sistemi di produzione. Questo ambiente consente alle organizzazioni di individuare e colmare le lacune nei piani prima che si verifichi un attacco. L’ambiente “cleanroom” può essere utilizzato anche per l’analisi forense di sistemi notoriamente infetti, aiutando così le organizzazioni a comprendere la causa principale di un attacco e ad adottare le misure necessarie per prevenire incidenti futuri. E quando si verifica effettivamente un incidente, il nostro servizio offre una Recovery sicura in una “cleanroom” nel cloud, indipendentemente dall’ambiente di origine, con portabilità “any-to-any”.

Bolster your cyber resilience with Commvault’s latest security integrations

Commvault ha stretto una partnership con Netskope, azienda specializzata in sicurezza informatica, per migliorare il livello di sicurezza dei clienti. Questa collaborazione aiuta i clienti a identificare rapidamente e a rispondere alle potenziali minacce, fornendo informazioni e visibilità combinate. I clienti possono arricchire le proprie informazioni di sicurezza integrando le analisi delle anomalie di Commvault Cloud in Netskope Cloud Threat Exchange. I team di sicurezza (SecOP) possono correlare le informazioni sulle minacce esistenti con queste analisi delle anomalie, promuovendo azioni di protezione proattive. Inoltre, i clienti ricevono da Netskope informazioni sulle minacce, quali i server che sono stati compromessi da attività malevole. Queste informazioni vengono visualizzate nella dashboard Security IQ di Commvault, consentendo ai clienti di intraprendere azioni di protezione e garantire la recuperabilità dei dati.

Security teams face the challenge of responding as quickly as possible to security events to minimize the impact of cyber threats. By leveraging threat insights from DarkTrace, customers can view protected servers that are impacted on Commvault’s Security IQ dashboard. This helps inform users of potential risks to backup assets, enabling proactive measures like Threat Scanning to safeguard data and enable recoverability.

Nuove opzioni hardware Dell per HyperScale X Commvault Cloud HyperScale X

Con l’introduzione dei nostri nuovi dispositivi di backup Dell, siamo lieti di offrirvi maggiore flessibilità e scelta nella protezione delle informazioni critiche. I clienti possono scegliere tra una gamma di fornitori di hardware per le Appliances HyperScale X, il che consente di personalizzare la soluzione in base alle proprie esigenze specifiche e al proprio budget, sfruttando al contempo l’infrastruttura esistente.

I clienti Dell possono ora usufruire dell’esperienza offerta dall’HyperScale X Appliance sullo stesso hardware utilizzato nei loro data center IT esistenti, con un numero maggiore di soluzioni in grado di soddisfare un’ampia gamma di esigenze, capacità e preferenze.

Expanded Commvault Cloud SaaS Capabilities – Coming Soon

Oltre a queste nuove Features, a partire da metà marzo amplieremo anche il nostro supporto completo alle funzionalità SaaS nelle seguenti aree:

  • Threat Scan support for Files: Threat Scan for SaaS now supports Files to enable you to securely recover data as quickly as possible by identifying malware, encrypted content, and vulnerable data. This provides safe recovery options to recover clean data and avoid reinfection by accidentally restoring malicious files.
  • Risk Analysis support for M365: Risk Analysis for SaaS supports M365, offers a better way to secure and defend your M365 data by making it easy to systematically discover, classify, and protect dark and sensitive data, empowering a proactive defense against data breaches and helping you meet your compliance requirements.
  • Auto Recovery for VMs: Auto Recovery as a service for VMs delivers secure, automated recovery at scale to help you quickly and securely recover VM workloads from disasters with minimal data loss and downtime.

Queste sono solo alcune delle straordinarie Features incluse nella versione 2024 della piattaforma. Per saperne di più sulle ultime Features:

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Gli attacchi informatici si sono trasformati in una minaccia pervasiva e sofisticata, che rappresenta un pericolo significativo per le organizzazioni di ogni dimensione. La natura in continua evoluzione delle minacce informatiche richiede un nuovo modo di pensare in materia di resilienza informatica. Nonostante l’implementazione delle migliori soluzioni di sicurezza perimetrale disponibili sul mercato, le probabilità che malintenzionati riescano a penetrare nel sistema sono molto elevate. Tenendo presente questo, come è possibile garantire una Recovery rapida quando si verificherà un evento del genere e, cosa altrettanto importante, come è possibile VERIFICARE in anticipo il proprio piano di Recovery per assicurarsi che funzioni?

Recupero in Cleanroom, lanciato a novembre e oggi disponibile per il supporto dei carichi di lavoro delle macchine virtuali (VM) software, fornisce alle organizzazioni le conoscenze necessarie per prevenire gli attacchi, difendersi dagli autori di azioni malevole e ripristinare gli ambienti in uno stato sicuro.

But, Cleanroom Recovery also provides a safe and isolated environment where organizations can easily test their cyber recovery plans without disrupting production systems. This environment allows organizations to identify and address gaps in their plans before an actual attack occurs. Cleanroom environments also provide forensic analysis of known infected systems and provide analysis that helps organizations understand the root cause of the attack—critical information to prevent future incidents.

Cleanroom Recovery should be a primary pillar in every organization’s cyber resilience strategy.

Today’s Cyber Recovery Reality: It’s Not Easy

Negli ultimi anni la frequenza e la gravità degli attacchi informatici sono aumentate drasticamente, rappresentando una minaccia concreta per le organizzazioni di tutti i settori. Questi attacchi possono avere conseguenze devastanti, tra cui violazioni dei dati, perdite finanziarie e danni irreparabili alla reputazione.

In unrecente sondaggio condotto da The Futurum Group,il 98% degli intervistati ha indicato che la recuperabilità dei dati influisce sulla loro resilienza contro gli attacchi ransomware, con tre quarti degli intervistati che ritengono che tale influenza sia molto o estremamente significativa. Un’efficace Recovery informatica è fondamentale affinché le organizzazioni possano ridurre al minimo i tempi di inattività, ripristinare le operazioni aziendali e salvaguardare la propria reputazione dopo un attacco informatico. Tuttavia, molte organizzazioni hanno difficoltà a testare adeguatamente i propri piani di Recovery informatica, rimanendo così vulnerabili agli attacchi reali.

In un mondo ibrido in continua evoluzione, le organizzazioni devono attenersi alle diverse disposizioni normative che entrano in gioco. Nello specifico, i quadri normativi del National Institute of Standards and Technology (NIST) e del Digital Operational Resilience Act (DORA) sono diventati una priorità assoluta per le organizzazioni. Queste disposizioni normative stabiliscono i requisiti relativi ai test, attribuendo alle imprese la responsabilità di predisporre test continui che aiutino le organizzazioni a evitare sanzioni e multe ingenti.

Le organizzazioni devono verificare costantemente il proprio approccio alla Recovery per garantire un ritorno alle attività aziendali rapido e senza intoppi.

https://play.vidyard.com/Yz7D3oyrUPoTpuEHMTWZzb
Guarda il nostro webinar sul Cleanroom Recovery perPer saperne di più.

I limiti degli attuali approcci di verifica del Recovery informatico

I metodi tradizionali di verifica della capacità di Recovery informatica, come le esercitazioni teoriche, spesso non riescono a preparare adeguatamente le organizzazioni alle complessità e al caos degli scenari reali di Recovery informatica. Queste esercitazioni prevedono in genere discussioni e simulazioni che non hanno il realismo e l’urgenza di un attacco vero e proprio.

Moreover, testing cyber recovery plans in hybrid environments can be time-consuming, complex, and expensive. With workloads spread across multiple clouds, on-premises hypervisors, and physical servers, organizations must perform testing within each environment separately. True cyber resilience isn’t solely a technological threshold that enterprises must hurdle; organizations must also understand its role in achieving true resilience.

In presenza di più team e di diversi compartimenti stagni, si tratta tanto di un’iniziativa fondamentale per l’azienda quanto di una necessità tecnologica. Tradizionalmente, i settori IT operavano in modo separato, ma per garantire una vera resilienza informatica, i team tecnologici e le linee di business devono collaborare e unire i propri sforzi. I dirigenti di alto livello devono imporre alle organizzazioni di promuovere la consapevolezza in materia di sicurezza informatica e di adottare le migliori pratiche per garantire un rapido Recovery.

As business culture evolves to encourage more and more collaboration across teams, today’s organizations are ready to embrace cleanroom recovery.

Commvault Cloud Cleanroom Recovery

Di fronte alla costante minaccia di attacchi informatici, il successo della Recovery dipende dall’accuratezza dei test di sicurezza informatica e dalle strategie di resilienza informatica.

Commvault Cloud’s Cleanroom Recovery addresses a critical need for cyber readiness by providing a comprehensive testing and failover solution that enables organizations to more effectively mitigate risk.

Le caratteristiche principali della funzionalità “Cleanroom Recovery” di Commvault Cloud includono:

  • Comprehensive testing environment: Cleanroom Recovery provides a safe and isolated environment where organizations can test their cyber recovery plans without the risk of disrupting production systems.
  • Secure forensic analysis: Cleanroom Recovery can be used to conduct forensic analysis of known infected systems and identify the root cause of an attack.
  • Faster recovery times: Cleanroom Recovery can help organizations recover from cyberattacks more quickly by providing a streamlined recovery process.
  • Reduced downtime: Cleanroom Recovery can help organizations minimize downtime by providing a production failover solution.

Cleanroom Recovery offre un ambiente sicuro e isolato per testare i piani di Recovery informatico, condurre analisi forensi e garantire la continuità operativa nel caso in cui si verifichi una violazione. Cleanroom Recovery può aiutare le organizzazioni a migliorare la propria resilienza informatica offrendo vantaggi quali:

  • Reduced risk of re-infection: Cleanroom Recovery provides a safe and isolated environment where workloads can be recovered without the risk of re-infection.
  • Enhanced security: Cleanroom Recovery can be used to identify and address security vulnerabilities in cyber recovery plans.
  • Simplified failover: Cleanroom Recovery can serve as a production failover solution in the event of a breach, ensuring that production operation recovery is conducted within a sanitized environment.

Casi d’uso per Cleanroom Recovery

Oggi le organizzazioni possono applicare la strategia “Cleanroom Recovery” in diversi scenari per garantire che le operazioni aziendali proseguano senza intoppi anche in caso di attacchi informatici.

Test dei piani di Recovery informatico in un ambiente ibrido

Cleanroom Recovery semplifica e ottimizza il processo di test dei piani di recupero informatico in ambienti ibridi. Grazie alla sua funzionalità di portabilità “any-to-any”, Cleanroom Recovery consente alle organizzazioni di ripristinare i carichi di lavoro provenienti da più cloud, hypervisor on-premise e server fisici in un ambiente comune all’interno della “cleanroom”. Ciò elimina la necessità di eseguire i test separatamente all’interno di ciascun ambiente, consentendo di risparmiare tempo e risorse.

Analisi forense di sistemi notoriamente infetti

Oltre ai test di ripristino informatico, Cleanroom Recovery offre un ambiente sicuro in cui condurre analisi forensi su sistemi notoriamente infetti. Queste analisi possono aiutare le organizzazioni a identificare la causa principale di un attacco, a comprendere in che modo gli autori dell’attacco abbiano ottenuto l’accesso ai loro sistemi e ad adottare misure volte a prevenire incidenti futuri.

Failover della produzione in caso di violazione della sicurezza

Cleanroom Recovery can serve as a production failover solution in the event of a breach. This means that if a cyberattack disrupts an organization’s production systems, it can quickly and easily recover its workloads to a clean environment within the cleanroom. This can help organizations minimize downtime and get their business back up and running quickly.

Il fallimento non è un’opzione

In today’s dynamic cybersecurity landscape, organizations must proactively address the ever-increasing threat of cyberattacks. Commvault Cloud’s Cleanroom Recoveryè uno strumento potente che consente alle organizzazioni di migliorare la propria resilienza informatica, fornendo un ambiente di test completo, funzionalità di analisi forense sicure e una soluzione di failover per l’ambiente di produzione. Adottando Cleanroom Recovery, le organizzazioni possono testare con sicurezza i propri piani di ripristino informatico, identificare e correggere le vulnerabilità e garantire la continuità operativa in caso di attacchi informatici.

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements

Il ransomware prospera nell’incertezza. La resilienza ne risente. Mantenere la propria azienda online e far fronte a un attacco è già di per sé abbastanza stressante. L’incertezza e il caos non dovrebbero provenire proprio dai fornitori che si propongono di aiutare a mantenere la resilienza.

The latest industry consolidation news with Cohesity announcing its intention to acquire Veritas’ data protection unit is causing uncertainty and doubt for their customers — and for good reason.

Insidie da evitare in caso di fusione per i clienti di Veritas e Cohesity

This merger brings disconnected platforms, with disconnected approaches, and dissonant cultures, to try to address a single problem: maintaining resilience through cyberattacks. With such major redundancies in their product lines the question on customers’ and partners’ minds is, “what gets cut and what stays?”

These deals often require customers to ultimately make changes, whether they like it or not. And change has been constant for many customers. In the last few years there have been multiple changes to Veritas’s platform starting with a switch to a new vendor for SaaS workloads, only toacquire another companylater and force yet another change. Customers may also wonder what other changes are in store: What changes will they need to make to their disaster and cyber recovery plans? How will all this impact costs, operational resources, and their ability to be resilient?

The integration process between any two companies is a complex and time-consuming endeavor, likely taking several years to complete. At a time when data has never been more vulnerable to attacks, the transition can be quite chaotic for impacted customers and partners. But it doesn’t have to be.

Commvault Cloud: la soluzione al caos

We are biased: we exist to help customers stay online and fight through threats to their business. The cure for this chaos is consistency. Consistent innovation. Consistent focus. Consistent customer success. We have a proven track record that demonstrates our consistent leadership. We’ve been public since 2006, just had our best quarter in history, and we recently introduced a unique cyber resilience platform — Commvault Cloud — that is unlike anything else on the market today. It offers cyber resilience through a single and unified platform with the flexibility to deploy as SaaS or on-premises, all running on the same modern highly scalable and secure codebase.

La nostra architettura unificata èprogettata in modo dagarantire la resilienza informatica a prova di futuro. Offriamo l’unica piattaforma di resilienza informatica con portabilità “any-to-any”, che consente di proteggere qualsiasi dato, in qualsiasi luogo, e di ripristinarlo da qualsiasi luogo verso qualsiasi destinazione. Il risultato è una resilienza senza pari per l’azienda ibrida.

We also recognize that cyber resilience starts before an attack, and never stops. That’s why we built Commvault Cloud to enable customers to advance their security posture before an attack by understanding the risk of sensitive data, categorizing and remediating those risks, getting an early warning of attacks to minimize the impact, and enabling rapid recovery in the event of an attack.

We’re also revolutionizing cyber recovery with cutting-edge innovations as part of Commvault Cloud, like Cleanroom Recovery. This offering provides a clean, safe environment to perform full-scale recoveries at-scale to enable business resilience in the face of cyberattacks. Equally as important, we enable customers to test their recovery plans, closing the gap between incident response planning and recovery. With Cleanroom Recovery, you can have peace of mind knowing that your data is protected, and your operations can swiftly resume, allowing you to focus on what matters most: serving your customers’ needs.

Un ecosistema interconnesso

I partner sono fondamentali per Commvault Cloud. Oggi disponiamo di integrazioni con tutti i principali fornitori di servizi cloud, oltre che con i principali GSI e partner nei settori della tecnologia, della distribuzione, della sicurezza e dell’intelligenza artificiale. Commvault Cloud diventa sempre più efficace man mano che si espande nel panorama dei partner.

Scegli la soluzione più sicura con Commvault Cloud

When it comes to cyber resilience, there is no time for chaos. Commvault Cloud is the cure for chaos and we’re just getting started. Give us a try today: https://www.commvault.com/free-trial

More related posts


Thumbnail_Blog-Dangerous-Silos-IDC-Resops-2026 (1)

The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan

Read more about The Importance of Recovery Point Objective (RPO) in Your Business Continuity Plan
Thumbnail_Blog-IDC-Resops-2026

Business Continuity Planning for the Cloud-Native Era

Read more about Business Continuity Planning for the Cloud-Native Era
Thumbnail_Blog-Bringing-Trust-to-CVE-2026

Demystifying SOC 2 Data Protection Requirements

Read more about Demystifying SOC 2 Data Protection Requirements